Ukrainian cops seize cash, computers as part of Clop ransomware crew disruption
Full article591 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Clop is the same gang thought responsible for a messy extortion incident that affected the IT provider Accellion.
Ukrainian authorities said Wednesday they’ve taken action against a hacking outfit that was responsible for roughly half a billion dollars in digital extortion in recent years, in a rare example of law enforcement disrupting accused ransomware scammers.
Six unnamed suspects are accused of infecting organizations in the U.S. and South Korea with the Clop ransomware. Investigators previously linked prior Clop activity to TA505, a financial hacking group, and a messy data breach at Accellion, in which hackers leveraged access to an IT vendor to threaten a number of its partners.
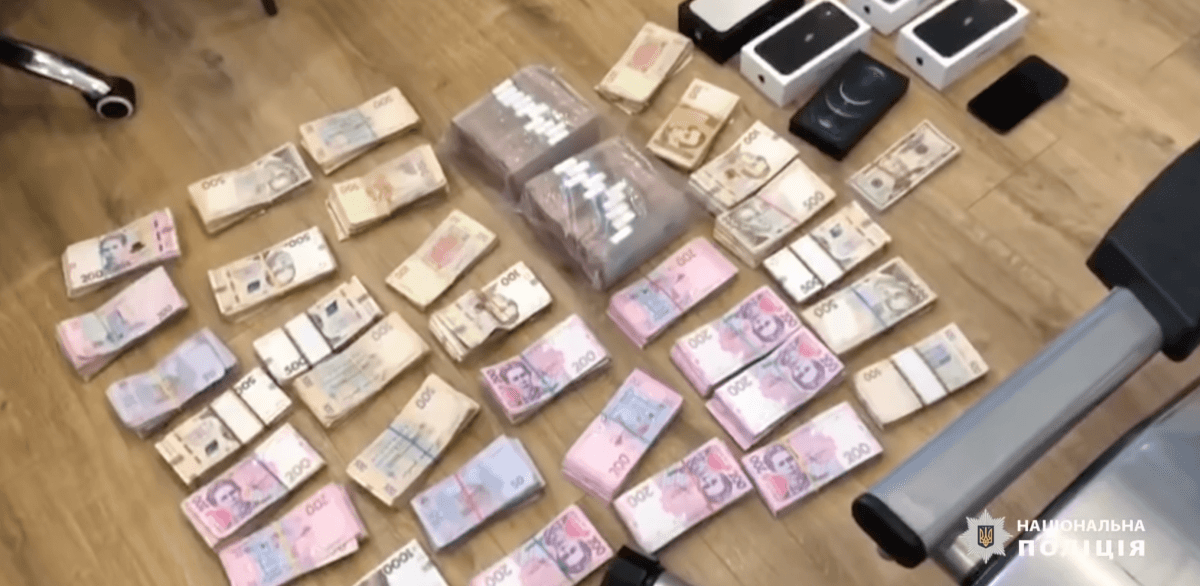
According to a statement Wednesday police carried out 21 searches in the capital city of Kyiv, including the homes and cars of the defendants, to seize computer equipment and $5 million in Ukrainian hryvnia currency (roughly $184,000 in U.S. dollars). Whether police had targeted Clop developers or an affiliate group that subscribed to a larger ransomware service was not immediately clear. The six suspected likely functioned as a money laundering arm of the larger ransomware operation, the threat intelligence firm Intel 471 suggested.
Victims included Stanford University’s Medical School, the University of Maryland, the University of California and a number of Korean organizations that Ukrainian authorities did not disclose.
Hackers combined the use of Clop (alternately stylized as Cl0p) with other hacking tools, such as the malicious software Cobalt Strike and a remote managed program dubbed “FlawedAmmyy RAT” to cause damages of up to $500 million, according to the police statement.
Each defendant faces up to eight years in prison if convicted.
U.S. and Korean law enforcement also aided the investigation.
Previous victims of the Clop ransomware spree also appear to include the Michigan-based Flagstar Bank, the cloud computing service Qualys and the grocery chain Kroger. The group is one of the many responsible for pushing extortion demands higher over the past year.
The police action comes amid recent comments from U.S. officials that ransomware represents a national security threat along the lines of global terrorism following breaches at the meat producer JBS and Colonial Pipeline, an oil and gas delivery firm.
Authorities also published a video of the Ukrainian action Wednesday.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/ukrainian-cops-seize-cash-computers-as-part-of-clop-ransomware-crew-disruption/