House panel leaders call on Microsoft president to testify over security shortcomings
Full article836 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The Homeland Security Committee plans a May 22 hearing.
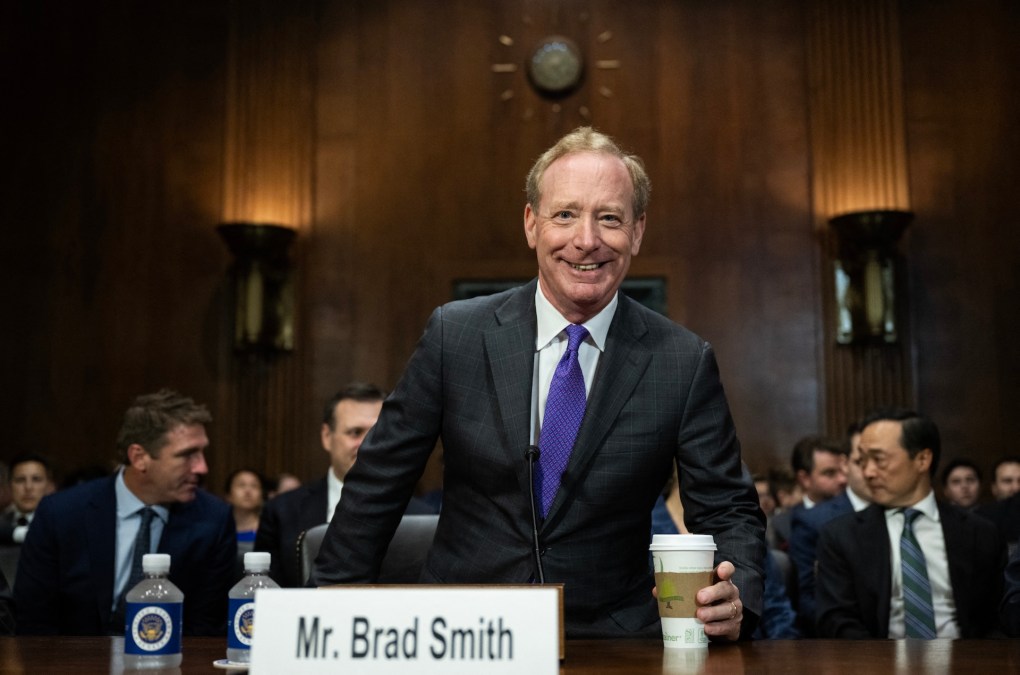
Leaders of the House Homeland Security Committee want Microsoft President Brad Smith to testify before their panel in the aftermath of accumulating cybersecurity incidents that have drawn ample negative attention to the tech giant.
In particular, the committee is zeroing in on a Cyber Safety Review Board report that faulted Microsoft for “a cascade of security failures” that abetted Chinese government-affiliated hackers’ theft last summer of thousands of emails, including those from federal agencies.
“As a trusted provider of operating systems, cloud platforms, and productivity software for U.S. government agencies, including those within the U.S. intelligence community, Microsoft bears a profound responsibility to prioritize and implement effective cybersecurity measures,” Chairman Mark Green, R-Tenn., and top panel Democrat Bennie Thompson of Mississippi wrote in a Thursday letter to Smith.
The lawmakers continued: “However, the CSRB report revealed that Microsoft has repeatedly failed to prevent substantial cyber intrusions, causing grave implications for the security and integrity of U.S. government data, networks, and information, and putting Americans — including U.S. government officials — at risk.”
The panel plans a hearing on May 22.
“While Microsoft’s cooperation with the CSRB’s investigation was encouraging, the numerous failures revealed in the report led to serious threats to our homeland and must be fully examined by this Committee,” Green said in a written statement to CyberScoop. “Amid ever-increasing cyber threats from China, Russia, Iran, and others, it is of paramount importance that a critical provider of operating systems, cloud platforms, and productivity software for the U.S. government can safeguard its systems and properly implement cybersecurity measures to prevent cyber intrusions.
“We believe recent events have undermined that trust and must be fully examined by this Committee,” he continued. “We look forward to the company’s cooperation as we work to increase the security and the resilience of our federal networks.”
Microsoft said it welcomed the discussion but didn’t commit to the hearing date yet.
“We’re always committed to providing Congress with information that is important to the nation’s security, and we look forward to discussing the specifics of the best time and way to do this,” a Microsoft spokesperson said.
The incident described in the report isn’t the only one to make headlines involving Microsoft and federal agencies. The Cybersecurity and Infrastructure Security Agency issued an emergency directive to address another breach that occurred in January.
With dismay over Microsoft’s vulnerabilities growing in Washington, D.C., the company announced organizational changes designed to improve its security culture. The Homeland Security Committee leaders said part of the hearing’s purpose is to examine future Microsoft plans for improvement.
More Scoops
Rep. Delia Ramirez takes over as top House cybersecurity Dem
She replaces Rep. Eric Swalwell following his resignation, giving her the position of ranking member of the Subcommittee on Cybersecurity and Infrastructure Protection.
Across party lines and industry, the verdict is the same: CISA is in trouble
Lawmakers probe CISA leader over staffing decisions
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/house-panel-leaders-call-on-microsoft-president-to-testify-over-security-shortcomings/