Wyden urges DHS to adopt secure email authentication protocol
Full article951 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The driving force behind Wyden's increasingly granular push to improve U.S. government cybersecurity is Chris Soghoian, the former ACLU technologist who joined Wyden's office earlier this year.
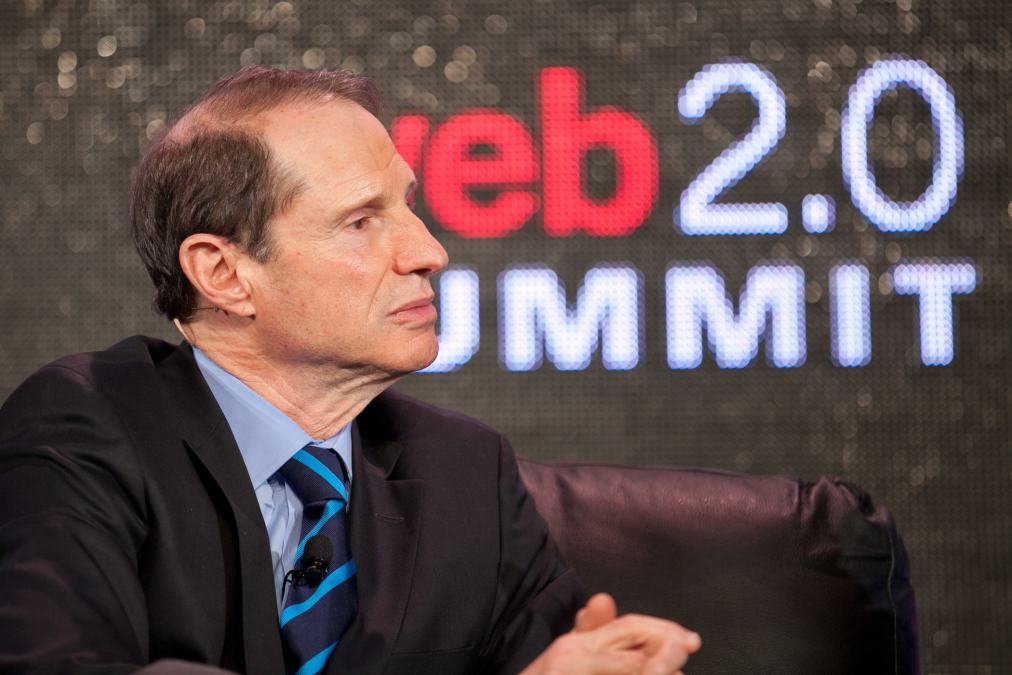
Sen. Ron Wyden, D-Ore., has asked the Department of Homeland Security to move the federal government to adopt a protocol that would defend and protect government offices from email spoofing and phishing attempts.
According to a letter sent to acting DHS Deputy Undersecretary of Cybersecurity Jeanette Manfra, Wyden wants the government to adopt Domain-based Message Authentication, Reporting & Conformance. Widely known as DMARC, the protocol is a technical standard finalized in 2015 by contributors including Google, Yahoo, Mail.ru, JPMorganChase and Symantec.
The push for widespread adoption of DMARC is particularly timely now in the wake of a June 2017 report concluding that less than one-third of the largest 98 public and private hospitals in the United States secure their email with the technology. The same email-based threats faced by private enterprise have hit the U.S. government, especially in the last year.
“The threat posed by criminals and foreign governments impersonating U.S. government agencies is real,” Wyden wrote. “For example, in May, news reports revealed an active phishing campaign in which hackers were sending emails purporting to come from the Defense Security Service. Likewise, in 2016, the Internal Revenue Service reported a 400 percent increase in attempts by criminals to impersonate the agency through phishing.”
DHS is tasked with defending federal networks and has the authority, under the Federal Information Security Modernization Act, to mandate agencies enable DMARC.
Wyden has been pushing government agencies to adopt and mandate industry standard security practices with a level of detail that lawmakers rarely approach. In March, he called for the Department of Defense to adopt STARTTLS encryption. In April, he pushed for multifactor authentication in the Senate.
The driving force behind Wyden’s push to improve U.S. government cybersecurity is Chris Soghoian, the former ACLU technologist who joined Wyden’s office earlier this year as a TechCongress Innovation Fellow. Soghoian, a rarity in Congress due his technical expertise (he holds a graduate degree in Security Informatics from Johns Hopkins University), gained fame in his four years working for the American Civil Liberties Union for being both technically-minded and outspoken on cybersecurity and privacy issues.
Expect the push to improve government security to keep coming from Wyden. Cybersecurity has become top of mind for a certain set of lawmakers, especially as reports come to light that federal agencies may be gutted of its cybersecurity policy leadership.
“Sen. Wyden is pushing government agencies to pick up years-old, common sense stuff,” Keith Chu, a spokesman for Wyden, said. “Especially when you keep seeing politicians looking for encryption backdoors and other extreme measures of security, Wyden wants to show that you don’t have to have a trade off on security measures if you take the easy steps that government is often taking, like encryption and two-factor authentication.”
The Global Cyber Alliance (GCA), a partnership of European and American law enforcement and research organizations, said DMARC “has been proven effective, and deployment can reasonably be done by organizations of all sizes, making it an invaluable resource for hospitals who need to protect their patients’ digital health.”
An analysis in May found that only about two percent of federal domains had implemented DMARC, according to GCA CEO Phil Reitinger.
“All federal agencies should without question implement DMARC as Sen. Wyden wants,” Reitinger told CyberScoop. “I believe the U.S. Government understands the value of DMARC and is already considering broad deployment. The leadership gets it.”
Read the letter below:
[documentcloud url=”http://www.documentcloud.org/documents/3896917-Download.html” responsive=true sidebar=false text=false pdf=false]
Shaun Waterman contributed to this report.
More Scoops
Sen. Wyden urges feds to discard older, insecure, public-facing VPNs
In a letter first reported by CyberScoop, Ron Wyden, D-Ore., said ‘devastating’ attacks on the federal government have accumulated due to the tech.
Wyden calls on FTC to investigate Microsoft for ‘gross cybersecurity negligence’ in protecting critical infrastructure
Blistering Wyden letter seeks review of federal court cybersecurity, citing ‘incompetence,’ ‘negligence’
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/ron-wyden-dhs-dmarc-letter-chris-sogohian/