ISSE 2009
Full article339 words · extracted from securelist.com · click to collapse



Greetings from the “Steigenberger Kurhaus Hotel” in The Hague, or “Den Haag”, as the locals like to call it, where the 2009 ISSE Conference is currently taking place.
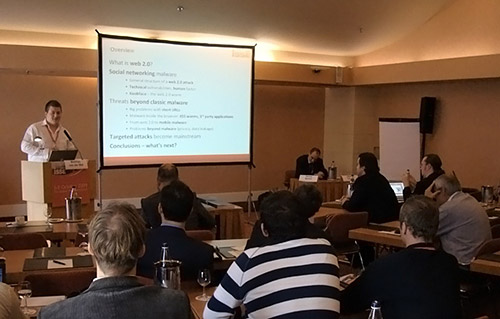
I’m here with my colleague Stefan (in the pic), who delivered his presentation on WEB 2.0 threats earlier today, on the second day of the conference.
Yesterday was the grand opening day, with a number of interesting speeches. Norbert Pohlmann, Chairman of the Board, TeleTrusT, had a very interesting talk about the way we’ll work in the future. His data indicates that today we have about 70 CPUs per person, in netbooks, cars, mobiles etc…but we’ll reach thousands of CPUs per person in the next 10 years.
Jim King, PDF Platform Architect, from Adobe Systems Incorporated, delivered a very interesting presentation on the advantages of using PDF and embedding digital signatures into them. With PDF being today’s file format of choice for malware delivery, it may be that some organizations start moving away from PDF files. This is why it’s very important that Adobe begins what Microsoft did in 2002 with the Trustworthy Computing Initiative.
Mike Reavey, Director of MRSC (Microsoft), delivered a very interesting speech explaining the MSRC process; he did say a few controversial things which generated heated debate afterwards – for instance, “There are hackers who actually work at Microsoft”.
All the best from the cloudy Netherlands!
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/isse-2009/30565/