Multimedia Overwriter with Spy Features
Full article361 words · extracted from securelist.com · click to collapse



Yesterday morning we received a sample from Cuba of a malware that looks for the following audio and video file extensions after infecting a victim’s machine: .mp3, .mp4, .mpg, .avi, .mkv, .vob, .dat, .rmvb, .flv, .wav

Once the files are found, the malware overwrites them with a generic mp3 track that you may listen to here.
It’s a locally refurbished version, probably in the same country mentioned above, targeting mainly Spanish-speaking users. It’s written in Delphi and according to the timestamp, it was compiled on September 10, 2013. There is a message intentionally left in the code:
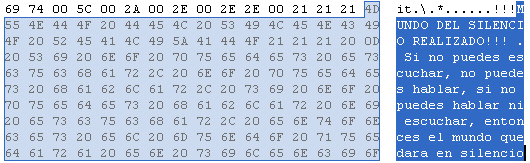
!!!MUNDO DEL SILENCIO REALIZADO!!!
Si no puedes escuchar, no puedes hablar, si no puedes hablar ni escuchar, entonces el mundo quedara en silencio.
Translation: World of Achieved Silence!
If you can’t listen, you can’t speak, if you can’t speak nor listen then the world will remain in silence.
There is another hidden functionality to this malware- it spies the victims’ machines. It steals information from the clipboard, makes screenshots and registers all keystrokes from the keyboard of the victim. Given this concealed function, the malware’s initial act of overwriting the audio and video files is probably just a distraction from its true purpose.
The sample propagates via USB devices by enumerating the disks and making a copy of itself on them.
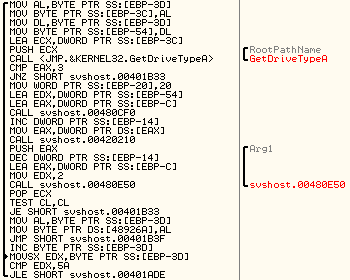
The sample was initially detected by KSN technology some time ago and now it’s also detected via regular updates as Trojan.Win32.Malex.af
You may follow me on twitter @dimitribest
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/multimedia-overwriter-with-spy-features/57189/