CeBIT 2005
Full article243 words · extracted from securelist.com · click to collapse
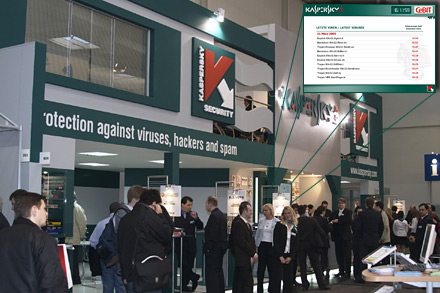

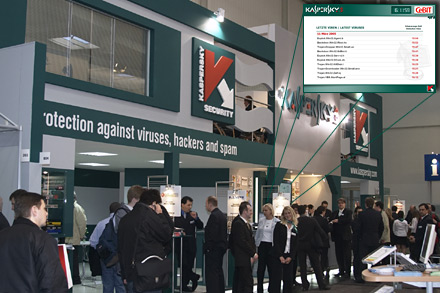
Another year, another CeBIT.
And here we are again in Hanover, at the biggest international IT fair. There’s a lot going on, with all the security exhibitors in Hall 7. We’re at Stand 04, and we’ve got a lot more space than last year.
Yesterday was busy – a press conference and presentation which brought lots of questions. There’s also participants visiting our stand to see what we are up to. One highlight – a screen displaying in real time the names of the viruses which our analysts are busy detecting back in Moscow. Gives an overall view of what’s going on in the malware world, and how for every ‘loud’ virus, there are hundreds of little ones which normally users never hear about.
Come and visit us and take a look!
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/cebit-2005/29978/