The vulnerability landscape in Q1 2026
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2017-0199 | Remote Code Execution in Microsoft Office and WordPad via crafted document files CVE-2017-0199 is a remote code execution vulnerability in Microsoft Office and WordPad that stems from improper parsing of specially crafted files. Attackers trigger it by getting a user to open a malicious document, after which attacker-controlled code executes with the privileges of the logged-in user. Anyone running the affected Microsoft Office or WordPad software is exposed, and CISA notes the flaw has been leveraged in ransomware campaigns; no CVSS score is available in the source data. The flaw was added to CISA's Known Exploited Vulnerabilities catalog on 2021-11-03, and EPSS assigns a 99.9% probability of exploitation within 30 days (100th percentile), indicating active, ongoing exploitation. Do: Apply Microsoft's security updates for Office and Windows per vendor instructions, as required by CISA's KEV catalog; the flaw was publicly reported as fixed in Microsoft's April 2017 security updates. Until patched, treat unsolicited Office documents and email attachments as high-risk, since exploitation requires a user to open a crafted file. Verify that all Office and WordPad installations across the estate—especially endpoints that handle untrusted documents—have received the update. | 7.8 | 100% | KEV ransomware PoC ×6 |
| masshundreds of millions of Office installations worldwide (exact count unknown) | |
| CVE-2017-11882 | Memory Corruption RCE in Microsoft Office via Legacy Equation Editor CVE-2017-11882 is a memory corruption vulnerability (CWE-119) in Microsoft Office, residing in the legacy Microsoft Equation Editor component (EQNEDT32.EXE), that allows remote code execution in the context of the current user. Attackers trigger it by persuading a user to open a crafted document, most commonly an RTF file or other Office document carrying a malicious embedded equation object, which overflows a buffer while the equation content is parsed. Successful exploitation lets the attacker run arbitrary code with the privileges of the signed-in user, a typical foothold for malware delivery and, per CISA, for ransomware operations. Any environment running affected Microsoft Office builds is exposed; the source data does not enumerate specific affected version ranges. The flaw is confirmed exploited in the wild: it was added to the CISA Known Exploited Vulnerabilities catalog on 2021-11-03 with known ransomware use and holds a 99.9% EPSS score (percentile 100), though the source data lists no public PoC. Do: Apply Microsoft's Office security updates (November 2017 or later) across all endpoints, prioritizing this KEV-listed flaw given its known ransomware use. On systems that cannot yet be patched, disable or unregister the legacy Equation Editor (EQNEDT32.EXE) and consider blocking or warning on RTF attachments as interim mitigations. Check for indicators of abuse such as EQNEDT32.EXE spawning unexpected child processes after document opens. | 7.8 | 100% | KEV ransomware PoC ×10 |
| masshundreds of millions of users/installations (Office is near-ubiquitous on Windows and in enterprises; the share still unpatched is unknown) | |
| CVE-2018-0802 | Memory Corruption RCE in Microsoft Office Equation Editor A memory-corruption flaw (out-of-bounds write, CWE-787) in the legacy Equation Editor component (EQNEDT32.EXE) shipped with Microsoft Office 2007, 2010, 2013, and 2016 allows remote code execution due to improper handling of objects in memory. An attacker triggers it by persuading a user to open a specially crafted document (for example an RTF or DOCX containing a malformed embedded equation object), causing the Equation Editor process to corrupt memory when the file is opened in Word; the user-interaction requirement is reflected in the CVSS 3.1 vector (AV:L/UI:R). Successful exploitation gives the attacker code execution in the context of the current user, with high impact on confidentiality, integrity, and availability (CVSS 3.1 score 7.8, High). Any user of the affected Office versions, the Office Compatibility Pack, or Word on an unpatched system is affected. Exploitation is confirmed in the wild: the flaw is in CISA's Known Exploited Vulnerabilities catalog (added 2021-11-03) with known ransomware use, carries a 93.3% EPSS probability of exploitation within 30 days, and multiple public analyses and proof-of-concepts exist. Do: Apply Microsoft's January 2018 security updates for Office 2007, 2010, 2013, and 2016 and the Office Compatibility Pack, and verify the legacy Equation Editor executable (EQNEDT32.EXE) on endpoints has been patched or removed (Microsoft later retired the component). Because the flaw is exploited in the wild and used in ransomware campaigns, prioritize remediation per CISA KEV required action and hunt for Word spawning EQNEDT32.EXE or unexpected child processes when documents are opened. Until patched, open untrusted documents in Protected View and treat email-delivered RTF/DOCX attachments as untrusted. | 7.8 | 93% | KEV ransomware PoC ×3 |
| masshundreds of millions of Office users at time of disclosure (vulnerable Equation Editor shipped by default with Office 2007-2016); largely patched today, with… | |
| CVE-2019-13272 | Local Privilege Escalation to Root in Linux Kernel ptrace (pkexec PTRACE_TRACEME) CVE-2019-13272 is an improper privilege management flaw in the Linux kernel's ptrace_link function (kernel/ptrace.c), present in kernels before 5.1.17, in which the credentials of a process requesting a ptrace relationship are mishandled. A local attacker triggers it by stepping into a parent-child process chain where a privileged parent drops privileges and calls execve, typically by abusing Polkit's pkexec helper with PTRACE_TRACEME; contributing factors include an object lifetime issue and incorrect marking of the ptrace relationship as privileged. Successful exploitation grants the attacker full root-level privileges on the host, and the object lifetime bug can in some cases cause a system panic. Any Linux system running an unpatched kernel is affected, spanning the upstream kernel and distributions such as Debian, Fedora, Ubuntu, Red Hat Enterprise Linux and its variants, as well as NetApp AFF A700s firmware. The flaw is in CISA's Known Exploited Vulnerabilities catalog (added 2021-12-10), has multiple public proof-of-concept exploits, and carries a high exploitation probability (EPSS ~52%), so defenders should treat it as an active exploitation risk. Do: Upgrade the Linux kernel to 5.1.17 or later, or install the backported kernel update from your distribution (Debian, Ubuntu, Fedora, Red Hat) and NetApp's fixed firmware for AFF A700s, per CISA's required action to apply vendor updates. Where patching is delayed, SELinux with deny_ptrace may serve as a usable mitigation in some environments. Prioritize hosts that expose local shells to untrusted users and that have Polkit's pkexec installed, and verify the running kernel version (not just the installed package) on each system. | 7.8 | 52% | KEV PoC ×5 |
| masstens of millions of installations (Linux hosts on unpatched kernels across servers, cloud instances, desktops and embedded devices) | |
| CVE-2021-22555 | Linux Kernel Netfilter Heap OOB Write Enables Privilege Escalation (CVE-2021-22555) CVE-2021-22555 is a heap out-of-bounds write (CWE-787) in the netfilter x_tables code (net/netfilter/x_tables.c) of the Linux kernel, a flaw present since version v2.6.19-rc1. A local attacker can trigger the heap memory corruption through user namespaces, meaning even unprivileged users, such as workloads running inside containers, can reach the vulnerable code path. Successful exploitation lets the attacker gain elevated kernel-level privileges, typically fully escaping a container, or crash the system in a denial of service. Affected users are essentially any Linux deployment on kernels in the affected range (distributions, cloud servers, container hosts), and CISA's product mapping additionally covers NetApp firmware for its c400/c250, H300S/H410S/H410C/H500S/H700S, FAS 8300/8700 and AFF A400 systems plus Brocade Fabric OS. The flaw has public proof-of-concept exploits (including Google security research), a high 78.7% EPSS exploitation probability over 30 days, and CISA added it to the Known Exploited Vulnerabilities catalog on 2025-10-06, confirming exploitation in the wild. Do: Upgrade Linux kernels to patched versions from your distribution and apply vendor live patches where offered (Ubuntu Kernel Live Patch notices LSN-0080/0081/0083 are referenced in public advisories), and install the corresponding NetApp and Brocade firmware updates for the listed systems. Where patching must wait, restrict creation of unprivileged user namespaces and limit unprivileged users' ability to configure netfilter rules. As a CISA KEV entry, federal agencies must remediate per BOD 22-01 by the catalog due date. | 7.8 | 79% | KEV PoC ×5 |
| massbillions of devices (Linux kernel runs on most servers, cloud instances, container hosts, Android devices and embedded systems) | |
| CVE-2022-0847 | Local Privilege Escalation ('Dirty Pipe') in the Linux Kernel CVE-2022-0847, widely known as 'Dirty Pipe,' is a privilege escalation flaw in the Linux kernel caused by improper initialization of the 'flags' member of the new pipe buffer structure in the copy_page_to_iter_pipe and push_pipe functions, allowing stale flag values to persist (CWE-665). An unprivileged local user can trigger the flaw by writing through a pipe into the page cache of files they can read, overwriting the contents of otherwise read-only files. This enables tampering with privileged files — for example, hijacking SUID binaries per the public proof-of-concepts — to escalate privileges to root on the local system. Affected products include the Linux kernel as tracked by CISA, with downstream distribution and appliance vendors Fedora, Red Hat Enterprise Linux (including EUS, IBM Z, Power little-endian, and Real Time/NFV variants), oVirt, NetApp, Siemens, and SonicWall. Exploitation is confirmed in the wild: the flaw is on CISA's Known Exploited Vulnerabilities catalog (added 2022-04-25), carries an 89.7% EPSS probability of exploitation within 30 days, and multiple public proof-of-concept exploits are available. Do: Apply vendor-supplied fixed kernel updates immediately per the CISA KEV required action, including patches from Fedora and Red Hat Enterprise Linux (all listed variants) and from oVirt, NetApp, Siemens, and SonicWall appliances or products that embed affected kernels; verify the running kernel version on hosts, container hosts, and appliances and reboot into the patched kernel. There is no complete workaround — the kernel itself must be patched — so prioritize multi-user servers, systems running untrusted code or containers, and internet-exposed appliances, since any local account can gain root. | 7.8 | 90% | KEV PoC ×4 |
| mass≈1 billion+ Linux-based systems (servers, cloud VMs, Android/embedded devices) potentially vulnerable on unpatched kernels | |
| CVE-2023-32233 | In the Linux kernel through 6.3.1, a use-after-free in Netfilter nf_tables when processing batch requests can be abused to perform arbitrary read and write oper In the Linux kernel through 6.3.1, a use-after-free in Netfilter nf_tables when processing batch requests can be abused to perform arbitrary read and write operations on kernel memory. Unprivileged local users can obtain root privileges. This occurs because anonymous sets are mishandled. NVD description · AI analysis pending | 7.8 | 13% |
| — | ||
| CVE-2023-38831 | Code Execution in RARLAB WinRAR via Crafted ZIP File/Folder Name Confusion RARLAB WinRAR before 6.23 mishandles ZIP archives that contain a benign file (such as a JPG) alongside a folder with the same name, causing the folder's contents - which can include malicious executable files - to be processed when the user merely attempts to view the benign file. By sending a crafted ZIP archive, an attacker gains arbitrary code execution on the victim's machine with the user's privileges. Because the flaw is local (AV:L) and requires user interaction, risk is limited to Windows systems running an unpatched copy of WinRAR, while machines without the tool are unaffected. The bug was actively exploited in the wild from April through October 2023, including by government-backed actors (APT28), SideCopy attacks on Indian government entities, ransomware operations, and trading-account theft campaigns, and it was added to CISA's Known Exploited Vulnerabilities catalog on 2023-08-24. Do: Upgrade all Windows systems running WinRAR to version 6.23 or later, which fixes this flaw; if patching is not immediately possible, treat ZIP files from untrusted sources with caution and check archives for duplicate file/folder names before opening. Given KEV listing with known ransomware use and public proof-of-concept exploits, hunt for compromise by reviewing whether unexpected executables or scripts ran when ZIP archives were opened, and apply vendor mitigations per CISA's required action or discontinue use if mitigations are unavailable. | 7.8 | 98% | KEV ransomware PoC ×4 |
| masshundreds of millions of users/installations worldwide (WinRAR is one of the most widely installed Windows archive utilities) | |
| CVE-2025-6218 | Directory Traversal RCE in RARLAB WinRAR RARLAB WinRAR contains a directory traversal flaw (CWE-22) in its handling of file paths within archive files, allowing a crafted archive path to traverse to unintended directories during extraction. Exploitation requires user interaction: the target must open a malicious file (e.g., a booby-trapped archive) or visit a malicious page. A successful attacker executes arbitrary code in the context of the current user, yielding full high-impact code execution on the endpoint (CVSS 3.0: 7.8, local attack vector with required user interaction). Any installation running an affected version of RARLAB WinRAR is exposed; the specific affected version range is not stated in the source data, so defenders should confirm against RARLAB's advisory. The flaw is being actively exploited: CISA added it to the Known Exploited Vulnerabilities catalog on 2025-12-09, Google warned of active exploitation, public reporting ties the campaign to APT-C-08 and at least one other actor group, and EPSS stands at 90.5%. Do: Update WinRAR to the latest vendor release that addresses CVE-2025-6218 per RARLAB's advisory (the fixed version number is not provided in the source data), and treat this as urgent given the KEV listing and 90.5% EPSS. Warn users not to open archives from untrusted or unexpected sources, and inspect email-borne .rar/.zip attachments. Hunt for unusual child processes or file writes outside expected directories following archive extraction, and note U.S. federal civilian agencies must apply mitigations under BOD 22-01. | 7.8 | 91% | KEV PoC ×2 |
| masshundreds of millions of users/installations worldwide | |
| CVE-2025-8088 | WinRAR Path Traversal (CVE-2025-8088) Enables Arbitrary Code Execution A path traversal flaw (CWE-35) in the Windows version of WinRAR allows attackers to achieve arbitrary code execution by delivering a specially crafted archive file that writes outside the expected location when it is opened or processed. Because the CVSS 4.0 vector indicates a local attack requiring user interaction, victims are typically infected by extracting or previewing a malicious archive received via phishing, a malicious download, or another delivery channel. A successful attacker gains the privileges of the user running WinRAR, providing an initial foothold that has been used for both espionage and ransomware operations. Anyone running the Windows version of WinRAR — one of the most widely deployed Windows desktop utilities — is affected, and CPE data additionally lists dtSearch as an affected vendor. Exploitation is confirmed in the wild by nation-state actors (e.g., the China-linked Amaranth-Dragon group per related reporting) and criminal actors including ransomware operators; the flaw was added to CISA's Known Exploited Vulnerabilities catalog on 2025-08-12 and carries a near-maximal 94.6% EPSS score. Do: Update WinRAR to the latest patched release from RARLAB on all Windows endpoints, prioritizing remediation per CISA KEV and BOD 22-01 requirements, and verify that dtSearch deployments bundling the affected component are also updated. Because exploitation requires a user to open or extract a crafted archive, warn users to treat unexpected archive files delivered by email or download with suspicion. Given confirmed ransomware use, hunt across user workstations — not just exposed servers — for suspicious archive-based infections and confirm the patched WinRAR version is installed. | 8.4 | 95% | KEV ransomware |
| masshundreds of millions of Windows users/devices (est.; RARLAB has historically claimed user counts in the hundreds of millions) | |
| CVE-2026-21509 | Local Security Feature Bypass in Microsoft Office Under Active Exploitation CVE-2026-21509 is a security feature bypass in Microsoft Office caused by reliance on untrusted input when making a security decision (CWE-807): Office trusts attacker-controlled data when deciding whether a protection applies, allowing an unauthorized local attacker to bypass that security feature. Exploitation is local and requires user interaction (per the CVSS vector), most plausibly by getting a user to open a crafted file or document, and the flaw carries high confidentiality, integrity, and availability impact. Anyone running Microsoft Office, Microsoft 365 Apps, or Office Long Term Servicing Channel is in scope, giving the flaw a potential audience in the hundreds of millions of seats. The flaw is being actively exploited: it was added to CISA's Known Exploited Vulnerabilities catalog on 2026-01-26, Microsoft issued an emergency patch, and headlines attribute in-the-wild use to Russian state hackers targeting Ukrainian and EU organizations, including the maritime and transport sectors (a related APT28 campaign was tied to a separate Office/MSHTML 0-day, CVE-2026-21513). EPSS estimates a 72.6% probability of exploitation within the next 30 days (99th percentile). Do: Apply Microsoft's emergency Office update and the follow-on February 2026 Patch Tuesday fixes across Microsoft 365 Apps, Office, and Office LTSC, checking Microsoft's advisory for the exact affected builds since no version ranges are given in the source data. Given the KEV listing, federal agencies must patch per CISA BOD 22-01 timelines (or follow cloud-service guidance). Hunt for exploitation per vendor guidance — headlines report Russian state use against EU/Ukrainian and maritime/transport targets — and prioritize endpoints where users open untrusted files. | 7.8 | 73% | KEV |
| masshundreds of millions of users/devices (Office and Microsoft 365 Apps have a global installed base on the order of 10^8+ seats) | |
| CVE-2026-21513 | MSHTML Security Feature Bypass in Windows Exploited in the Wild (CVE-2026-21513) CVE-2026-21513 is a protection mechanism failure (CWE-693) in Microsoft's MSHTML framework, the legacy HTML rendering engine built into Windows and hosted by browsers, Office, and countless applications that display web content. An unauthorized attacker can exploit it over a network to bypass a Windows security feature; the CVSS vector requires user interaction (UI:R), consistent with delivery via a malicious link or document whose content is rendered through MSHTML. Although classified as a security-feature bypass, the vendor-scored impact is high for confidentiality, integrity, and availability (C:H/I:H/A:H), indicating significant downstream effect when chained with other techniques. All supported Windows client and server releases are in scope, from Windows 10 1607 through Windows 11 25H2 and Windows Server 2012 through Windows Server 2022 23H2. The flaw is being actively exploited: CISA added it to the KEV catalog on 2026-02-10, Microsoft confirmed in-the-wild exploitation, and public reporting ties exploitation to APT28 ahead of the February 2026 Patch Tuesday; EPSS assigns a 15.6% probability of exploitation within 30 days (97th percentile). Do: Apply Microsoft's February 2026 Windows security updates to all in-scope Windows 10, Windows 11, and Windows Server versions as soon as possible; the flaw is KEV-listed and confirmed exploited in the wild (reporting ties it to APT28), making patching a priority even though ransomware use is not yet confirmed. Because the vector requires user interaction and MSHTML is reached through rendered content, strengthen email and web-lure defenses and hunt for APT28 activity on unpatched hosts; US federal agencies must apply vendor mitigations per BOD 22-01 or discontinue use if mitigations are unavailable. | 8.8 | 16% | KEV |
| masshundreds of millions of Windows devices and servers (effectively the entire supported Windows install base, >1 billion devices worldwide) | |
| CVE-2026-21514 | Actively Exploited Security Feature Bypass in Microsoft Word (CVE-2026-21514) CVE-2026-21514 is a security feature bypass in Microsoft Word caused by the application relying on untrusted inputs when making a security decision (CWE-807). The flaw carries a local attack vector with a user-interaction requirement, so it is most plausibly triggered when a user opens attacker-supplied content, such as a crafted document, on a system running Word. A local, unauthorized attacker who exploits it can circumvent a Word security feature, with high-impact confidentiality, integrity, and availability effects on the local system; bypasses of this type are commonly chained with other flaws for deeper compromise. Any organization running Microsoft 365 Apps or Office Long Term Servicing Channel (LTSC) is affected. CISA added the bug to the Known Exploited Vulnerabilities catalog on 2026-02-10, confirming exploitation in the wild, though no public proof-of-concept is known and EPSS currently estimates a 1.5% chance of exploitation in the next 30 days (73rd percentile). Do: Apply the February 2026 Patch Tuesday security updates from Microsoft for Microsoft 365 Apps and Office LTSC immediately; fixed version numbers were not provided in the source data, so use Microsoft's release guidance to confirm builds. Because the flaw is in CISA KEV, federal agencies must satisfy BOD 22-01 by applying the update (or directed mitigations) within the mandated weeks, and all organizations should prioritize endpoints that open untrusted documents. Until patched, consider Office hardening such as marking files from the internet as untrusted in Word and watching for anomalous document-driven local activity. | 7.8 | 2% | KEV |
| masshundreds of millions of users (Word is bundled in Microsoft 365 and Office across most enterprise desktop fleets) |
Full article1,952 words · extracted from securelist.com · click to collapse
During Q1 2026, the exploit kits leveraged by threat actors to target user systems expanded once again, incorporating new exploits for the Microsoft Office platform, as well as Windows and Linux operating systems.
In this report, we dive into the statistics on published vulnerabilities and exploits, as well as the known vulnerabilities leveraged by popular C2 frameworks throughout Q1 2026.
Statistics on registered vulnerabilities
This section provides statistical data on registered vulnerabilities. The data is sourced from cve.org.
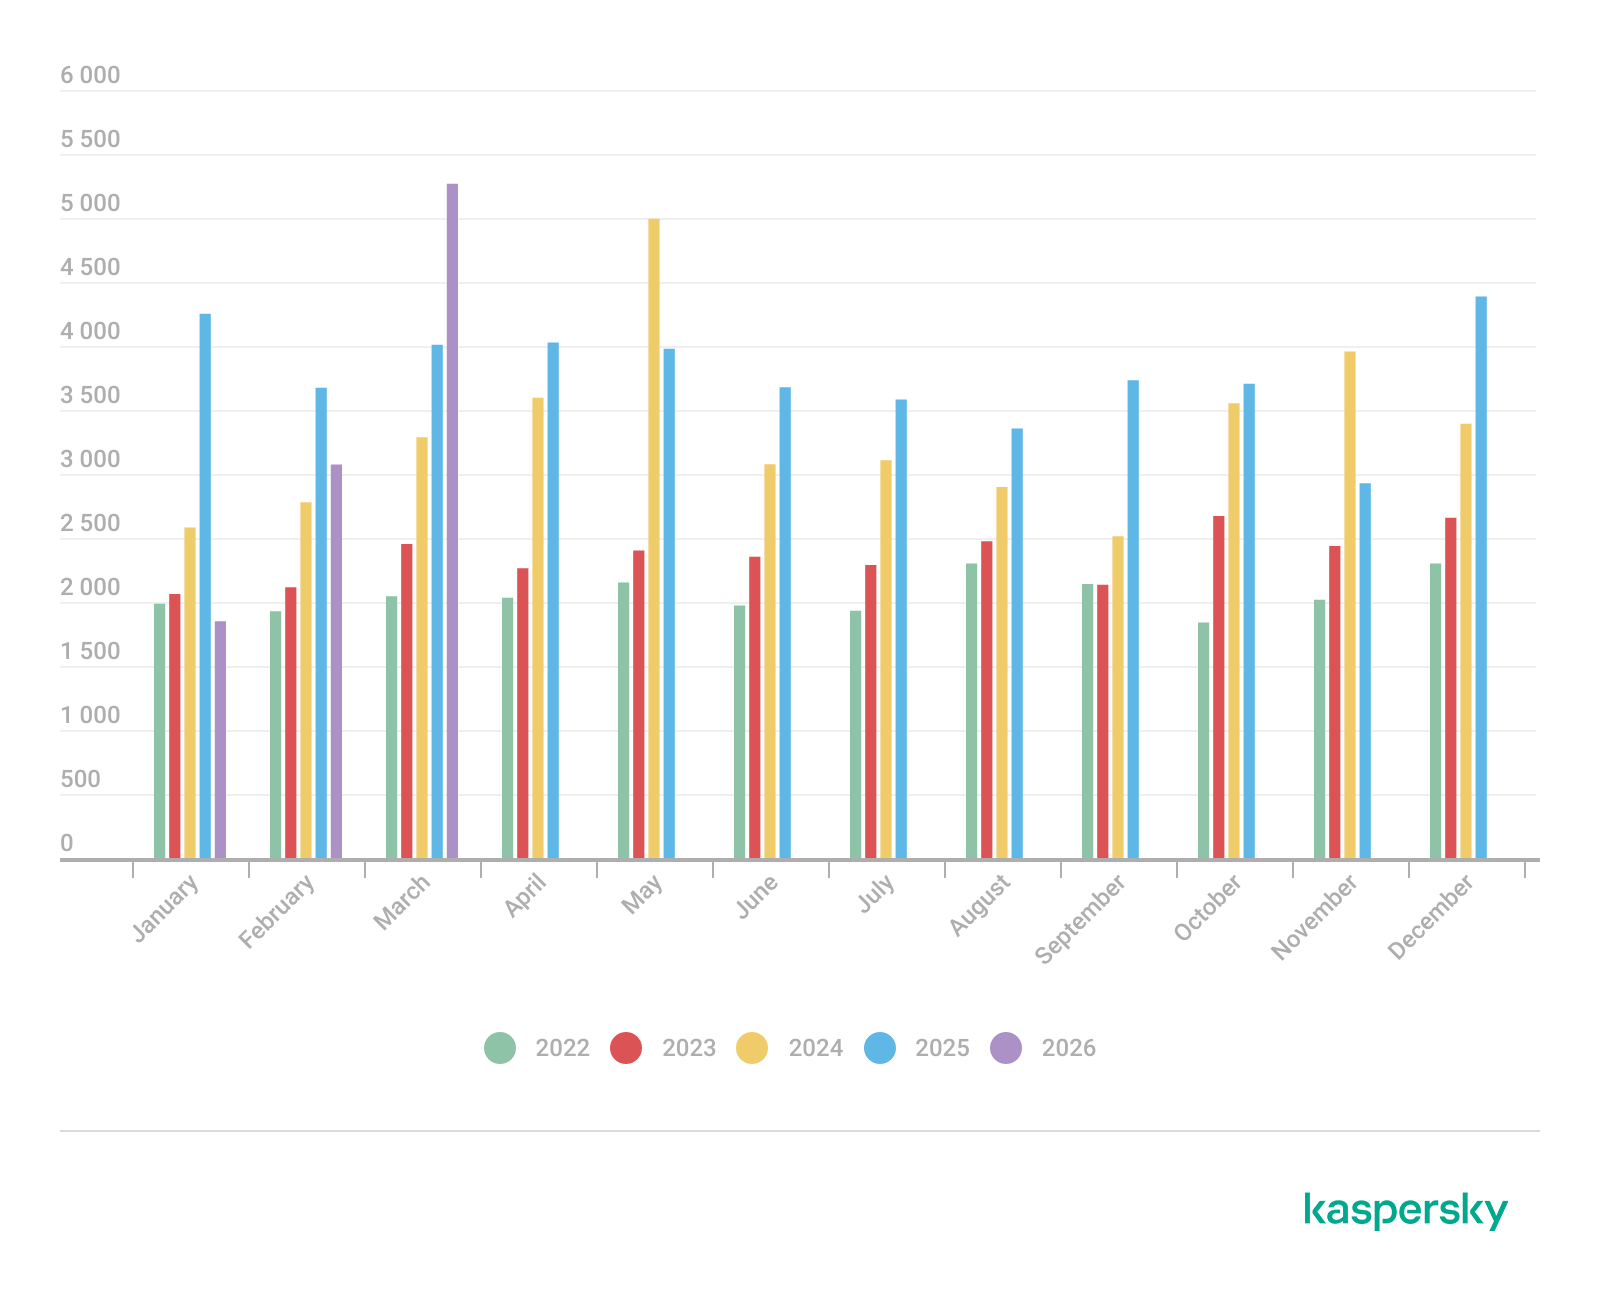
We examine the number of registered CVEs for each month starting from January 2022. The total volume of vulnerabilities continues rising and, according to current reports, the use of AI agents for discovering security issues is expected to further reinforce this upward trend.
Total published vulnerabilities per month from 2022 through 2026 (download)
Next, we analyze the number of new critical vulnerabilities (CVSS > 8.9) over the same period.
Total critical vulnerabilities published per month from 2022 through 2026 (download)
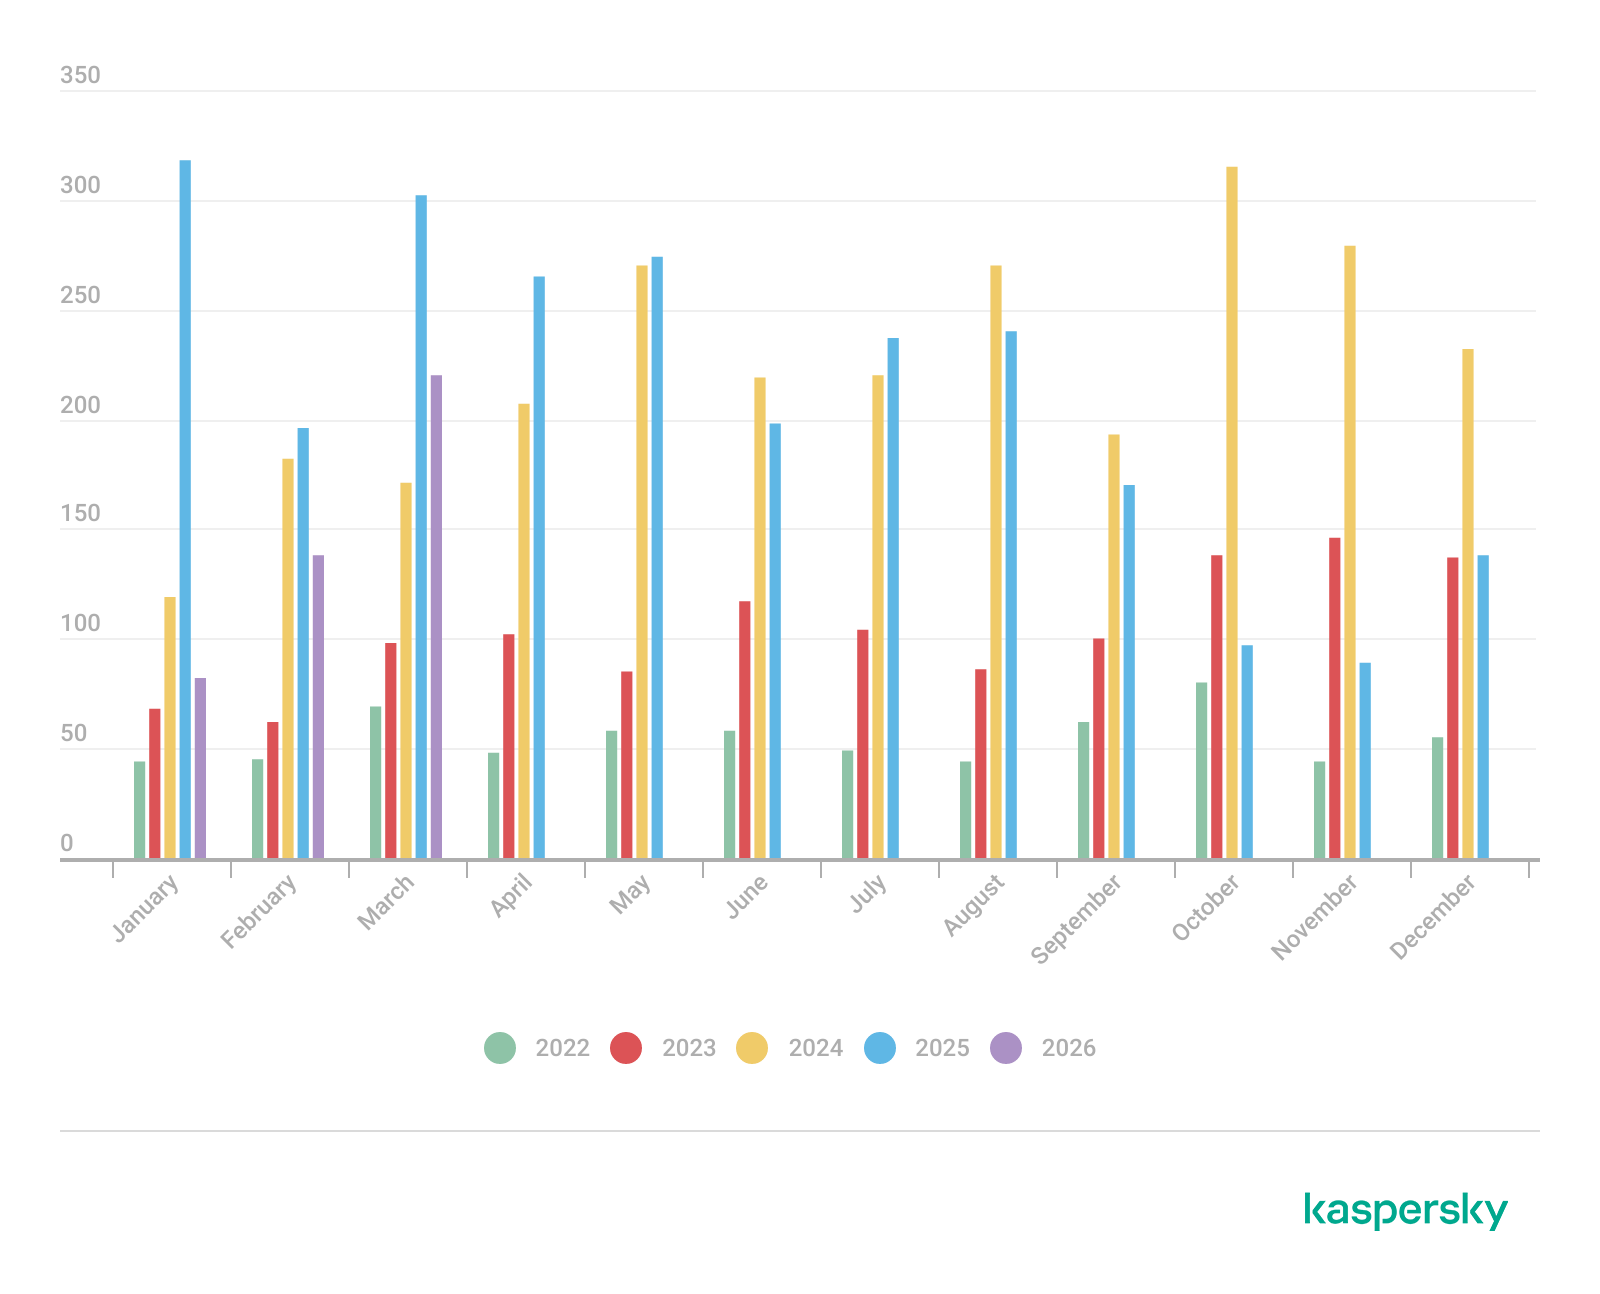
The graph indicates that while the volume of critical vulnerabilities slightly decreased compared to previous years, an upward trend remained clearly visible. At present, we attribute this to the fact that the end of last year was marked by the disclosure of several severe vulnerabilities in web frameworks. The current growth is driven by high-profile issues like React2Shell, the release of exploit frameworks for mobile platforms, and the uncovering of secondary vulnerabilities during the remediation of previously discovered ones. We will be able to test this hypothesis in the next quarter; if correct, the second quarter will show a significant decline, similar to the pattern observed in the previous year.
Exploitation statistics
This section presents statistics on vulnerability exploitation for Q1 2026. The data draws on open sources and our telemetry.
Windows and Linux vulnerability exploitation
In Q1 2026, threat actor toolsets were updated with exploits for new, recently registered vulnerabilities. However, we first examine the list of veteran vulnerabilities that consistently account for the largest share of detections:
- CVE-2018-0802: a remote code execution (RCE) vulnerability in the Equation Editor component
- CVE-2017-11882: another RCE vulnerability also affecting Equation Editor
- CVE-2017-0199: a vulnerability in Microsoft Office and WordPad that allows an attacker to gain control over the system
- CVE-2023-38831: a vulnerability resulting from the improper handling of objects contained within an archive
- CVE-2025-6218: a vulnerability allowing the specification of relative paths to extract files into arbitrary directories, potentially leading to malicious command execution
- CVE-2025-8088: a directory traversal bypass vulnerability during file extraction utilizing NTFS Streams
Among the newcomers, we have observed exploits targeting the Microsoft Office platform and Windows OS components. Notably, these new vulnerabilities exploit logic flaws arising from the interaction between multiple systems, making them technically difficult to isolate within a specific file or library. A list of these vulnerabilities is provided below:
- CVE-2026-21509 and CVE-2026-21514: security feature bypass vulnerabilities: despite Protected View being enabled, a specially crafted file can still execute malicious code without the user’s knowledge. Malicious commands are executed on the victim’s system with the privileges of the user who opened the file.
- CVE-2026-21513: a vulnerability in the Internet Explorer MSHTML engine, which is used to open websites and render HTML markup. The vulnerability involves bypassing rules that restrict the execution of files from untrusted network sources. Interestingly, the data provider for this vulnerability was an LNK file.
These three vulnerabilities were utilized together in a single chain during attacks on Windows-based user systems. While this combination is noteworthy, we believe the widespread use of the entire chain as a unified exploit will likely decline due to its instability. We anticipate that these vulnerabilities will eventually be applied individually as initial entry vectors in phishing campaigns.
Below is the trend of exploit detections on user Windows systems starting from Q1 2025.
Dynamics of the number of Windows users encountering exploits, Q1 2025 – Q1 2026. The number of users who encountered exploits in Q1 2025 is taken as 100% (download)
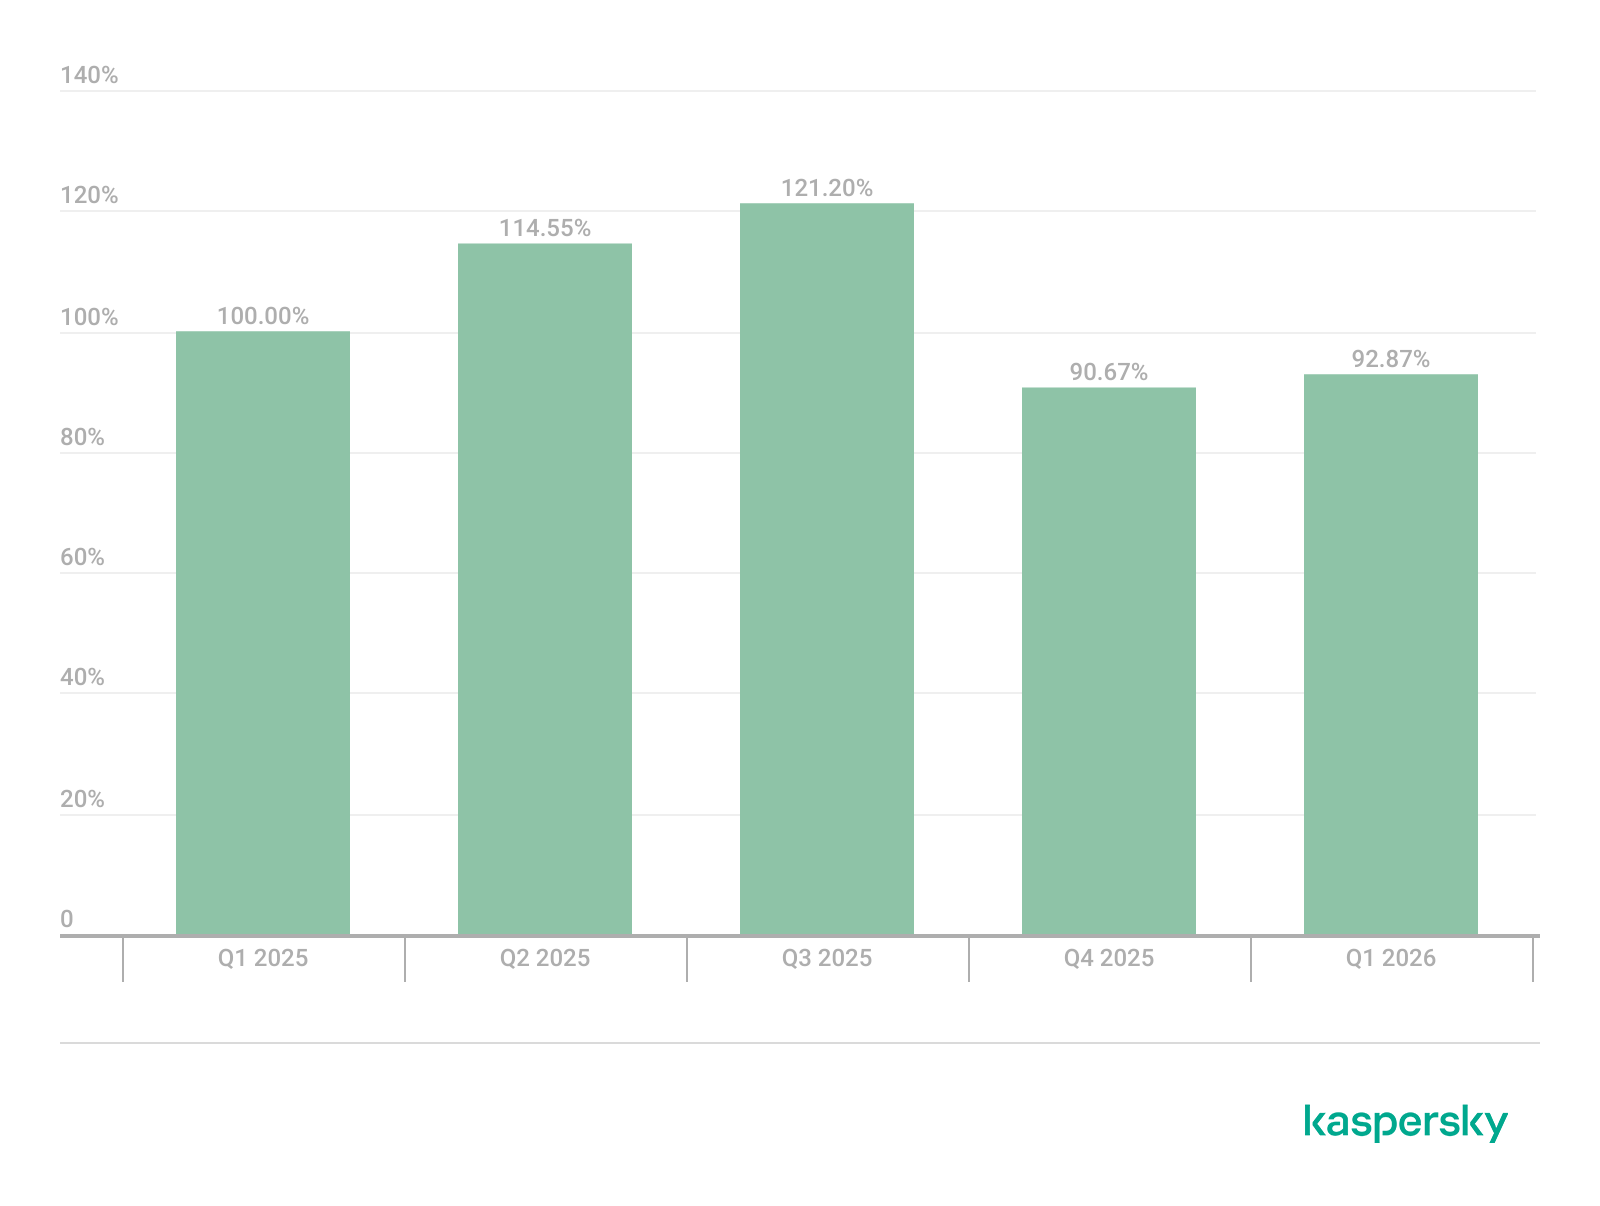
The vulnerabilities listed here can be leveraged to gain initial access to a vulnerable system and for privilege escalation. This underscores the critical importance of timely software updates.
On Linux devices, exploits for the following vulnerabilities were detected most frequently:
- CVE-2022-0847: a vulnerability known as Dirty Pipe, which enables privilege escalation and the hijacking of running applications
- CVE-2019-13272: a vulnerability caused by improper handling of privilege inheritance, which can be exploited to achieve privilege escalation
- CVE-2021-22555: a heap out-of-bounds write vulnerability in the Netfilter kernel subsystem
- CVE-2023-32233: a vulnerability in the Netfilter subsystem that allows for Use-After-Free conditions and privilege escalation through the improper processing of network requests
Dynamics of the number of Linux users encountering exploits, Q1 2025 – Q1 2026. The number of users who encountered exploits in Q1 2025 is taken as 100% (download)
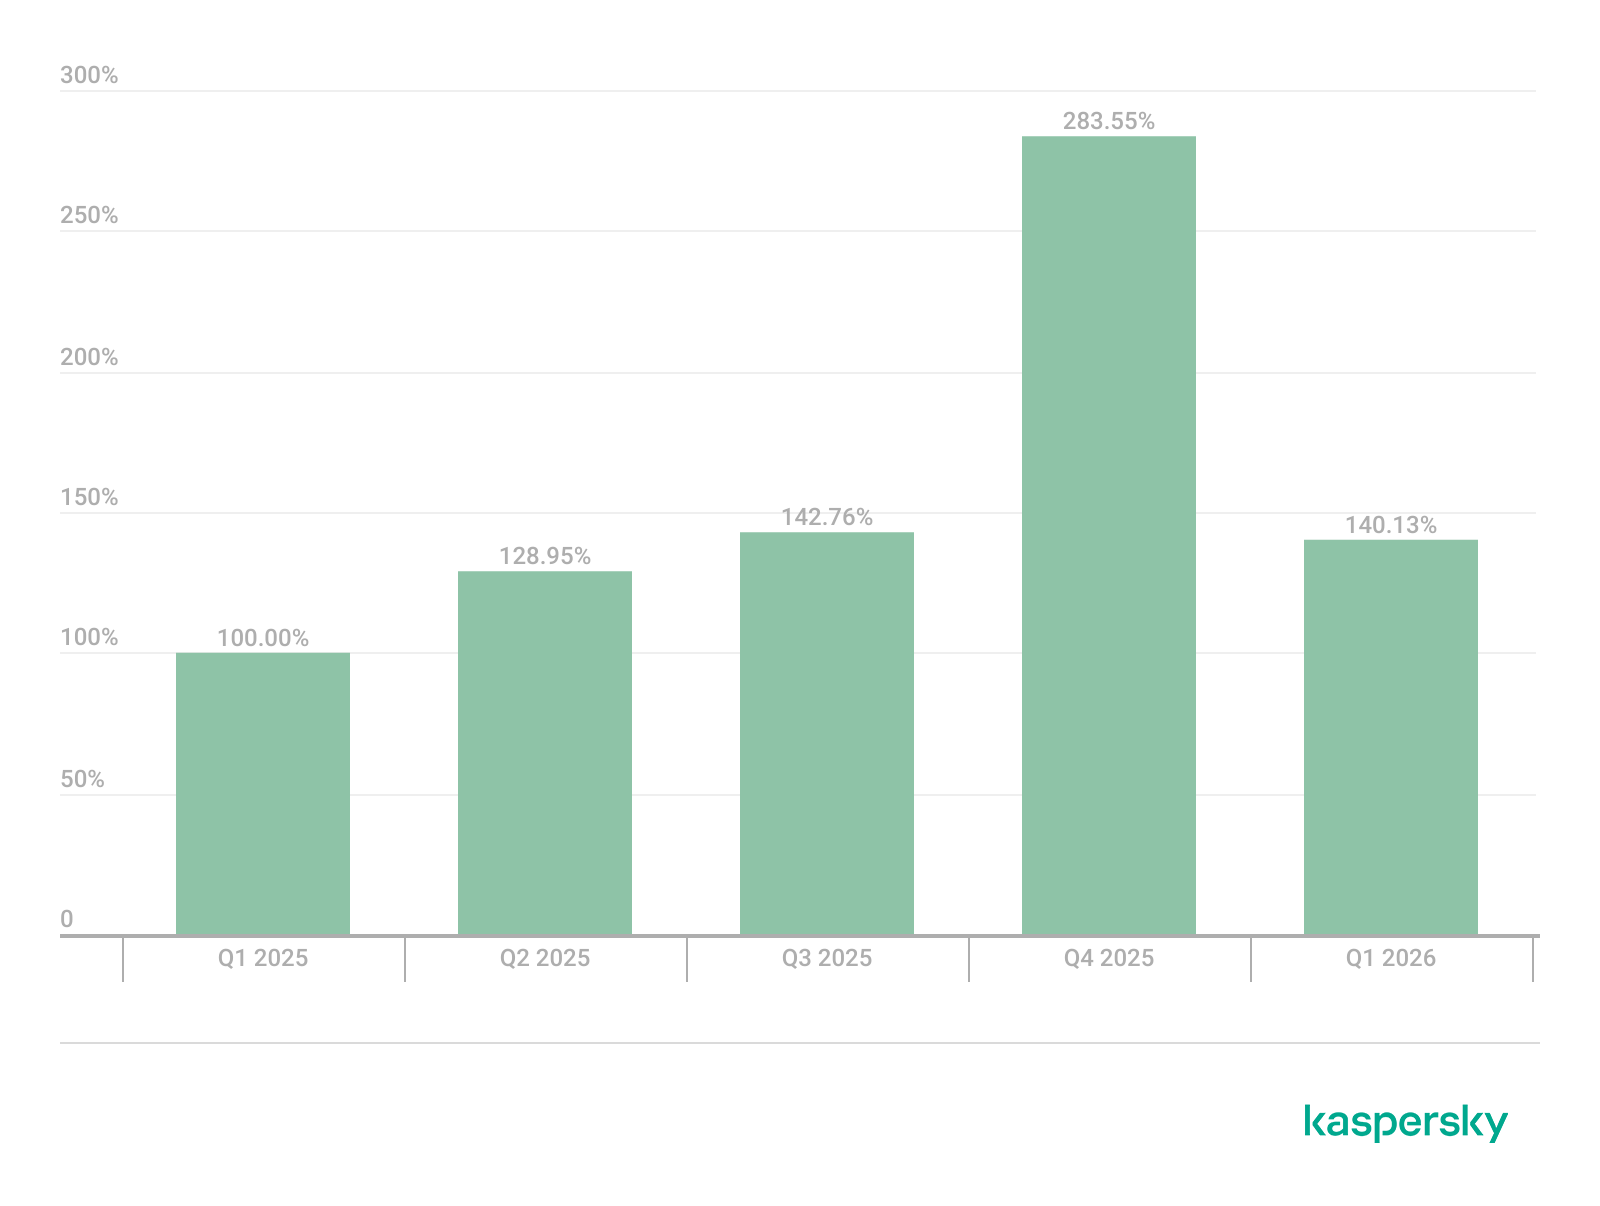
In the first quarter of 2026, we observed a decrease in the number of detected exploits; however, the detection rates are on the rise relative to the same period last year. For the Linux operating system, the installation of security patches remains critical.
Most common published exploits
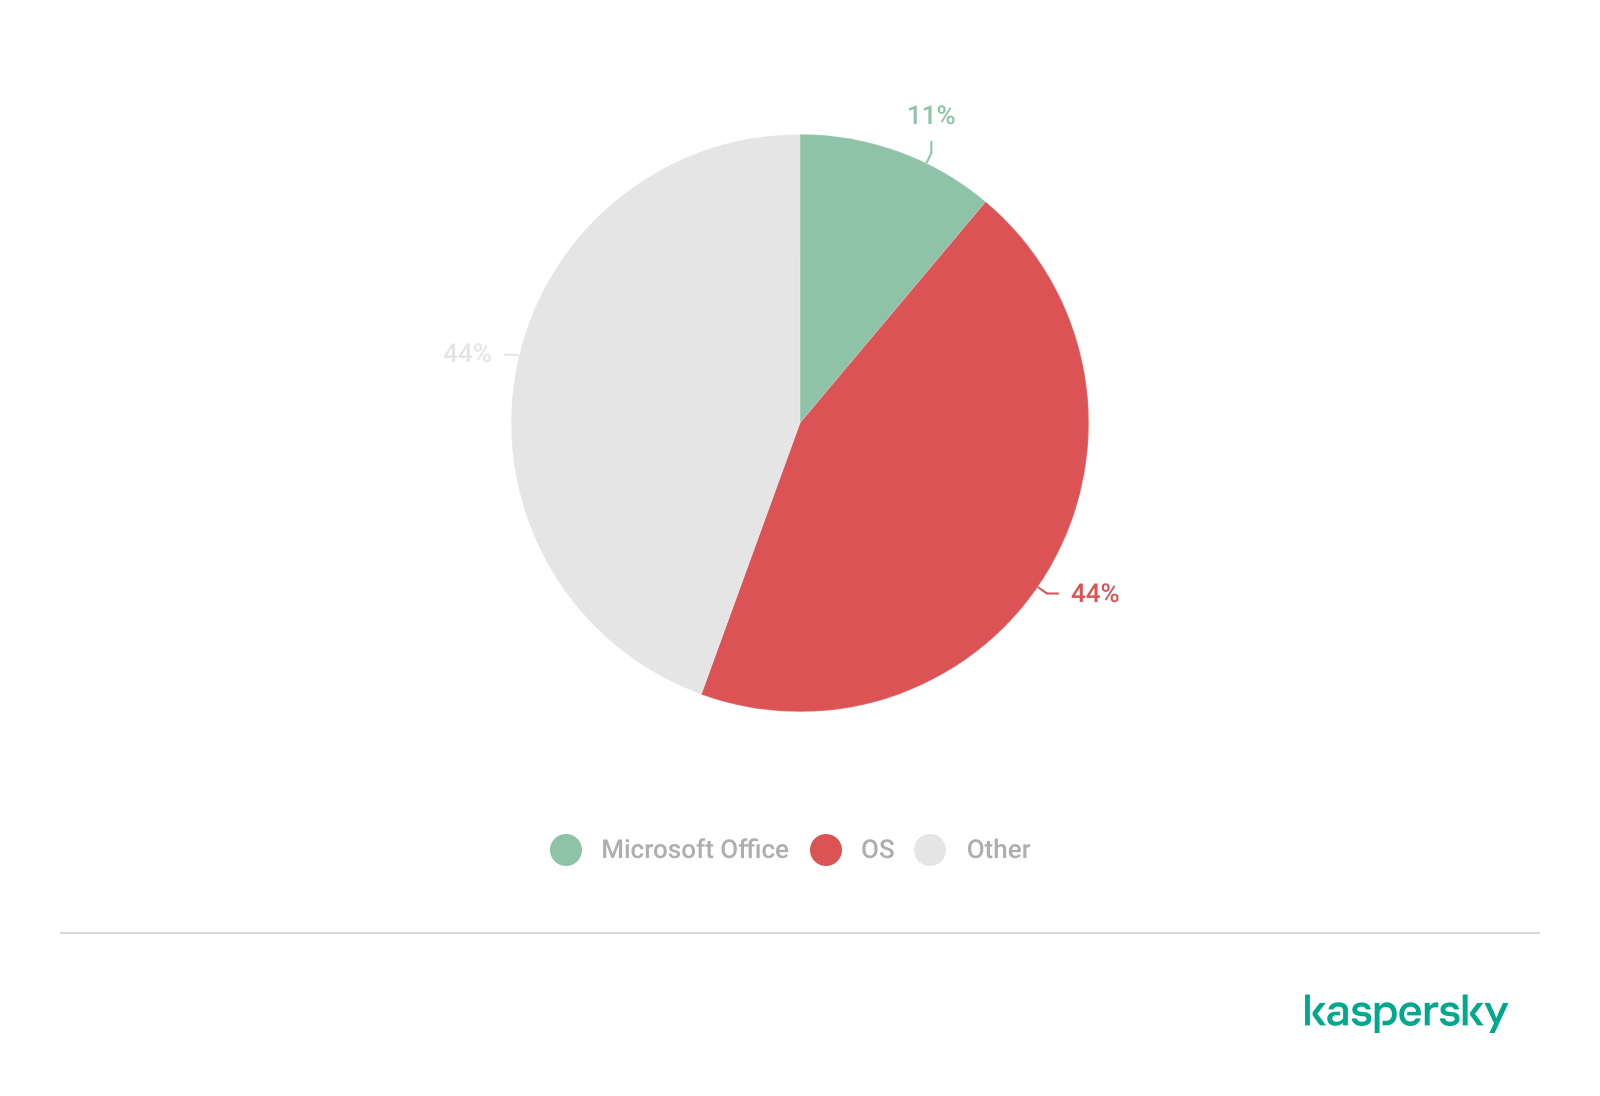
The distribution of published exploits by software type in Q1 2026 features an updated set of categories; once again, we see exploits targeting operating systems and Microsoft Office suites.
Distribution of published exploits by platform, Q1 2026 (download)
Vulnerability exploitation in APT attacks
We analyzed which vulnerabilities were utilized in APT attacks during Q1 2026. The ranking provided below includes data based on our telemetry, research, and open sources.
TOP 10 vulnerabilities exploited in APT attacks, Q1 2026 (download)
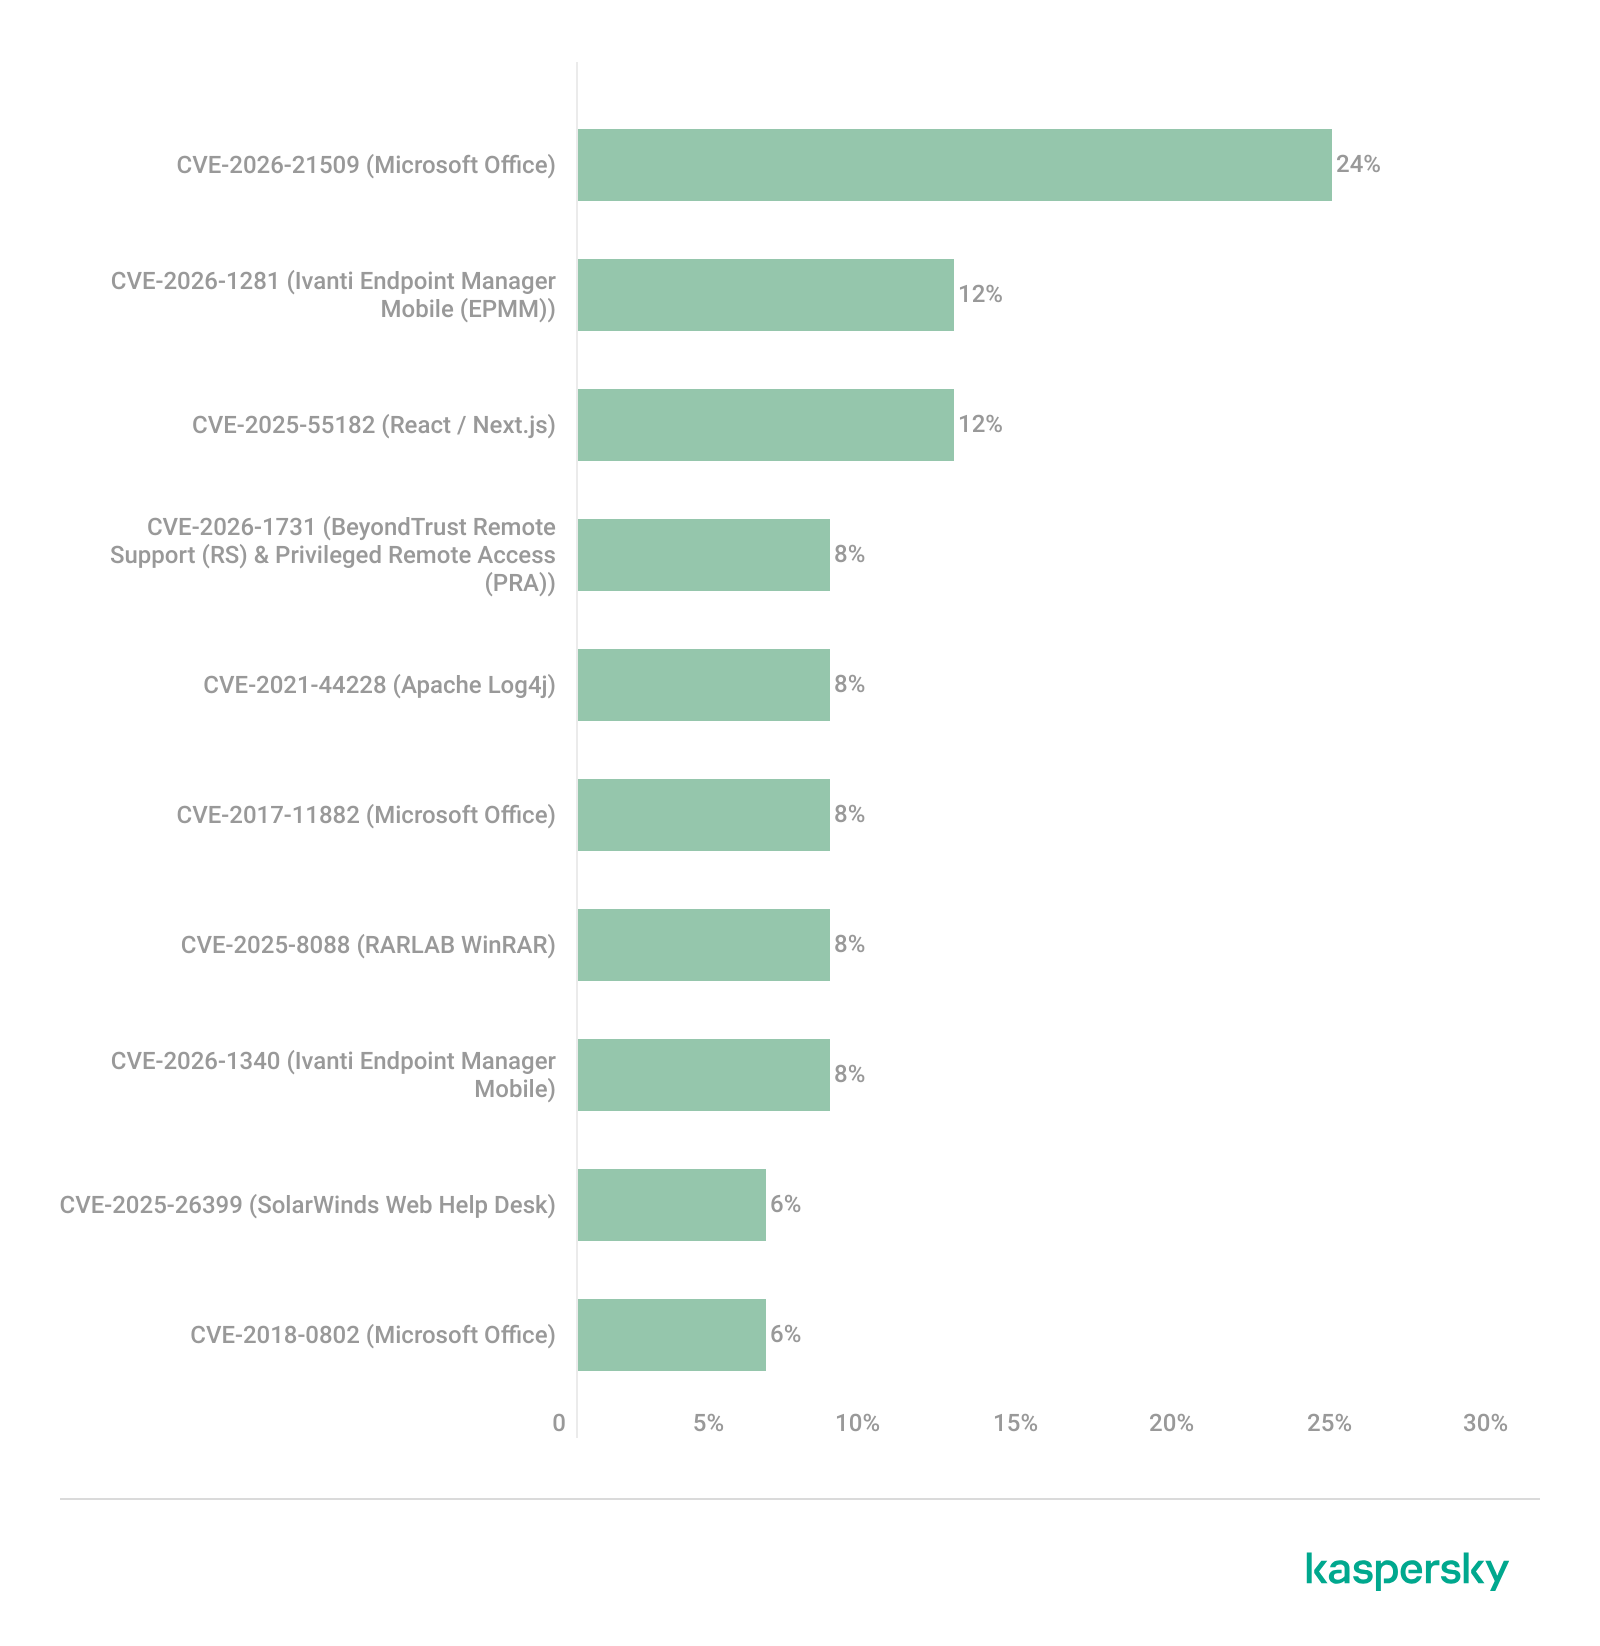
In Q1 2026, threat actors continued to utilize high-profile vulnerabilities registered in the previous year for APT attacks. The hypothesis we previously proposed has been confirmed: security flaws affecting web applications remain heavily exploited in real-world attacks. However, we are also observing a partial refresh of attacker toolsets. Specifically, during the first quarter of the year, APT campaigns leveraged recently discovered vulnerabilities in Microsoft Office products, edge networking device software, and remote access management systems. Although the most recent vulnerabilities are being exploited most heavily, their general characteristics continue to reinforce established trends regarding the categories of vulnerable software. Consequently, we strongly recommend applying the security patches provided by vendors.
C2 frameworks
In this section, we examine the most popular C2 frameworks used by threat actors and analyze the vulnerabilities targeted by the exploits that interacted with C2 agents in APT attacks.
The chart below shows the frequency of known C2 framework usage in attacks against users during Q1 2026, according to open sources.
TOP 10 C2 frameworks used by APTs to compromise user systems, Q1 2026 (download)
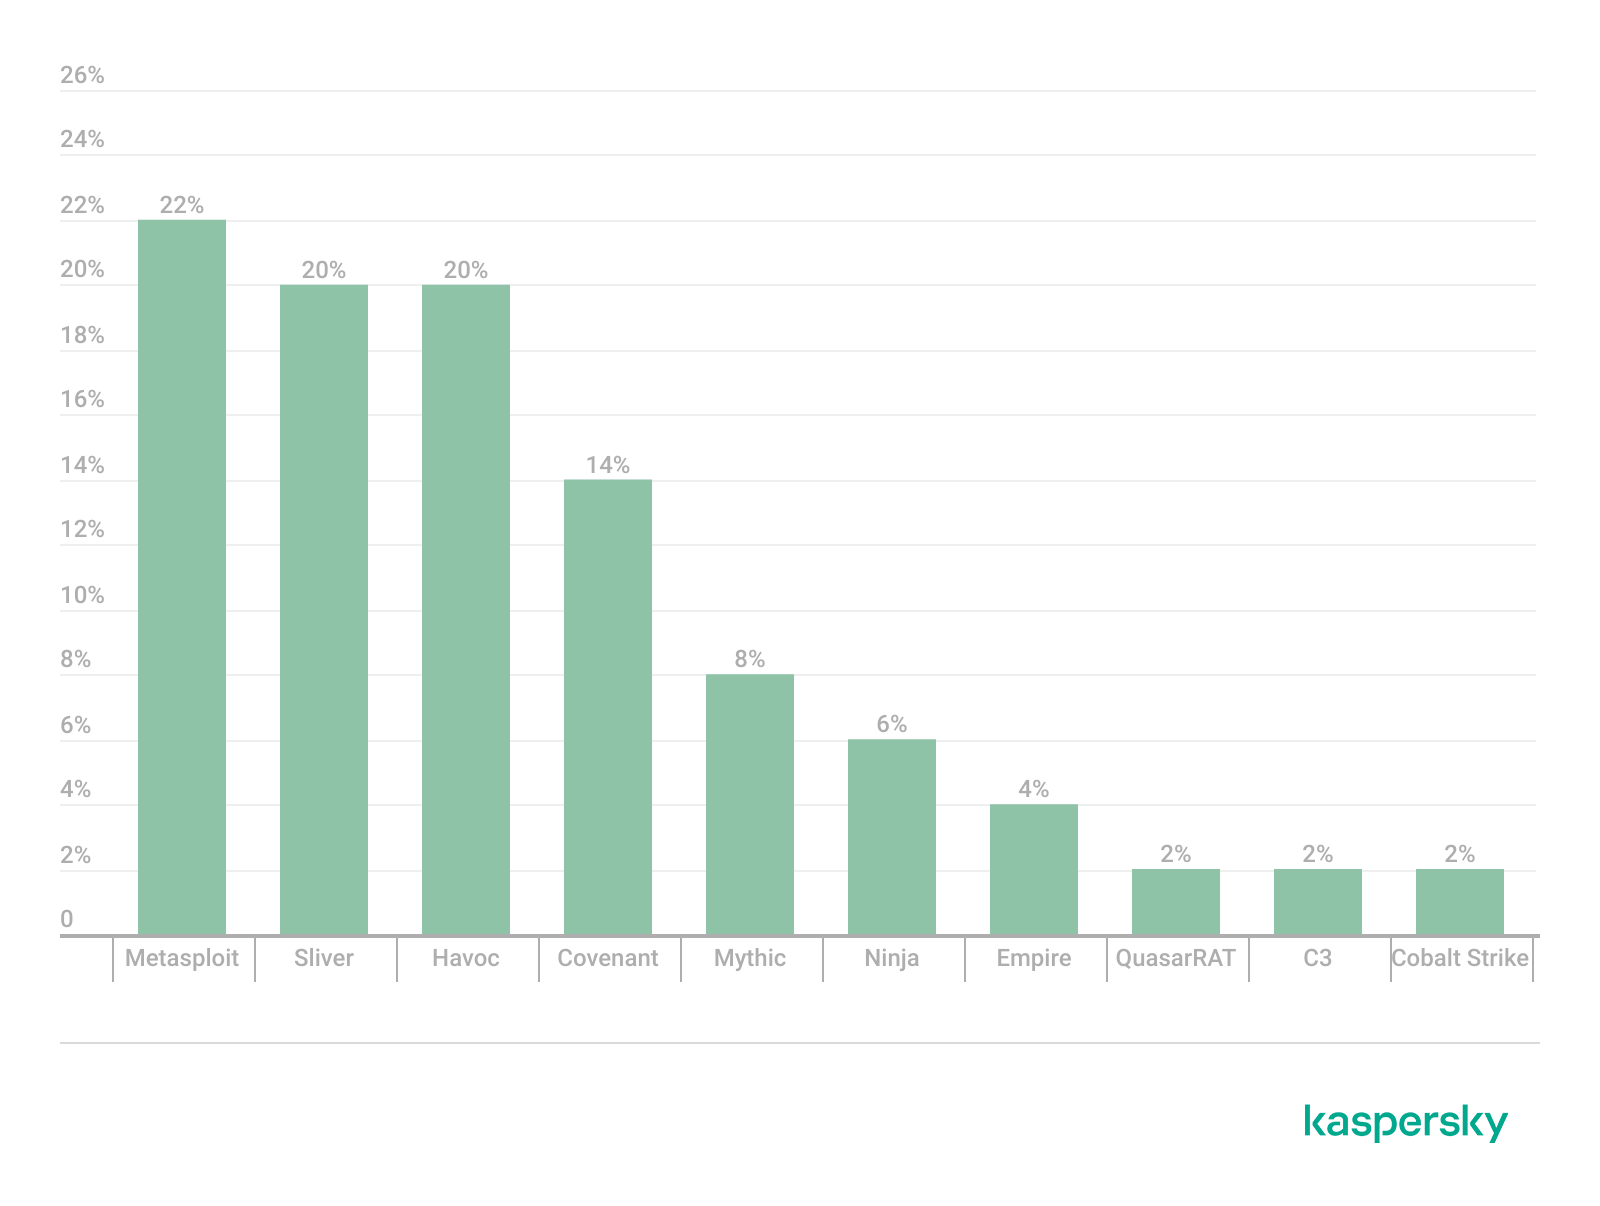
Metasploit has returned to the top of the list of the most common C2 frameworks, displacing Sliver, which now shares the second position with Havoc. These are followed by Covenant and Mythic, the latter of which previously saw greater popularity. After studying open sources and analyzing samples of malicious C2 agents that contained exploits, we determined that the following vulnerabilities were utilized in APT attacks involving the C2 frameworks mentioned above:
- CVE-2023-46604: an insecure deserialization vulnerability allowing for arbitrary code execution within the server process context if the Apache ActiveMQ service is running
- CVE-2024-12356 and CVE-2026-1731: command injection vulnerabilities in BeyondTrust software that allow an attacker to send malicious commands even without system authentication
- CVE-2023-36884: a vulnerability in the Windows Search component that enables command execution on the system, bypassing security mechanisms built into Microsoft Office applications
- CVE-2025-53770: an insecure deserialization vulnerability in Microsoft SharePoint that allows for unauthenticated command execution on the server
- CVE-2025-8088 and CVE-2025-6218: similar directory traversal vulnerabilities that allow files to be extracted from an archive to a predefined path, potentially without the archiving utility displaying any alerts to the user
The nature of the described vulnerabilities indicates that they were exploited to gain initial access to the system. Notably, the majority of these security issues are targeted to bypass authentication mechanisms. This is likely due to the fact that C2 agents are being detected effectively, prompting threat actors to reduce the probability of discovery by utilizing bypass exploits.
Notable vulnerabilities
This section highlights the most significant vulnerabilities published in Q1 2026 that have publicly available descriptions.
CVE-2026-21519: Desktop Window Manager vulnerability
At the core of this vulnerability is a Type Confusion flaw. By attempting to access a resource within the Desktop Window Manager subsystem, an attacker can achieve privilege escalation. A necessary condition for exploiting this issue is existing authorization on the system.
It is worth noting that the DWM subsystem has been under close scrutiny by threat actors for quite some time. Historically, the primary attack vector involves interacting with the NtDComposition* function set.
RegPwn (CVE-2026-21533): a system settings access control vulnerability
CVE-2026-21533 is essentially a logic vulnerability that enables privilege escalation. It stems from the improper handling of privileges within Remote Desktop Services (RDS) components. By modifying service parameters in the registry and replacing the configuration with a custom key, an attacker can elevate privileges to the SYSTEM level. This vulnerability is likely to remain a fixture in threat actor toolsets as a method for establishing persistence and gaining high-level privileges.
CVE-2026-21514: a Microsoft Office vulnerability
This vulnerability was discovered in the wild during attacks on user systems. Notably, an LNK file is used to initiate the exploitation process. CVE-2026-21514 is also a logic issue that allows for bypassing OLE technology restrictions on malicious code execution and the transmission of NetNTLM authentication requests when processing untrusted input.
Clawdbot (CVE-2026-25253): an OpenClaw vulnerability
This vulnerability in the AI agent leaks credentials (authentication tokens) when queried via the WebSocket protocol. It can lead to the compromise of the infrastructure where the agent is installed: researchers have confirmed the ability to access local system data and execute commands with elevated privileges. The danger of CVE-2026-25253 is further compounded by the fact that its exploitation has generated numerous attack scenarios, including the use of prompt injections and ClickFix techniques to install stealers on vulnerable systems.
CVE-2026-34070: LangChain framework vulnerability
LangChain is an open-source framework designed for building applications powered by large language models (LLMs). A directory traversal vulnerability allowed attackers to access arbitrary files within the infrastructure where the framework was deployed. The core of CVE-2026-34070 lies in the fact that certain functions within langchain_core/prompts/loading.py handled configuration files insecurely. This could potentially lead to the processing of files containing malicious data, which could be leveraged to execute commands and expose critical system information or other sensitive files.
CVE-2026-22812: an OpenCode vulnerability
CVE-2026-22812 is another vulnerability identified in AI-assisted coding software. By default, the OpenCode agent provided local access for launching authorized applications via an HTTP server that did not require authentication. Consequently, attackers could execute malicious commands on a vulnerable device with the privileges of the current user.
Conclusion and advice
We observe that the registration of vulnerabilities is steadily gaining momentum in Q1 2026, a trend driven by the widespread development of AI tools designed to identify security flaws across various software types. This trajectory is likely to result not only in a higher volume of registered vulnerabilities but also in an increase in exploit-driven attacks, further reinforcing the critical necessity of timely security patch deployment. Additionally, organizations must prioritize vulnerability management and implement effective defensive technologies to mitigate the risks associated with potential exploitation.
To ensure the rapid detection of threats involving exploit utilization and to prevent their escalation, it is essential to deploy a reliable security solution. Key features of such a tool include continuous infrastructure monitoring, proactive protection, and vulnerability prioritization based on real-world relevance. These mechanisms are integrated into Kaspersky Next, which also provides endpoint security and protection against cyberattacks of any complexity.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/vulnerabilities-and-exploits-in-q1-2026/119733/