COVID-19 hacking extends to supply chain for controlling vaccine temperature, IBM says
Full article858 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The phishing campaign began in September and has targeted organizations in six countries in Europe and Asia, according to IBM.
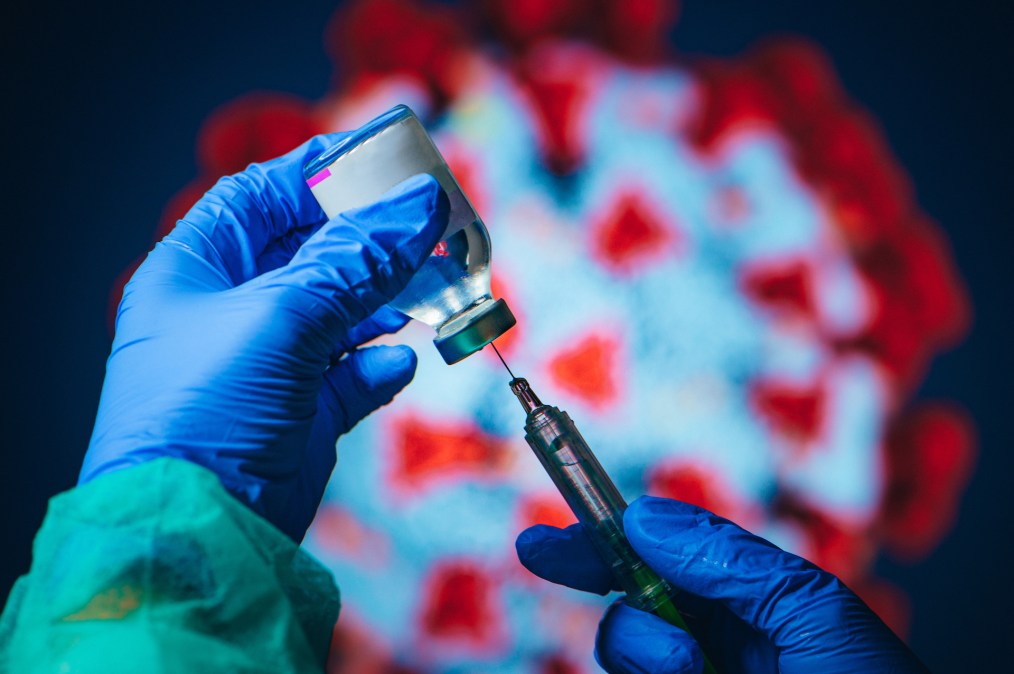
As drug companies turn their attention from the development to the deployment of a coronavirus vaccine, well-resourced hackers are doing the same.
IBM researchers on Thursday revealed a global spearphishing campaign they said was aimed at companies involved in the storage and transport of vaccines in temperature-controlled environments. Those controls allow the medicine to be sent to far-flung places. IBM suspects the attackers are tied to a government, but they said they didn’t have enough evidence to determine which one.
The attackers’ goal may have been to steal login credentials from those companies in order to gain future access “to corporate networks and sensitive information relating to the COVID-19 vaccine distribution,” the researchers said. It’s unclear how successful the phishing has been.
The findings illustrate how virtually every step of the months-long project by drug companies to produce a vaccine has been targeted by hackers. The U.S. government accused Chinese hackers of targeting vaccine research in May, and examples of similar espionage operations tied to North Korea and Russia have also emerged.
The phishing campaign uncovered by IBM began in September and has targeted organizations in six countries in Europe and Asia. All of the organizations appear to be associated with a supply-chain program run by Gavi, an international organization that handles vaccines.
The attackers targeted companies from the energy, manufacturing and software sectors that are supporting the distribution of a vaccine (IBM did not name any of them.) With access to internal communications at such companies, the attackers could gather information on the “infrastructure that governments intend to use to distribute a vaccine to the vendors that will be supplying it,” the IBM researchers said.
“This adversary picked the perfect cover – one that would pass scrutiny and suspicion,” Claire Zaboeva, senior cyber threat analyst at IBM Security X-Force, said in an email.
That cover saw the hackers pose as an executive at Haier Biomedical, a supplier involved in Gavi’s vaccine supply-chain program, and send phishing emails to companies supporting transportation needs for the program. China-based Haier touts itself as “the world’s only complete cold chain provider,” or organization that offers the full range of temperatures needed for storing biomedical equipment.
The Department of Homeland Security’s Cybersecurity and Infrastructure Security Agency on Thursday highlighted the IBM research and urged organizations to guard against the hacking.
“Today’s report highlights the importance of cybersecurity diligence at each step in the vaccine supply chain,” said Josh Corman, CISA’s chief strategist for health care. “CISA encourages all organizations involved in vaccine storage and transport to harden attack surfaces, particularly in cold storage operation, and remain vigilant against all activity in this space.”
More Scoops
Plankey vows to boot China from U.S. supply chain, advocate for CISA budget
But Trump’s pick to lead CISA sidestepped questions about alleged past or future election manipulation claims.
Ransomware gang strikes Iowa agriculture business New Cooperative, the latest hack on food supply chain
White House rolls out pipeline, supply chain security initiatives as companies pledge billions in cyber spending
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/coronavirus-vaccine-hacking-ibm/