SEC's breach disclosure rule raises concerns about tipping off hackers to flawed systems
Full article981 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
New rules require publicly traded companies to disclose cybersecurity breaches within four days of them being deemed material.
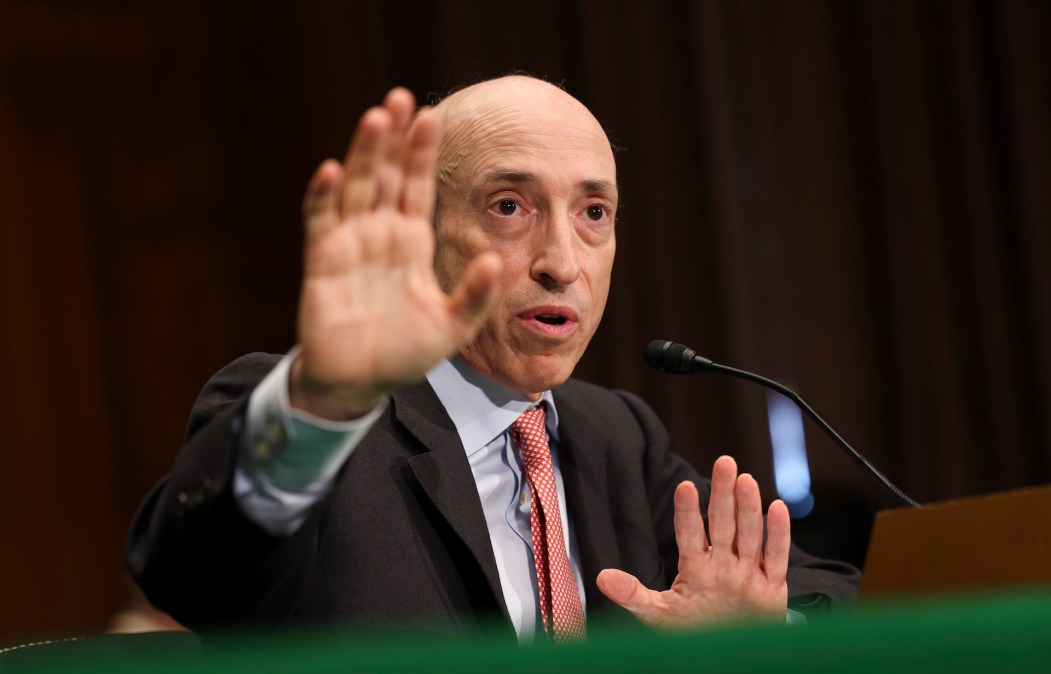
The Securities and Exchange Commission approved rules on Wednesday that will require publicly traded companies to disclose cybersecurity breaches that pose a material risk to a firm’s bottom line.
While many companies already disclose breaches, the SEC’s new rules aim to bring greater transparency and consistency to the information available to investors. “Whether a company loses a factory in a fire — or millions of files in a cybersecurity incident — it may be material to investors,” SEC Chair Gary Gensler said in a statement.
The rules, which are set take effect 30 days after they are published in the Federal Register, require companies to disclose breaches four days after they are deemed material. The disclosure regime represents a potentially major shift in how public companies disclose computer breaches.
Security and legal experts caution that determining what types of breaches are material and require reporting may pose a challenge for some firms and that rushing to alert investors about breaches before they are remedied could put companies at risk.
The public nature of the disclosure and tight timeline is what could expose companies to additional risk, said Harley Geiger, a counsel at the Center for Cybersecurity Policy and Law. While Geiger welcomed regulators’ growing emphasis on disclosure, he said that Wednesday’s rule may have unintended consequences.
Companies are already subject to a patchwork of disclosure requirements, but the SEC’s new rule differs in one marked respect: Breach disclosures will be public in the 8-K forms filed with the commission and made available to investors.
Within four days of determining that a breach is material, “the company may or may not have expelled the attacker and patched the vulnerability or the vector that caused the incident in the first place,” Geiger said. Disclosure of a breach may tip off other attackers to a vulnerable system, and if an attacker remains in an affected system, they may attempt to grab whatever data is available to them or burn down any infrastructure they have access to, he added.
Publicly traded companies are already required to reveal information deemed material to investors, but Wednesday’s rule shortens the timeline for when companies must disclose breaches deemed material and also requires that they provide an annual report on their cybersecurity risk management strategy.
The rules adopted Wednesday include the possibility of extending the timeline of disclosure if the U.S. attorney general determines that disclosure poses a risk to national security or public safety, but during the comment period, U.S. business interests pushed for far greater leniency in the disclosure timeline.
Cybersecurity experts caution that Wednesday’s rules will require firms to overhaul how they think about breaches and that they may be poorly prepared to determine what needs to be disclosed to investors.
“Businesses will have to translate bits and bytes of cyber risk into dollars and cents of ‘material’ business risk,” said Saket Modi, the CEO of Safe Security. “Most organizations are not prepared to comply with the SEC guidelines as they cannot determine materiality.”
More Scoops
What the Hugging Face breach reveals about defense in the age of agentic AI
We almost never get both sides of an intrusion. This time we did. Last month, Hugging Face disclosed a breach into part of its production infrastructure, saying…
Critics call FCC router rule a ‘big swing’ that could create more supply chain uncertainty
Why ‘secure-by-design’ systems are non-negotiable in the AI era
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/sec-cybersecurity-breach-disclosure/