New VPN flaws highlight proven pathway for hackers into industrial organizations
Full article855 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The research comes the week after the NSA and CISA told industrial companies to clamp down on VPN security.
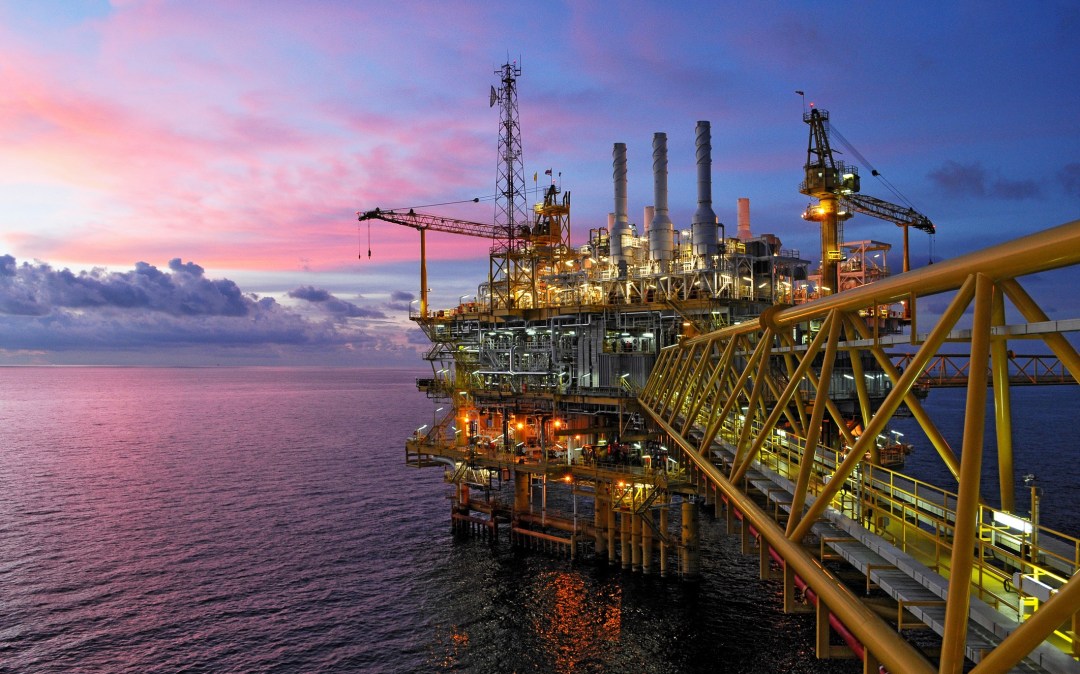
Sometime in the second half of 2019, suspected Iranian hackers started burrowing into the network of an unnamed organization in the Middle East. What likely began, according to investigators, as a breach of a virtual private network application led to a compromise of the organization’s administrative network accounts. It culminated in a data-wiping attack on Dec. 29 that hit most of the machines on the organization’s IT network.
A forensic report on the attack produced by Saudi cybersecurity officials warns industrial companies to secure VPN connections, which employees use for remote connectivity, lest they become a valuable foothold for hackers in search of sensitive data.
Seven months later, with the rise in remote work during the coronavirus pandemic, that advice is even more critical. On Tuesday, researchers from cybersecurity company Claroty drove the point home by publishing data on multiple remote-connectivity products popular in the oil, gas and other industrial sectors. If exploited as part of a larger attack, the researchers say, the bugs in VPN servers and devices could serve as a pathway for going beyond an IT network to access industrial computers that are used to connect to machinery.
Claroty hasn’t seen the vulnerabilities exploited in the wild, but the company said it is withholding some details on the bugs because some affect internet-facing servers.
“We are aware that releasing technical information can help other malicious attackers to exploit the vulnerabilities and put potential customers at risk,” Nadav Erez, the company’s research team lead, told CyberScoop.
The research comes the week after the U.S. National Security Agency and Department of Homeland Security’s cyber division told industrial companies to clamp down on their security by, among other things, ensuring VPN traffic was encrypted.
“Due to the increase in adversary capabilities and activity, the criticality to U.S. national security and way of life, and the vulnerability of OT [operational technology] systems, civilian infrastructure makes attractive targets for foreign powers attempting to do harm to U.S. interests or retaliate for perceived U.S. aggression,” the NSA and DHS said.
It’s not just the Iranians who are fond of using VPN software to target industrial organizations. Multiple state-linked hacking groups known for probing industrial control systems, including those affiliated with Russia, have targeted remote-access technology. The hackers behind the Trisis malware — which caused a Saudi petrochemical facility to shut down in 2017 — have also shown an interest in the tech. (No one has publicly pointed the finger at a state for being behind that attack.)
The three vendors whose products Claroty found vulnerabilities in — HMS Networks, Moxa and Secomea — have released security fixes. The researchers initially saw hundreds of internet-facing servers exposed to one of the bugs, including those affiliated with offshore oil rigs, manufacturing plants and utility providers. Now, some 20% of those servers have been patched, said Erez, who credited the vendors for rolling out updates quickly. “We are working on contacting more asset owners to encourage them to update their versions.”
More Scoops
Wyden seeks upgraded NSA security guidance on commercial VPN use
it’s the latest in a sequence of letters to feds from Sen. Ron Wyden, D-Ore., on commercial VPNs.
Sen. Wyden urges feds to discard older, insecure, public-facing VPNs

Questions mount as Ivanti tackles another round of zero-days
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
FCC proposes public scorecard to rate telecoms on anti-robocall efforts
Pegasus, NoviSpy variant spyware found on devices of Serbian activists
The Collective Cyber Defense letter wrote your next vendor questionnaire
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Election official says Tina Peters would be consultant, won’t have access to election systems
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/vpn-vulnerabilities-claroty-industrial-control-systems/