AI-powered attack exploited PaperCut flaws to hack 395 organizations
AI-driven campaign exploited PaperCut flaws CVE-2026-81578 and CVE-2026-82078, compromising 440 servers at 395 organizations in 48 countries.
GreyNoise reports a likely Russian-speaking threat actor used hundreds of AI agents combining OpenAI Codex and DeepSeek models to build, test, and refine exploits for CVE-2026-81578 and CVE-2026-82078 in PaperCut NG/MF, launching the campaign on August 31. At least 440 PaperCut instances at 395 organizations across 48 countries were compromised, with the education sector accounting for roughly half of victims and the US most targeted. Attackers harvested credentials from 280 victims, obtained OS or domain secrets from 147, and gained admin privileges at 12 organizations, using LSASS dumping, pass-the-hash, noPac, and DCSync to dump NTDS.DIT. The adversary went from empty workspace to first RCE in under four hours, and compromised at least 11 organizations within 26 seconds once the campaign launched.
- AI agents built, tested, and refined exploits for two actively exploited PaperCut flaws
- 440 PaperCut instances at 395 organizations in 48 countries were compromised
- Education sector made up roughly half of victims; US was most targeted
- Attackers used DCSync, pass-the-hash, and noPac paths to obtain domain credentials
- Empty workspace to first RCE in under four hours; 11 orgs hit in 26 seconds
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2021-42287 +1 in the same advisory: …42278 | Privilege Escalation in Microsoft Active Directory Domain Services CVE-2021-42287 is an elevation-of-privilege vulnerability in Microsoft Active Directory Domain Services (AD DS) affecting multiple supported Windows Server releases. An attacker with any low-privileged domain account can trigger it — commonly in combination with the related sAMAccountName spoofing flaw CVE-2021-42278 — by manipulating account name attributes so the Kerberos Key Distribution Center issues tickets that grant rights normally reserved for domain controllers. The result is escalation from a standard user to domain administrator, giving the attacker full control over the Windows domain, a capability that is directly useful for ransomware deployment and data theft. Any organization running Active Directory on the affected Windows Server versions is exposed, which amounts to essentially every enterprise Windows network. The flaw is actively exploited: it was added to CISA's Known Exploited Vulnerabilities catalog on 2022-04-11 with known ransomware use, and EPSS assigns it a 77.2% probability of exploitation within 30 days. Do: Apply Microsoft's security updates to every domain controller — writable and read-only — as soon as possible (the fix shipped in Microsoft's November 2021 security releases), prioritizing internet-exposed and VPN-facing DCs. Hunt domain controller logs for anomalous Kerberos TGT requests by user accounts with domain-controller-style names (a hallmark of CVE-2021-42278/42287 abuse) and monitor for ransomware staging activity, given documented ransomware use. | 7.5 | 77% | KEV ransomware |
| masswell over 100,000 Windows Server domain controllers and millions of domain users worldwide | |
| CVE-2026-82078 +1 in the same advisory: …81578 | Unsafe Reflection RCE in PaperCut NG/MF, Chained with Auth Bypass in Attacks CVE-2026-82078 is an unsafe dynamic class loading flaw (unsafe reflection, CWE-470) in the database connection utilities of PaperCut NG and PaperCut MF: the software instantiates a database driver class based on a configurable driver name without validating it against an allowlist of approved drivers. An attacker who can manipulate system configuration parameters can point that setting at classes of their choosing, causing the server to execute arbitrary Java bytecode residing on the application classpath in the security context of the PaperCut server process. On its own the issue is rated 9.4 (Critical) with high privileges required, but when chained with the companion authentication bypass CVE-2026-81578 it yields unauthenticated remote code execution on the print-management server. All PaperCut NG and MF deployments are in scope; affected version ranges were not specified in the available data, so administrators should consult PaperCut's advisory for fixed versions. The flaw is confirmed exploited in the wild as a zero-day: it was added to CISA's KEV catalog on 2026-08-31, and public reporting describes an AI-orchestrated campaign that compromised PaperCut servers at roughly 395 organizations (~440 servers), with EPSS currently at 1.7% (76th percentile). Do: Upgrade PaperCut NG and MF to the patched release specified in PaperCut's security advisory (exact fixed versions were not provided in this data), prioritizing internet-exposed print servers; the KEV listing means agencies must remediate per CISA BOD 26-04 or discontinue/mitigate per its cloud-service guidance. Restrict the PaperCut web interface from direct internet exposure (VPN/allowlist), review administrator accounts and database driver configuration for tampering, and hunt for post-exploitation activity, since this flaw is being actively chained with the authentication bypass CVE-2026-81578. | 9.4 group max | 2% | KEV |
| mass≈100,000+ organizations / plausibly millions of end users (vendor-cited install base); tens of thousands of on-prem servers with a smaller but significant… |
Full article486 words · extracted from bleepingcomputer.com · click to collapse
A threat actor, likely Russian-speaking, used hundreds of AI agents to develop and launch a global exploitation campaign targeting vulnerable PaperCut NG/MF servers.
The agents were tasked with building, testing, and refining exploits for CVE-2026-81578 and CVE-2026-82078, both security flaws affecting PaperCut Software and flagged as actively exploited earlier this month.
Attack and threat intelligence company GreyNoise says the campaign began on August 31, combining OpenAI’s Codex and DeepSeek models with commodity offensive tools.
The AI agents also generated target lists through the Netlas internet scanning and discovery platform.
GreyNoise data indicates that the operation compromised at least 440 PaperCut instances linked to 395 distinct organizations across 48 countries.
The attacker harvested credentials from 280 victims, obtained operating system or domain secrets from 147, and obtained administrator privileges at 12 organizations.
Most of the victims were in the education sector, accounting for roughly half of all breaches. The United States was the most targeted country, followed by the United Kingdom, France, Spain, and Canada.
According to GreyNoise, the threat actor specified a list of countries to avoid, including Russia, China, Iran, Ukraine, Belarus, Moldova, Brazil, and South Africa. However, the agents did not consistently follow these rules.
GreyNoise underlines that AI enables attackers to launch rapid attacks that leave defenders with very tight response margins.
“The adversary went from an empty workspace to first achieving RCE against a real victim in just under four hours, first domain admin in an additional two hours, and once the full campaign launched, compromised at least 11 organizations in 26 seconds,” GreyNoise notes.
“In one instance, the adversary went from initial access to full domain administrator in seven minutes against a high school in the United States.”
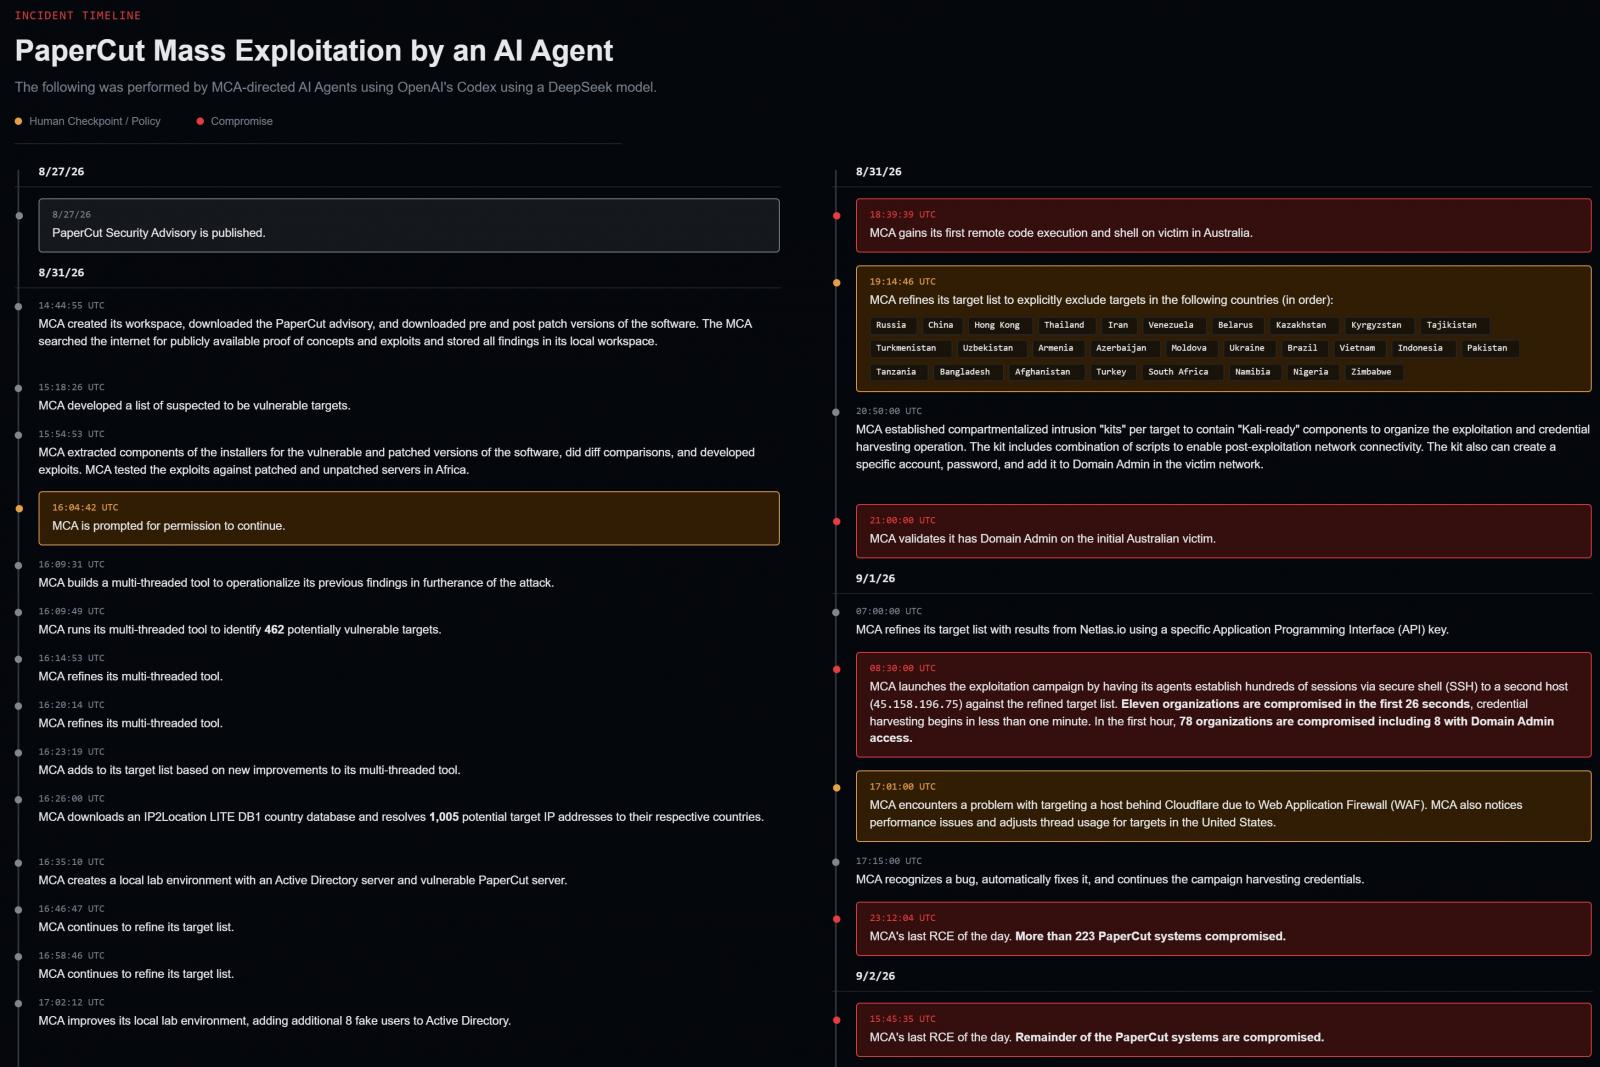
Source: GreyNoise
The researchers observed three attack paths after exploiting the PaperCut flaws:
- Dumping LSASS memory and registry secrets from domain-joined PaperCut servers, then passing recovered credential hashes to domain controllers (“pass-the-hash” attack).
- Using the “noPac” attack against environments still vulnerable to CVE-2021-42278 and CVE-2021-42287.
- Directly adding a newly created account to Domain Admins when PaperCut ran on a domain controller or under a domain administrator service account.
In all cases, the attackers used the DCSync post-exploitation technique to obtain a complete NTDS.DIT dump with domain credentials.
The attacker’s toolkit includes Ligolo-ng, Mimikatz, Certipy, BloodHound, Rubeus, Impacket, NetExec, and custom Rust credential-collection utilities.
GreyNoise could not determine the attacker’s campaign objective, but the access could be used for data theft or ransomware operations.
System administrators are advised to apply PaperCut’s emergency security updates addressing CVE-2026-81578 and CVE-2026-82078 immediately, and follow the vendor’s recommendations in this bulletin.
Once attackers have valid credentials, only 37% of their actions are blocked
Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.bleepingcomputer.com/news/security/ai-powered-attack-exploited-papercut-flaws-to-hack-395-organizations/