House Armed Services chair calls national security software, systems 'too vulnerable'
Full article988 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Rep. Adam Smith said the U.S. needs to invest in modernizing national security software and systems, which he said are vulnerable to cyberattacks.
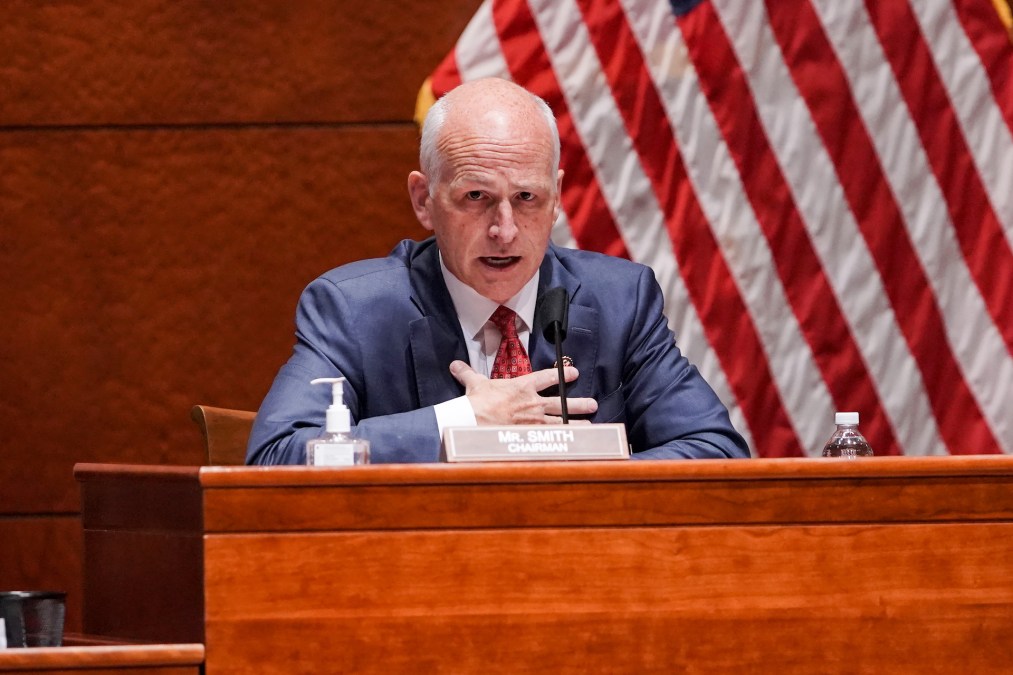
Rep. Adam Smith, the chairman of the House Armed Services Committee, said Tuesday that the United States needs to invest far more in protecting national security communications and software.
“Our number one biggest vulnerability in the cyber world is we have systems that are too vulnerable to attack right now because they’re old and we just, we haven’t updated those systems,” the Washington Democrat said. “Rather than buying another how many ever F-35s [combat planes] … I’d rather pour that money into developing the JADC2 [Joint All-Domain Command and Control] vision of a secure communication system that we can protect.”
JADC2 refers to the Department of Defense’s aspiration to connect sensors from all of the military services into a single network.
“DOD officials have argued that future conflicts may require decisions to be made within hours, minutes or potentially seconds compared with the current multi-day process to analyze the operating environment and issue commands,” the Congressional Research Service said of JADC2 in January. “They have also stated that the department’s existing command and control architecture is insufficient to meet the demands of the National Defense Strategy.”
Smith told reporters gathered for a session of the Defense Writers’ Group that the U.S. must “make a significant investment in upgrading our communication systems and our software” to ensure they are better protected.
“We’re talking about software systems that, you know, operate our missiles and our ships and everything, they just don’t, they are not as protected as they should be,” Smith said. “When it comes to cyber, protecting our systems, I think, is our greatest problem right now — even more so than our ability to exploit other people’s systems, though we certainly need to develop that capability as well.”
Smith also discussed the debate about the recent White House-led revisions to National Security Policy Memorandum-13 (NSPM-13), a process which ultimately led to a pairing back of DOD’s cyber operations authorities.
The congressman resisted the notion that the DOD ever had “unfettered capability” to lead cyber operations without oversight but said the current system works well, particularly with Gen. Paul Nakasone at the helm of both the National Security Agency and U.S. Cyber Command.
“When it comes to cyber, protecting our systems, I think, is our greatest problem right now — even more so than our ability to exploit other people’s systems, though we certainly need to develop that capability as well.”
House armed services chairman rep. adam smith
“We have a chain of command for a reason — now, I don’t want to let loose a bunch of hackers and say, go have fun, and let us know how it turns out,” Smith said during the wide-ranging discussion. “There’s going to be oversight, and there needs to be oversight and I think having NSA and Cyber [Command] together gives you an appreciation for the threats and the possibilities. I think that system works fine.”
Smith later said the Ukraine conflict has shined a light on Russia’s skill at using cyberattacks to conduct information operations, but he urged reporters to recognize the U.S.’s own capabilities in that terrain. Noting that while the U.S. hasn’t “invaded anyone lately so we haven’t needed to use it,” Smith asserted that information operations are a central component of modern warfare and one America excels at executing.
“Massing a lot of firepower isn’t what it used to be,” Smith said. “You need to have those hybrid capabilities … so that that’s what we’re trying to do in terms of the authorities we’re giving the Pentagon and what we’re trying to fund.”
More Scoops
Open-source security is posing challenges governments can’t easily solve
A diffuse landscape, fruitful targets, companies not stepping up, AI’s influence and flagging U.S. government efforts all figure into a shifting threat.
Former NSA chiefs worry American offensive edge in cybersecurity is slipping

Senate Intel chair urges national cyber director to safeguard against open-source software threats
Latest Podcasts
Government
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/adam-smith-national-security-software-house-armed-services/