Magento Developers Impersonated in Targeted GitHub Malware Operation
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| sha1 | 239087899df69b7ef9ba5d9716e3312c73c800ba | 58f521cbea21465b7ff6b claude-code-magento-agents/luajit.exe 239087899df69b7ef9ba5d9716e3312c73c800ba claude-code-magento-agents/tcp.log a6de13e6a4aef51f7b2bc298 |
| sha1 | 270f66d2c84ee86ff4b07c6220c51abd4897b5f0 | untime is identical across all samples: File SHA1 lua51.dll 270f66d2c84ee86ff4b07c6220c51abd4897b5f0 luajit.exe f5199b4191add11d02d58f521cbea21465b7ff6b Launche |
| sha1 | 29ee31ee046198594bb712d186a14a49d1346a50 | d11d02d58f521cbea21465b7ff6b Software_2.5-beta.5/luajit.exe 29ee31ee046198594bb712d186a14a49d1346a50 claude-code-magento-agents/Launcher.cmd 270f66d2c84ee86ff4b |
| sha1 | 6911c27ebedcad66076a8abf3c2d182ccf559feb | 20aa6ba45ef1be6e423e9576fed Manager_Google_1.0/Launcher.bat 6911c27ebedcad66076a8abf3c2d182ccf559feb Manager_Google_1.0/clx.txt 270f66d2c84ee86ff4b07c6220c51abd |
| sha1 | 7adf9cf2b2cc720aa6ba45ef1be6e423e9576fed | uncher scripts and obfuscated payloads vary per repository: 7adf9cf2b2cc720aa6ba45ef1be6e423e9576fed Manager_Google_1.0/Launcher.bat 6911c27ebedcad66076a8abf3c2 |
| sha1 | a6de13e6a4aef51f7b2bc298181ee5e02dd94861 | f9ba5d9716e3312c73c800ba claude-code-magento-agents/tcp.log a6de13e6a4aef51f7b2bc298181ee5e02dd94861 magento-frankenphp-images_2.4/Launcher.cmd bef485d8b3ab03ec |
| sha1 | a72a4990db017897d37759f991e1c1515171c77b | 0aa6ba45ef1be6e423e9576fed Software_2.5-beta.5/Launcher.bat a72a4990db017897d37759f991e1c1515171c77b Software_2.5-beta.5/clx.txt 270f66d2c84ee86ff4b07c6220c51ab |
| sha1 | bef485d8b3ab03ec389b984a231369f9aa2852c0 | 181ee5e02dd94861 magento-frankenphp-images_2.4/Launcher.cmd bef485d8b3ab03ec389b984a231369f9aa2852c0 magento-frankenphp-images_2.4/clib.txt 270f66d2c84ee86ff4b0 |
| sha1 | c6c9d7de860a848e4053acca3993d2d914889e64 | 412bf20b145f83cbd12 static_deploy_magento_v1.9/Launcher.cmd c6c9d7de860a848e4053acca3993d2d914889e64 static_deploy_magento_v1.9/arch.txt Malicious GitHub accoun |
| sha1 | df37352a15f99cb79f88d412bf20b145f83cbd12 | 521cbea21465b7ff6b magento-frankenphp-images_2.4/luajit.exe df37352a15f99cb79f88d412bf20b145f83cbd12 static_deploy_magento_v1.9/Launcher.cmd c6c9d7de860a848e405 |
| sha1 | f5199b4191add11d02d58f521cbea21465b7ff6b | a51.dll 270f66d2c84ee86ff4b07c6220c51abd4897b5f0 luajit.exe f5199b4191add11d02d58f521cbea21465b7ff6b Launcher scripts and obfuscated payloads vary per repositor |
Full article467 words · extracted from sansec.io · click to collapse
Rob Aimes alerted us to malicious GitHub repositories targeting Magento developers. The repos pose as legitimate tools but deliver Windows malware: a RAT and keylogger bundled as a LuaJIT package. The campaign is part of the FakeGit operation.
How the attack works
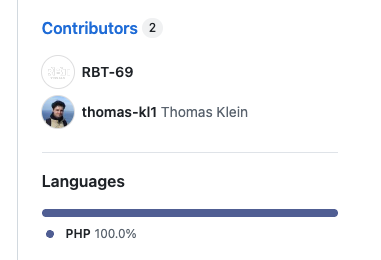
The attackers create repositories with luring names: deployment tools, Docker images, and configuration utilities. To appear trustworthy, they copy code from real open source projects, preserving the original commit history. This causes legit authors' avatars to appear in the "Contributors" section.
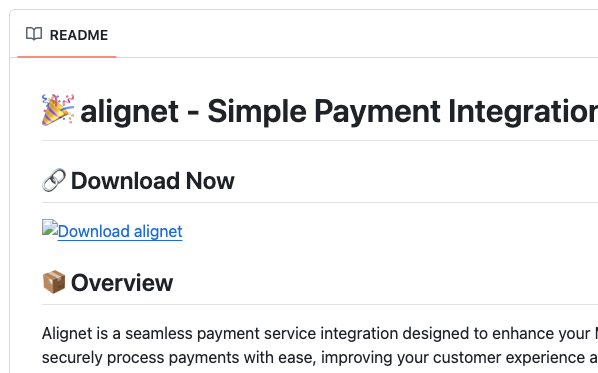
All repositories were created within the past 24 hours, though their commit timestamps appear older. These timestamps are fabricated.
By reusing commits from legitimate projects, the attackers make real open source contributors appear in the repository sidebar:
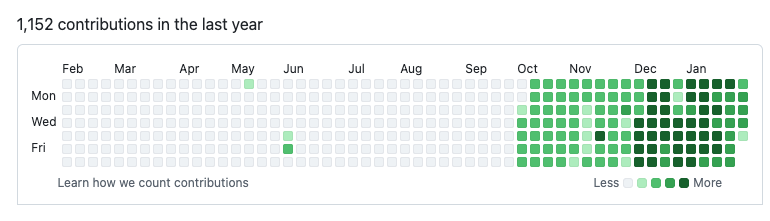
The publishing accounts share a distinctive activity pattern: dormant for months, then suddenly active:
Malicious repositories
Sansec identified these malicious GitHub accounts and repositories:
github.com/Uros5294/magento2-static-deploygithub.com/RBT-69/magento2-applicationgithub.com/suhanimish12/magento-frankenphp-imagesgithub.com/saddam237262/configdiffgithub.com/Sultanzacki9506/Google_Managergithub.com/NobreTakeshi/claude-code-magento-agentsgithub.com/ske1et2/Telegrams-Best-Scrappergithub.com/priya77771/module-widgetkit
| Repository | Original Author | Most Recent Committer Email |
|---|---|---|
| Uros5294/magento2-static-deploy | peterjaap ([email protected]) | |
| [email protected] | ||
| RBT-69/magento2-application | Thomas Klein ([email protected]) | [email protected] |
| suhanimish12/magento-frankenphp-images | Mohamed El Mrabet ([email protected]) | [email protected] |
| saddam237262/configdiff | Paul Frederiksen ([email protected]) | |
| [email protected] | ||
| Sultanzacki9506/Google_Manager | Sultanzacki9506 ([email protected]) | [email protected] |
| NobreTakeshi/claude-code-magento-agents | NobreTakeshi ([email protected]) | [email protected] |
| ske1et2/Telegrams-Best-Scrapper | SkillSany ([email protected]) | [email protected] |
Payload analysis
Visitors are encouraged to download a ZIP file containing the "application." Inside is a self-contained LuaJIT runtime with an obfuscated Lua script. The package structure follows a consistent pattern across all repositories:
Launcher.bat (or Launcher.cmd)
lua51.dll
luajit.exe
[payload].txt        # obfuscated Lua script (clx.txt, clib.txt, arch.txt, tcp.log)
The Lua script, when executed via the batch launcher, deploys a RAT and keylogger targeting Windows systems.
Indicators of Compromise
File hashes (SHA1)
The LuaJIT runtime is identical across all samples:
| File | SHA1 |
|---|---|
lua51.dll | 270f66d2c84ee86ff4b07c6220c51abd4897b5f0 |
luajit.exe | f5199b4191add11d02d58f521cbea21465b7ff6b |
Launcher scripts and obfuscated payloads vary per repository:
7adf9cf2b2cc720aa6ba45ef1be6e423e9576fed  Manager_Google_1.0/Launcher.bat
6911c27ebedcad66076a8abf3c2d182ccf559feb  Manager_Google_1.0/clx.txt
270f66d2c84ee86ff4b07c6220c51abd4897b5f0  Manager_Google_1.0/lua51.dll
f5199b4191add11d02d58f521cbea21465b7ff6b  Manager_Google_1.0/luajit.exe
7adf9cf2b2cc720aa6ba45ef1be6e423e9576fed  Software_2.5-beta.5/Launcher.bat
a72a4990db017897d37759f991e1c1515171c77b  Software_2.5-beta.5/clx.txt
270f66d2c84ee86ff4b07c6220c51abd4897b5f0  Software_2.5-beta.5/lua51.dll
f5199b4191add11d02d58f521cbea21465b7ff6b  Software_2.5-beta.5/luajit.exe
29ee31ee046198594bb712d186a14a49d1346a50  claude-code-magento-agents/Launcher.cmd
270f66d2c84ee86ff4b07c6220c51abd4897b5f0  claude-code-magento-agents/lua51.dll
f5199b4191add11d02d58f521cbea21465b7ff6b  claude-code-magento-agents/luajit.exe
239087899df69b7ef9ba5d9716e3312c73c800ba  claude-code-magento-agents/tcp.log
a6de13e6a4aef51f7b2bc298181ee5e02dd94861  magento-frankenphp-images_2.4/Launcher.cmd
bef485d8b3ab03ec389b984a231369f9aa2852c0  magento-frankenphp-images_2.4/clib.txt
270f66d2c84ee86ff4b07c6220c51abd4897b5f0  magento-frankenphp-images_2.4/lua51.dll
f5199b4191add11d02d58f521cbea21465b7ff6b  magento-frankenphp-images_2.4/luajit.exe
df37352a15f99cb79f88d412bf20b145f83cbd12  static_deploy_magento_v1.9/Launcher.cmd
c6c9d7de860a848e4053acca3993d2d914889e64  static_deploy_magento_v1.9/arch.txt
Malicious GitHub accounts
Uros5294RBT-69suhanimish12saddam237262Sultanzacki9506NobreTakeshiske1et2
Recommendations
- Verify repository authenticity: check the account age, activity history, and whether the repository is linked from official project documentation
- Never run downloaded executables from untrusted sources, especially batch files that launch interpreters
- Report suspicious repositories to GitHub via their abuse reporting system
- If you downloaded and executed any of these packages, scan your system for malware immediately
For Magento store owners, run eComscan to detect any compromise on your server infrastructure.
You can monitor for new malicious repositories via GitHub's search, sorted by most recently updated.
Read more
Text extracted automatically; images, tables and formatting may be missing. Original: https://sansec.io/research/fake-magento-repos-github-malware