Iran hacking group impersonates defense firms, hostage campaigners
Full article841 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
A hacking campaign linked to the Islamic Revolutionary Guard Corps is targeting firms in the defense sector with a pair of new backdoors.
An Iranian-sponsored cyberespionage unit is impersonating major brands like Boeing and the Chinese drone manufacturer DJI as part of a social engineering and phishing campaign targeting the aerospace, aviation and defense industries across the Middle East, researchers with Mandiant said late Tuesday.
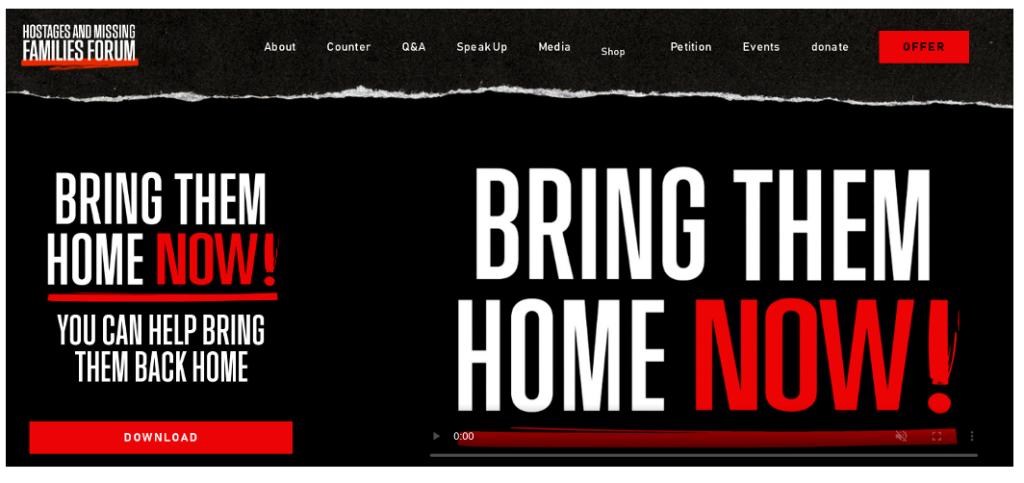
The Iranian hacking group has also been observed employing a fake website playing on the Israel-Hamas war, using the “Bring Them Home Now!” slogan associated with a campaign to free hostages held by Hamas. The website is the latest example of the way in which Iranian hacking groups are using the conflict between Israel and Hamas to carry out opportunistic attacks linked to the fighting.
The Iranian campaign relies on phony job offers from major international companies and the fake hostage-themed website to funnel targets to compromised websites designed to either harvest credentials or deliver one of two previously unreported and unique backdoors dubbed “MINIBUS” and “MINIBIKE,” the researchers said.
The current campaign dates to at least June 2022 and remains active. It has mostly targeted Israel, the United Arab Emirates and, potentially Turkey, India and Albania, the researchers said.
The unit behind the campaign is tracked as UNC1549 by Mandiant and the infrastructure described by Mandiant overlaps with the hacking groups dubbed Tortoiseshell and Imperial Kitten. The unit is likely linked to the Islamic Revolutionary Guard Corps and has a history of using fake job offers and similar lures in social engineering campaigns going back years.
In July 2021, for instance, Facebook announced the disruption of one of the group’s campaigns that used accounts on the social media platform to pose as recruiters to target U.S. military members. An October 2023 PwC analysis noted that the group is known to employ both custom and off-the-shelf malware to achieve its espionage goals, which includes credential harvesting and data exfiltration.
The current campaign uses Microsoft Azure cloud infrastructure for command and control and hosting functions, “making it difficult to discern the activity from legitimate network traffic,” the researchers said.
More Scoops
Researchers say Israeli government likely behind AI-generated disinfo campaign in Iran
The group leveraged dozens of social media accounts and “routinely used” AI-generated imagery and video to stoke unrest among Iran’s population, according to Citizen Lab.
Iranian hackers were more coordinated, aligned during Israel conflict than it seemed
Iran’s Bank Sepah disrupted by cyberattack claimed by pro-Israel hacktivist group
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Election official says Tina Peters would be consultant, won’t have access to election systems
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/iran-hostages-boeing-dji/