ICCYBER 2010
Full article233 words · extracted from securelist.com · click to collapse
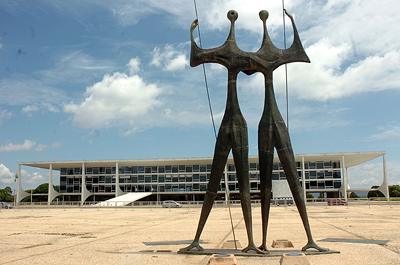

Greetings from beautiful Brasília, the capital of Brazil, with its unique architecture. I’m here for a few days to take part in the 7th International Conference on Cybercrime Investigation (ICCyber), promoted by the Brazilian Association of Specialists in High Technology (ABEAT). The event is being run in collaboration with the Brazilian Federal Police.
There are 800 attendees from law enforcement agencies around the world like Interpol, Europol, Scotland Yard, and several Federal Police agencies. Representatives from security companies, and Brazilian banks are here too – and we’re all talking about the fight against cybercrime.
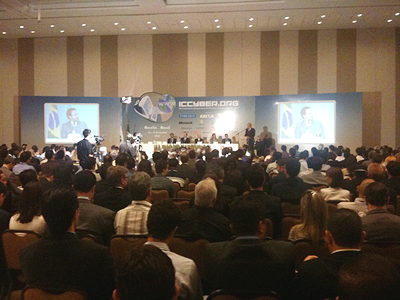
We’re here to present our research on malware trends in the Latin America region, and also to reinforce our links with the police and banking communities.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/iccyber-2010/29627/