IT Security for the Next Generation
Full article352 words · extracted from securelist.com · click to collapse



We’ve just held the first European edition of our international student conference, IT Security for the Next Generation. Young researchers, masters and PhD students, professors and Kaspersky Lab experts all presented and discussed different issues relating to cybercrime at the beautiful University of East London.
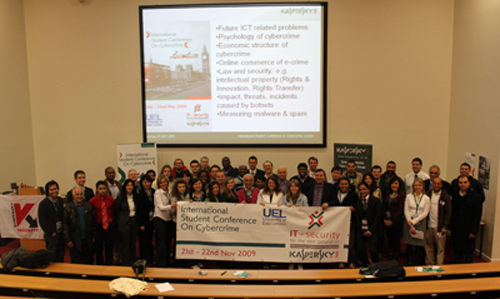
I was involved as a member of the program committee and had to evaluate students’ research reports and papers. To be honest, it wasn’t an easy task to choose the best from so many different interesting topics: incidents caused by botnets, analysis of drive-by download attacks, measuring malware & spam, psychology of cybercrime, etc…
The event gave young IT professionals to attend lectures and workshops led by Kaspersky analysts and experts: my colleague, Denis Maslennikov made an interesting workshop about mobile malware, Georg Wicherski let participants into some of the basics of malware analysis, Eddy Willems talked about the human factor and security, and Sergey Golovanov revealed how he became a Kaspersky expert.
But the conference wasn’t just about lectures and learning: we had two days full of fun, drive, meeting new people and great teambuilding, as well as surviving the English weather!
It’s sad that the conference is over, but we’ll be running more events like this on a regular basis around the world. And I’m sure that meetings like this inspire everyone to new challenges, new research, new opportunities, and that everyone who came is motivated to be with us on the light side!
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/it-security-for-the-next-generation/30588/