Rep. Connolly: National data breach notification law could be coming
Full article569 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Gerry Connolly said he hopes for a national standard to evolve among the private sector, but massive breaches like that at credit monitoring firm Equifax may force Congress’s hand.
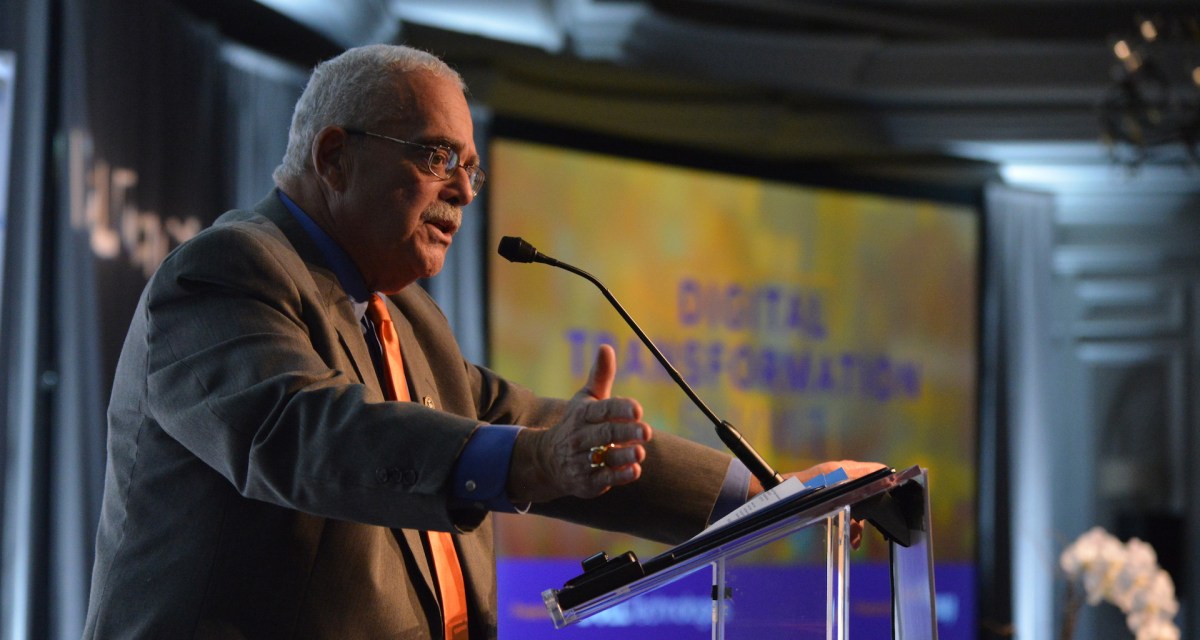
A cybersecurity-focused lawmaker says Congress may have to consider national data-breach notification legislation if companies don’t do a better job of alerting people when they’ve suffered a breach.
Rep. Gerry Connolly, D-Va., said he hopes for a national standard to evolve among the private sector, but massive breaches like that at credit monitoring firm Equifax may force Congress’s hand.
Congress doesn’t “want to upset the technology community with obtrusive regulation,” but the private sector has been poor in instilling confidence that it will act in the public’s best interest, he said.
“I think its headed that way absent some fresh look by industry, a benchmark standard that everybody’s accepted voluntarily to meet, so that federal regulation is unnecessary,” Connolly told CyberScoop Thursday during Dell Technologies’ Digital Transformation Summit. ”I think Equifax is a great test of whether industry is capable of meeting that test.”
Equifax has come under great scrutiny for the way it handled a breach that affected 145.5 million people. The firm discovered the breach July 29, six weeks before revealing it to the public.
Currently, companies are held to a patchwork of state-level breach notification laws that differ depending on the location. Equifax, headquartered in Atlanta, was bound to Georgia law.
The state’s law stipulates that data breach notifications “shall be made in the most expedient time possible and without unreasonable delay, consistent with any measures necessary to determine the scope of the breach and restore the reasonable integrity, security, and confidentiality of the data system.”
There has been movement before on a national data breach notification law. In 2015, the Obama administration pushed the Personal Data Notification & Protection Act, but it did not advance in Congress.
Connolly said another reason Congress hasn’t been able to agree to a breach notification standard is a lack of understanding on cybersecurity as a whole.
“I have always been depressed with how slow Congress has been to react to cyberthreats, both in the federal government and the private sector,” Connolly said.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/national-data-breach-notification-gerry-connolly/