Boston Aftermath
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| md5 | 5ea646ffdc1e9bc7759fdfc926de7660 | .Win32.Tepfer.*”. MD5sums of some of the collected samples: 5EA646FFDC1E9BC7759FDFC926DE7660 959E2DCAD471C86B4FDCF824A6A502DC Latest Webinars Reports Ka |
| md5 | 959e2dcad471c86b4fdcf824a6a502dc | of the collected samples: 5EA646FFDC1E9BC7759FDFC926DE7660 959E2DCAD471C86B4FDCF824A6A502DC Latest Webinars Reports Kaspersky researchers have discover |
Full article219 words · extracted from securelist.com · click to collapse



While many are still in shock after the Boston Marathon bombings on 16 April, it didn’t take long for cyber criminals to abuse that tragic incident for their dirty deeds.
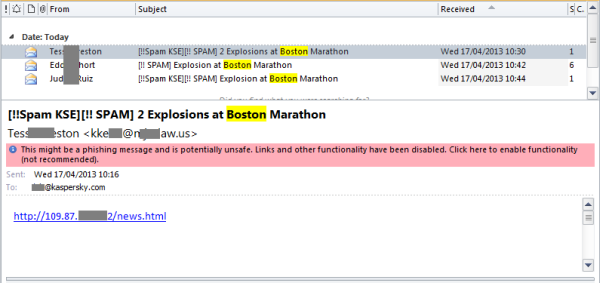
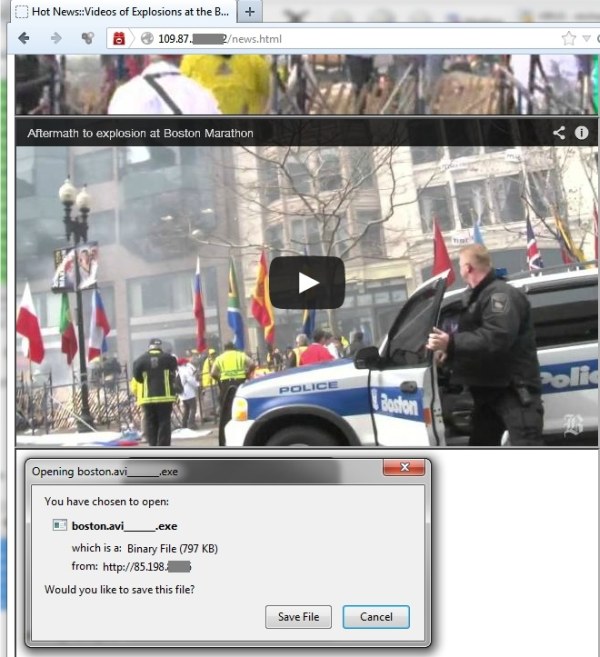
Today we already started receiving emails containing links to malicious locations with names like “news.html”. These pages contain URLs of non-malicious youtube clips covering the recent event. After a delay of 60 seconds, another link leading to an executable file is activated.
The malware, once running on an infected machine, tries to connect to several IP addresses in Ukraine, Argentina and Taiwan.
Kaspersky Lab detects this threat as “Trojan-PSW.Win32.Tepfer.*”.
MD5sums of some of the collected samples:
5EA646FFDC1E9BC7759FDFC926DE7660
959E2DCAD471C86B4FDCF824A6A502DC
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/boston-aftermath-9/35741/