Five Eyes nations warn of evolving Russian cyberespionage practices targeting cloud environments
Full article732 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The advisory issued by the U.K.'s National Cyber Security Centre breaks down tactics and techniques from SVR hacking ops.
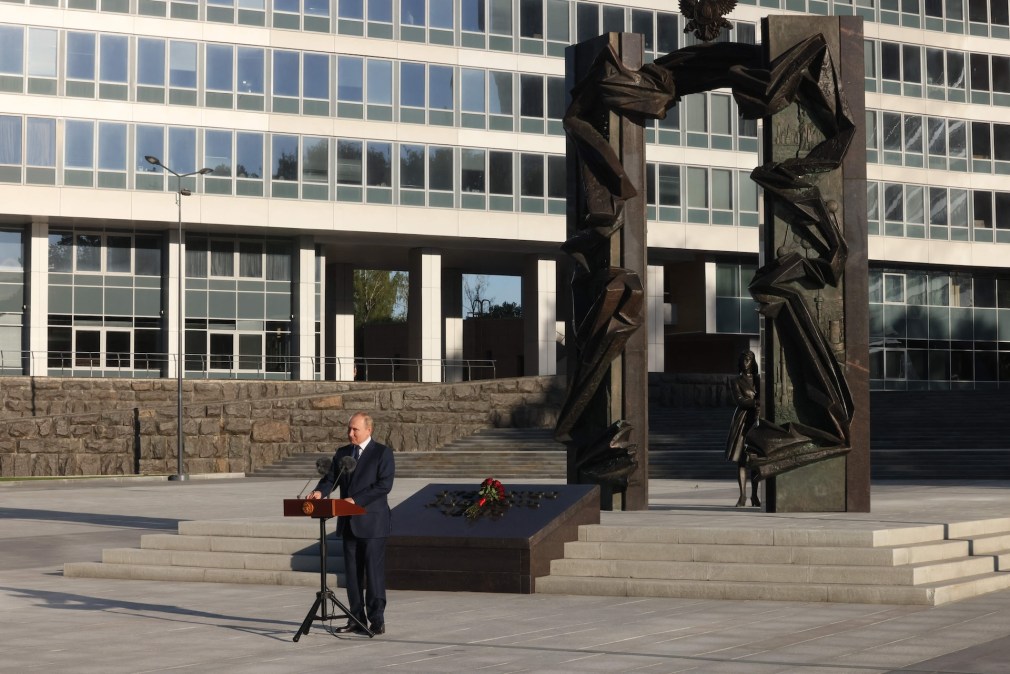
Longstanding cyberespionage and data collection units tied to Russia’s Foreign Intelligence Service (SVR) are evolving their techniques to gain access to cloud environments, the British, U.S. and partner governments said in an advisory Monday.
The advisory — issued by the U.K.’s National Cyber Security Centre and co-signed by a range of counterpart agencies in the U.S., Australia, Canada and New Zealand — details the evolving tactics, techniques and procedures that SVR hacking operations, tracked widely under the “APT29” and “Cozy Bear” monikers, are employing to penetrate the increasing number of cloud environments used by both private and public organizations.
APT29 operations are considered highly sophisticated and have been tracked since at least 2014, targeting a wide range of North American and European industries, including biotechnology, government, nonprofits, telecommunications and think tanks, according to an April 2022 report from Mandiant.
The U.S. government, for instance, attributed to APT29 the 2020 SolarWinds supply chain attack, one of the most consequential cyberespionage operations in recent years.
Even still, the agencies said Monday, basic cloud security measures can go a long way toward stymieing APT29 efforts.
“The SVR is a sophisticated actor capable of carrying out a global supply chain compromise such as the 2020 SolarWinds, however the guidance in this advisory shows that a strong baseline of cyber security fundamentals can help defend from such actors,” the notice read.
Attackers must first successfully authenticate to the cloud provider, the notice read, so basic steps can go a long way. Some of those steps include regularly evaluating and disabling dormant accounts that could be tied to employees who are no longer with organizations, working with cloud providers to limit the validity time of system-issued tokens (which enable logins without passwords), and more stringent device-enrollment policies.
The Cybersecurity and Infrastructure Security Agency has also shared best practices for business-oriented cloud environments through its Secure Cloud Business Applications (SCuBA) project, the advisory said.
More Scoops
Trump blames Minnesota for cyberattacks on water sector, drawing pushback from cyber world
The president went against his intelligence agencies’ conclusions about Iran being the likely suspect in the campaign.
Iranian hackers launching disruptive attacks at U.S. energy, water targets, feds warn
After major Poland energy grid cyberattack, CISA issues warning to U.S. audience
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/five-eyes-nations-warn-of-evolving-russian-cyberespionage-practices-targeting-cloud-environments/