Ransomware incidents in manufacturing grow as transparency, and attack options, increase
Full article872 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Manufacturing, like other sectors such as health care, has endured a rise in opportunistic attacks from criminals.
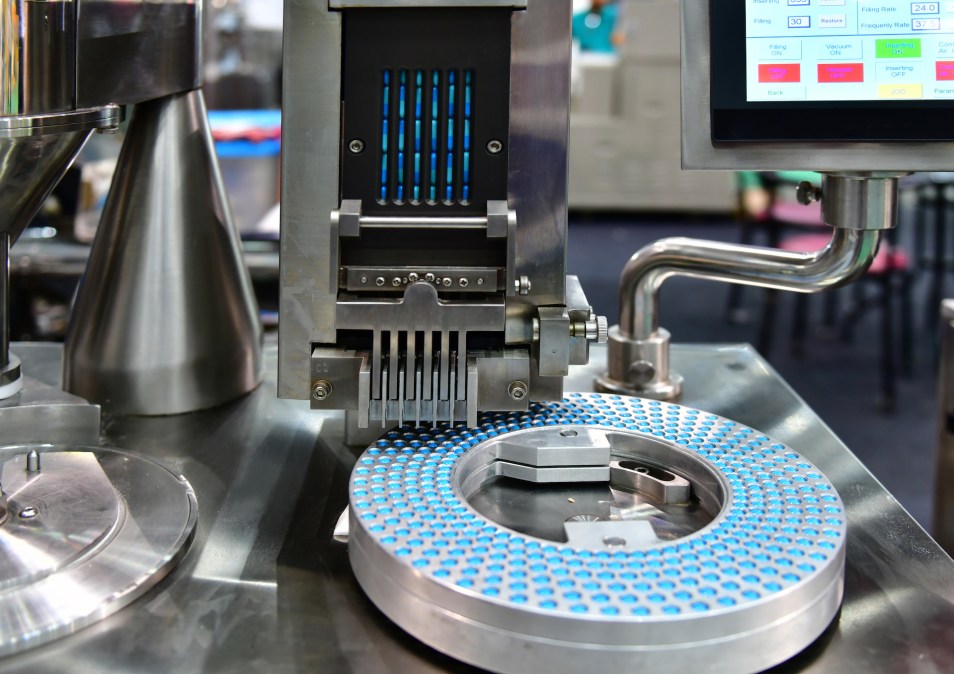
The number of publicly documented ransomware incidents at manufacturing organizations has jumped considerably in 2020 as attackers have found ways to disrupt facilities’ operations by affecting both traditional IT networks and software that supports industrial processes, according to research published Thursday.
Industrial security company Dragos found that ransomware incidents in the manufacturing sector had more than “tripled” this year compared to 2019, though the company did not specify the number of incidents.
Two things help explain the report’s findings: Companies are being more transparent about reporting incidents; and manufacturing, like other sectors such as health care, has endured a rise in opportunistic attacks from criminals who know how bring an organization to its knees.
“Companies that rely on availability of their operations [are] being targeted and held for ransom to be able to restart those processes,” said Selena Larson, a senior cyberthreat analyst at Dragos.
Among the Dragos tally were reported ransomware incidents at Honda in June and Evraz, a steel maker, in March. Both companies were reportedly forced to halt some production operations.
The Honda incident pointed to a troubling trend, Dragos said: Some threat groups are increasingly using ransomware with code that contains the ability to disrupt software that supports industrial processes. EKANS, the ransomware reportedly used on Honda, was also suspected in a May attack on Fresenius Group, a European health care conglomerate, that hampered some pharmaceutical production.
But it doesn’t take tailored code like that to affect manufacturers’ operations. Attackers could also encrypt IT networks containing logistics data, throwing a wrench in scheduling plans.
“A simple, non-manufacturing-specific attack [including ransomware] can easily spill out of the enterprise network to the factory floor and, in absence of strong air-gapping measures, halt the production,” said Federico Maggi, a senior researcher at cybersecurity company Trend Micro who specializes in manufacturing.
A possible testing ground
State-linked hacking groups rarely confine themselves to targeting just one sector. Five such groups have shown an interest in manufacturing while at the same time targeting electricity, aerospace and other sectors, according to Dragos.
The report makes the case that such advanced persistent threats, as state-linked groups are often known, could test out their capabilities on the manufacturing sector. Some big manufacturing companies have on-site power operations that contain some of the same equipment exploited by suspected Russian hackers who cut power in Ukraine in 2016.
“It’s possible that manufacturing would be an interesting and attractive target for an adversary’s offensive tool development because we often see that it’s less sophisticated in terms of its cybersecurity operations and there’s just not quite as much oversight or regulations,” Larson said.
More Scoops
Former incident responders sentenced to 4 years in prison for committing ransomware attacks
Ryan Goldberg and Kevin Martin attacked five companies in 2023 and extorted nearly $1.3 million from one of their victims.
Dragos: Despite AI use, new malware targeting water plants is ‘hype’
Iranian attacks on US critical infrastructure puts 3,900 devices in crosshairs
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/ransomware-manufacturing-dragos-honda/