CrowdStrike exec apologizes in front of Congress over huge global IT outage
Full article688 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
House lawmakers struck a sympathetic tone toward the company at a hearing where they nevertheless said nothing like that could happen again.
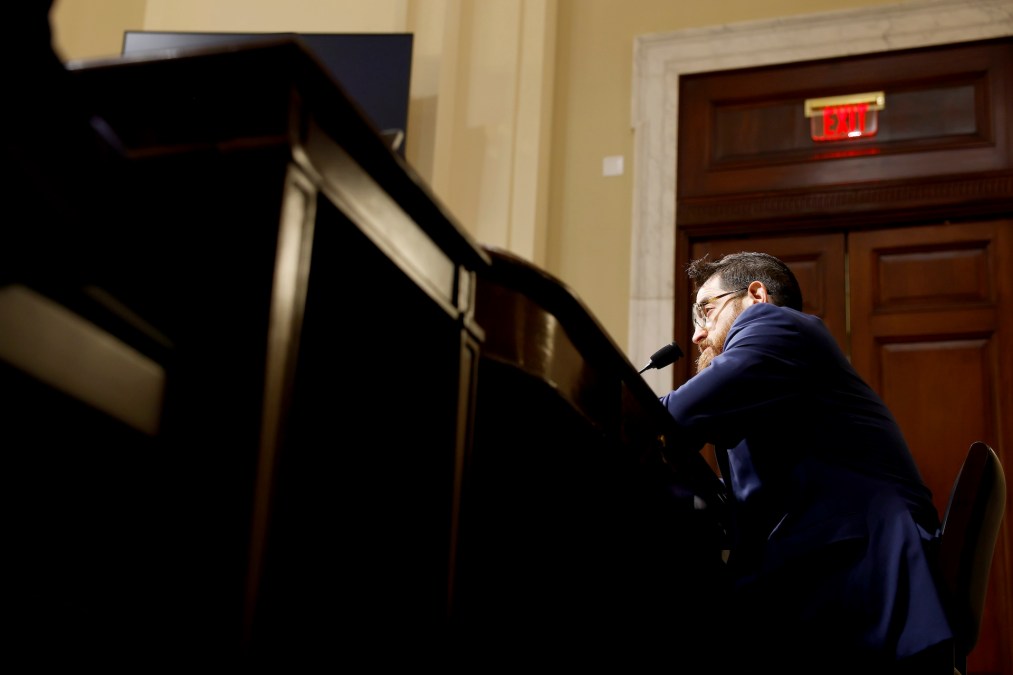
A CrowdStrike executive apologized Tuesday over a faulty update that caused a massive IT outage two months ago, saying the company has taken steps to make sure it can’t happen again.
The history-making July 19 problem involved new threat detection configurations for CrowdStrike’s Falcon security platform that were sent to sensors running on Microsoft Windows devices that the Falcon sensor’s rules engine did not understand, Adam Meyers, the company’s senior vice president of counter adversary operations, testified to the House Homeland Security panel’s cybersecurity subcommittee.
Essentially, it was like trying to move a chess piece where there wasn’t a square, Meyers explained. Approximately 8.5 million systems crashed as a result, leading to billions of dollars worth of losses.
In response, CrowdStrike has introduced new validation checks, enhanced testing procedures, additional controls for customers, gradual rollout across increasing rings of deployment, more runtime checks and third-party reviews, Meyers told the subcommittee.
“We let our customers down,” he said. “On behalf of everyone at CrowdStrike I want to apologize. We are deeply sorry and we are determined to prevent this from ever happening again.”
Lawmakers largely struck a sympathetic tone with Meyers, approving of how the company responded in the aftermath. But they said they, too, wanted to avoid any repeats.
“The largest IT outage in history was due to a mistake,” said committee Chair Mark Green, R-Tenn., comparing it to a catastrophe straight out of a movie. “Mistakes can happen. However, we can’t allow a mistake of this magnitude to happen again.”
Meyers emphasized that the incident didn’t involve a cyberattack, and that artificial intelligence played no role in sending the faulty update. The incident did have further cyber implications, however.
Rep. Andrew Garbarino, R-N.Y., who chairs the cyber subcommittee, asked why federal agencies were impacted by the updates and whether there were different updates to test for commercial versus government clients.
The updates went to Microsoft Windows operating sensors regardless of which system was running on a given device, Meyers answered.
Even if lawmakers indicated a sense of understanding on CrowdStrike’s behalf, others have proven more antagonistic, particularly Delta Airlines, which has threatened a lawsuit against the cyber giant.
Meyers said it has worked to aid customers affected by the outage and will do whatever it has to do to make them feel comfortable working with CrowdStrike again. He also said the company would be willing to cooperate with any potential review by the Cyber Safety Review Board.
“Trust takes years to make and seconds to break,” he said.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/crowdstrike-exec-apologizes-congressional-hearing-it-outage/