NATO investigating breach, leak of internal documents
Full article936 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
A politically motivated hacking group known as SiegedSec claims to have breached NATO systems and leaked a cache of documents online.
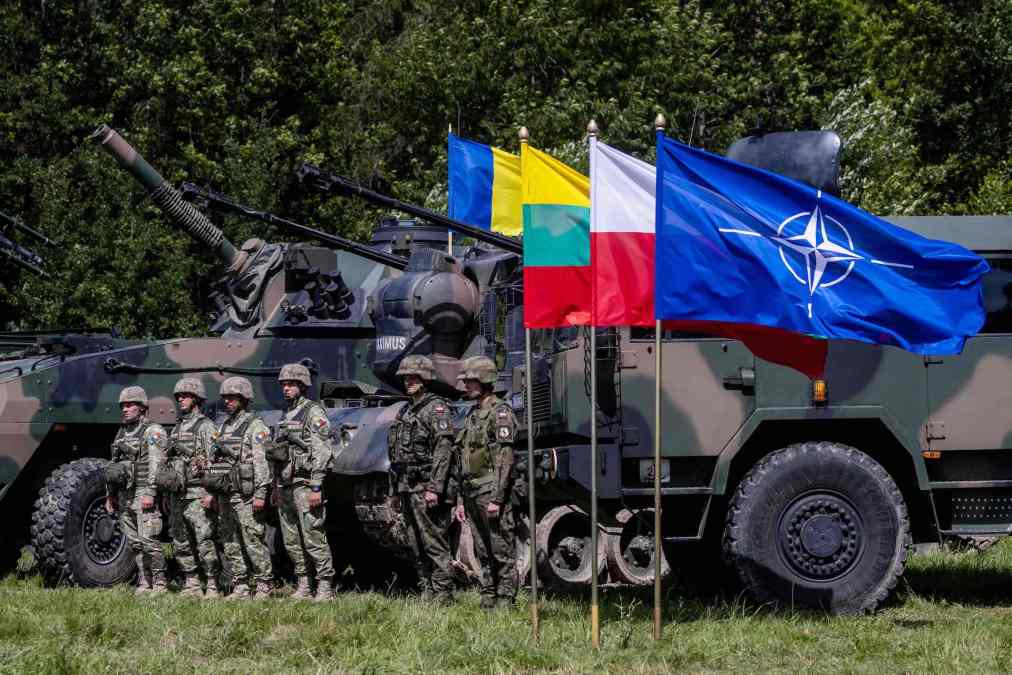
NATO is investigating claims by a politically motivated hacktivist group that it breached the defense alliance’s computer systems, which, if confirmed, would mark the second time in the last three months that the group known as SiegedSec has broken into NATO systems.
SiegedSec, a cybercrime group with a history of politically-motived attacks, claimed on its Telegram channel on Saturday that it had stolen roughly 3,000 NATO documents and posted six screenshots allegedly showing access to various NATO web pages. The group claimed the 3,000 stolen files total more than nine gigabytes of data.
“NATO cyber experts are actively addressing incidents affecting some unclassified NATO websites,” a NATO official told CyberScoop Tuesday. “Additional cyber security measures have been put in place. There has been no impact on NATO missions, operations and military deployments.”
In July, SiegedSec posted a link to roughly 700 files stolen from the NATO Community of Interest Cooperation Portal, an unclassified information sharing and collaboration site maintained by the international agency.
At the time, NATO confirmed to CyberScoop that it was reviewing the matter. On Tuesday, the NATO official declined to comment on the status of that investigation.
According to SiegedSec’s message Saturday, files from the attack come from the Joint Advanced Distributed Learning platform, the NATO Lessons Learned Portal, the Logistics Network Portal, the Communities of Interest Cooperation Portal and the NATO Standardization Office. CyberScoop was not able to independently confirm the authenticity of the files but is reporting on SiegedSec’s claim given its track record of purported attacks against NATO.
Hacking groups supportive of the Russian government, such as Killnet, have in recent months posted files online claimed to have been stolen from NATO, which has taken on a key role in coordinating aid to Ukraine following Russia’s invasion. But SiegedSec claims no affiliation with a state and has cited its attacks on Russian targets as evidence of its independence.
In a message posted alongside its breach of NATO in July, SiegedSec said the attack had “nothing to do with the war between Russia and Ukraine” and said it was “a retaliation against the countries of NATO for their attacks on human rights.”
SiegedSec emerged as a group on Telegram in April of 2022 and quickly began sharing data and files it claimed had been stolen from organizations around the world. In the summer of 2022, the group claimed attacks on state websites in Kentucky and Arkansas over those states’ legislative efforts to limit access to abortion. In July, the group claimed to have targeted multiple satellite receivers and industrial control systems “particularly in states banning gender affirming care.”
After those attacks, a SiegedSec representative told CyberScoop that they consider themselves “more blackhat than hacktivists.” Money “is not our main goal,” the person said. “Most of the time we just want to have fun and destroy stuff.”
More recently the group has claimed connections with other cybercrime groups or channels that advertise financially-motivated extortion activity and has also promoted a channel selling what it says is access to compromised government email accounts and other platforms to enable fraudulent emergency data requests, which can be used to obtain private information on people from various social media platforms.
More Scoops
The GTA VI leaks are breaking the internet. Security researchers have seen this before.
A memecoin, a manifesto, and a week of daily leaks — but to researchers, it's a familiar extortion playbook with an unusually large audience.
Pro-Russian DDoS group NoName057(16) disrupted by international law enforcement operation
Hacktivists release two gigabytes of Heritage Foundation data
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/nato-siegedsec-breac/