U.S. Air Force pays out $103,883 to hackers in bug bounties
Full article552 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Add up all the U.S. military's bug bounty programs and over 3,000 vulnerabilities have been found in federal government systems.
The U.S. military’s love affair with bug bounty programs continues.
The second iteration of “Hack the Air Force” in December paid out $103,883 in bounties to freelance hackers for 106 vulnerabilities found over a 20-day period. The highest bounty was $12,500, the largest paid by the U.S. government to date.
The Air Force’s first bug bounty program launched in April 2017 following similar efforts like Hack the Pentagon and Hack the Army in 2016. In total, more than 3,000 vulnerabilities have been found in federal government systems since the programs began.
The bug bounty platform HackerOne, a private company, continues to handle the military’s bug bounty initiatives. Air Force CISO Peter Kim, who helped kick off and cheerlead the service’s first round last year, also played a leading role this time.
“We continue to harden our attack surfaces based on findings of the previous challenge and will add lessons learned from this round,” Kim said in a statement. “This reinforces the work the Air Force is already doing to strengthen cyber defenses and has created meaningful relationships with skilled researchers that will last for years to come.”
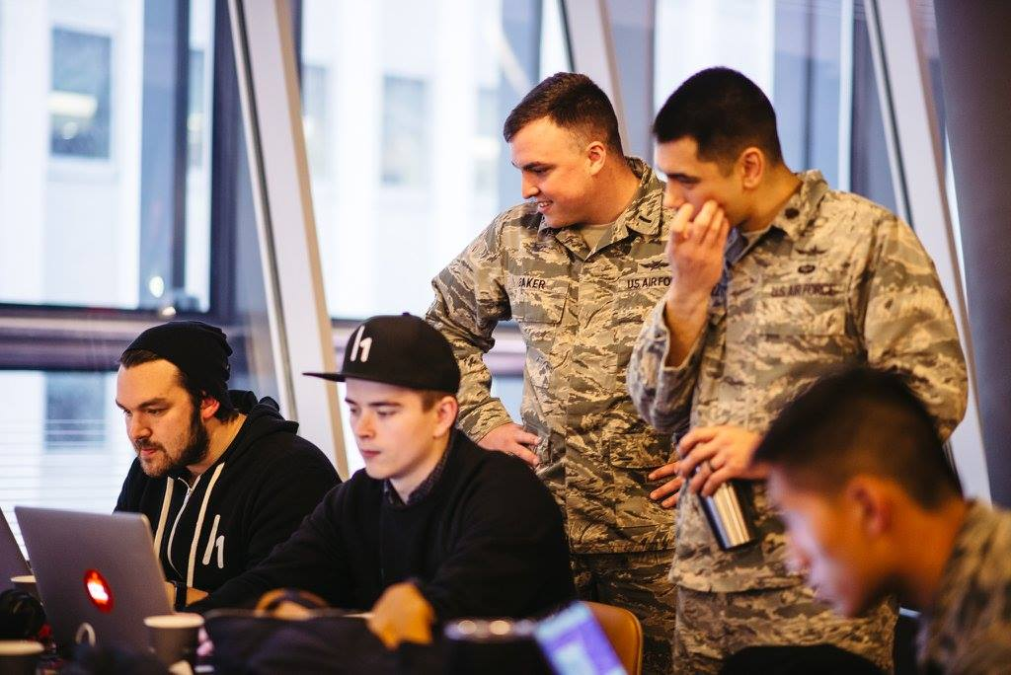
The program began on Dec. 9 with a live hacking event in a New York City subway station. Hackers worked with Air Force officers looking over their shoulders. That sounds stressful, but it didn’t stop Brett Buerhaus (ziot) and Mathias Karlsson (avlidienbrunn) from finding a vulnerability in an Air Force website and then moving into the Pentagon’s unclassified network.
“I didn’t expect how willing they were to work with us to figure out the issue and see how impactful it was,” Buerhaus said. “There’s such a perception of the government being closed off and ready to sweep issues under the rug. It was great seeing how excited they were to work with us. This honestly changes everything, and it’s clear they care about working with us to protect their interests.”
They were rewarded with a $10,650 bounty.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/u-s-air-force-pays-out-103883-in-bug-bounties/