Rail industry gets new cyber directives from TSA
Full article669 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Companies will have to designate cybersecurity coordinators and follow clear rules for incident response.
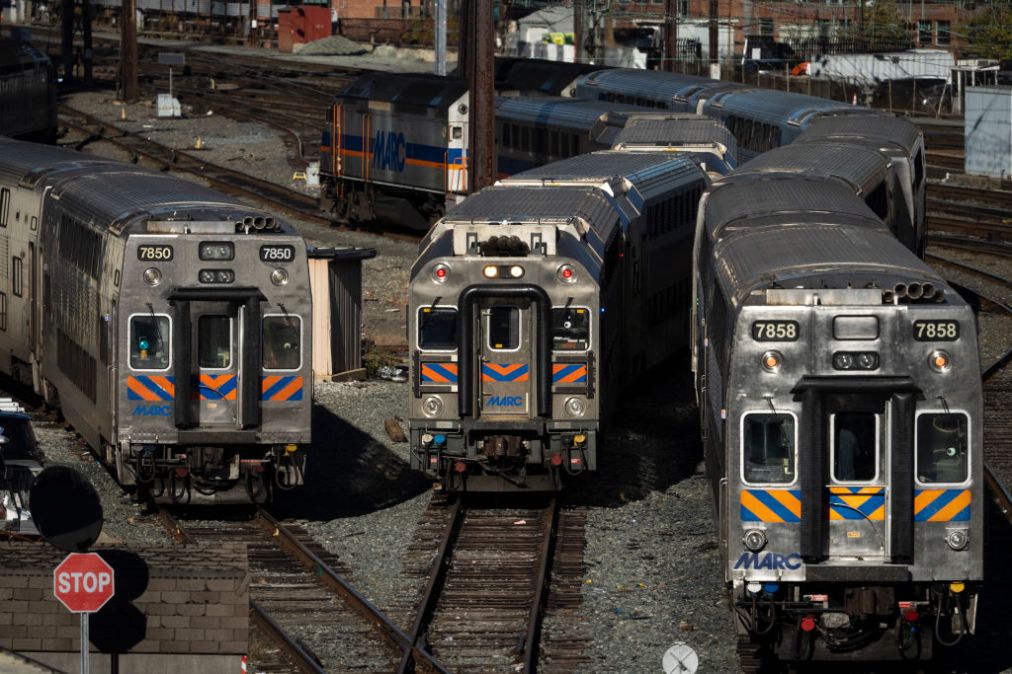
U.S. rail companies must commit more attention and resources to cybersecurity under Transportation Security Administration directives announced Thursday by the Department of Homeland Security.
The new requirements include that surface rail owner and operators designate a cybersecurity coordinator; report a cybersecurity incident to DHS’s cybersecurity agency within 24 hours; complete a vulnerability assessment; and create a plan to respond to cybersecurity incidents.
The directives will cover approximately 80 percent of freight rail and 90 percent of passenger rail, according to a DHS official.
DHS Secretary Alejandro Mayorkas announced that TSA would be rolling out directives for surface transportation in an October speech at the Billington cybersecurity summit.
Early plans for the directives, which would have required companies to report incidents within 12 hours, received criticism from industry and Republicans.
In October, Republicans led by Sen. Rob Portman of Ohio called for DHS’s OIG to investigate the directives, citing industry complaints that the agency should “give adequate consideration to feedback from stakeholders and subject matter experts who work in these fields and that the requirements are too inflexible.”
A DHS official pushed back against the concerns in a call with reporters, noting that the requirements are baseline best cybersecurity practices many companies already follow. DHS officials say that they worked with the industry while developing the directives, including sharing and receiving comments on two drafts.
The directives go into effect December 31. Owners and operators will have 90 days to conduct a cybersecurity vulnerability assessment and 180 days to implement a cybersecurity incident response plan.
The TSA this summer also issued additional security requirements for the pipeline sector after a May ransomware attack on Colonial Pipeline, one of the largest east coat fuel providers. At the time, no mandatory cybersecurity requirements existed for private pipeline operators and owners.
At a House Transportation Committee hearing Thursday, Chairman Peter DeFazio, D-Ore., praised the new directives as a positive step for the industry.
“Voluntary cooperation sometimes isn’t enough,” he said. “The leeches on Wall Street are going to say, ‘Hey, why are you spending all that money on cybersecurity, it’s driving down your stock price? We just want to see you put the money in the bank.'”
Republican Rep. Brian Babin of Texas expressed skepticism.
“We’ve got to be extraordinarily careful as lawmakers and rulemakers to make sure we don’t meddle in something we don’t understand and unintentionally create more bloated regulation or stifle innovation with overly burdensome requirements that don’t truly secure our infrastructure,” he said.
Tim Starks contributed reporting to this story.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/rail-transportation-directives-dhs/