Phishing Attacks Abuse Trusted Email Infrastructure and URL Cloaking to Evade Security Filters
VBSpam Q3 2026 test shows phishers abusing DKIM-aligned domains, Amazon SES, and multi-stage URL cloaking to defeat email filters.
Virus Bulletin's Q3 2026 VBSpam test (AMTSO-LS1-TP207) found phishing campaigns moving payloads past the email itself via browser-fingerprinting gates, redirect chains, and hidden POST requests. Examples include a Dutch McAfee/TotalAV scareware renewal scam, a German overdue-payment Web3 fraud delivered via Amazon SES from DKIM-aligned moolaah.com, and Romanian BCR PSD2 credential phishing embedding IPv6-mapped URLs resolving to 103.193.179.223. Net at Work NoSpamProxy ranked first with a 99.995 score while open-source Rspamd caught only 62.55% of phishing mail.
- Malicious activity shifted to post-click redirects and fingerprinting gates
- DKIM-aligned domains and Amazon SES abuse trust signals
- IPv6-mapped URLs evade simple URL extraction and reputation checks
- Rspamd caught only 62.55% of phishing; NoSpamProxy led at 99.995
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | 31-59-175-195.syd.nbn.aussiebb.net | gets through redirect and tracking infrastructure including 31-59-175-195[.]syd[.]nbn[.]aussiebb[.]net , loadswage[.]com , and eightindigostove[.]com . Th |
| domain | eightindigostove.com | 75-195[.]syd[.]nbn[.]aussiebb[.]net , loadswage[.]com , and eightindigostove[.]com . The final operation was assessed as fake renewal scarew |
| domain | loadswage.com | ture including 31-59-175-195[.]syd[.]nbn[.]aussiebb[.]net , loadswage[.]com , and eightindigostove[.]com . The final operation was as |
| domain | moolaah.com | d through Amazon Simple Email Service from the DKIM-aligned moolaah[.]com domain and urged recipients to open a supposed Mahnschrei |
| domain | opensea.io | itting a concealed POST request and eventually resolving to opensea[.]io during live analysis. Virus Bulletin’s Q3 2026 VBSpam tes |
| domain | web5-4s4c-online-garantibbva.vibtee.com | s IPv4 address 103[.]193[.]179[.]223 and redirected through web5-4s4c-online-garantibbva[.]vibtee[.]com/ro/ before ultimately reaching Google during verificati |
| domain | website-2df62808.mvplineup.com | ent reminder. No file was attached. Its embedded URL led to website-2df62808[.]mvplineup[.]com/audacity/underside , a first-stage page containing deco |
| domain | xmasbrick.com | : Virus Bulletin). Sent from the DKIM-aligned but unrelated xmasbrick[.]com domain, the message embedded an IPv6-mapped address: hxxp |
| url | http://[0000:0000:0000:0000:0000:FFFF:67C1:B3DF | [.]com domain, the message embedded an IPv6-mapped address: hxxp://[0000:0000:0000:0000:0000:FFFF:67C1:B3DF]/11881659 . That notation represents IPv4 address 103[.]193 |
Full article780 words · extracted from gbhackers.com · click to collapse
Phishing operators are increasingly shifting away from malware-laden attachments and toward trusted delivery services, authenticated domains, and multi-stage URL cloaking designed to defeat conventional email inspection.
The continuously running VBSpam comparative test evaluated ten public full email-security products and one open-source solution against wanted, unwanted, and malicious mail streams.
The assessment was conducted under the Anti-Malware Testing Standards Organization (AMTSO) standard, identified as AMTSO-LS1-TP207.
Modern campaigns observed in the test relied on familiar business and consumer pretexts unpaid invoices, banking-consent updates, antivirus renewals, and subscription alerts but removed the indicators that legacy controls most readily detect.
The malicious element was often not an attachment or an obvious payload.
Instead, it emerged after victims clicked through a chain of redirects, browser fingerprinting checks, hidden POST requests, and selectively served destination pages.
One Dutch-language campaign impersonated McAfee and TotalAV, claiming a device was infected with “631 dangerous viruses.”
It combined an urgent account-closure warning with a 90% discount offer, directing targets through redirect and tracking infrastructure including 31-59-175-195[.]syd[.]nbn[.]aussiebb[.]net, loadswage[.]com, and eightindigostove[.]com.
The final operation was assessed as fake renewal scareware or subscription fraud, potentially seeking payment data or affiliate revenue rather than delivering a confirmed malware payload.
The campaign illustrates why attachment-centric filtering is insufficient.
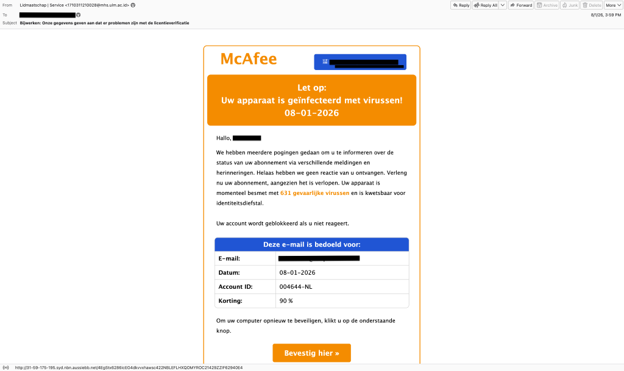
The email used HTML-only social engineering, a legitimate-looking sender domain, separate tracking and unsubscribe links, and live infrastructure whose final destination could change by time, location, or victim profile.
A scanner that evaluates only the original message or performs a simplified link detonation may see little more than a plausible commercial renewal notice.
A separate August campaign used an overdue-payment letter in German to conceal a Web3-related fraud flow.
The email was delivered through Amazon Simple Email Service from the DKIM-aligned moolaah[.]com domain and urged recipients to open a supposed Mahnschreiben, or payment reminder.
No file was attached. Its embedded URL led to website-2df62808[.]mvplineup[.]com/audacity/underside, a first-stage page containing decoy markup, hidden text, a zero-size iframe, and obfuscated JavaScript.
That page gathered browser and timezone signals before submitting a concealed POST request and eventually resolving to opensea[.]io during live analysis.
Virus Bulletin’s Q3 2026 VBSpam test shows that, even as leading gateways maintain near-perfect catch rates, attackers are using browser-aware redirect chains to move the most malicious activity outside the email itself.
Trusted Email Abuse
The chain points to a cloaked crypto or NFT fraud route, rather than verified malware delivery.
The use of an authenticated sender, a clean transactional format, and a fingerprinting gate highlights how attackers can exploit the trust signals that organizations commonly use to reduce false positives.
Banking lures also incorporated URL-format evasion. A Romanian-language phishing email impersonating BCR S.A. claimed that PSD2 consent renewal was mandatory and warned that online and mobile banking access would be restricted without action.
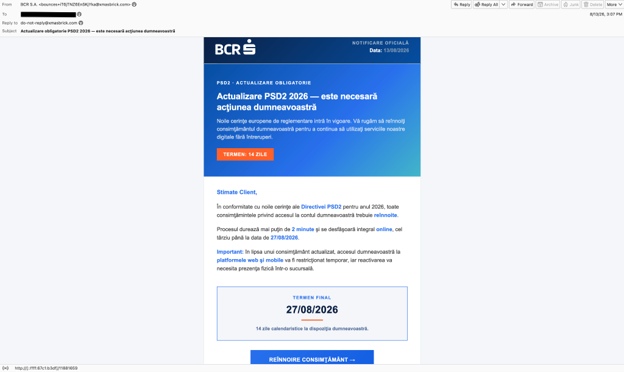
Sent from the DKIM-aligned but unrelated xmasbrick[.]com domain, the message embedded an IPv6-mapped address: hxxp://[0000:0000:0000:0000:0000:FFFF:67C1:B3DF]/11881659.
That notation represents IPv4 address 103[.]193[.]179[.]223 and redirected through web5-4s4c-online-garantibbva[.]vibtee[.]com/ro/ before ultimately reaching Google during verification.
Such formatting can frustrate simplistic URL extraction and reputation checks, while cloaking may return harmless content to automated crawlers.
The likely objective was credential theft, delivered through localized regulatory language, convincing bank branding, and an authenticated-looking email path.
Despite these tactics, top-performing platforms delivered exceptionally high detection rates.
Net at Work NoSpamProxy ranked first with a 99.995 final score, a 100% malware catch rate, 99.990% phishing detection, and no false positives.
Bitdefender GravityZone Premium followed at 99.994, while SEPPmail.cloudfilter scored 99.985. FortiMail, N-able Mail Assure, and N-able SpamExperts also achieved VBSpam+ certification-level results.
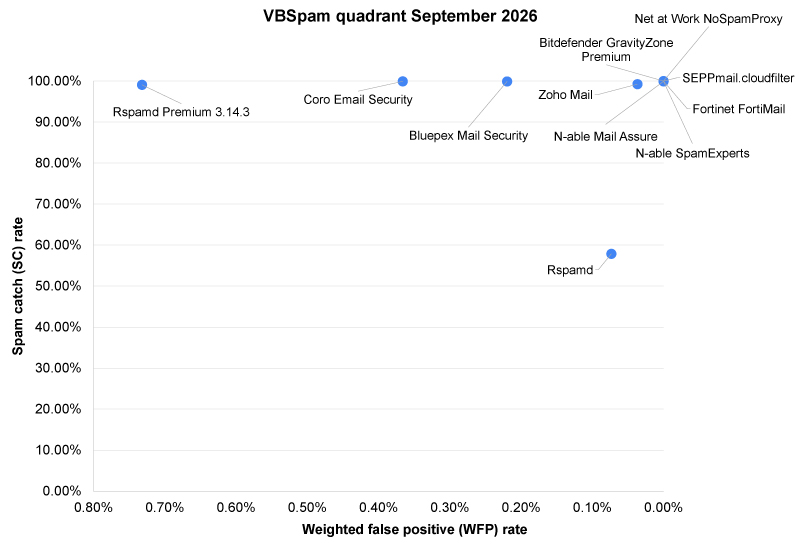
By contrast, the open-source Rspamd deployment recorded a 57.507 final score and caught 62.550% of phishing mail.
The findings reinforce that organizations should treat SPF, DKIM, and DMARC as sender-authentication controls not proof that an email is safe.
Defenses need to normalize obfuscated URLs, follow and repeatedly reassess redirect chains, detect browser-fingerprinting behavior, and correlate email telemetry with web, DNS, and identity signals.
Security teams should also train users to independently access banking, subscription, and invoice portals rather than following links embedded in unsolicited messages.
Those figures describe sender-IP geolocation in the test feed, not necessarily the operators’ physical locations.
Spam observed during the test was predominantly sent from U.S.-based IP addresses, accounting for 67.54% of samples, followed by China at 7.06% and Russia at 3.36%.
★ Learn 7 Metric-Gated AI SOC Deployment Phases – Download Free AI SOC Deployment Playbook 2026.
Mayura Kathirhttps://gbhackers.com/
Mayura Kathir is a cybersecurity reporter at GBHackers News, covering daily incidents including data breaches, malware attacks, cybercrime, vulnerabilities, zero-day exploits, and more.
Text extracted automatically; images, tables and formatting may be missing. Original: https://gbhackers.com/trusted-email-abuse/