Internal needs on the black market
Full article361 words · extracted from securelist.com · click to collapse



At the end of 2010 I noticed a big wave of recruitment spam for money mule work. Initially, the criminals used spam sent from hacked email accounts. I even got some messages like this from people I know personally:
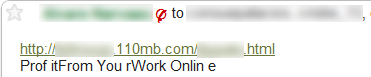
Right after that, to speed-up the recruitment process, the messages came via Windows Live Messenger (aka MSN):
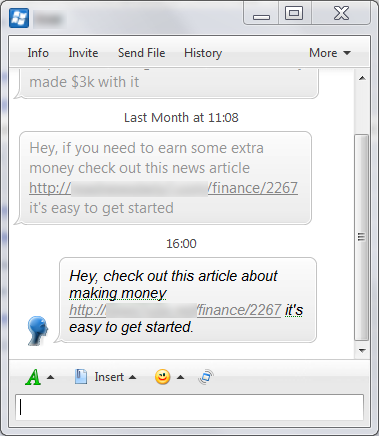
And of course, the criminals also used legitimate accounts that had been hacked to spread their messages. Finally, right before the end of the year I saw a big campaign on Facebook, especially targeting Spanish speaking communities. But yesterday I was completely surprised when I found an advertising banner on a legitimate IT site leading to the same page – money mule recruitment.
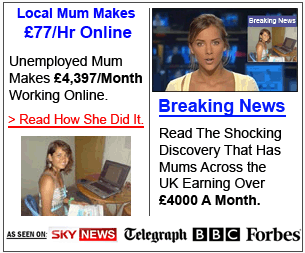
All these developments make think there is a huge demand on the black market for money mule workers. The criminals seem to have enough stolen information like credit card PINs, as well as details for online banking accounts and payment systems. Their problem now is how to launder the money they have made. Our statistics confirm there is a clear growth in Trojan-Spy malware able to steal any kind of personal information. This includes well known Trojans like Zbot (Zeus) or SpyEye.
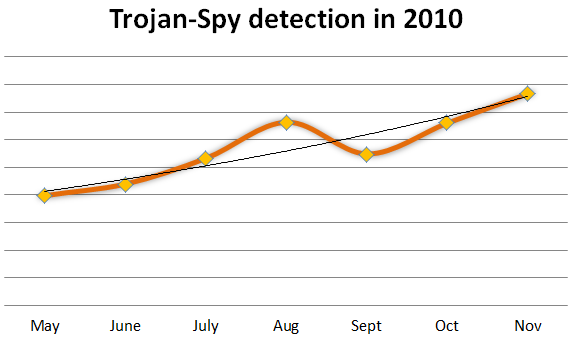
It’s worth remembering that money mule activity is considered illegal. Basically, if nobody wanted to launder their money, cybercriminals would find it much harder to make money from stolen account details. Everyone can contribute in their own way to the global security, not just AV and other Security companies.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/internal-needs-on-the-black-market/29812/