RootedCON V
Full article453 words · extracted from securelist.com · click to collapse



It was five years ago when a group of computer security enthusiasts decided to gather together and organize a security conference mainly for a Spanish-speaking audience.
Last week RootedCon celebrated its fifth birthday, gathering more than 1000 attendees. It is now firmly established as the most important security event in Spain.
The talks covered several hot topics including cyberintelligence, crytpo analysis, offensive security and cyberdefense, among others. Thanks to the organizers we had the chance to witness a panel on cyber-weapons, with some of the most authorized voices in Spain discussing the topic, including representatives from CNPIC, CCN and the new Spanish Cyberdefense Command group.
When attending such panels you can get the impression that panelists are highly trained in political discussion and avoid all the hot topics and difficult questions, and sometimes you need to read between lines.
It was not the case with this one. When directly asked for a definition of ‘cyberweapon’, we heard a surprising broad one – “any software developed with a malicious purpose”. When asked about the position of the Cyberdefense Command on such weapons, the answer was “we should arm ourselves in order to dissuade our enemies”. Finally, when asked about developing such weapons, the answer was “well…” followed by some laughs and “let’s say we are focused on the defensive side”.
One of the most interesting talks was from the State Attorney, Jorge Bermudez, explaining some of the difficulties of prosecuting fast-moving digital crimes with laws designed decades ago – and how he is “exploiting” these laws to put these criminals behind bars. It was a really educative and inspiring talk, helping us understand how we can help in such labors.
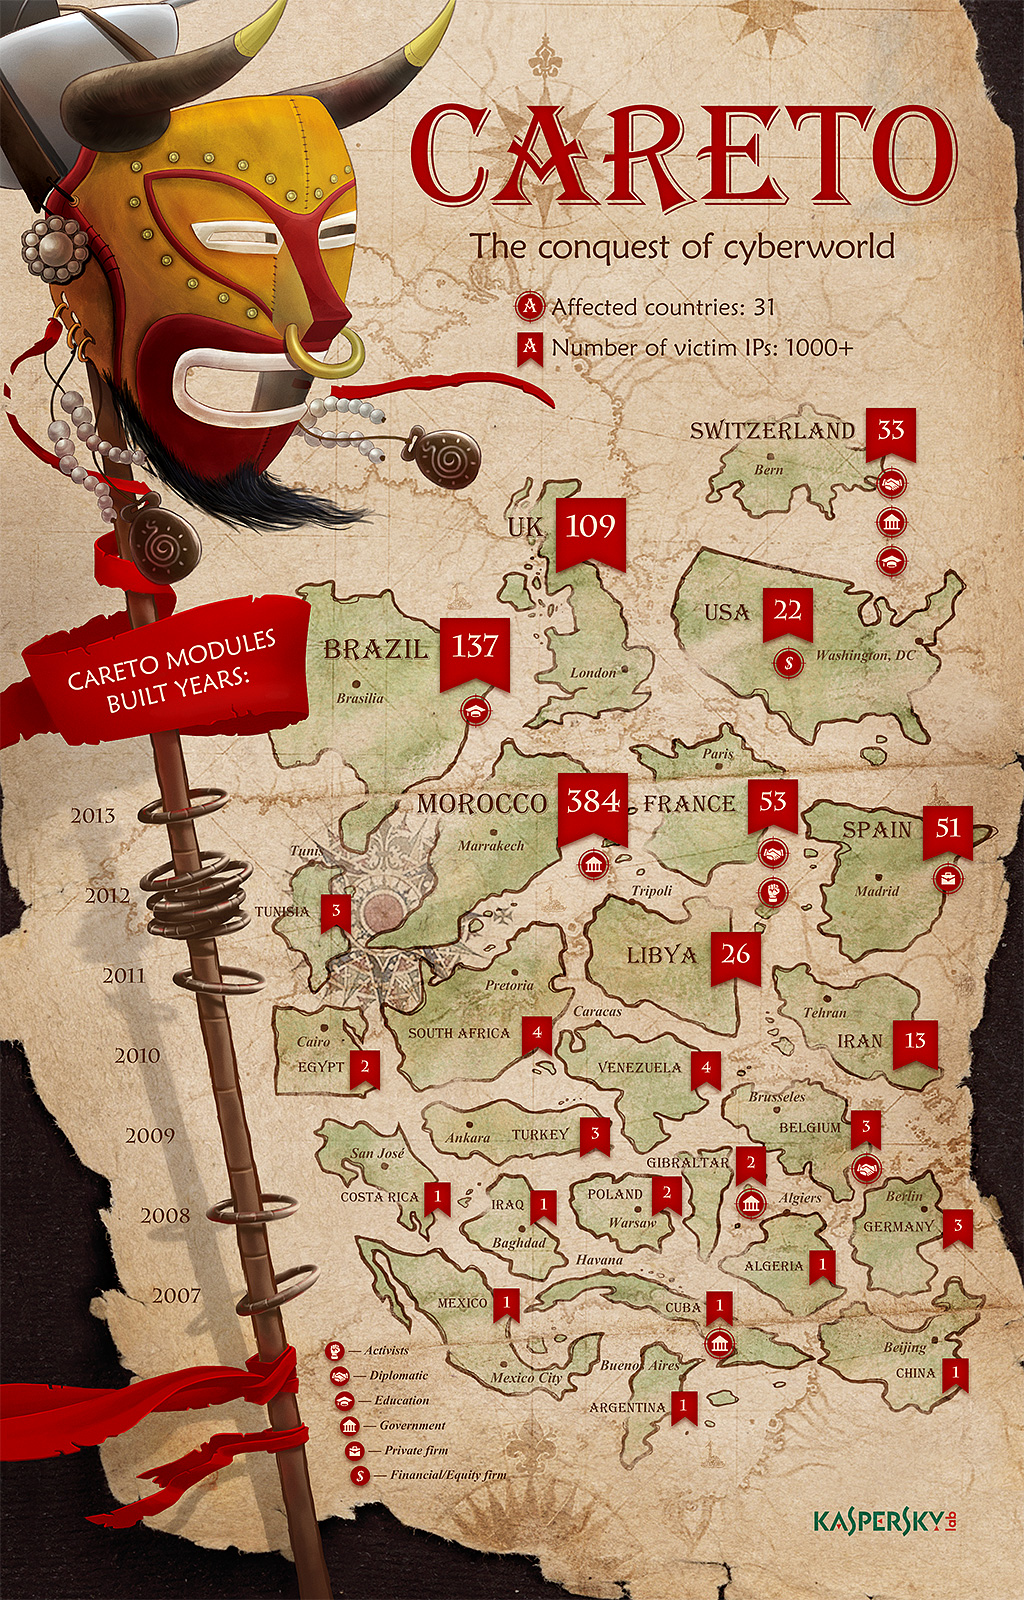
Finally, we would like to mention that one of the most repeated words I heard during the conference was Careto! It even appeared in one of the presentations:
Ok, the picture is not very good, but you can recognize the Careto infographic.
All the videos of the presentations (all, except two, in Spanish) will be available in a few weeks at rootedcon.es.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/rootedcon-v/58547/