Hello from CeBIT!
Full article209 words · extracted from securelist.com · click to collapse



If you happen to be anywhere near Hannover these days, feel free to stop by our stand at CeBIT 2007. It is in Hall 7, stand A06. Here’s how it looks:
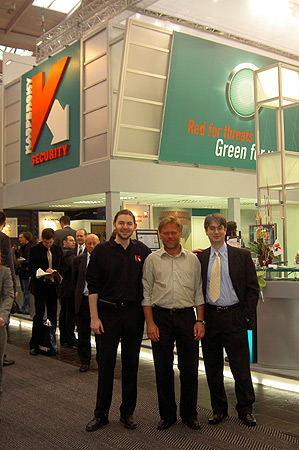
One of the hot subjects here is mobile malware. Actually, as Roel was doing a routine scan of the neighborhood, the software he was using kept crashing. We were able to trace the problem and find the reason for this. Looks like there were simply too many visible Bluetooth devices around, more than the developers ever expected to be in one place.
Greetings from a Bluetooth-crowded CeBIT!
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/hello-from-cebit/30305/