Emotet's tax
Full article514 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Researchers at Cofense say the operators behind the Emotet botnet "have upped their game" for 2022's tax season.
IRS-themed phishing campaigns are reliable signs of spring, so the question each year becomes, “What’s new?”
Researchers at Cofense are answering the question with evidence that the operators behind the Emotet malware “have upped their game” for this tax season. The cybersecurity company points to sham emails that are intended to look more convincing and pull more tricks than similar campaigns in previous years.
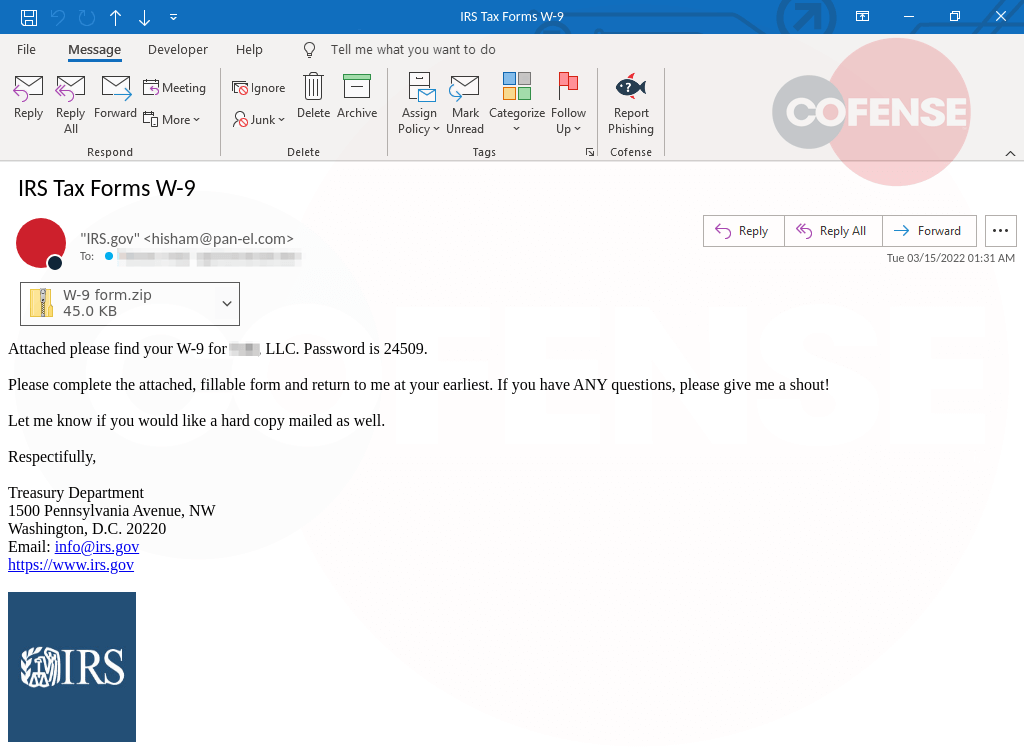
Cofense says the group’s malicious messages now include the IRS logo; make specific mention of the organization that employs the targeted people; and include a password that works to open a file archived attached to the email.
What seems like a convenient nudge to open and save a W-9 form actually results in Emotet propagating itself on the recipient’s system: “When the Office-macro-laden spreadsheets enclosed in the password-protected archives are opened, they request that macros be enabled. If macros are enabled, Emotet .dll files are delivered to the victim’s computer,” Cofense says.
Emotet’s first goal is to propagate itself as a botnet, which can then be used for other malicious activities. Researchers from Lumen’s Black Lotus Labs noted earlier this month that at least 130,000 unique computers had been infected since late 2021. The malware’s operators have been associated with the Conti cybercrime group and a similar platform known as TrickBot, which appears to have gone offline earlier this year.
Phishing emails are just one part of a broad gallery of tax-season scams, of course. The IRS regularly updates its warning page, especially as the mid-April deadline for filing U.S. federal taxes approaches each year. In many ways, it’s just like Christmas.
Here’s an example of the malicious emails found by Cofense:
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/cofense-emotet-irs-phishing/