IBM interns find 19 vulnerabilities in corporate check
Full article564 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Two university students who work for IBM’s red-teaming unit have found 19 previously undisclosed flaws in the automated systems that companies use to check visitors into their facilities.
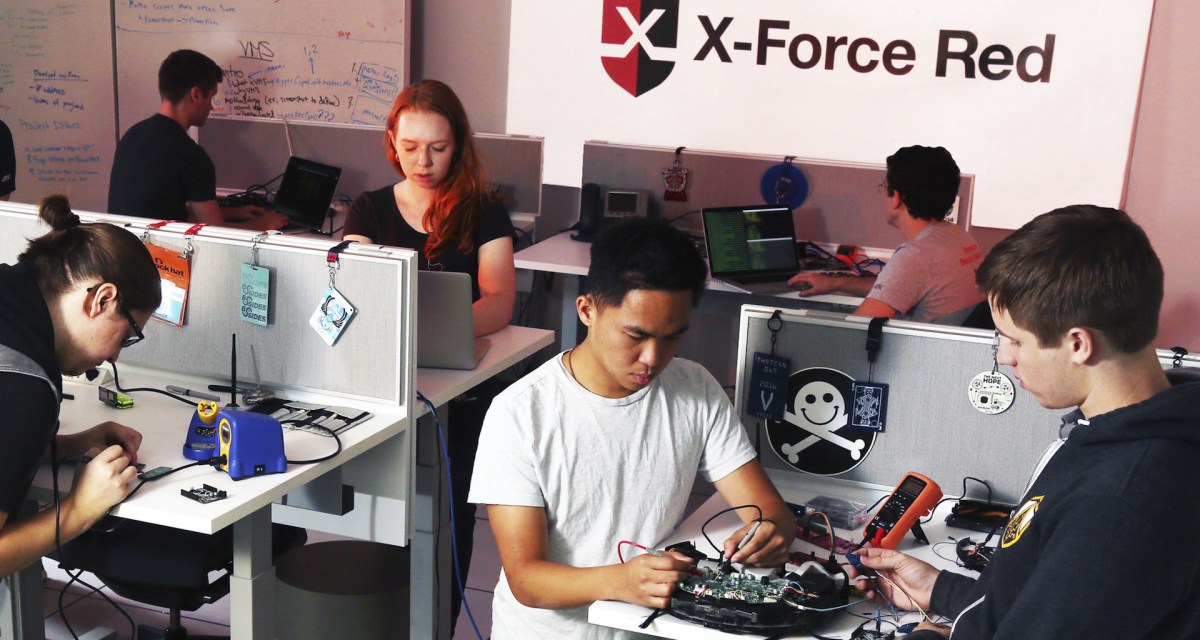
A pair of precocious interns at IBM’s red-teaming unit has found 19 previously undisclosed vulnerabilities in the automated systems that companies use to check visitors into their facilities.
A hacker exploiting the security flaws could access visitor logs, contact information, and other company data, and use that access to go after corporate networks, the IBM X-Force Red researchers said.
The study of five popular visitor-management systems is a warning of the risk of automating common societal tasks without security precautions. These systems are supplanting security guards as an efficient way of enabling access to a building, and apparent negligence in their architecture leaves them vulnerable.
The interns, Hanna Robbins and Scott Brink, are students at the University of Tulsa and the Rochester Institute of Technology, respectively, according to their LinkedIn profiles. Robbins and Brink found default administrative login credentials that would give attackers complete control of a visitor-management application. They also uncovered software flaws that could let a hacker use Windows shortcut keys and dialogue boxes to wrest control of the application.
The data held by the visitor systems could be of interest to corporate competitors or foreign intelligence agencies intent on economic espionage.
“Knowing, for instance, that the CEO of a related company has been visiting every day for the last few weeks could be valuable intelligence to collect,” IBM’s Daniel Crowley wrote in a blog post Monday.
Several of the affected vendors have already patched their software or are planning to, IBM said. If no patch is coming for certain software, companies should determine how exploitable a vulnerability is and work to isolate affected systems from others, Crowley advised.
The research points to the need to shore up security in visitor management systems as they continue to proliferate. The global market for these check-in kiosks is expected to grow from $824 million in 2018 to $1.3 billion in 2025, according to MarketResearch.com.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/ibm-interns-find-19-vulnerabilities-corporate-check-systems/