Spot the imposter: pretending to be the original
Full article309 words · extracted from securelist.com · click to collapse



Some months ago I wrote a blog post called “Rogue AV raising the stakes” which mentioned a new trend in the graphical user interfaces of Fake Anti-viruses. Our predictions were correct, as today my colleague Fabio Assolini found a Web site with an interface very similar to Kaspersky Anti-Virus. See for yourself:
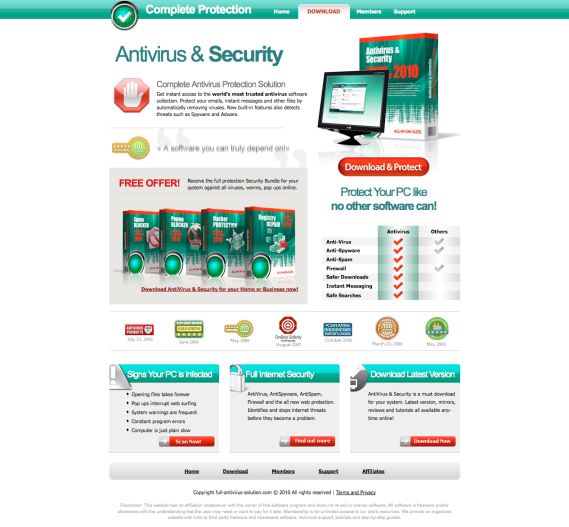
This isn’t the first time we’ve found this kind of fake imitation of our solutions. The interesting part is that during our research we found fake versions of other Anti-Virus solutions on the same malicious host. Can you spot the difference?
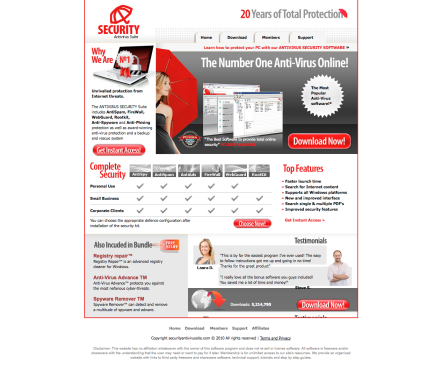
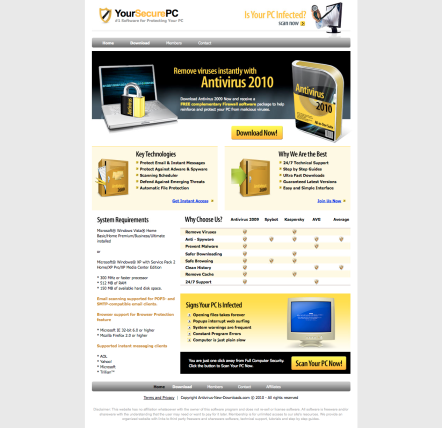
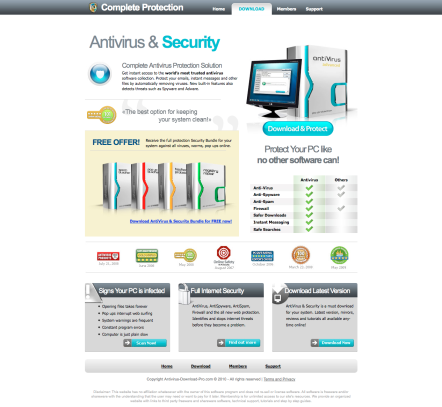
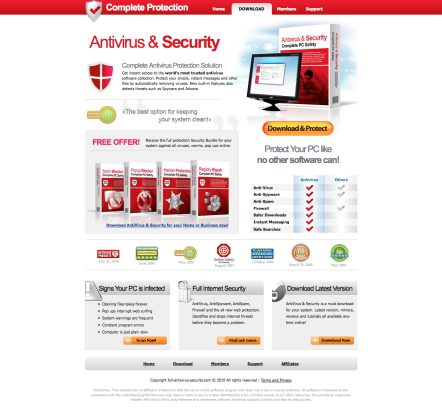
These are just some of the examples. Since some Internet users know what the most popular Anti-Virus solutions look like they can be confused and pay for a Rogue AV solution. This is the main goal of the criminals; to confuse as many people they can, and to get as much money as possible.
On this same malicious server we found 256 different malicious rogue domains with different content but with the same intention: to cheat people by making them pay money for nothing.
Please be careful and always check the domain of the page you’re visiting. Don’t be a victim of criminals!
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/spot-the-imposter-pretending-to-be-the-original/29695/