Japan's Tokio Marine is the latest insurer to be victimized by ransomware
Full article598 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
It's the third to announce a successful attack since March.
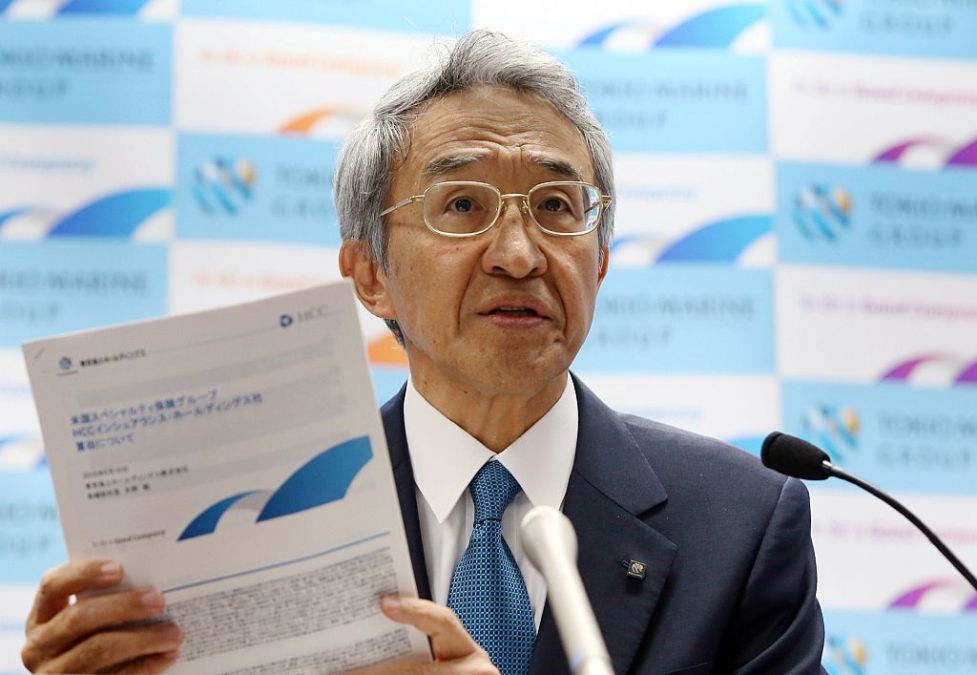
Ransomware struck Japan’s largest property and casualty insurer, Tokio Marine Holdings, at its Singapore branch, the company disclosed on Monday.
Tokio Marine, which has a U.S. division and offers a cyber insurance product, said it did not have any immediate indication that any customer information was breached. Such data could be a smorgasbord for hackers who would use the data to extort victims based on their coverage amounts.
It’s at least the third major insurer to disclose a ransomware attack in recent months, following CNA and AXA. And it’s the second insurer just this week, with Ryan Specialty Group — fresh off launching an initial public offering — to disclose a cyber incident.
Cyber insurers have, of late, taken to asking more detailed questions about policyholders’ cybersecurity safeguards as a condition for providing coverage. But the spate of recent successful attacks suggests that insurers, too, might need to step up their defenses.
“We sincerely apologize for any inconvenience and concern caused to our customers or related parties,” Tokio Marine said. “The Group has taken information security safeguards so far and will endeavor to make further efforts to keep our customer information as well as our confidential information protected.”
Tokio Marine said it was still trying to determine the scope of the damage and had hired an outside vendor to help. The company said it isolated the affected network, and notified local law enforcement. It did not announce when the attack occurred, or when investigators discovered the breach.
Ryan Specialty Group, which has ventured into the cyber insurance market, said it discovered unusual activity in April and found that some employee email accounts were accessed without authorization. By June, the company found that some personal information for “a limited number of individuals” was accessible.
Congress has been debating mandatory cyber incident disclosure rules for certain industries, with one bill seeking 24-hour notification.
Ryan Specialty Group couldn’t determine whether the information, which included sensitive data like Social Security numbers, was actually accessed. The insurer is providing two years credit monitoring and identity protection services to anyone whose information was accessible, a standard practice in data breach incidents.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/tokio-marine-ryan-specialty-group-ransomware-cyber-insurance/