Virus Bulletin 2012: From Privacy Issues to Exploit Sales
Full article416 words · extracted from securelist.com · click to collapse



Greetings from Dallas, Texas, where the anti-malware industry is meeting for the 22nd edition of Virus Bulletin.
The first day of the conference brought us some interesting themes to think about. The event started with the keynote by privacy rights advocate Christopher Soghoian who spoke about the sale of vulnerabilities and exploits to governments around the world and the ethics associated with middlemen who has no interest in end user security. Soghoian called on the exploit sales industry to consider self-regulation to introduce a higher level of transparency to the business. The underlying question was: do we need to regulate the business of selling exploits, or do we need to put pressure on companies to fix or write better code?
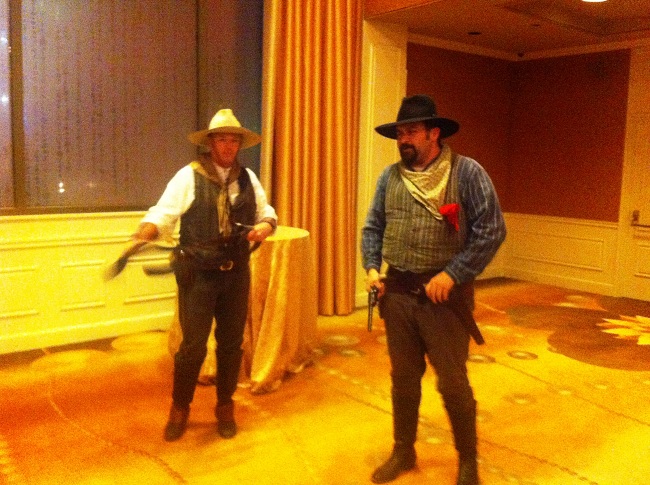
Theyre not middlemen, just traditional Texan cowboys
My colleague Vicente Diaz presented Im not a number, Im a free man a talk about privacy issues and how on-line advertisement companies are tracking the end user surfing the web. As he stated if we visit a single popular newspaper, we do an average of 11.3 requests to different tracking sites. Over 93% of the top 100 most popular sites include at least one request to tracking sites. A single request to a site may result in more than 10 cookies created in your browser. Why so much tracking? According Vicente the answer is money. It’s not about advertisements; it’s about profiling users In the near future, all companies could have access to super-profiles where all our data is available, and then the computer will decide….
Colleagues from other vendors also presented interesting topics, such as Candid West, from Symantec, presenting Where do we stand with banking trojans today?
and Righard Zwienenberg, from ESET, about BYOD:(B)rought (Y)our (O)wn (D)estruction?.
The conference continues all week, stay tuned for more blog posts about the event.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/virus-bulletin-2012-from-privacy-issues-to-exploit-sales-2/32042/