FBI: Someone broke into an email account on Clinton's private server
Full article1,033 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Newly released FBI documents, focused on an investigation into the use of a private email server used by former Secretary of State Hillary Clinton, shows that a single email account on the server was breached by an “unauthorized” Tor user.
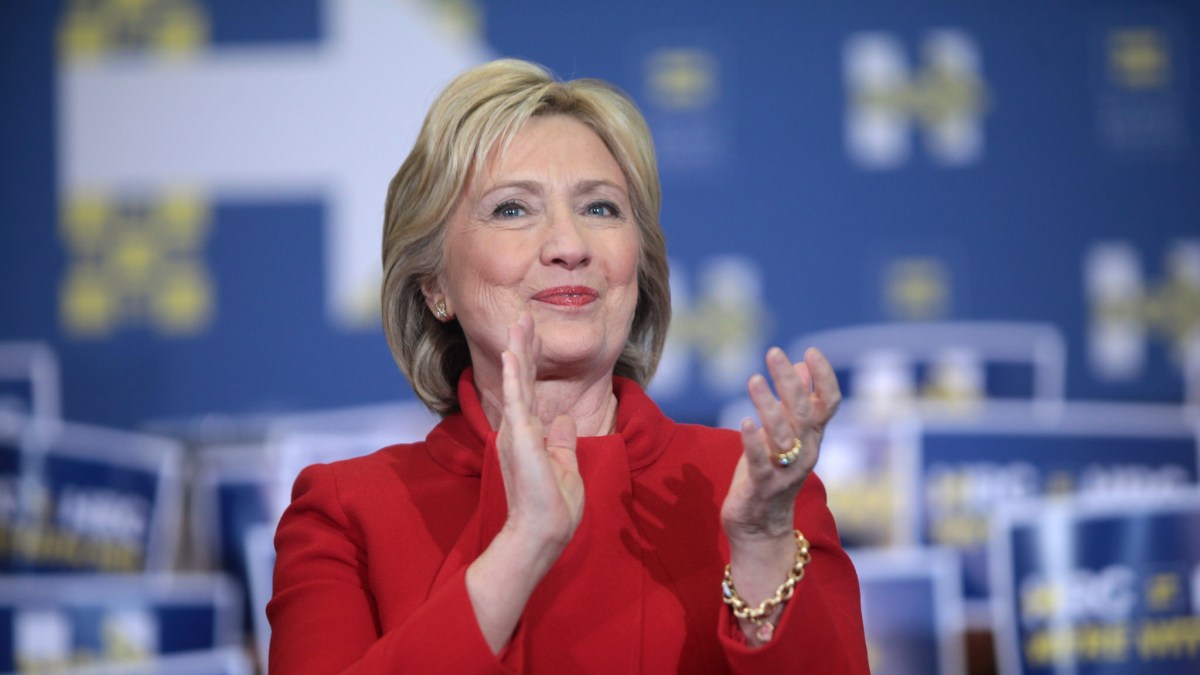
Newly released FBI documents, focused on an investigation into the use of a private email server by former Secretary of State Hillary Clinton shows that a single email account on the server was breached by an “unauthorized” Tor user.
It appears someone was able to acquire the credentials to an email owned by a former Bill Clinton staffer and then proceeded to access the email while using Tor, an anonymous web browsing service, on Jan. 5, 2013. The FBI could not determine how this hacker was able to obtain the staffer’s username and password.
The incident represents the first known digital intrusion into Clinton’s email system, disclosed by the bureau. Cybersecurity experts, however, are cautious to call the event a “smoking gun,” explaining that it does not suggest — at least on its own — that the server was “hacked.”
Due to a lack of publicly available evidence and information, it remains unclear exactly how Clinton’s private server system was configured, controlled, and accessed, all of which might help explain how a hacker could feasible gain administrative server controls from a single account, explained K2 Intelligence managing director Milan Patel and ThreatConnect Chief Intelligence Officer Richard Barger.
The FBI had previously stated that they did not find evidence to show Clinton’s email server was hacked.
“Based on the information available, if we saw this incident in a [security operations center] environment then I think we would probably create a ticket to look into the account activity but we wouldn’t assume the server was compromised,” said Barger, a former U.S. Army intelligence analyst and security consultant.
In July, FBI Director James Comey called Clinton and her aides’ conduct “extremely careless” though he ultimately declined to recommend charges in connection with the democratic presidential candidates’ email practices.
“The FBI’s review of available…web logs showed scanning attempts from external IP addresses over the course of [IT manager Bryan] Pagliano’s administration of the server, only one appears to have resulted in a successful compromise of an email account on the server,” the new report reads.
The 60-page FBI report does not, for example, mention if the individual who breached this staffer’s email account engaged in downloading or sending new emails during the time period in question. It also does not specify what sort of administrative controls the user may have been privileged to by default.
But if this unnamed Tor user was in fact a malicious actor, then they would have likely sought additional privileges — moving laterally across the database — so as to access other information stored elsewhere on the server, explained Patel, a former chief technology officer for the FBI Cyber Division.
Such an operation may have hypothetically taken the form of a targeted email phishing campaign, sending weaponized malware-laden email attachments to address book contacts that would otherwise trust messages sent by the staffer’s account.
In short, the presence of a Tor user on a private email system might be a “red flag,” said Barger, but it is not a sure-fire sign of an intrusion on its own. Also, it does not indicate a vulnerability on the server.
Dave Aitel, a former NSA security analyst, told Wired that it appears Clinton’s private IT staff “weren’t auditing and restricting IP addresses accessing the server.”
“That’s annoying and difficult when your user is the Secretary of State and traveling all around the world … But if she’s in Russia and I see a login from Afghanistan, I’d say that’s not right, and I’d take some intrusion detection action. That’s not the level this team was at,” said Aitel.
There are some spectators who are “overreacting and jumping to conclusions [about the presence of a Tor user in this instance],” said Patel, “when the reality is that it could mean much more or much less than we think right now … The fact of the matter is that we simply don’t know enough, at the moment, about this hacker’s activity.”
More Scoops

FBI takes down massive China-based cybercrime network that caused $1.9B in losses
Outsider provided phishing kits and infrastructure for cybercriminals to scam victims with lures claiming they missed packages, had unpaid tolls or parking violations.
Iranian hackers, Handala, claim to compromise FBI Director Kash Patel’s personal data
FBI targeted with ‘suspicious’ activity on its networks
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/fbi-someone-broke-email-account-clintons-private-server/