New IoT Malware Uses Public Linux Exploits to Gain Root and Launch DDoS Attacks
Nozomi details KATARU, an IoT botnet that brute-forces Telnet, exploits public Linux kernel flaws for root access, and launches multi-protocol DDoS attacks.
KATARU, discovered after honeypot Telnet brute-force activity from a Vietnamese IP, downloads an ARM payload (vlxx.arm) and attempts privilege escalation by editing /etc/passwd or exploiting CVE-2026-46300 (Fragnesia), CVE-2026-43284 (Dirty Frag), and CVE-2026-31431 (Copy Fail). It combines Mirai-style TCP, UDP, ICMP, HTTP, QUIC and DNS floods with application attacks against Minecraft, FiveM, OpenVPN and WireGuard. The malware uses X25519 and ChaCha20-Poly1305 encrypted C2, unusually broad persistence across systemd, cron, init frameworks, and Android hooks, plus anti-debugging and decoy traffic to hinder analysis. Implementers copied x86 shellcode into the ARM binary and reused an RFC 7748 test-vector key, indicating low-quality but rapidly evolving commodity development.
- Brute-forces Telnet, then escalates from low-privilege access to root via public kernel exploits
- Exploits CVE-2026-46300, CVE-2026-43284 and CVE-2026-31431, but embeds mismatched x86 shellcode
- Encrypts C2 with X25519 key exchange and ChaCha20-Poly1305, yet pins an RFC 7748 test-vector key
- Attempts persistence across systemd, cron, rc.local, OpenWrt, U-Boot, and rooted Android boot paths
- Defends with ptrace/Valgrind anti-analysis checks and decoy beacon traffic that pollutes IoCs
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2026-31431 | Local Privilege Escalation (Copy Fail) in Linux Kernel algif_aead Interface CVE-2026-31431 ('Copy Fail') is an incorrect resource transfer between spheres (CWE-669/CWE-1288) in the Linux kernel's algif_aead implementation of the AF_ALG userspace crypto interface, introduced roughly nine years ago (around 2017, per public reporting) when commit 72548b093ee3 switched AEAD operations to in-place handling even though the source and destination buffers come from different mappings. A local, unprivileged user can trigger the flaw by performing AEAD operations through the AF_ALG socket interface, causing the kernel to mishandle the copy of ciphertext and associated data. Successful exploitation provides a reliable local privilege escalation to root (C:H/I:H/A:H per the CVSS vector). Nearly every major Linux distribution and enterprise platform is exposed, including the kernel itself, Red Hat Enterprise Linux (including AUS, EUS, TUS and Update Services for SAP Solutions), OpenShift Container Platform, Amazon Linux, Ubuntu, Debian, openSUSE Leap, SUSE CaaS Platform, NixOS, and Linux-based products from Arista and Siemens. The flaw has public proof-of-concept code, a 99.9% EPSS score, and was added to CISA's Known Exploited Vulnerabilities catalog on 2026-05-01, indicating exploitation in the wild (ransomware use is unknown). Do: Patch by installing the kernel update for CVE-2026-31431 through your distribution's security channel (Red Hat Enterprise Linux including AUS/EUS/TUS/SAP channels, OpenShift, Amazon Linux, Ubuntu, Debian, openSUSE Leap, SUSE CaaS Platform, NixOS, and Arista/Siemens firmware/software as applicable) and reboot into the patched kernel; the data provides no fixed version numbers, so defer to vendor advisories. Because the flaw is in CISA's KEV catalog (added 2026-05-01) with a 99.9% EPSS score, prioritize internet-reachable and multi-user systems first and follow BOD 22-01 guidance for cloud services. Check running kernel versions ('uname -r') and distribution advisory status to confirm you are on a fixed build. | 7.8 | 100% | KEV PoC ×5 |
| masshundreds of millions to billions of installations (servers, cloud instances, desktops, and Android/embedded devices running affected kernel generations) | |
| CVE-2026-43284 | Linux kernel ESP-in-UDP decrypts in place over shared splice pages (CWE-123) CVE-2026-43284 is a write-what-where memory-safety flaw (CWE-123) in the Linux kernel's xfrm/ESP (IPsec) code: the IPv4/IPv6 UDP datagram send paths fail to mark pages spliced into a UDP skb with SKBFL_SHARED_FRAG when MSG_SPLICE_PAGES attaches pipe pages, so the ESP input path wrongly treats the packet as privately owned and decrypts it in place over memory the skb does not exclusively own. It is triggered when locally generated UDP traffic built from spliced pipe pages is processed by the ESP decryption path, typically in IPsec NAT-traversal (ESP-in-UDP, UDP port 4500) configurations; the in-place decrypt can corrupt or expose data still referenced by the pipe or other owners of those shared pages. A local, low-privileged attacker can thereby cause high-severity confidentiality, integrity, and availability impact that extends beyond the packet itself (CVSS 3.1: 8.8, scope changed); no remote or unauthenticated trigger is described. Any Linux system running a kernel with the vulnerable UDP splice and ESP-in-UDP paths is affected, most importantly IPsec VPN gateways and clients; the advisory lists no affected version ranges. No public proof-of-concept or confirmed in-the-wild exploitation is known (not on CISA KEV), but EPSS assigns a 93.2% probability of exploitation within 30 days (100th percentile), so patching should not be deferred. Do: Apply your distribution's kernel security update containing the xfrm/esp fix for CVE-2026-43284 and reboot into the patched kernel, prioritizing IPsec VPN gateways and clients that use ESP-in-UDP NAT-T (UDP/4500). Until patched, restrict untrusted local users from sending splice-based (MSG_SPLICE_PAGES) UDP traffic through IPsec-protected paths, or temporarily avoid ESP-in-UDP encapsulation where feasible. Verify the fix via your vendor's package changelog, as the advisory does not name specific fixed version numbers. | 8.8 | 93% |
| mass≈1M+ Linux installations carry the vulnerable code in default distro kernels; hundreds of thousands of hosts expose IPsec NAT-T (UDP/4500) in public internet… | ||
| CVE-2026-46300 | In the Linux kernel, the following vulnerability has been resolved: In the Linux kernel, the following vulnerability has been resolved: net: skbuff: preserve shared-frag marker during coalescing skb_try_coalesce() can attach paged frags from @from to @to. If @from has SKBFL_SHARED_FRAG set, the resulting @to skb can contain the same externally-owned or page-cache-backed frags, but the shared-frag marker is currently lost. That breaks the invariant relied on by later in-place writers. In particular, ESP input checks skb_has_shared_frag() before deciding whether an uncloned nonlinear skb can skip skb_cow_data(). If TCP receive coalescing has moved shared frags into an unmarked skb, ESP can see skb_has_shared_frag() as false and decrypt in place over page-cache backed frags. Propagate SKBFL_SHARED_FRAG when skb_try_coalesce() transfers paged frags. The tailroom copy path does not need the marker because it copies bytes into @to's linear data rather than transferring frag descriptors. NVD description · AI analysis pending | 7.8 | 9% |
| — |
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| sha256 | 13382c16e2401b07451577b46e634b8031ec254d98b876e59692b5fa22abc1d4 | nd execute an ARM payload named vlxx.arm, with SHA-256 hash 13382c16e2401b07451577b46e634b8031ec254d98b876e59692b5fa22abc1d4. Staging markers including condi72 and condixx link the del |
| sha256 | 6fbae3505ae0d638b820165c572d548ce92dda71e82dc47e8efe13f30617f35f | 634b8031ec254d98b876e59692b5fa22abc1d4 SHA-256 Hash (ARM32) 6fbae3505ae0d638b820165c572d548ce92dda71e82dc47e8efe13f30617f35f SHA-256 Hash (ARM32) 9d87e6615c810907443ebd5e915f3b35099c3b |
| sha256 | 9d7cd4948a1fcbaeadc425752fce9a933bd6fc41eeede030dffd7b99b3bc51d5 | 5f3b35099c3b5c6b6c684637138a7f8ec9cebc SHA-256 Hash (AMD64) 9d7cd4948a1fcbaeadc425752fce9a933bd6fc41eeede030dffd7b99b3bc51d5 IPv4 Address 160[.]191.242.92 Telnet credential brute-force |
| sha256 | 9d87e6615c810907443ebd5e915f3b35099c3b5c6b6c684637138a7f8ec9cebc | 2d548ce92dda71e82dc47e8efe13f30617f35f SHA-256 Hash (ARM32) 9d87e6615c810907443ebd5e915f3b35099c3b5c6b6c684637138a7f8ec9cebc SHA-256 Hash (AMD64) 9d7cd4948a1fcbaeadc425752fce9a933bd6fc |
| sha256 | cc76bc218627279ecb4d0ce74ad2651e9db9e3e843e35d6569576e056e3a9218 | imperfect. IOCs Indicator Type Value SHA-256 Hash (Loader) cc76bc218627279ecb4d0ce74ad2651e9db9e3e843e35d6569576e056e3a9218 SHA-256 Hash (ARM32) 13382c16e2401b07451577b46e634b8031ec25 |
Full article905 words · extracted from gbhackers.com · click to collapse
A newly observed IoT malware family dubbed KATARU targets internet-exposed devices through Telnet credential brute-forcing, then attempts to gain root privileges with publicly available Linux kernel exploits before enrolling compromised systems in a DDoS botnet.
The sample combines familiar Mirai-style flooding functions with encrypted command-and-control, broad persistence logic, anti-analysis checks and decoy network activity designed to complicate incident response.
Following successful access, the operator used BusyBox commands to download and execute an ARM payload named vlxx.arm, with SHA-256 hash 13382c16e2401b07451577b46e634b8031ec254d98b876e59692b5fa22abc1d4.
Staging markers including condi72 and condixx link the delivery flow to a basic loader believed to be related to previously public dropper code.
KATARU’s defining feature is its attempt to turn initial, low-privilege access into full root control.
The malware first checks whether /etc/passwd is writable; if it is, KATARU modifies the root:x: entry to root::, potentially allowing passwordless use of su.
If that shortcut fails, it attempts multiple Linux local privilege-escalation exploits derived from public proof-of-concept code.
These include CVE-2026-46300, known as Fragnesia, which affects Linux kernel XFRM ESP-in-TCP processing and can enable a local attacker to modify page-cache-backed read-only files and escalate privileges.
The malware also embeds code associated with the Dirty Frag vulnerabilities, including CVE-2026-43284, and the Copy Fail flaw, CVE-2026-31431.
Both vulnerability families have been documented as local root-escalation risks affecting Linux kernel networking or cryptographic subsystems.
However, analysis shows that the ARM KATARU binary contains x86-oriented shellcode within its privilege-escalation routines.
That mismatch strongly indicates the authors copied exploit material without adequately porting or testing it for the device architecture.
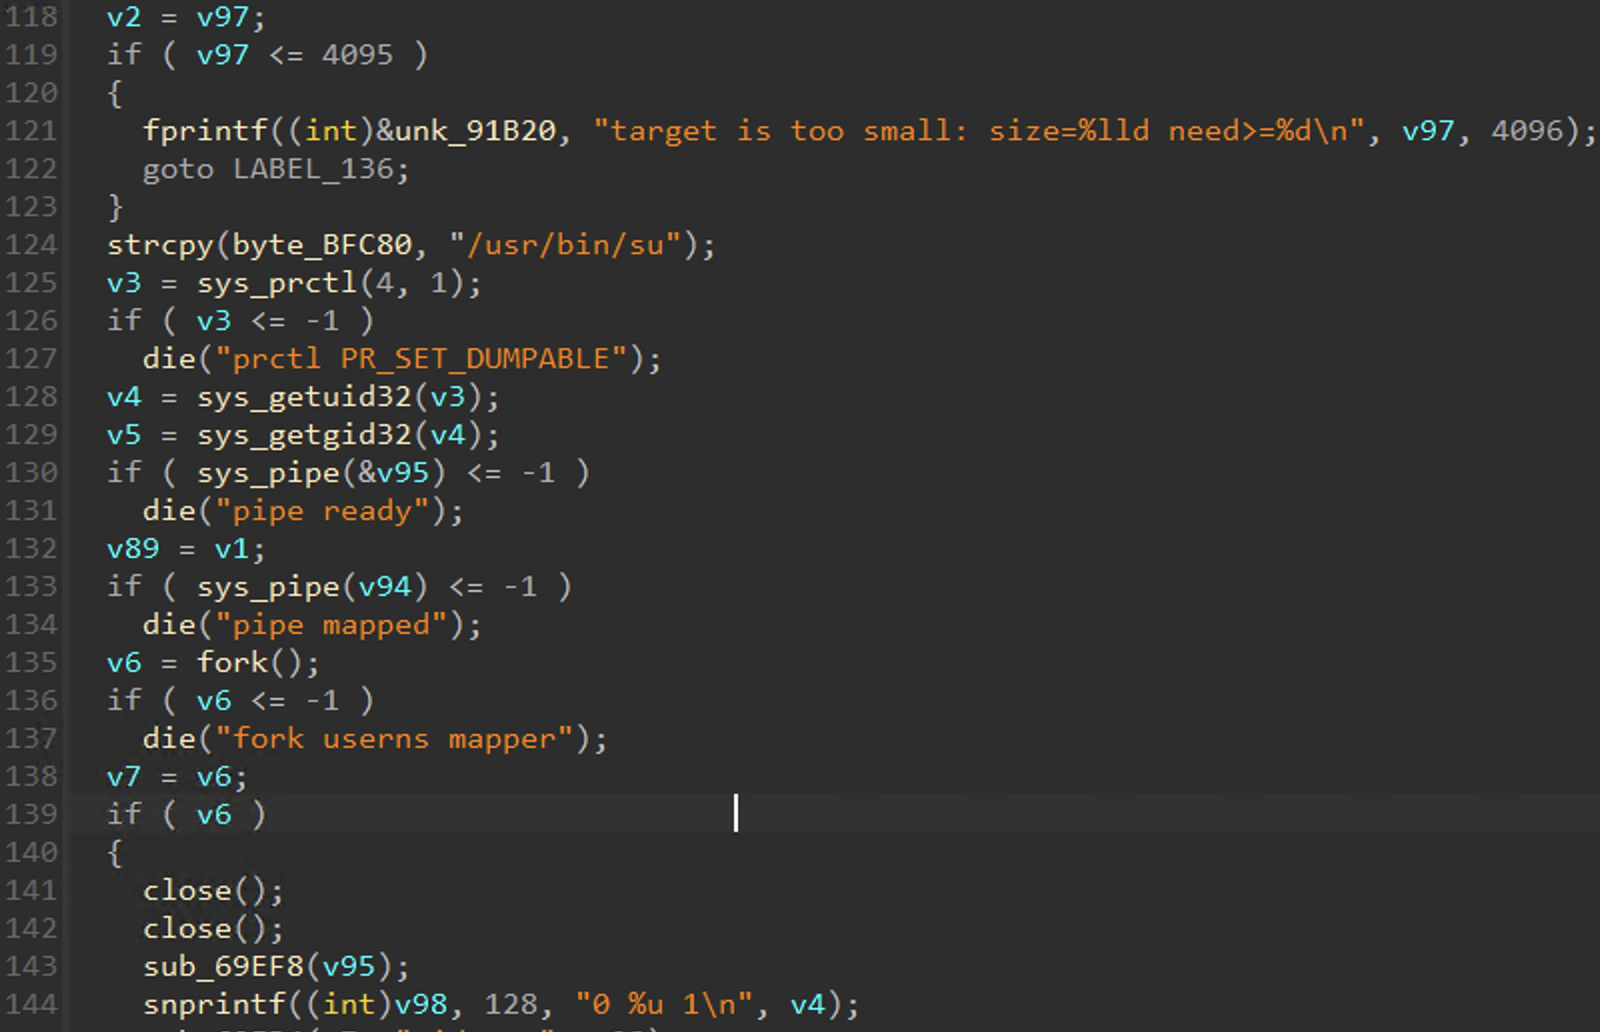
The flaw does not make the malware harmless: attackers can still succeed against misconfigured systems or selectively deploy working variants for target hardware.
After execution, KATARU discovers its running path through /proc/self/exe and copies itself into candidate filesystem locations.
Where privileges permit, it can alter file attributes, overwrite targets and apply immutable or append-only flags to impede removal.
Its persistence coverage is unusually expansive. The malware attempts to abuse systemd services, timers, generators and path units; cron jobs and @reboot; rc.local; SysV init files; shell profiles.
Nozomi said in a report shared with GBhackers, the malware was identified after a honeypot received brute-force Telnet activity from an IP address in Vietnam.
IoT Malware Attack
OpenWrt hotplug and procd mechanisms; U-Boot and NVRAM hooks; DHCP, udev and package-manager scripts; alternative init frameworks including OpenRC, runit, s6 and dinit; and XDG desktop autostart locations.
It also contains Android-oriented logic, checking boot-script locations associated with rooted Android systems and attempting to create an init service launched after boot completion.
This “try everything” persistence model gives the botnet opportunities to survive reboot on routers, embedded Linux devices, industrial appliances, Linux hosts and potentially modified Android endpoints.
KATARU departs from the plain-text communications common in older Mirai derivatives.
It uses an X25519 key exchange and ChaCha20-Poly1305 encrypted, authenticated message frames to communicate with its command-and-control infrastructure.
The design can make passive traffic inspection and C2 impersonation more difficult.
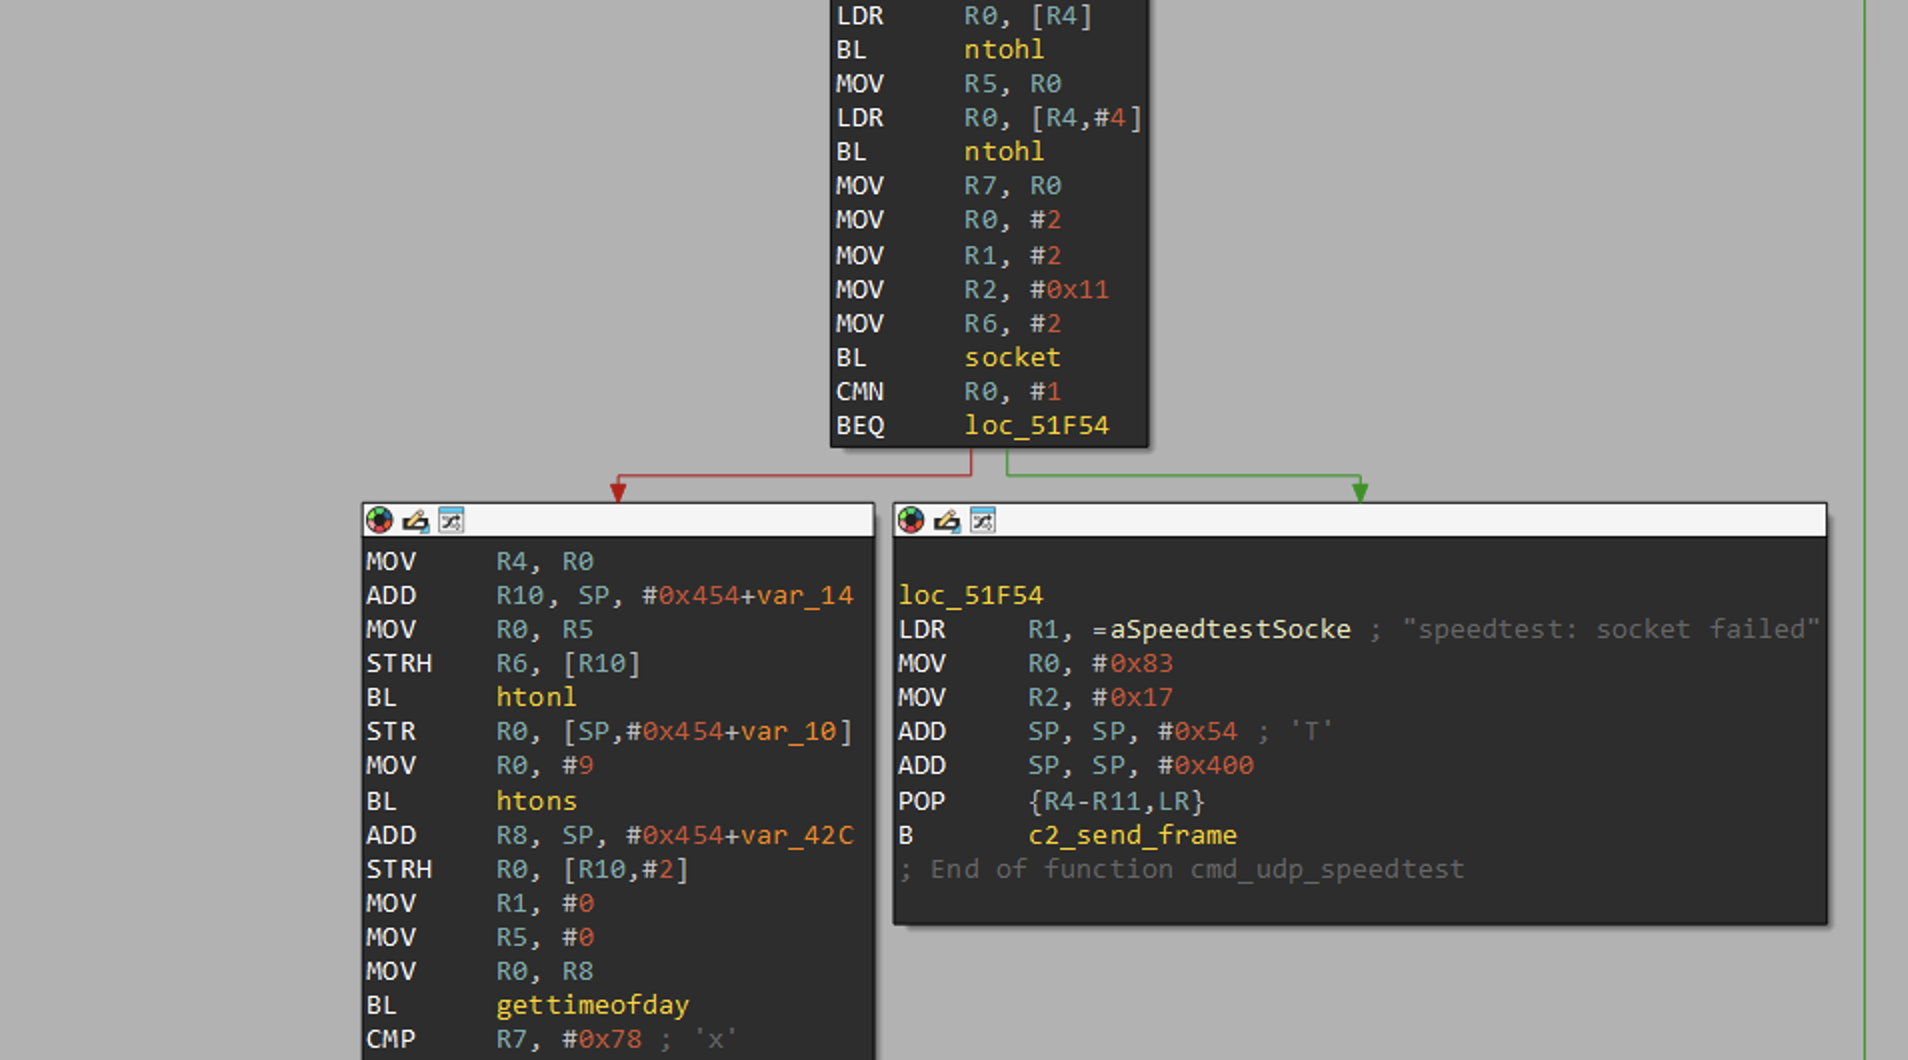
A notable implementation error is that its embedded pinned X25519 public key matches Alice’s public key from the RFC 7748 test vectors an artifact consistent with copied reference code rather than production-grade cryptographic key management.
Once controlled, infected devices can launch TCP, UDP, ICMP, HTTP, QUIC and DNS floods.
KATARU also includes attacks aimed at Minecraft, FiveM, OpenVPN and WireGuard services, along with an SSH brute-force function using embedded credentials.
C2 operators can additionally order bots to download and run second-stage payloads, execute shell commands, conduct UDP throughput tests, stop active attacks or remove the malware and its persistence artifacts.
The malware includes anti-debugging checks for ptrace, TracerPid, LD_PRELOAD, Valgrind, radare2-related environment variables and analyst tool process names.
It also uses a timing check intended to detect debugging or instrumented execution.
KATARU further emits fake beacon traffic, synthetic HTTP requests, misleading JWT data, decoy hostnames, IRC-style chatter and junk UDP packets.
Some decoy destinations use RFC documentation address ranges, while others point to legitimate third-party infrastructure.
Analysts should therefore avoid treating every hostname, IP address or string embedded in the binary as a confirmed indicator of compromise.
Organizations should disable Telnet wherever possible, eliminate default credentials, restrict device administration to segmented management networks or VPNs, and patch supported device firmware and Linux kernels.
The Fragnesia, Dirty Frag and Copy Fail issues demonstrate why low-privilege footholds can become root-level compromise on vulnerable systems.access.
Defenders should also monitor for unauthorized systemd units, cron jobs, altered boot scripts, OpenWrt hooks, unexpected immutable files, unusual outbound encrypted connections and sudden high-volume traffic from IoT assets.
KATARU shows how rapidly commodity botnets can combine public exploits, copied code and AI-assisted development into a disruptive threat even when their implementation remains noisy and imperfect.
IOCs
| Indicator Type | Value |
|---|---|
| SHA-256 Hash (Loader) | cc76bc218627279ecb4d0ce74ad2651e9db9e3e843e35d6569576e056e3a9218 |
| SHA-256 Hash (ARM32) | 13382c16e2401b07451577b46e634b8031ec254d98b876e59692b5fa22abc1d4 |
| SHA-256 Hash (ARM32) | 6fbae3505ae0d638b820165c572d548ce92dda71e82dc47e8efe13f30617f35f |
| SHA-256 Hash (ARM32) | 9d87e6615c810907443ebd5e915f3b35099c3b5c6b6c684637138a7f8ec9cebc |
| SHA-256 Hash (AMD64) | 9d7cd4948a1fcbaeadc425752fce9a933bd6fc41eeede030dffd7b99b3bc51d5 |
| IPv4 Address | 160[.]191.242.92 Telnet credential brute-force activity and command-and-control (C2) |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
★ Learn 7 Metric-Gated AI SOC Deployment Phases – Download Free AI SOC Deployment Playbook 2026.
Mayura Kathirhttps://gbhackers.com/
Mayura Kathir is a cybersecurity reporter at GBHackers News, covering daily incidents including data breaches, malware attacks, cybercrime, vulnerabilities, zero-day exploits, and more.
Text extracted automatically; images, tables and formatting may be missing. Original: https://gbhackers.com/iot-malware-attacks/