MongoBleed (CVE-2025-14847): the US, China, and the EU are among the top exploited GEOs
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2025-14847 | Unauthenticated Heap Memory Disclosure in MongoDB Server (MongoBleed) CVE-2025-14847 ('MongoBleed') is an improper handling of length parameter inconsistency (CWE-130) in MongoDB Server's processing of Zlib-compressed protocol headers, where mismatched length fields cause the server to return uninitialized heap memory. An unauthenticated remote client can trigger the leak by sending specially crafted compressed protocol messages to a vulnerable server, with no credentials, user interaction, or complex conditions required. The impact is confidentiality-only: an attacker can harvest fragments of the server's heap memory, which may contain sensitive in-memory data such as documents, credentials, or keys, reflected in the High confidentiality rating in the 8.7 CVSS 4.0 score. Virtually every MongoDB Server release from 3.6 through 8.2 is affected unless updated to the fixed patch levels (e.g., 8.2.3, 8.0.17, 7.0.28, 6.0.27, 5.0.32, 4.4.30), so the potentially exposed population is extremely large. The flaw was added to CISA's Known Exploited Vulnerabilities catalog on 2025-12-29, is reported as actively exploited in the wild worldwide (including a joint US-Australia advisory), and carries a very high EPSS of 83.2%, making patching urgent. Do: Upgrade MongoDB Server immediately to the fixed release for your branch: 8.2.3+, 8.0.17+, 7.0.28+, 6.0.27+, 5.0.32+, or 4.4.30+; 3.6, 4.0, and 4.2 deployments are affected in all versions and should be moved to a patched release or retired per MongoDB guidance. Until patched, restrict network access to MongoDB to trusted clients and consider disabling Zlib network compression as an interim mitigation, and review logs for unauthenticated client connections. Because the flaw is on CISA's KEV catalog with active exploitation observed (including ransomware-adjacent tracking), apply mitigations per BOD 22-01 timelines or discontinue use of affected unpatched instances. | 8.7 | 83% | KEV PoC ×3 |
| masstens of thousands of MongoDB instances directly exposed to the internet, within millions of total deployments worldwide (estimate) |
Full article397 words · extracted from securityaffairs.com · click to collapse
 Pierluigi Paganini
 December 31, 2025

MongoBleed (CVE-2025-14847) lets attackers remotely leak memory from unpatched MongoDB servers using zlib compression, without authentication.
A critical vulnerability, CVE-2025-14847 (MongoBleed), was disclosed right after Christmas, an unwelcome “gift” for the cybersecurity community, impacting MongoDB Server deployments that use zlib network compression.
MongoDB is a popular open-source NoSQL database used to store and manage data in a flexible, document-based format.
Instead of tables and rows like traditional SQL databases, MongoDB stores data as JSON-like documents (called BSON). This makes it well-suited for modern applications that need scalability, high performance, and flexible data models.
Any internet-facing MongoDB instance, whether cloud-hosted or on-premises, including production, staging, or test environments, with zlib compression enabled is potentially vulnerable.
In practice, this impacts all MongoDB versions from 3.6 onward if they have not been patched. The vulnerability can be exploited remotely and without authentication, meaning an attacker only needs network access to the MongoDB service port. As a result, both internet-exposed databases and internally accessible instances reachable through lateral movement are at risk of leaking sensitive process memory.
Based on the available telemetry, the highest number of exposed vulnerable MongoDB instances were observed in the following countries:
- China: 16,576 exposed instances
- United States: 14,486 exposed instances
- Germany: 11,547 exposed instances
- Hong Kong: 5,521 exposed instances
- Singapore: 4,130 exposed instances
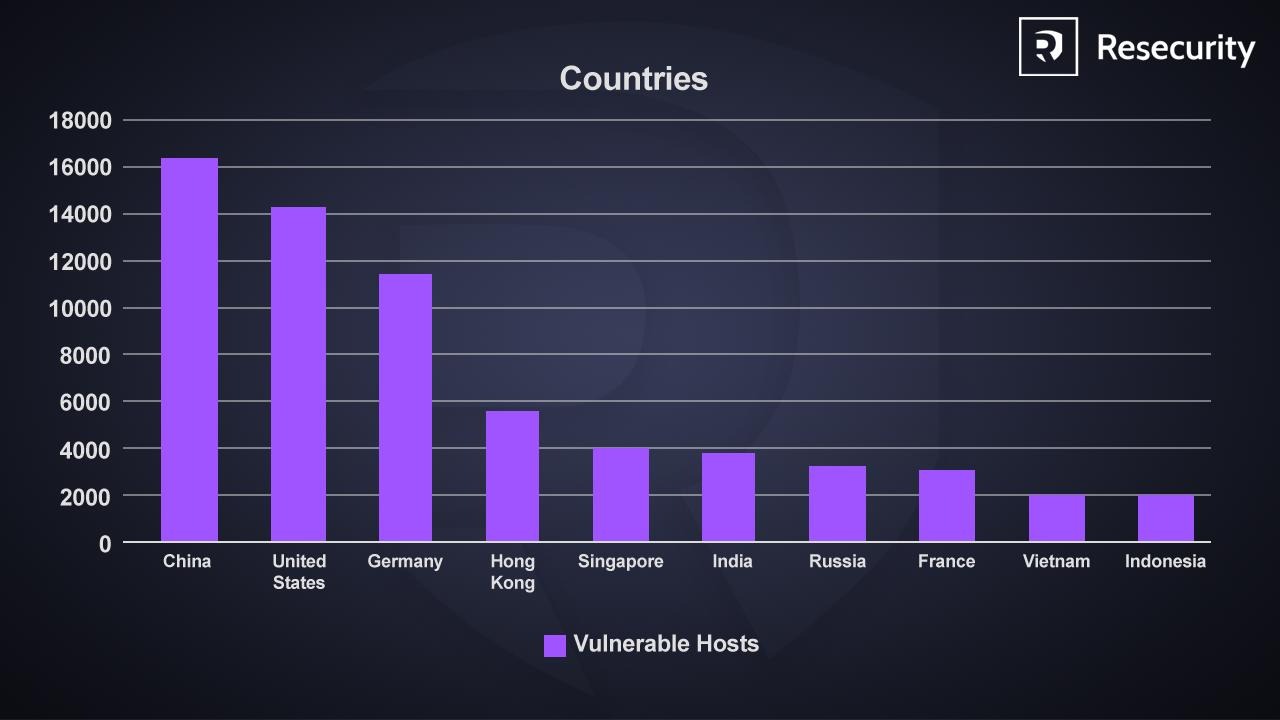
According to Resecurity, additional exposures were observed in India, Russia, France, Vietnam, and Indonesia, suggesting the issue is globally distributed rather than regionally isolated.
“The concentration of vulnerable MongoDB instances on large cloud and hosting providers highlights the risk of misconfiguration at scale. Attackers can rapidly enumerate and target these environments using internet-wide scanning platforms, enabling automated exploitation, data exposure, and service compromise across multiple tenants.” reads the report published by Resecurity. “The infrastructure and cloud providers hosting the highest number of affected systems.”

Resecurity researchers published a detailed analysis of the PoC methodology and the leaked output, along with recommendations to prevent it.
U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added CVE-2025-14847 to its Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. The Australian Signals Directorate similarly warned that it is aware of active global exploitation of this vulnerability. All federal civilian executive branch agencies should remediate CVE-2025-14847 by Jan. 19, according to CISA.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, newsletter)
Text extracted automatically; images, tables and formatting may be missing. Original: https://securityaffairs.com/186338/hacking/mongobleed-cve-2025-14847-the-us-china-and-the-eu-are-among-the-top-exploited-geos.html