SonicWall warns of max severity SSRF flaw in SMA1000 gateways
SonicWall patches maximum-severity unauthenticated SSRF CVE-2026-102255 in SMA1000 gateways; no exploitation reported.
SonicWall released hotfixes for CVE-2026-102255, a maximum-severity server-side request forgery flaw in the WorkPlace interface of SMA1000 models 6210, 7210, and 8200v. A remote unauthenticated attacker could make the appliance issue requests and reach internal functionality; the SMA 100 Series and firewall SSL-VPN are unaffected. SonicWall said there is no evidence this flaw is being exploited in the wild. Shadowserver tracks more than 400 internet-exposed SMA1000 appliances, and prior SMA1000 zero-days, including CVE-2026-15409 and CVE-2026-15410, were previously used in ransomware-linked attacks.
- CVE-2026-102255 is an unauthenticated low-complexity SSRF on SMA1000.
- Hotfixes cover 6210, 7210, and 8200v WorkPlace interfaces.
- SonicWall reports no evidence of in-the-wild exploitation.
- Shadowserver sees over 400 internet-exposed SMA1000 appliances.
- SMA 100 Series and firewall SSL-VPN are not affected.
Vulnerabilities mentionedAll →
- CVE-2026-10225510.0—Pre-auth SSRF in SonicWall SMA1000 Work Place interfacepublished · SonicWall SMA1000 Appliance (Work Place interface)
- CVE-2026-1540910.07%Unauthenticated SSRF in SonicWall SMA1000 Appliancespublished · SonicWall SMA1000 Appliances (SMA 6210 firmware)
Full article406 words · extracted from bleepingcomputer.com · click to collapse
SonicWall has released hotfixes to address a maximum-severity server-side request forgery (SSRF) flaw in SMA1000 series appliances.
Tracked as CVE-2026-102255, the vulnerability was found in the Appliance WorkPlace interface of SMA1000 6210, 7210, and 8200v models, but it does not affect the SMA 100 Series product line or SSL-VPN running on SonicWall firewalls.
The flaw stems from an unintended alternate access-path weakness that remote attackers without privileges can exploit in low-complexity attacks.
"By abusing this path, a remote unauthenticated attacker could potentially exploit this vulnerability to direct the appliance to issue requests on their behalf and reach internal functionality and perform unauthorized operations," SonicWall explained.
While it has not yet flagged these flaws as actively exploited, the company urged customers to deploy hotfixes released on Tuesday to block potential attacks targeting their virtual or physical appliances.
"SonicWall strongly advises users of the SMA1000 series appliances to upgrade to the mentioned fixed release version to address these vulnerabilities," the company added. "There is currently no evidence any of the vulnerabilities addressed in this release are being exploited in the wild."
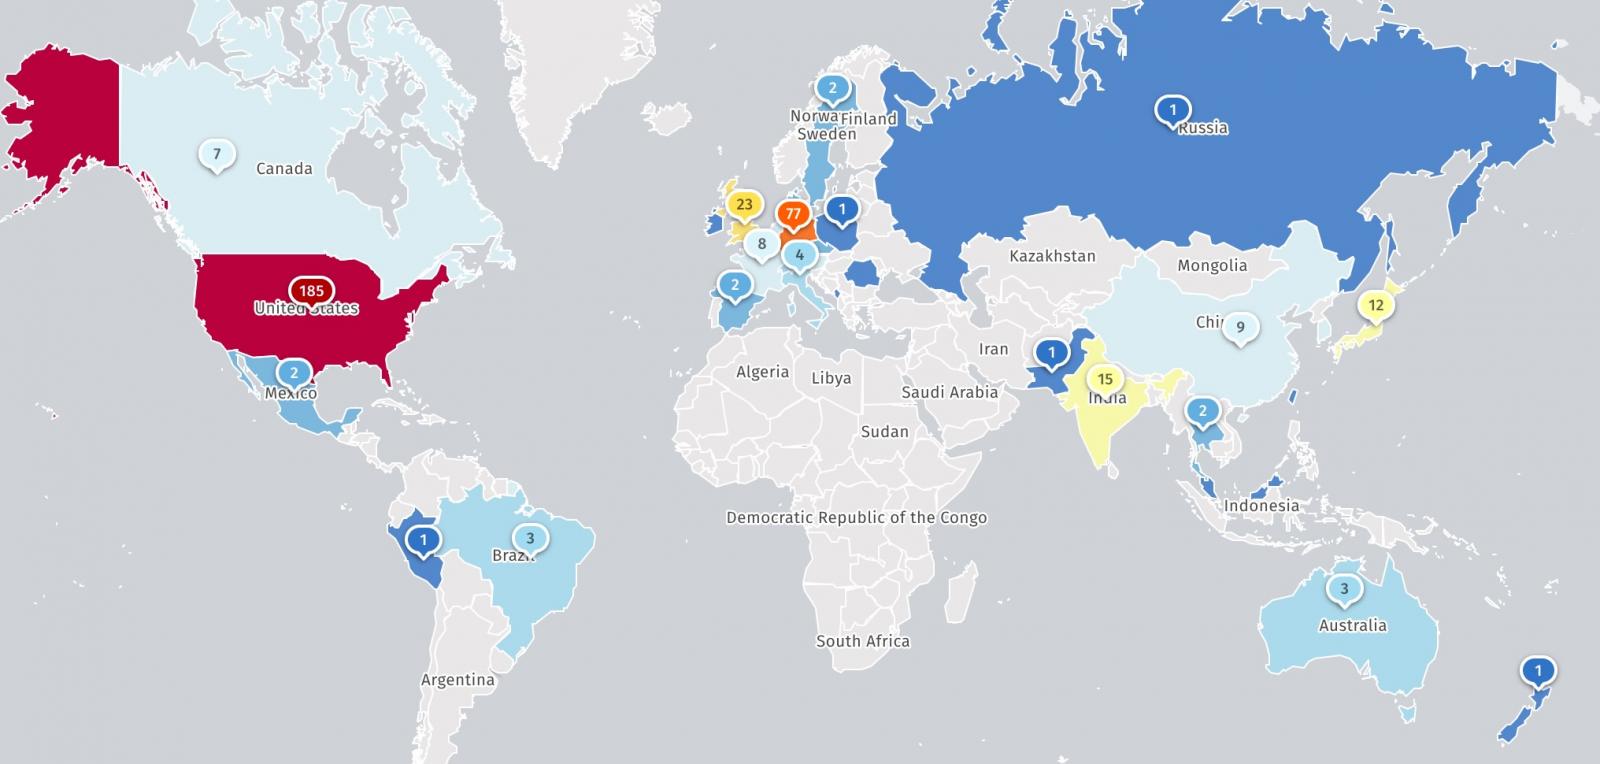
Internet security threat watchdog Shadowserver currently tracks over 400 Internet-exposed SMA1000 appliances, although some may have already been patched.
Although CVE-2026-102255 is not exploited in the wild, attackers often target SMA1000 flaws because they affect enterprise-grade secure remote access gateways used by government agencies, Managed Service Providers (MSSPs), and many large corporations to provide VPN access to internal apps and corporate networks.
Since the start of the year, threat actors have exploited several SMA1000 security vulnerabilities in zero-day attacks.
In July, two SMA1000 zero-days (CVE-2026-15409 and CVE-2026-15410) were exploited for weeks to install custom Sou5, OrangeTail, and RootRun malware on vulnerable VPN appliances in attacks that the U.S. Cybersecurity and Infrastructure Security Agency (CISA) linked to ransomware gangs.
Last month, SonicWall also warned customers that attackers were chaining two new zero-days (CVE-2026-83548 and CVE-2026-83549) to execute remote code on vulnerable SMA1000 gateways.
CISA has added 19 SonicWall vulnerabilities to its list of actively exploited flaws over the last four years, 13 of which have also been abused in ransomware attacks.
Build your security blueprint for AI-powered attacks
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.