Cloud Atlas group acquires PowerCloud, ReverseSocks, SSH
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2018-0802 | Memory Corruption RCE in Microsoft Office Equation Editor A memory-corruption flaw (out-of-bounds write, CWE-787) in the legacy Equation Editor component (EQNEDT32.EXE) shipped with Microsoft Office 2007, 2010, 2013, and 2016 allows remote code execution due to improper handling of objects in memory. An attacker triggers it by persuading a user to open a specially crafted document (for example an RTF or DOCX containing a malformed embedded equation object), causing the Equation Editor process to corrupt memory when the file is opened in Word; the user-interaction requirement is reflected in the CVSS 3.1 vector (AV:L/UI:R). Successful exploitation gives the attacker code execution in the context of the current user, with high impact on confidentiality, integrity, and availability (CVSS 3.1 score 7.8, High). Any user of the affected Office versions, the Office Compatibility Pack, or Word on an unpatched system is affected. Exploitation is confirmed in the wild: the flaw is in CISA's Known Exploited Vulnerabilities catalog (added 2021-11-03) with known ransomware use, carries a 93.3% EPSS probability of exploitation within 30 days, and multiple public analyses and proof-of-concepts exist. Do: Apply Microsoft's January 2018 security updates for Office 2007, 2010, 2013, and 2016 and the Office Compatibility Pack, and verify the legacy Equation Editor executable (EQNEDT32.EXE) on endpoints has been patched or removed (Microsoft later retired the component). Because the flaw is exploited in the wild and used in ransomware campaigns, prioritize remediation per CISA KEV required action and hunt for Word spawning EQNEDT32.EXE or unexpected child processes when documents are opened. Until patched, open untrusted documents in Protected View and treat email-delivered RTF/DOCX attachments as untrusted. | 7.8 | 93% | KEV ransomware PoC ×3 |
| masshundreds of millions of Office users at time of disclosure (vulnerable Equation Editor shipped by default with Office 2007-2016); largely patched today, with… |
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | amerikastaj.com | licious and compromised domains used in MS Office documents amerikastaj[.]com bigbang[.]me paleturquoise-dragonfly-364512.hostingersite |
| domain | bigbang.me | mised domains used in MS Office documents amerikastaj[.]com bigbang[.]me paleturquoise-dragonfly-364512.hostingersite[.]com wizzif |
| domain | cloudguide.in | C05 Domains and IPs Reverse SSH/Socks domains tenkoff[.]org cloudguide[.]in goverru[.]com kufar[.]org ultimatecore[.]net spbnews[.]ne |
| domain | com.au | ]com firsai.tipshub[.]net alnakhlah.com[.]sa allgoodsdirect.com[.]au agenciakharis.com[.]br Powershell payload staging istochn |
| domain | com.br | et alnakhlah.com[.]sa allgoodsdirect.com[.]au agenciakharis.com[.]br Powershell payload staging istochnik[.]org znews[.]net i |
| domain | com.sa | [.]si fishingflytackle[.]com firsai.tipshub[.]net alnakhlah.com[.]sa allgoodsdirect.com[.]au agenciakharis.com[.]br Powershell |
| domain | co.uk | .]org mamurjor[.]com landscapeuganda[.]com lafortunaitalian.co[.]uk kommando[.]live internationalcommoditiesllc[.]com humanit |
| domain | fishingflytackle.com | ndo[.]live internationalcommoditiesllc[.]com humanitas[.]si fishingflytackle[.]com firsai.tipshub[.]net alnakhlah.com[.]sa allgoodsdirect.co |
| domain | goverru.com | IPs Reverse SSH/Socks domains tenkoff[.]org cloudguide[.]in goverru[.]com kufar[.]org ultimatecore[.]net spbnews[.]net onedrivesupp |
| domain | hostingersite.com | erikastaj[.]com bigbang[.]me paleturquoise-dragonfly-364512.hostingersite[.]com wizzifi[.]com totallegacy[.]org mamurjor[.]com landscapeu |
| domain | humanitas.si | n.co[.]uk kommando[.]live internationalcommoditiesllc[.]com humanitas[.]si fishingflytackle[.]com firsai.tipshub[.]net alnakhlah.com |
| domain | internationalcommoditiesllc.com | dscapeuganda[.]com lafortunaitalian.co[.]uk kommando[.]live internationalcommoditiesllc[.]com humanitas[.]si fishingflytackle[.]com firsai.tipshub[.]ne |
| domain | investika-club.com | br Powershell payload staging istochnik[.]org znews[.]net i investika-club[.]com 194.102.104[.]207 46.17.45[.]56 46.17.45[.]49 46.17.44[.] |
| domain | istochnik.org | .com[.]au agenciakharis.com[.]br Powershell payload staging istochnik[.]org znews[.]net i investika-club[.]com 194.102.104[.]207 46.1 |
| domain | kommando.live | murjor[.]com landscapeuganda[.]com lafortunaitalian.co[.]uk kommando[.]live internationalcommoditiesllc[.]com humanitas[.]si fishingf |
| domain | kufar.org | H/Socks domains tenkoff[.]org cloudguide[.]in goverru[.]com kufar[.]org ultimatecore[.]net spbnews[.]net onedrivesupport[.]net Ma |
| domain | landscapeuganda.com | ersite[.]com wizzifi[.]com totallegacy[.]org mamurjor[.]com landscapeuganda[.]com lafortunaitalian.co[.]uk kommando[.]live internationalcom |
| domain | mamurjor.com | -364512.hostingersite[.]com wizzifi[.]com totallegacy[.]org mamurjor[.]com landscapeuganda[.]com lafortunaitalian.co[.]uk kommando[. |
| domain | onedrivesupport.net | goverru[.]com kufar[.]org ultimatecore[.]net spbnews[.]net onedrivesupport[.]net Malicious and compromised domains used in MS Office docum |
| domain | spbnews.net | loudguide[.]in goverru[.]com kufar[.]org ultimatecore[.]net spbnews[.]net onedrivesupport[.]net Malicious and compromised domains u |
| domain | tenkoff.org | 90EF27F8890D4EC05 Domains and IPs Reverse SSH/Socks domains tenkoff[.]org cloudguide[.]in goverru[.]com kufar[.]org ultimatecore[.] |
| domain | tipshub.net | itiesllc[.]com humanitas[.]si fishingflytackle[.]com firsai.tipshub[.]net alnakhlah.com[.]sa allgoodsdirect.com[.]au agenciakharis. |
| domain | totallegacy.org | urquoise-dragonfly-364512.hostingersite[.]com wizzifi[.]com totallegacy[.]org mamurjor[.]com landscapeuganda[.]com lafortunaitalian.co[ |
| domain | ultimatecore.net | ins tenkoff[.]org cloudguide[.]in goverru[.]com kufar[.]org ultimatecore[.]net spbnews[.]net onedrivesupport[.]net Malicious and comprom |
| domain | wizzifi.com | ang[.]me paleturquoise-dragonfly-364512.hostingersite[.]com wizzifi[.]com totallegacy[.]org mamurjor[.]com landscapeuganda[.]com la |
| domain | znews.net | akharis.com[.]br Powershell payload staging istochnik[.]org znews[.]net i investika-club[.]com 194.102.104[.]207 46.17.45[.]56 46 |
| md5 | 0320dd389fdbab25d46792bd2817675e | 2950D2E13B075001CE0C52AA97 A75DBED984963B9AB21309C5B2F8FD9B 0320DD389FDBAB25D46792BD2817675E 5339D1A666F3E40FE756505CF1D87D4B 67D7E3AEEB673BF60C59361C12 |
| md5 | 0577db70844e88b32b954906e2f20798 | B250F855C8C872FFFB9BB656ED ED34F5A136FBA4FDEA976570FAA33ED7 0577DB70844E88B32B954906E2F20798 28ECF8FB6719E14231B94B4D37629B0E 0857C84B62289A1A9F29E19244 |
| md5 | 0857c84b62289a1a9f29e19244e9a499 | 70844E88B32B954906E2F20798 28ECF8FB6719E14231B94B4D37629B0E 0857C84B62289A1A9F29E19244E9A499 0C514E137860F489E3801213460EF938 50568B1F9335A7E3BA4E5DF035 |
| md5 | 097ca205ad9e3b72018750280904718c | 19BFEC0DC4607C17112B9E3B2C A632858F14B36F03D0F213F5F5D6BFF2 097CA205AD9E3B72018750280904718C 69121C36EB8BF77962DCA825FCFFD873 C5702EB250F855C8C872FFFB9B |
| md5 | 0c514e137860f489e3801213460ef938 | FB6719E14231B94B4D37629B0E 0857C84B62289A1A9F29E19244E9A499 0C514E137860F489E3801213460EF938 50568B1F9335A7E3BA4E5DF035A8FB86 7F776AD200287D6DE14A29158C |
| md5 | 116f59e70a9df97f4adaea71eecb1e9a | D21C483A40156F4E40D08DADED 216CB7F31D383C0DD892B284DF05A495 116F59E70A9DF97F4ADAEA71EECB1E9A 7242AC065B50BCDE9308756B49DBADCB 8158552950D2E13B075001CE0C |
| md5 | 1a11b26dd0261ef27a112ce8b361c247 | cuted a suspicious PowerShell script named rdp_new.ps1 (MD5 1A11B26DD0261EF27A112CE8B361C247): The script is designed to allow multiple RDP sessions in |
| md5 | 1b39e86eb772a0e40060b672b7f574f1 | 1681455DAE1B6A26709DEF453 C:\Windows\pla\reports\winlog.exe 1B39E86EB772A0E40060B672B7F574F1 C:\Windows\System32\timecontrolsvc\vmnetdrv64.exe 1D401D6E6 |
| md5 | 1d401d6e6fc0b00aaa2c65a0ac0cfd6b | 2B7F574F1 C:\Windows\System32\timecontrolsvc\vmnetdrv64.exe 1D401D6E6FC0B00AAA2C65A0AC0CFD6B C:\Windows\setup\scripts\install\software\activation\aact\d |
| md5 | 2042eb5d52f0b535a1ce6b6f954c8c2b | F285E32A05E6591D1EB36EBFFC F42085522EC2EBB16EDCF814E7C330AD 2042EB5D52F0B535A1CE6B6F954C8C2B 2AA1E9765EF6B00B94A9B6BE0041436A 36120F5E9411BCBAC7104EF3FA |
| md5 | 216cb7f31d383c0dd892b284df05a495 | DEC8CD8F54F3F60A85F3ED600E EC076CD21C483A40156F4E40D08DADED 216CB7F31D383C0DD892B284DF05A495 116F59E70A9DF97F4ADAEA71EECB1E9A 7242AC065B50BCDE9308756B49 |
| md5 | 25c8ed0511375dca57ef136ac3fa0cca | 18A7E922FBA1A8 dfsvc.exe F6F62456FB0FCC396FB654CBED339BC3 – 25C8ED0511375DCA57EF136AC3FA0CCA C:\branding\dwmw.exe Browser checker 5329F7BFF9D0D5DB28821B |
| md5 | 28ecf8fb6719e14231b94b4d37629b0e | A136FBA4FDEA976570FAA33ED7 0577DB70844E88B32B954906E2F20798 28ECF8FB6719E14231B94B4D37629B0E 0857C84B62289A1A9F29E19244E9A499 0C514E137860F489E380121346 |
| md5 | 2aa1e9765ef6b00b94a9b6be0041436a | 522EC2EBB16EDCF814E7C330AD 2042EB5D52F0B535A1CE6B6F954C8C2B 2AA1E9765EF6B00B94A9B6BE0041436A 36120F5E9411BCBAC7104EF3FA964ED2 5000A353399500BC78381DC95B |
| md5 | 2b4ba4facf8c299749771a3a4369782e | C26D628F C:\ProgramData\checker_[redacted].exe ReverseSocks 2B4BA4FACF8C299749771A3A4369782E C:\Windows\PLA\System\bounce.exe C:\Windows\pla\print_statu |
| md5 | 2cabb721681455dae1b6a26709def453 | 64AADD948F9CE C:\Windows\migration\wtr\MicrosoftBrowser.exe 2CABB721681455DAE1B6A26709DEF453 C:\Windows\pla\reports\winlog.exe 1B39E86EB772A0E40060B672B |
| md5 | 344ca9ea07cd4ac90ef27f8890d4ec05 | 0ED20791A5AC9FC4267D67CCB0 B6AAE073E7BFEBF4D643C2BBEB5C02E1 344CA9EA07CD4AC90EF27F8890D4EC05 Domains and IPs Reverse SSH/Socks domains tenkoff[.]org clo |
| md5 | 36120f5e9411bcbac7104ef3fa964ed2 | 5D52F0B535A1CE6B6F954C8C2B 2AA1E9765EF6B00B94A9B6BE0041436A 36120F5E9411BCBAC7104EF3FA964ED2 5000A353399500BC78381DC95B6ED2DC 579A9952D31CAD801A3988DBE7 |
| md5 | 369b75bdcded16469ede7ab8bedcfae1 | s\ime\imetc\help\IMTCEN14.exe Malicious MS Office documents 369B75BDCDED16469EDE7AB8BEDCFAE1 9EAAE9491F6A50D6DF0BE393734A44CB 3E6E9DF00A764B348EC611EE85 |
| md5 | 38fa4306fa4406ba31cf171af4d36e34 | 52D31CAD801A3988DBE7914CE7 867B634588C0FD6B26684D502C15AB03 38FA4306FA4406BA31CF171AF4D36E34 83EDDE9F7EEEFAC0363413972F35572B CC751619BFEC0DC4607C17112B |
| md5 | 3c75cedb1196df5eab91f31411ed4b33 | 212A4A32763DE36732D40 C:\Windows\ime\imejp\dicts\i39884.exe 3C75CEDB1196DF5EAB91F31411ED4B33 C:\pla\reports.exe 42AC350BFBC5B4EB0FEDBA16C81919C7 C:\Prog |
| md5 | 3e6e9df00a764b348ec611ee8504aca0 | BDCDED16469EDE7AB8BEDCFAE1 9EAAE9491F6A50D6DF0BE393734A44CB 3E6E9DF00A764B348EC611EE8504ACA0 9BD788F285E32A05E6591D1EB36EBFFC F42085522EC2EBB16EDCF814E7 |
| md5 | 40a562b8600f843b717bc5951b2e3c29 | ws\setup\scripts\install\software\activation\aact\dfsvc.exe 40A562B8600F843B717BC5951B2E3C29 C:\Windows\branding\scat.exe F721A76DEB28FD0B80D27FCE6B8F50 |
| md5 | 42ac350bfbc5b4eb0fedba16c81919c7 | 884.exe 3C75CEDB1196DF5EAB91F31411ED4B33 C:\pla\reports.exe 42AC350BFBC5B4EB0FEDBA16C81919C7 C:\ProgramData\update_[redacted].exe 493B901D1B33EB577DB64A |
| md5 | 493b901d1b33eb577db64aadd948f9ce | C5B4EB0FEDBA16C81919C7 C:\ProgramData\update_[redacted].exe 493B901D1B33EB577DB64AADD948F9CE C:\Windows\migration\wtr\MicrosoftBrowser.exe 2CABB72168145 |
| md5 | 5000a353399500bc78381dc95b6ed2dc | 765EF6B00B94A9B6BE0041436A 36120F5E9411BCBAC7104EF3FA964ED2 5000A353399500BC78381DC95B6ED2DC 579A9952D31CAD801A3988DBE7914CE7 867B634588C0FD6B26684D502C |
| md5 | 50568b1f9335a7e3ba4e5df035a8fb86 | 4B62289A1A9F29E19244E9A499 0C514E137860F489E3801213460EF938 50568B1F9335A7E3BA4E5DF035A8FB86 7F776AD200287D6DE14A29158C457179 51F7F794ED43FB90D0F8EBBB5E |
| md5 | 51f7f794ed43fb90d0f8ebbb5effe628 | 1F9335A7E3BA4E5DF035A8FB86 7F776AD200287D6DE14A29158C457179 51F7F794ED43FB90D0F8EBBB5EFFE628 B8C753DD254509FBA5077FFD5067EAB0 BC3739DEC8CD8F54F3F60A85F3 |
| md5 | 5329f7bff9d0d5db28821b86c26d628f | tionally, the attackers used another PowerShell script (MD5 5329F7BFF9D0D5DB28821B86C26D628F), compiled into an executable file via PS2EXE, which checks |
| md5 | 5339d1a666f3e40fe756505cf1d87d4b | D984963B9AB21309C5B2F8FD9B 0320DD389FDBAB25D46792BD2817675E 5339D1A666F3E40FE756505CF1D87D4B 67D7E3AEEB673BF60C59361C12A4ED81 89572F0ED20791A5AC9FC4267D |
| md5 | 579a9952d31cad801a3988dbe7914ce7 | 5E9411BCBAC7104EF3FA964ED2 5000A353399500BC78381DC95B6ED2DC 579A9952D31CAD801A3988DBE7914CE7 867B634588C0FD6B26684D502C15AB03 38FA4306FA4406BA31CF171AF4 |
| md5 | 63b6be9ae8d8024a40b200cccb438f1d | A6D62E C:\Users\[redacted]\AppData\Local\1c\1cv8\1cv8ud.exe 63B6BE9AE8D8024A40B200CCCB438F1D C:\Windows\notepad.exe 6AA586BCC45CA2E92A4F0EF47E086FA1 C:\ |
| md5 | 67d7e3aeeb673bf60c59361c12a4ed81 | 389FDBAB25D46792BD2817675E 5339D1A666F3E40FE756505CF1D87D4B 67D7E3AEEB673BF60C59361C12A4ED81 89572F0ED20791A5AC9FC4267D67CCB0 B6AAE073E7BFEBF4D643C2BBEB |
| md5 | 69121c36eb8bf77962dca825fcffd873 | 8F14B36F03D0F213F5F5D6BFF2 097CA205AD9E3B72018750280904718C 69121C36EB8BF77962DCA825FCFFD873 C5702EB250F855C8C872FFFB9BB656ED ED34F5A136FBA4FDEA976570FA |
| md5 | 6aa586bcc45ca2e92a4f0ef47e086fa1 | exe 63B6BE9AE8D8024A40B200CCCB438F1D C:\Windows\notepad.exe 6AA586BCC45CA2E92A4F0EF47E086FA1 C:\Windows\splwow32.exe EBA3BCDB19A7E256BF8E2CC5B9C1CCA9 C: |
| md5 | 6d7b2d1172bbdb7340972d844f6f0717 | AA306FF659DB1FAC28574A C:\ProgramData\update_[redacted].exe 6D7B2D1172BBDB7340972D844F6F0717 C:\Users\[redacted]\AppData\Local\1c\1cv8\1cv8ud.exe C:\Use |
| md5 | 7242ac065b50bcde9308756b49dbadcb | F31D383C0DD892B284DF05A495 116F59E70A9DF97F4ADAEA71EECB1E9A 7242AC065B50BCDE9308756B49DBADCB 8158552950D2E13B075001CE0C52AA97 A75DBED984963B9AB21309C5B2 |
| md5 | 7a95360b7e0eb5b107a3d231abbc541a | ted, please contact [email protected] . PowerCloud 7A95360B7E0EB5B107A3D231ABBC541A C:\Windows\wininet.exe C0D1EAA15A2CEFBAB9735787575C8D8E C:\ |
| md5 | 7f776ad200287d6de14a29158c457179 | 137860F489E3801213460EF938 50568B1F9335A7E3BA4E5DF035A8FB86 7F776AD200287D6DE14A29158C457179 51F7F794ED43FB90D0F8EBBB5EFFE628 B8C753DD254509FBA5077FFD50 |
| md5 | 8158552950d2e13b075001ce0c52aa97 | E70A9DF97F4ADAEA71EECB1E9A 7242AC065B50BCDE9308756B49DBADCB 8158552950D2E13B075001CE0C52AA97 A75DBED984963B9AB21309C5B2F8FD9B 0320DD389FDBAB25D46792BD28 |
| md5 | 83edde9f7eeefac0363413972f35572b | 4588C0FD6B26684D502C15AB03 38FA4306FA4406BA31CF171AF4D36E34 83EDDE9F7EEEFAC0363413972F35572B CC751619BFEC0DC4607C17112B9E3B2C A632858F14B36F03D0F213F5F5 |
| md5 | 867b634588c0fd6b26684d502c15ab03 | 53399500BC78381DC95B6ED2DC 579A9952D31CAD801A3988DBE7914CE7 867B634588C0FD6B26684D502C15AB03 38FA4306FA4406BA31CF171AF4D36E34 83EDDE9F7EEEFAC0363413972F |
| md5 | 89572f0ed20791a5ac9fc4267d67ccb0 | A666F3E40FE756505CF1D87D4B 67D7E3AEEB673BF60C59361C12A4ED81 89572F0ED20791A5AC9FC4267D67CCB0 B6AAE073E7BFEBF4D643C2BBEB5C02E1 344CA9EA07CD4AC90EF27F8890 |
| md5 | 9769f43b9de8d19e803263267fa6d62e | cv8ud.exe C:\Users\[redacted]\AppData\Local\1c\1cv8\svc.exe 9769F43B9DE8D19E803263267FA6D62E C:\Users\[redacted]\AppData\Local\1c\1cv8\1cv8ud.exe 63B6BE |
| md5 | 9bd788f285e32a05e6591d1eb36ebffc | 491F6A50D6DF0BE393734A44CB 3E6E9DF00A764B348EC611EE8504ACA0 9BD788F285E32A05E6591D1EB36EBFFC F42085522EC2EBB16EDCF814E7C330AD 2042EB5D52F0B535A1CE6B6F95 |
| md5 | 9eaae9491f6a50d6df0be393734a44cb | icious MS Office documents 369B75BDCDED16469EDE7AB8BEDCFAE1 9EAAE9491F6A50D6DF0BE393734A44CB 3E6E9DF00A764B348EC611EE8504ACA0 9BD788F285E32A05E6591D1EB3 |
| md5 | a632858f14b36f03d0f213f5f5d6bff2 | 9F7EEEFAC0363413972F35572B CC751619BFEC0DC4607C17112B9E3B2C A632858F14B36F03D0F213F5F5D6BFF2 097CA205AD9E3B72018750280904718C 69121C36EB8BF77962DCA825FC |
| md5 | a75dbed984963b9ab21309c5b2f8fd9b | 065B50BCDE9308756B49DBADCB 8158552950D2E13B075001CE0C52AA97 A75DBED984963B9AB21309C5B2F8FD9B 0320DD389FDBAB25D46792BD2817675E 5339D1A666F3E40FE756505CF1 |
| md5 | b4e183627b7399006c1bc47b3711e419 | 6BF8E2CC5B9C1CCA9 C:\Users\[redacted]\Desktop\soc\stant.exe B4E183627B7399006C1BC47B3711E419 C:\WINDOWS\ime\service.exe F56B31A4B47AD3365B18A7E922FBA1A8 |
| md5 | b6aae073e7bfebf4d643c2bbeb5c02e1 | AEEB673BF60C59361C12A4ED81 89572F0ED20791A5AC9FC4267D67CCB0 B6AAE073E7BFEBF4D643C2BBEB5C02E1 344CA9EA07CD4AC90EF27F8890D4EC05 Domains and IPs Reverse SS |
| md5 | b8c753dd254509fba5077ffd5067eab0 | D200287D6DE14A29158C457179 51F7F794ED43FB90D0F8EBBB5EFFE628 B8C753DD254509FBA5077FFD5067EAB0 BC3739DEC8CD8F54F3F60A85F3ED600E EC076CD21C483A40156F4E40D0 |
| md5 | ba9ce06641067742f2afc9691faff1dc | ndows\PLA\System\bounce.exe C:\Windows\pla\print_status.exe BA9CE06641067742F2AFC9691FAFF1DC C:\ProgramData\hp\client.exe FB0F8027ACF1B1E47E07A63D8812ED |
| md5 | bbf1fa694122e07635deeac11ad712f8 | D8812ED50 C:\Windows\System32\timecontrolsvc\vmnetdrv64.exe BBF1FA694122E07635DEEAC11AD712F8 C:\Windows\System32\HostManagement.exe F301AA3D62B5095EEC4D |
| md5 | bc3739dec8cd8f54f3f60a85f3ed600e | 94ED43FB90D0F8EBBB5EFFE628 B8C753DD254509FBA5077FFD5067EAB0 BC3739DEC8CD8F54F3F60A85F3ED600E EC076CD21C483A40156F4E40D08DADED 216CB7F31D383C0DD892B284DF |
| md5 | c0d1eaa15a2cefbab9735787575c8d8e | oud 7A95360B7E0EB5B107A3D231ABBC541A C:\Windows\wininet.exe C0D1EAA15A2CEFBAB9735787575C8D8E C:\Windows\LiveKernelReports\update.exe D5B38B252CF212A4A32 |
| md5 | c5702eb250f855c8c872fffb9bb656ed | 05AD9E3B72018750280904718C 69121C36EB8BF77962DCA825FCFFD873 C5702EB250F855C8C872FFFB9BB656ED ED34F5A136FBA4FDEA976570FAA33ED7 0577DB70844E88B32B954906E2 |
| md5 | cc751619bfec0dc4607c17112b9e3b2c | 06FA4406BA31CF171AF4D36E34 83EDDE9F7EEEFAC0363413972F35572B CC751619BFEC0DC4607C17112B9E3B2C A632858F14B36F03D0F213F5F5D6BFF2 097CA205AD9E3B720187502809 |
| md5 | d3c8afd22baa306ff659db1fac28574a | 28FD0B80D27FCE6B8F5016 C:\Windows\ime\imekr\dicts\dfsvc.exe D3C8AFD22BAA306FF659DB1FAC28574A C:\ProgramData\update_[redacted].exe 6D7B2D1172BBDB7340972D |
| md5 | d5b38b252cf212a4a32763de36732d40 | FBAB9735787575C8D8E C:\Windows\LiveKernelReports\update.exe D5B38B252CF212A4A32763DE36732D40 C:\Windows\ime\imejp\dicts\i39884.exe 3C75CEDB1196DF5EAB91F |
| md5 | eba3bcdb19a7e256bf8e2cc5b9c1cca9 | xe 6AA586BCC45CA2E92A4F0EF47E086FA1 C:\Windows\splwow32.exe EBA3BCDB19A7E256BF8E2CC5B9C1CCA9 C:\Users\[redacted]\Desktop\soc\stant.exe B4E183627B7399006 |
| md5 | ec076cd21c483a40156f4e40d08daded | DD254509FBA5077FFD5067EAB0 BC3739DEC8CD8F54F3F60A85F3ED600E EC076CD21C483A40156F4E40D08DADED 216CB7F31D383C0DD892B284DF05A495 116F59E70A9DF97F4ADAEA71EE |
| md5 | ed34f5a136fba4fdea976570faa33ed7 | 36EB8BF77962DCA825FCFFD873 C5702EB250F855C8C872FFFB9BB656ED ED34F5A136FBA4FDEA976570FAA33ED7 0577DB70844E88B32B954906E2F20798 28ECF8FB6719E14231B94B4D37 |
| md5 | f301aa3d62b5095eec4d8e34201a4769 | E07635DEEAC11AD712F8 C:\Windows\System32\HostManagement.exe F301AA3D62B5095EEC4D8E34201A4769 C:\Windows\ime\imejp\msfu.exe F9C3BBE108566D1A6B070F9C5FB03 |
| md5 | f42085522ec2ebb16edcf814e7c330ad | F00A764B348EC611EE8504ACA0 9BD788F285E32A05E6591D1EB36EBFFC F42085522EC2EBB16EDCF814E7C330AD 2042EB5D52F0B535A1CE6B6F954C8C2B 2AA1E9765EF6B00B94A9B6BE00 |
| md5 | f56b31a4b47ad3365b18a7e922fba1a8 | B4E183627B7399006C1BC47B3711E419 C:\WINDOWS\ime\service.exe F56B31A4B47AD3365B18A7E922FBA1A8 dfsvc.exe F6F62456FB0FCC396FB654CBED339BC3 – 25C8ED0511375D |
| md5 | f6f62456fb0fcc396fb654cbed339bc3 | \ime\service.exe F56B31A4B47AD3365B18A7E922FBA1A8 dfsvc.exe F6F62456FB0FCC396FB654CBED339BC3 – 25C8ED0511375DCA57EF136AC3FA0CCA C:\branding\dwmw.exe Bro |
| md5 | f721a76deb28fd0b80d27fce6b8f5016 | A562B8600F843B717BC5951B2E3C29 C:\Windows\branding\scat.exe F721A76DEB28FD0B80D27FCE6B8F5016 C:\Windows\ime\imekr\dicts\dfsvc.exe D3C8AFD22BAA306FF659DB |
| md5 | f9c3bbe108566d1a6b070f9c5fb03160 | 1AA3D62B5095EEC4D8E34201A4769 C:\Windows\ime\imejp\msfu.exe F9C3BBE108566D1A6B070F9C5FB03160 C:\Windows\ime\imetc\help\IMTCEN14.exe Malicious MS Office |
| md5 | fb0f8027acf1b1e47e07a63d8812ed50 | 9CE06641067742F2AFC9691FAFF1DC C:\ProgramData\hp\client.exe FB0F8027ACF1B1E47E07A63D8812ED50 C:\Windows\System32\timecontrolsvc\vmnetdrv64.exe BBF1FA694 |
Full article2,069 words · extracted from securelist.com · click to collapse
In 2025, we observed pervasive SSH tunnel activity, which has remained active into 2026, affecting many government organizations and commercial companies in Russia and Belarus. Behind some of this activity is Cloud Atlas, a group we have known since 2014. During our investigation, we identified new tools used by this group, as well as indicators of compromise.
The group is back to sending out archives containing malicious shortcuts that launch PowerShell scripts. This technique is employed in addition to the previously described use of malicious documents, which exploit an old vulnerability in the Microsoft Office Equation Editor process (CVE-2018-0802) to download and execute malicious code. We have observed the use of third-party public utilities (Tor/SSH/RevSocks) to gain a foothold in infected systems and create additional backup control channels.
Technical details
Initial infection
As for the primary compromise, Cloud Atlas remains consistent in using phishing. In the observed campaigns, the attackers emailed a ZIP archive containing an LNK file as an attachment.
Malware execution flow
Attackers use LNK shortcuts to covertly execute PowerShell scripts hosted on external resources. The command line of the shortcut:
Example of the PowerShell script downloaded and executed by the shortcut:
Example of the PowerShell script downloaded by the shortcut
Actions performed by the downloaded PowerShell:
| Step | Action | Description |
| 1 | Drops “$temp\fixed.ps1” | Pre-staging: places the main payload locally in advance to ensure an execution capability independent of subsequent network connectivity or C2 availability. |
| 2 | Creates “Run” registry key “YandexBrowser_setup” for “$temp\fixed.ps1” startup | Early persistence: guarantees execution upon the next logon or reboot. If the script is interrupted during later stages, the payload will still activate automatically. |
| 3 | Downloads and drops “$temp\rar.zip” Extracts “*.pdf” from the downloaded “$temp\rar.zip” |
Payload delivery: retrieves the decoy archive from the remote server to prepare user-facing content for the distraction phase. |
| 4 | Extracts “*.pdf” from the downloaded “$temp\rar.zip” | Decoy preparation: unpacks the legitimate-looking document so it can be executed silently without requiring user interaction. |
| 6 | Opens extracted decoy document “*.pdf” with user’s default software | User distraction: opens a convincing document to maintain user engagement and creates a legitimate workflow appearance to buy additional 30–120 seconds for background operations. |
| 6 | Executes “taskkill.exe /F /Im winrar.exe” | Process concealment: terminates the archive extractor to prevent the user from seeing the archive contents or noticing unexpected file extraction activity. |
| 7 | Searches and deletes “rar.zip”, “*.pdf.zip” and “*.pdf.lnk” | Anti-forensic cleanup: removes the initial infection artifacts before activating the main payload, reducing the number of disk traces available for incident response or EDR correlation. |
| 8 | Executes “$temp\fixed.ps1” | Controlled execution: launches the main payload only after persistence is secured, the user is distracted, and access traces are cleaned up. |
Fixed.ps1 (loader)
The primary purpose of the Fixed.ps1 script is to deliver and install subsequent malware onto the compromised system, specifically VBCloud and PowerShower. Fixed.ps1 establishes persistence (by adding itself to registry Run keys), creates a decoy for the user (by opening a PDF document), and executes the next stages of the attack.
Fixed.ps1::Payload (VBCloud dropper)
Example of the fixed.ps1::Payload (VBCloud dropper)
This module functions as a dropper for the VBCloud backdoor. It drops two files onto the infected machine:
- video.vbs: the loader of the backdoor,VBCloud::Launcher. This is a VBScript that decrypts the contents of video.mds (typically using RC4 with a hardcoded key) and executes it in memory.
- video.mds: the encrypted body of the backdoor, VBCloud::Backdoor. This is the main module that connects to a C2 server to receive additional scripts or execute built-in commands. This backdoor is designed to function as a stealer, specifically targeting files with extensions of interest (such as DOC, PDF, XLS) and exfiltrating them.
Fixed.ps1::Payload (PowerShower)
This module installs a second backdoor called PowerShower on the system. We don’t have the specific script that performs this installation, but we assume it’s performed by a script similar to fixed.ps1::Payload (VBCloud dropper).
Unlike VBCloud, which focuses on file theft, PowerShower is primarily used for network reconnaissance and lateral movement within the victim’s infrastructure. PowerShower can perform the following tasks:
- Collect information about running processes, administrator groups, and domain controllers.
- Download and execute PowerShell scripts from the C2 server.
- Conduct “Kerberoasting” attacks (stealing password hashes of Active Directory accounts).
PowerShower is dropped onto the system via the path ‘C:\Users\[username]\Pictures\googleearth.ps1’.
Contents of the googleearth.ps1(PowerShower)
PowerShower::Payload (credential grabber)
PowerShower downloads an additional script for stealing credentials. It performs the following actions:
- Creates a Volume Shadow Copy of the C:\ drive.
- Copies the SAM (stores local user password hashes) and SECURITY system files from this shadow copy to C:\Users\Public\Documents\, disguising them as PDF files.
- The script is launched in several stages. To execute with high privileges, the script uses a UAC bypass technique via fodhelper.exe (a built-in Windows utility). This allows PowerShell to run as an administrator without directly prompting the user, which could otherwise raise suspicion.
The full launch chain looks like this:
The full Base64-decoded script is given below.
Multi-user RDP by patching termsrv.dll
Moving laterally across the victim’s network, the attackers executed a suspicious PowerShell script named rdp_new.ps1 (MD5 1A11B26DD0261EF27A112CE8B361C247):
The script is designed to allow multiple RDP sessions in Windows 10 by patching the termsrv.dll file. Termsrv.dll is the core Windows library that enforces Remote Desktop Services rules.
By default, Windows limits the number of simultaneous RDP sessions. Removing this restriction allows attackers to operate on the machine in the background without disconnecting the legitimate user, thereby reducing the likelihood of detection.
At first, the script enables RDP on the firewall and downgrades the RDP security settings:
Before modifying termsrv.dll, the script takes ownership and assigns itself full permissions. Then the script finds the sequence of bytes 39 81 3C 06 00 00 ?? ?? ?? ?? ?? ?? and replaces it with B8 00 01 00 00 89 81 38 06 00 00 90. After these manipulations, the script restarts the RDP service.
Example of script
The patched version allows multiple concurrent logins so attackers can stay connected without disrupting the legitimate user, thereby reducing suspicion.
Reverse SSH tunneling
As mentioned above, during this wave of attacks, the adversaries widely deployed reverse SSH tunnels to many hosts of interest. The compromised machine initiates an SSH connection to an attacker-controlled server, which allows attackers to bypass standard firewall rules via establishing outbound connections.
That way, even if the primary backdoor is discovered, the attackers can maintain control through the SSH tunnel.
To install a reverse SSH tunnel on a victim’s host, the attackers run VBS scripts via PAExec or PsExec.
We’ve seen three types of scripts:
- Gen.vbs (WriteToSchedulerGenerateKey.vbs) generates key for SSH tunnel.
- Run.vbs (WriteToSchedulerRunSSH.vbs) runs reverse SSH tunnel.
- Kill.vbs (WriteToSchedulerKillSSH.vbs) stops reverse SSH tunnel via taskkill.exe.
To achieve persistence, the attackers added a new scheduled task in Windows:
In some cases, before establishing a reverse SSH tunnel, attackers set new access permissions to the folder containing the private key to prevent the legitimate user or system administrators from easily accessing or modifying it:
Patched OpenSSH
Some OpenSSH binaries used by the attackers had their imports modified. Instead of libcrypto.dll, the SSH executable imports syruntime.dll, which was placed in the same folder as the binary. This was likely done to evade detection and ensure stealth.
In addition, we found a portable version of OpenSSH, presumably compiled by the adversaries:
RevSocks
In addition to Reverse SSH tunnels, the attackers installed RevSocks using the same infrastructure. RevSocks is an alternative tool to SSH for establishing tunnels and proxy connections, written in Golang. This tool allows direct connection to workstations on the local network. It also allows attackers to gain access to other segments of the victim’s network by using the machine as a gateway. In some cases, C2 addresses were hardcoded into the binary; in other cases, the C2 was passed in command line arguments.
There were also reverse SOCKS samples with hardcoded C2 addresses:
Tor tunneling
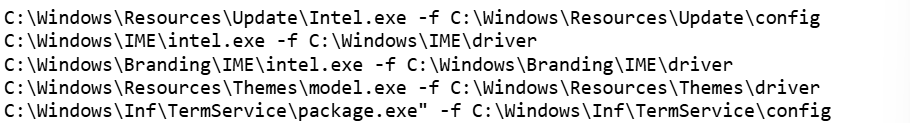
To maintain control over the compromised host, the Tor network was used in some cases. A minimal set of a Tor executable and configuration files, necessary for launching HiddenService, was copied to the system directories of infected devices. The name of the Tor Browser executable file was modified. As a result, the infected machine was accessible via RDP from the Tor network when accessing the generated .onion domain.
Below is an example of a configuration file for routing connections from Tor to RDP ports on the local network, as well as example command lines for logging into Tor.
Example of TOR configuration file
PowerCloud
We analyzed a new Cloud Atlas tool, PowerCloud. It collects user data with administrator privileges and writes this information to Google Sheets in Base64 format.
The tool represents an obfuscated PowerShell script. In most cases, it is packaged into an executable file using the PS2EXE utility, but we have also encountered variants in the form of a separate PowerShell script.
To find administrators on the victim host, the tool executes the following command:
This information is appended with the computer name and current date, the data is encoded in base64, and then the collected data is added to an existing Google Sheet.
PowerCloud script
Browser checker
Additionally, the attackers used another PowerShell script (MD5 5329F7BFF9D0D5DB28821B86C26D628F), compiled into an executable file via PS2EXE, which checks whether browser processes (Chrome, Edge, Firefox, and other) are running. This helps detect when the user is working on the computer. This can be used to choose the optimal time for conducting attacks (for example, when the user is away but their browser is still open) or simply to gather information about the victim’s habits.
The information about running browsers is written to a log file on the local host.
Fragment of the deobfuscated script
Victims
According to our telemetry, in late 2025 and early 2026, the identified targets of the described malicious activities are located in Russia and Belarus. The targeted industries mostly include government agencies and diplomatic entities.
We attribute the activity described in this report to the Cloud Atlas APT group with a high degree of confidence. The group used techniques and tools described previously, such as the initial access vector, the Python script for information gathering, and the Tor application for forwarding ports to the Tor network. The victim profile and geography also matches the Cloud Atlas targets.
We couldn’t help but notice some parallels with recent Head Mare activity. The PhantomHeart backdoor (available in Russian only), attributed to Head Mare and used to create an SSH tunnel, was placed in directories actively used by Cloud Atlas:
- C:\Windows\ime
- C:\Windows\System32\ime
- C:\Windows\pla
- C:\Windows\inf
- C:\Windows\migration
- C:\Windows\System32\timecontrolsvc
- C:\Windows\SKB
However, TTPs are still differentiated.
Conclusion
For more than ten years, the Cloud Atlas group has continued its activities and expanded its arsenal. Over the course of last year, many targeted campaigns in general were found to employ ReverseSocks, SSH and Tor, and the use of these utilities was no exception for Cloud Atlas. Creating such backup control channels using publicly available utilities significantly complicates the complete disruption of attackers’ actions on compromised systems. We will continue to closely monitor the group’s activity and describe their new tools and techniques.
Indicators of compromise
Additional information about this activity, including indicators of compromise, is available to customers of the Kaspersky Intelligence Reporting Service. If you are interested, please contact [email protected].
PowerCloud
7A95360B7E0EB5B107A3D231ABBC541A C:\Windows\wininet.exe
C0D1EAA15A2CEFBAB9735787575C8D8E C:\Windows\LiveKernelReports\update.exe
D5B38B252CF212A4A32763DE36732D40 C:\Windows\ime\imejp\dicts\i39884.exe
3C75CEDB1196DF5EAB91F31411ED4B33 C:\pla\reports.exe
42AC350BFBC5B4EB0FEDBA16C81919C7 C:\ProgramData\update_[redacted].exe
493B901D1B33EB577DB64AADD948F9CE C:\Windows\migration\wtr\MicrosoftBrowser.exe
2CABB721681455DAE1B6A26709DEF453 C:\Windows\pla\reports\winlog.exe
1B39E86EB772A0E40060B672B7F574F1 C:\Windows\System32\timecontrolsvc\vmnetdrv64.exe
1D401D6E6FC0B00AAA2C65A0AC0CFD6B C:\Windows\setup\scripts\install\software\activation\aact\dfsvc.exe
40A562B8600F843B717BC5951B2E3C29 C:\Windows\branding\scat.exe
F721A76DEB28FD0B80D27FCE6B8F5016 C:\Windows\ime\imekr\dicts\dfsvc.exe
D3C8AFD22BAA306FF659DB1FAC28574A C:\ProgramData\update_[redacted].exe
6D7B2D1172BBDB7340972D844F6F0717 C:\Users\[redacted]\AppData\Local\1c\1cv8\1cv8ud.exe
C:\Users\[redacted]\AppData\Local\1c\1cv8\svc.exe
9769F43B9DE8D19E803263267FA6D62E C:\Users\[redacted]\AppData\Local\1c\1cv8\1cv8ud.exe
63B6BE9AE8D8024A40B200CCCB438F1D C:\Windows\notepad.exe
6AA586BCC45CA2E92A4F0EF47E086FA1 C:\Windows\splwow32.exe
EBA3BCDB19A7E256BF8E2CC5B9C1CCA9 C:\Users\[redacted]\Desktop\soc\stant.exe
B4E183627B7399006C1BC47B3711E419 C:\WINDOWS\ime\service.exe
F56B31A4B47AD3365B18A7E922FBA1A8 dfsvc.exe
F6F62456FB0FCC396FB654CBED339BC3 –
25C8ED0511375DCA57EF136AC3FA0CCA C:\branding\dwmw.exe
Browser checker
5329F7BFF9D0D5DB28821B86C26D628F C:\ProgramData\checker_[redacted].exe
ReverseSocks
2B4BA4FACF8C299749771A3A4369782E C:\Windows\PLA\System\bounce.exe
C:\Windows\pla\print_status.exe
BA9CE06641067742F2AFC9691FAFF1DC C:\ProgramData\hp\client.exe
FB0F8027ACF1B1E47E07A63D8812ED50 C:\Windows\System32\timecontrolsvc\vmnetdrv64.exe
BBF1FA694122E07635DEEAC11AD712F8 C:\Windows\System32\HostManagement.exe
F301AA3D62B5095EEC4D8E34201A4769 C:\Windows\ime\imejp\msfu.exe
F9C3BBE108566D1A6B070F9C5FB03160 C:\Windows\ime\imetc\help\IMTCEN14.exe
Malicious MS Office documents
369B75BDCDED16469EDE7AB8BEDCFAE1
9EAAE9491F6A50D6DF0BE393734A44CB
3E6E9DF00A764B348EC611EE8504ACA0
9BD788F285E32A05E6591D1EB36EBFFC
F42085522EC2EBB16EDCF814E7C330AD
2042EB5D52F0B535A1CE6B6F954C8C2B
2AA1E9765EF6B00B94A9B6BE0041436A
36120F5E9411BCBAC7104EF3FA964ED2
5000A353399500BC78381DC95B6ED2DC
579A9952D31CAD801A3988DBE7914CE7
867B634588C0FD6B26684D502C15AB03
38FA4306FA4406BA31CF171AF4D36E34
83EDDE9F7EEEFAC0363413972F35572B
CC751619BFEC0DC4607C17112B9E3B2C
A632858F14B36F03D0F213F5F5D6BFF2
097CA205AD9E3B72018750280904718C
69121C36EB8BF77962DCA825FCFFD873
C5702EB250F855C8C872FFFB9BB656ED
ED34F5A136FBA4FDEA976570FAA33ED7
0577DB70844E88B32B954906E2F20798
28ECF8FB6719E14231B94B4D37629B0E
0857C84B62289A1A9F29E19244E9A499
0C514E137860F489E3801213460EF938
50568B1F9335A7E3BA4E5DF035A8FB86
7F776AD200287D6DE14A29158C457179
51F7F794ED43FB90D0F8EBBB5EFFE628
B8C753DD254509FBA5077FFD5067EAB0
BC3739DEC8CD8F54F3F60A85F3ED600E
EC076CD21C483A40156F4E40D08DADED
216CB7F31D383C0DD892B284DF05A495
116F59E70A9DF97F4ADAEA71EECB1E9A
7242AC065B50BCDE9308756B49DBADCB
8158552950D2E13B075001CE0C52AA97
A75DBED984963B9AB21309C5B2F8FD9B
0320DD389FDBAB25D46792BD2817675E
5339D1A666F3E40FE756505CF1D87D4B
67D7E3AEEB673BF60C59361C12A4ED81
89572F0ED20791A5AC9FC4267D67CCB0
B6AAE073E7BFEBF4D643C2BBEB5C02E1
344CA9EA07CD4AC90EF27F8890D4EC05
Domains and IPs
Reverse SSH/Socks domains
tenkoff[.]org
cloudguide[.]in
goverru[.]com
kufar[.]org
ultimatecore[.]net
spbnews[.]net
onedrivesupport[.]net
Malicious and compromised domains used in MS Office documents
amerikastaj[.]com
bigbang[.]me
paleturquoise-dragonfly-364512.hostingersite[.]com
wizzifi[.]com
totallegacy[.]org
mamurjor[.]com
landscapeuganda[.]com
lafortunaitalian.co[.]uk
kommando[.]live
internationalcommoditiesllc[.]com
humanitas[.]si
fishingflytackle[.]com
firsai.tipshub[.]net
alnakhlah.com[.]sa
allgoodsdirect.com[.]au
agenciakharis.com[.]br
Powershell payload staging
istochnik[.]org
znews[.]neti
investika-club[.]com
194.102.104[.]207
46.17.45[.]56
46.17.45[.]49
46.17.44[.]125
46.17.44[.]212
185.22.154[.]73
194.87.196[.]163
195.58.49[.]9
93.125.114[.]193
93.125.114[.]57
45.87.219[.]116
37.228.129[.]224
185.53.179[.]136
185.126.239[.]77
5.181.21[.]75
146.70.53[.]171
45.15.65[.]134
185.250.181[.]207
81.30.105[.]71
File paths
VBS scripts
WriteToSchedulerKillSSH.vbs
Create_task_day.vbs
WriteToSchedulerGenerateKey.vbs
C:\Windows\INF\Run.vbs
c:\Windows\INF\install.vbs
Update.vbs
c:\Windows\PLA\System\Gen.vbs
C:\Windows\INF\GenK.vbs
c:\Windows\PLA\System\Kill.vbs
c:\Windows\PLA\System\Run.vbs
ssh.exe
c:\Windows\ime\imejp\Asset.exe
c:\Windows\PLA\System\conhosts.exe
c:\Windows\INF\BITS\esentprf.exe
c:\Windows\INF\MSDTC\RuntimeBrokers.exe
c:\Windows\inf\diagnostic.exe
ReverseSocks
C:\Windows\PLA\System\bounce.exe
C:\ProgramData\hp\client.exe
C:\Windows\System32\timecontrolsvc\vmnetdrv64.exe
Tor client
C:\Windows\Resources\Update\Intel.exe
C:\Windows\INF\package.exe
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/cloud-atlas-2026/119895/