AI shrinks vulnerability exploitation window to hours
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2025-55182 | Unauthenticated RCE in React Server Components (React2Shell) CVE-2025-55182 is a critical (CVSS 10.0) pre-authentication remote code execution flaw (CWE-502, deserialization of untrusted data) in React Server Components, specifically the react-server-dom-parcel, react-server-dom-turbopack, and react-server-dom-webpack packages in versions 19.0.0, 19.1.0, 19.1.1, and 19.2.0. It is triggered when the vulnerable code unsafely deserializes payloads from HTTP requests sent to Server Function endpoints, requiring no authentication or user interaction. An attacker gains arbitrary code execution on the affected server (CVSS scope changed, with high impact to confidentiality, integrity, and availability), and reporting notes a campaign in which hackers used the flaw to breach 766 Next.js hosts and steal credentials. Any React/Next.js application exposing Server Functions with the affected React versions is in scope, which given the ubiquity of React and Next.js is a very large deployed base. Exploitation is confirmed in the wild: the flaw was added to CISA's Known Exploited Vulnerabilities catalog on 2025-12-05 with known ransomware use, EPSS puts the 30-day exploitation probability at 99.8%, multiple public PoC/scanner repositories are available, and coverage has dubbed the flaw React2Shell. Do: Upgrade the react-server-dom-webpack, react-server-dom-parcel, and react-server-dom-turbopack packages to the vendor-patched releases (any version later than the vulnerable 19.0.0, 19.1.0, 19.1.1, and 19.2.0 line) and update Next.js per Vercel's advisory; as a KEV entry, U.S. federal agencies must apply vendor mitigations per BOD 22-01 or discontinue use. Audit internet-exposed Server Function endpoints for the vulnerable React versions and review logs for exploitation activity, including the reported campaign that breached 766 Next.js hosts and stole credentials, then rotate any exposed credentials. | 10.0 | 100% | KEV ransomware PoC ×7 |
| mass≈1M+ internet-facing Next.js/React Server Components deployments (order-of-magnitude estimate) |
Full article501 words · extracted from helpnetsecurity.com · click to collapse
Time has become organizations’ biggest vulnerability because the gap between vulnerability discovery and exploitation has narrowed to hours, according to Synack’s 2026 State of Vulnerabilities Report.
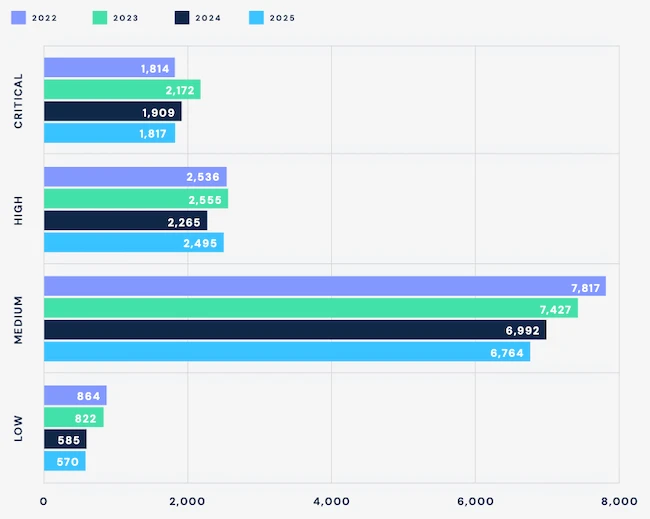
Total vulnerabilities by severity (2022-2025) (Source: Synack)
AI expands the attack surface
Agentic AI systems that act autonomously across systems introduce new risks that require human expertise to identify and understand. Automated scanning detects known signatures but can miss logic flaws, misconfigurations, and unexpected behavior.
In 2025, mean time to remediation dropped by approximately 47% across all severity levels, showing that the industry is moving toward continuous security validation, with periodic testing serving a supporting role.
Published CVEs reached 48,244 in 2025, a 20% year-over-year increase. Customer programs that maintained stable findings against that backdrop indicate that security posture is keeping pace with a faster-moving environment.
“Adversaries can identify and exploit vulnerabilities within increasingly shorter timeframes. Organizations that continuously validate security across their environment are responding faster and closing critical exposure windows earlier,” said Dr. Mark Kuhr, CTO of Synack.
Low- and medium-severity findings declined in 2025. High-severity findings increased, especially in mature programs that tend to generate less noise.
AI-enabled adversaries are shrinking the gap between a CVE’s public disclosure and the first observed exploitation by threat actors. Unexpected zero-day vulnerabilities such as React2Shell (CVE-2025-55182) allowed unauthenticated attackers to send malicious HTTP requests that resulted in remote code execution on servers.
In 2025, total vulnerability volume remained relatively stable, but high-severity vulnerabilities increased by 10% compared with 2024.
Familiar vulnerabilities, faster exploitation
The most frequently identified vulnerability remained cross-site scripting (XSS), followed by authorization and permission issues. Content injection, brute-force attacks, and remote code execution increased throughout 2025. These trends show growing attacker focus on social engineering, identity-based exploitation, supply chain vulnerabilities, and authentication boundaries, aligning with AI-enabled adversaries testing access controls.
Average mean time to remediation dropped from 63 days in 2024 to 38 days in 2025, while critical vulnerabilities were remediated 25 days faster. Shorter remediation timelines reflect pressure from AI-enabled attackers that continue to reduce average time to exploit. PTaaS platforms help teams correlate vulnerability data across assets and business units, improving prioritization and workflows.
Growing infrastructure expands exposure
Security teams in retail, financial services, government, technology, and manufacturing continue to face challenges in mapping IT assets and infrastructure. Average asset counts grew or remained stable in 2025, except in retail. Manufacturing recorded the sharpest increase, from 2,053 to 2,486 assets per organization.
Subdomains remained the largest asset category by volume, averaging about 40,000 per organization. Web applications also increased year over year, showing faster development cycles associated with AI coding assistants.
Critical and high-severity vulnerabilities accounted for 37% of findings across these industries. Manufacturing, technology, and government recorded the largest share of critical and high-severity findings. Retail and financial services remained below the overall average.
The technology sector accounted for the largest share of critical SQL injection findings, followed by financial services. Critical remote code execution findings were distributed more evenly across sectors.
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.helpnetsecurity.com/2026/05/18/synack-2025-ai-driven-vulnerability-trends-report/