What to know about the HTTP/2 Rapid Reset DDoS attacks
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2023-44487 | Rapid Reset Denial-of-Service in HTTP/2 (CWE-400 Resource Exhaustion) CVE-2023-44487 is a flaw in the HTTP/2 protocol's stream handling (CWE-400, uncontrolled resource consumption) in which a client opens a large number of streams and immediately cancels them with RST_STREAM frames, forcing the server to repeatedly allocate and tear down per-stream state. When this 'rapid reset' pattern is driven at high volume from many sources, it exhausts server CPU and memory, producing a distributed denial-of-service; Google, Cloudflare and AWS all reported record-scale attacks using this technique. The only impact is availability (denial of service), not code execution or data exposure, but any system speaking HTTP/2 is in scope, including web servers, load balancers, API gateways and CDN edges, and client-side implementations are also affected in a reverse-direction variant. Because the weakness is in the protocol specification itself (attributed to IETF HTTP/2), virtually every deployment with HTTP/2 enabled is affected until vendors ship mitigations or patches. Exploitation is confirmed in the wild: CISA added it to the Known Exploited Vulnerabilities catalog on 2023-10-10, and EPSS assigns a 100% probability of exploitation within 30 days. Do: Apply mitigations per vendor instructions as required by CISA KEV/BOD 22-01 guidance — most major web server, load balancer, and CDN vendors have shipped patches or tuning knobs, so check and update each HTTP/2-facing component in your estate. Where patching is not yet possible, limit the number of concurrent HTTP/2 streams per connection, rate-limit new stream creation and inbound HTTP/2 connections, or disable HTTP/2 on internet-exposed servers. Confirm with your CDN or cloud provider that rapid-reset DDoS mitigations are in place at the edge. | 7.5 | 100% | KEV |
| massmillions of servers and network edges (HTTP/2 is negotiated on a large share of HTTPS-capable hosts in public internet scans) |
Full article774 words · extracted from blog.talosintelligence.com · click to collapse
Wednesday, October 11, 2023 19:06
Cisco Talos is actively tracking the novel distributed denial-of-service (DDoS) attacks cloud services provider Cloudflare disclosed earlier this week. The techniques described in Cloudflare’s blog post resulted in a record-breaking DDoS attack and could facilitate much larger attacks in the future.
CVE-2023-44487
CVE-2023-44487, a vulnerability in the HTTP/2 protocol, was recently used to launch intensive DDoS attacks against several targets. The problem lies in the way that HTTP/2 protocol handles request cancellations or resets. When a client issues a reset for an HTTP/2 request, this consumes resources on the server as it cancels the corresponding stream. However, after issuing a reset, the client can instantly open a new stream. The rapid opening and canceling of the HTTP/2 streams is what causes the denial of service. Because HTTP/2 has been integrated into a variety of different web platforms, it is likely that this vulnerability will have a widespread impact.
HTTP/2 made improvements over previous versions of the HTTP protocol, including changing the ways HTTP requests were handled. Earlier versions of HTTP rely on request-response serialization, in which a client sends a request to a server and then receives a response from that server over the same TCP connection. HTTP/2, meanwhile, formats requests and responses into HTTP/2 frames. Each frame has its own stream ID, used to identify which requests and responses correspond with each other. This allows for multiplexing and concurrent requests. This design is much more in line with the way web traffic occurs today, typically requiring large amounts of asynchronous requests for various types of data as web pages load.
However, this new mechanism is where the denial-of-service vulnerability lies. Attackers have discovered that, by creating large amounts of requests and resets in a short period of time, they can consume valuable resources on HTTP/2 servers, resulting in a denial of service. The challenge is that when viewing certain types of web pages, large amounts of these requests are expected. This can also include some resets if the user is quickly scrolling through a page to speed up the rendering of the images ahead, for example. The other compounding factor is that there is a hard limit to the amount of concurrent connections HTTP/2 servers can support. According to RFC 9113, it is recommended that the SETTINGS_MAX_CONCURRENT_STREAMS for an HTTP/2 server be no smaller than 100, “so as to not unnecessarily limit parallelism.” If an attacker with a large number of systems under their control can fill up these connection pools with open or half-open HTTP/2 connections the HTTP/2 server can be overwhelmed.
This is exactly what has been occurring at Cloudflare and other large providers. Beginning in late August, these networks started seeing large-scale DDoS attacks leveraging this novel technique eventually peaking at more than 200 million requests a second, accomplished with a botnet of only 20,000 systems. If this type of attack was launched with a much larger botnet, the traffic volume could be orders of magnitude greater and have a much larger potential impact. As such, organizations are urged to patch or mitigate as quickly as possible.
Coverage
Ways our customers can detect and block this threat are listed below.
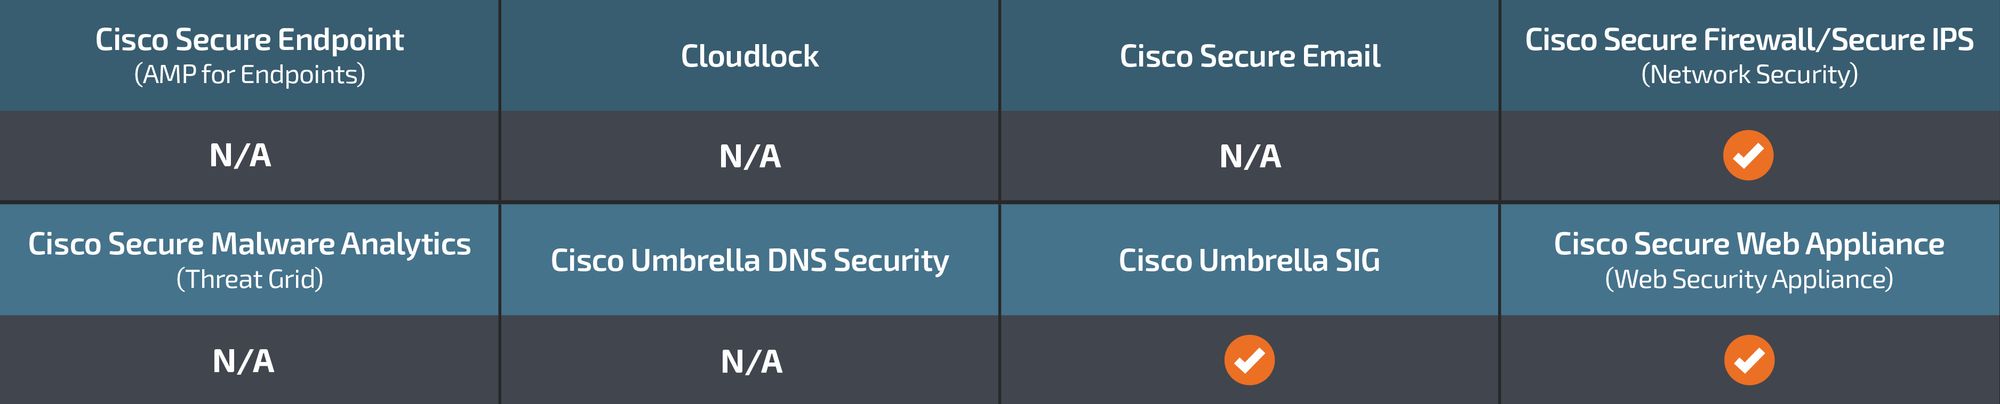
Cisco Secure Endpoint (formerly AMP for Endpoints) is ideally suited to prevent the execution of the malware detailed in this post. Try Secure Endpoint for free here.
Cisco Secure Email (formerly Cisco Email Security) can block malicious emails sent by threat actors as part of their campaign. You can try Secure Email for free here.
Cisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.
Cisco Secure Network/Cloud Analytics (Stealthwatch/Stealthwatch Cloud) analyzes network traffic automatically and alerts users of potentially unwanted activity on every connected device.
Cisco Secure Malware Analytics (Threat Grid) identifies malicious binaries and builds protection into all Cisco Secure products.
Umbrella, Cisco’s secure internet gateway (SIG), blocks users from connecting to malicious domains, IPs and URLs, whether users are on or off the corporate network. Sign up for a free trial of Umbrella here.
Cisco Secure Web Appliance (formerly Web Security Appliance) automatically blocks potentially dangerous sites and tests suspicious sites before users access them.
Additional protections with context to your specific environment and threat data are available from the Firewall Management Center.
Cisco Duo provides multi-factor authentication for users to ensure only those authorized are accessing your network.
Open-source Snort Subscriber Rule Set customers can stay up to date by downloading the latest rule pack available for purchase on Snort.org.
Snort SIDs:
62519
Text extracted automatically; images, tables and formatting may be missing. Original: https://blog.talosintelligence.com/http-2-rapid-reset-ddos-attacks/