PeckBirdy C2 Traffic Seen Across Enterprise Networks While Hiding Behind Casino Domains
Infoblox and Trend Micro detail China-aligned actors hiding PeckBirdy JavaScript C2 behind Chinese casino domains, with over 3% of enterprise customers resolving malicious domains.
Infoblox telemetry found just over 3% of enterprise customers resolved at least one PeckBirdy C2 domain, including cache-mcp[.]com and mcp-source[.]online, indicating reach beyond the campaign's apparent Asian victim focus. Trend Micro links PeckBirdy, a JScript C2 framework active since 2023, to China-aligned campaigns targeting Chinese gambling organizations, Asian government entities, and private-sector organizations. Low-quality casino portals such as vip311[.]cc embed malicious JavaScript and WebSocket C2 endpoints that evade scanners, delivering tailored landing scripts for MSHTA, HTML, and WScript execution and abusing Windows LOLBins. Infoblox tracks roughly 1.7 million Chinese-language casino domains, with the FUNNULL CDN and Vigorish Viper clusters covering about 81% of that population.
- Just over 3% of Infoblox enterprise customers resolved at least one PeckBirdy C2 domain
- Casino portals serve as cover for malicious JavaScript, WebSocket C2, and service-worker activity
- PeckBirdy delivers landing scripts for HTA, HTML, and WScript execution, abusing Windows LOLBins
- Key indicators include cache-mcp[.]com, mcp-source[.]online, and cache-cdn[.]org
- Defenders urged to classify casino domains by behavioral risk, not web-filter category
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | 11170011.com | ry Domains Illegal Chinese-Language Casino Domains (Type 1) 11170011[.]com puqxr[.]com 80074[.]cc Scambling Domains (Type 2) dollyca |
| domain | 80074.cc | Language Casino Domains (Type 1) 11170011[.]com puqxr[.]com 80074[.]cc Scambling Domains (Type 2) dollycasino[.]com dragobet[.]n |
| domain | appcasino.online | Scambling Domains (Type 2) dollycasino[.]com dragobet[.]net appcasino[.]online PeckBirdy C2 and Decoy Domains (Type 3) vip311[.]cc Decoy |
| domain | cache-cdn.org | ine, alongside previously documented infrastructure such as cache-cdn[.]org. Infoblox found that detection coverage declined sharply |
| domain | cache-mcp.com | casino branding while embedding the PeckBirdy-linked domain cache-mcp[.]com. Analysis of the malicious JavaScript then exposed an add |
| domain | dollycasino.com | 011[.]com puqxr[.]com 80074[.]cc Scambling Domains (Type 2) dollycasino[.]com dragobet[.]net appcasino[.]online PeckBirdy C2 and Decoy |
| domain | dragobet.net | ains or have broken experiences like the live site found at dragobet[.]net. Drago Bet Casino (dragobet[.]net) features numerous low- |
| domain | githubassets.net | irdy domains rather than overreacting to a single query for githubassets[.]net, a typosquat-like domain that can also result from develo |
| domain | mcp-source.online | pt then exposed an additional WebSocket-connected endpoint, mcp-source[.]online, which had zero VirusTotal detections at the time Infoblo |
| domain | puqxr.com | ling-themed templates. Screenshot of a recently active site puqxr[.]com hosting a “Point 72” Chinese investment platform featurin |
| domain | vip311.cc | ucture rather than as actual betting services. One example, vip311[.]cc, presented Chinese-language KY casino branding while embe |
Full article941 words · extracted from gbhackers.com · click to collapse
China-aligned threat actors are using low-quality Chinese-language casino and adult websites to conceal PeckBirdy command-and-control infrastructure, creating a detection challenge for enterprises that routinely deprioritize gambling-related domains.
Infoblox telemetry found that just over 3% of enterprise customers resolved at least one PeckBirdy-related C2 domain, indicating that the infrastructure is appearing well beyond the campaign’s apparent Asian victim focus.
The framework enables attackers to remotely deliver and execute JavaScript and to abuse Windows living-off-the-land binaries, including MSHTA and Windows Script Host, across multiple execution paths.
Trend Micro linked the activity to China-aligned campaigns targeting Chinese gambling organizations, Asian government entities, and private-sector organizations.
The latest research highlights a broader abuse of the gambling ecosystem: websites that appear to be disposable, poorly built casino portals can operate as set dressing for malware infrastructure rather than as actual betting services.
One example, vip311[.]cc, presented Chinese-language KY casino branding while embedding the PeckBirdy-linked domain cache-mcp[.]com.
Analysis of the malicious JavaScript then exposed an additional WebSocket-connected endpoint, mcp-source[.]online, which had zero VirusTotal detections at the time Infoblox reviewed it.
This operational model works because casino domains are frequently dismissed as policy violations, nuisance traffic, or consumer-fraud concerns rather than investigated as possible intrusion infrastructure.
The sites are visually difficult to distinguish from two much larger categories: illegal Chinese-language gambling portals used for wagering and money laundering, and “scambling” sites that accept deposits but frustrate or block withdrawals.
In the PeckBirdy cases, however, there are no genuine customers. The casino interface exists to blend malicious JavaScript, C2 requests, and WebSocket traffic into a large, noisy population of suspicious-looking domains.
Infoblox tracks approximately 1.7 million Chinese-language casino domains associated with illegal gambling activity.
The company says the largest clusters include the FUNNULL CDN and Vigorish Viper networks, which together account for roughly 81% of that observed domain population.
Such scale gives operators and associated threat actors abundant cover: domains can be registered, abandoned, redirected, or replaced quickly while retaining familiar gambling-themed templates.
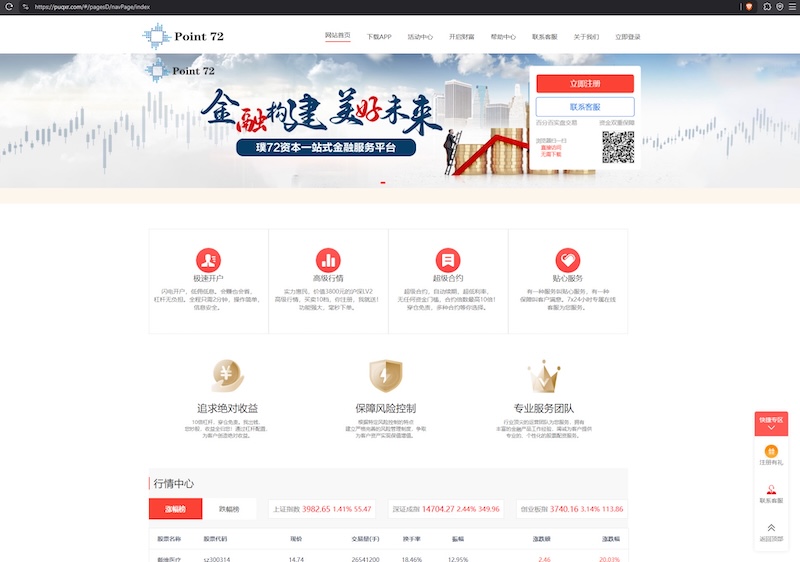
Infoblox Researchers said that, PeckBirdy is a JScript-based command-and-control framework that Trend Micro says has been active since 2023.
Casino Domains Hide C2 Traffic
The United Nations Office on Drugs and Crime has separately warned that illegal online gambling is no longer merely a regulatory issue in Southeast Asia.
Its 2026 regional assessment described the sector as a core revenue source and operational enabler for transnational organized crime, converging with cyber-enabled fraud, underground banking, money laundering, and trafficking.
Some scambling websites will use multiple domains or have broken experiences like the live site found at dragobet[.]net.
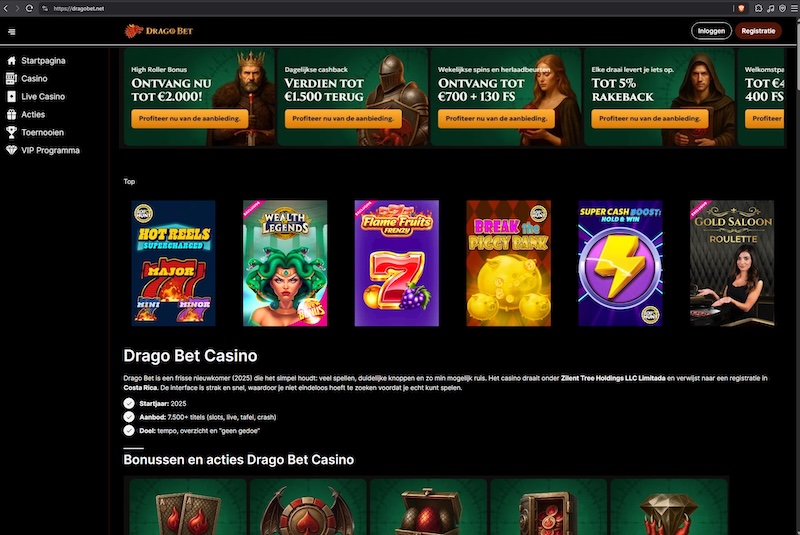
For defenders, that means a casino-themed domain should not automatically be treated as low-priority or solely as a web-filtering issue. Its category may reveal little about what it does at the DNS, browser, endpoint, or network layer.
The most concerning PeckBirdy indicators include cache-mcp[.]com and mcp-source[.]online, alongside previously documented infrastructure such as cache-cdn[.]org.
Infoblox found that detection coverage declined sharply for infrastructure that was harder for automated scanners to observe, particularly when the malicious behavior involved service-worker registration or WebSocket connections.
The use of WebSockets is especially relevant because many security workflows focus on domain reputation, HTTP requests, and downloaded files.
A browser session that loads a seemingly ordinary gambling page may establish a persistent connection to a second-stage C2 domain that is not obvious in standard URL inspection or passive scanning.
Trend Micro’s reporting shows PeckBirdy can expose API paths that download a main script and tailored landing scripts for HTA, HTML, and WScript execution.
This makes correlated telemetry essential: DNS resolution, browser process lineage, script-host execution, outbound WebSocket activity, and subsequent LOLBin use should be examined together rather than in isolation.
Security teams should investigate enterprise resolution of distinctive PeckBirdy domains rather than overreacting to a single query for githubassets[.]net, a typosquat-like domain that can also result from developer or user mistakes.
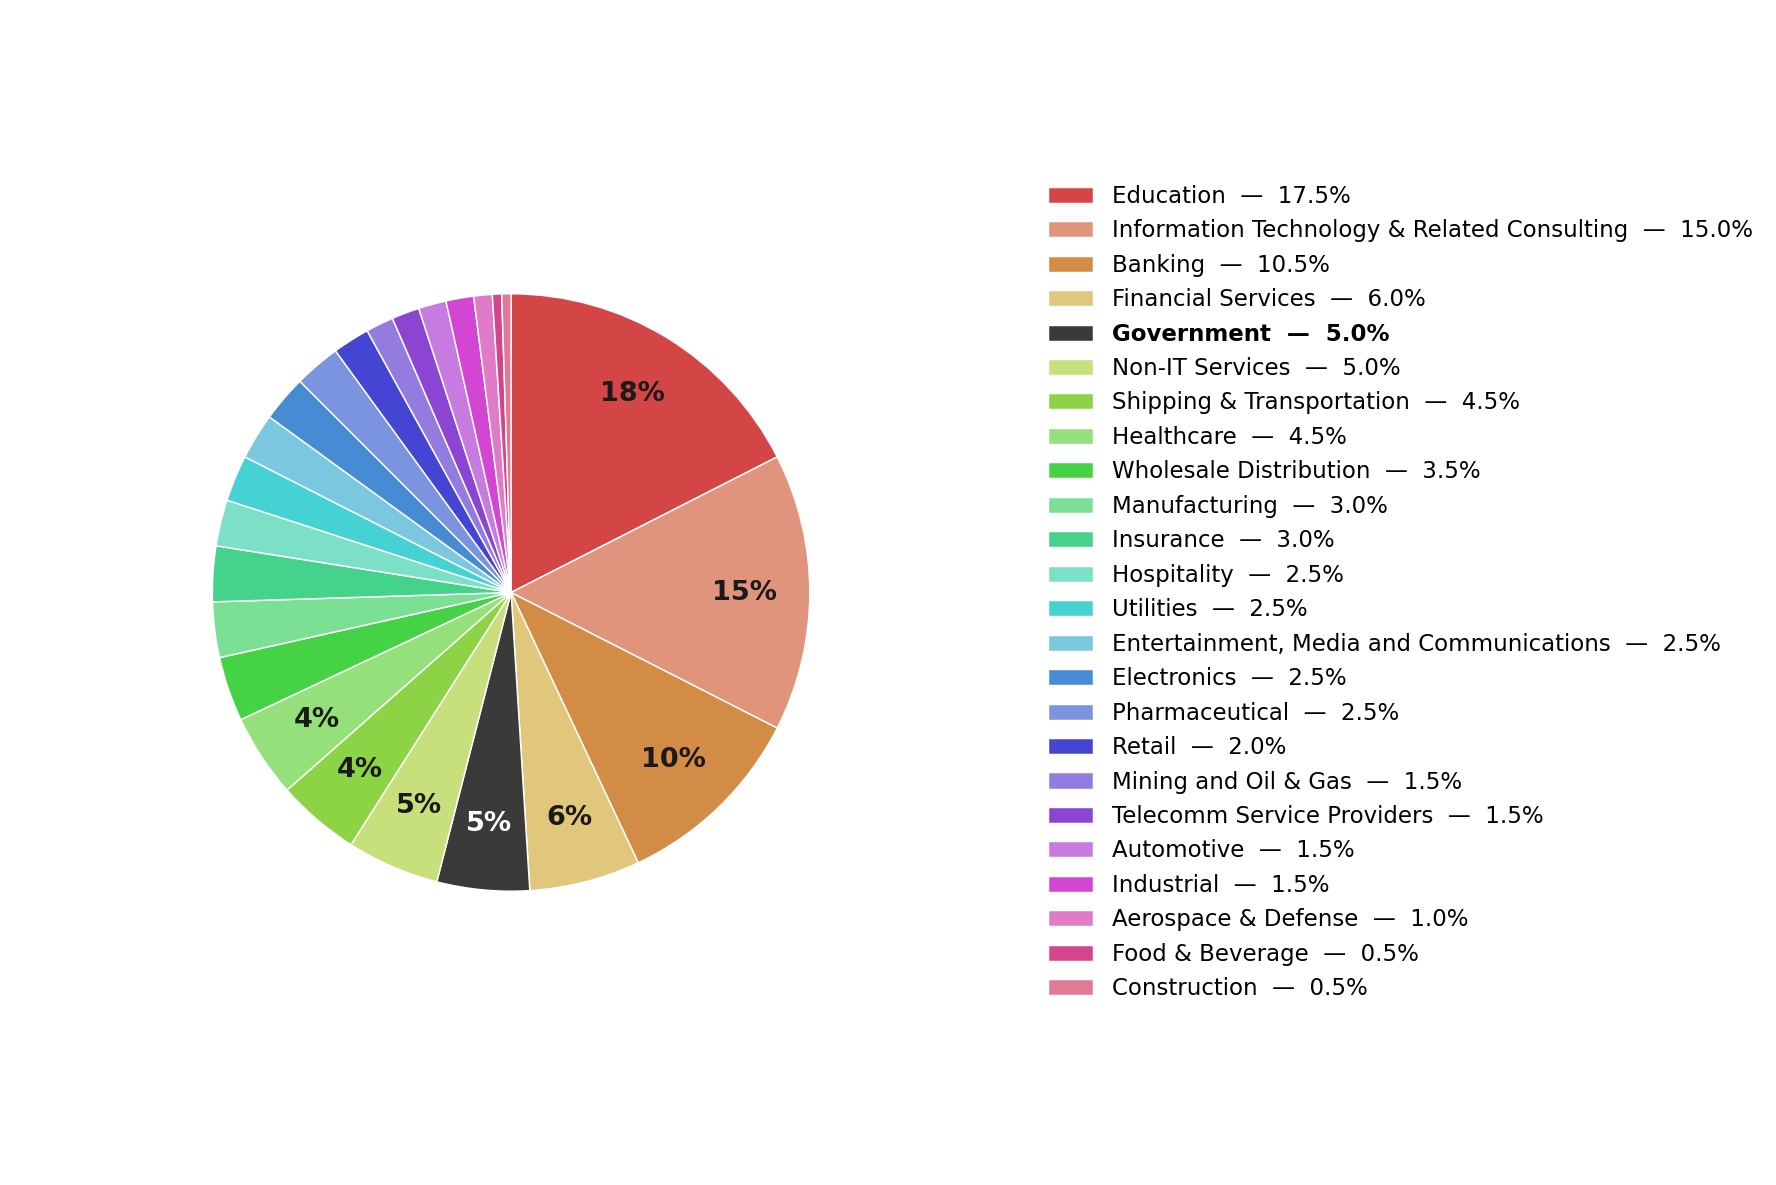
Infoblox noted that organizations resolving three to ten distinct PeckBirdy C2 domains present a more concerning pattern than those with only one or two observed domains.
Network defenders should block and retrospectively hunt for known PeckBirdy domains, inspect browser traffic to casino and adult domains for service workers and WebSocket destinations, and correlate those connections with mshta.exe, wscript.exe, cscript.exe, PowerShell, and unusual child-process activity.
Organizations should also ensure DNS security controls classify these domains by behavioral risk rather than relying only on gambling or adult-content categories.
The campaign demonstrates that online casino infrastructure is no longer only a fraud, compliance, or acceptable-use problem.
In PeckBirdy operations, it has become a plausible front for persistent malware command infrastructure targeting enterprises, financial organizations, educational institutions, and government environments.
IOCs
| Category | Domains |
|---|---|
| Illegal Chinese-Language Casino Domains (Type 1) | 11170011[.]compuqxr[.]com80074[.]cc |
| Scambling Domains (Type 2) | dollycasino[.]comdragobet[.]netappcasino[.]online |
| PeckBirdy C2 and Decoy Domains (Type 3) | vip311[.]cc Decoy domaincache-cdn[.]orgcache-mcp[.]com |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Cut every SOC alert investigation by 21 min. Power your SOC with instant IOC context for immediate response: Integrate TI Lookup in your SOC
Mayura Kathirhttps://gbhackers.com/
Mayura Kathir is a cybersecurity reporter at GBHackers News, covering daily incidents including data breaches, malware attacks, cybercrime, vulnerabilities, zero-day exploits, and more.
Text extracted automatically; images, tables and formatting may be missing. Original: https://gbhackers.com/casino-domains-hide-c2-traffic/