Wormable Flaw, 0days Lead Sept. 2022 Patch Tuesday
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2022-24521 | Out-of-bounds Write Privilege Escalation in Microsoft Windows CLFS Driver CVE-2022-24521 is an elevation-of-privilege flaw in the Windows Common Log File System (CLFS) driver, a kernel component, caused by an out-of-bounds write (CWE-787). A local attacker who already has limited privileges on an affected Windows machine can trigger the bug and gain elevated (SYSTEM/administrator) rights without any user interaction. Because the CLFS driver is part of the operating system, every user and service on an unpatched host is exposed to post-compromise escalation, which ransomware operators use to move from an initial foothold to full control. Affected products per the data include Windows 10 releases 1507, 1607, 1809, 1909, 20H2, 21H1, and 21H2, Windows 11 21H2, Windows 7, Windows 8.1, Windows RT 8.1, and Windows Server 2008. The flaw was patched in Microsoft's April 2022 Patch Tuesday, added to CISA's Known Exploited Vulnerabilities catalog on 2022-04-13, and is known to be used in ransomware campaigns, with public reporting tying exploitation to Cuba ransomware activity. Do: Apply the April 2022 Microsoft security updates (Patch Tuesday, released April 12, 2022) to all affected Windows 10/11, Windows 7/8.1/RT 8.1, and Windows Server 2008 systems immediately, per the CISA KEV required action; note that Windows 7/8.1/RT 8.1 and Server 2008 may require Extended Security Updates to receive the fix. Because this is a local privilege escalation, prioritize hosts reachable for initial access, review endpoint telemetry for suspicious limited-user-to-SYSTEM activity, and watch for indicators associated with Cuba ransomware campaigns exploiting this flaw. | 7.8 | 7% | KEV ransomware |
| mass≈1 billion+ Windows devices (the CLFS driver ships in all supported Windows 10/11 and legacy client releases) | |
| CVE-2022-32817 | An out-of-bounds read issue was addressed with improved bounds checking. An out-of-bounds read issue was addressed with improved bounds checking. This issue is fixed in watchOS 8.7, tvOS 15.6, iOS 15.6 and iPadOS 15.6, macOS Monterey 12.5. An app may be able to disclose kernel memory. NVD description · AI analysis pending | 5.5 | <1% |
| — | ||
| CVE-2022-32983 | Knot Resolver through 5.5.1 may allow DNS cache poisoning when there is an attempt to limit forwarding actions by filters. Knot Resolver through 5.5.1 may allow DNS cache poisoning when there is an attempt to limit forwarding actions by filters. NVD description · AI analysis pending | 5.3 | <1% |
| — | ||
| CVE-2022-32984 | BTCPay Server 1.3.0 through 1.5.3 allows a remote attacker to obtain sensitive information when a public Point of Sale app is exposed. BTCPay Server 1.3.0 through 1.5.3 allows a remote attacker to obtain sensitive information when a public Point of Sale app is exposed. The sensitive information, found in the HTML source code, includes the xpub of the store. Also, if the store isn't using the internal lightning node, the credentials of a lightning node are exposed. NVD description · AI analysis pending | 7.5 | 1% |
| — | ||
| CVE-2022-34700 +1 in the same advisory: …35805 | Microsoft Dynamics CRM (on-premises) Remote Code Execution Vulnerability Microsoft Dynamics CRM (on-premises) Remote Code Execution Vulnerability NVD description · AI analysis pending | 8.8 | 3% |
| — | ||
| CVE-2022-34721 | Windows Internet Key Exchange (IKE) Protocol Extensions Remote Code Execution Vulnerability Windows Internet Key Exchange (IKE) Protocol Extensions Remote Code Execution Vulnerability NVD description · AI analysis pending | 9.8 group max | 79% |
| — | ||
| CVE-2022-37969 | Out-of-bounds write flaw in Microsoft Windows CLFS driver enables privilege escalation The Windows Common Log File System (CLFS) driver contains an input-validation flaw (CWE-20) that leads to an out-of-bounds write (CWE-787), allowing an attacker who already has a foothold or local access on a system to escalate privileges. It is triggered when the driver processes malformed or specially crafted common log file data, rather than via a remote network request on its own. Successful exploitation yields elevated (typically SYSTEM-level) privileges, giving the attacker full control of the host and making the bug a common post-exploitation link in ransomware chains. CISA lists the affected product broadly as 'Microsoft Windows', so essentially all Windows installations current at the time of disclosure were in scope. The flaw is confirmed exploited in the wild: CISA added it to the KEV catalog on 2022-09-14 with known ransomware use, EPSS puts 30-day exploitation probability at 28.3% (98th percentile), and no public PoC is known. Do: Apply Microsoft's September 2022 (or later) cumulative updates to every Windows host per vendor instructions, prioritizing endpoints and servers exposed for user or remote access. Because this is a local privilege escalation, treat it as a post-exploitation risk: also harden and patch initial-access surfaces (RDP, VPN, other exposed services) and hunt for signs of compromise such as unexpected SYSTEM-spawned processes or anomalous activity involving clfs.sys. Ransomware operators are known to use this bug, so remediation should be treated as urgent. | 7.8 | 28% | KEV ransomware |
| mass>1 billion Windows devices (essentially all Windows installations at the time of disclosure; exploitation requires an existing local foothold) |
Full article1,016 words · extracted from krebsonsecurity.com · click to collapse
This month’s Patch Tuesday offers a little something for everyone, including security updates for a zero-day flaw in Microsoft Windows that is under active attack, and another Windows weakness experts say could be used to power a fast-spreading computer worm. Also, Apple has also quashed a pair of zero-day bugs affecting certain macOS and iOS users, and released iOS 16, which offers a new privacy and security feature called “Lockdown Mode.” And Adobe axed 63 vulnerabilities in a range of products.
Microsoft today released software patches to plug at least 64 security holes in Windows and related products. Worst in terms of outright scariness is CVE-2022-37969, which is a “privilege escalation” weakness in the Windows Common Log File System Driver that allows attackers to gain SYSTEM-level privileges on a vulnerable host. Microsoft says this flaw is already being exploited in the wild.
Kevin Breen, director of cyber threat research at Immersive Labs, said any vulnerability that is actively targeted by attackers in the wild must be put to the top of any patching list.
“Not to be fooled by its relatively low CVSS score of 7.8, privilege escalation vulnerabilities are often highly sought after by cyber attackers,” Breen said. “Once an attacker has managed to gain a foothold on a victim’s system, one of their first actions will be to gain a higher level of permissions, allowing the attacker to disable security applications and any device monitoring. There is no known workaround to date, so patching is the only effective mitigation.”
Satnam Narang at Tenable said CVE-2022-24521 — a similar vulnerability in the same Windows log file component — was patched earlier this year as part of Microsoft’s April Patch Tuesday release and was also exploited in the wild.
“CVE-2022-37969 was disclosed by several groups, though it’s unclear if CVE-2022-37969 is a patch-bypass for CVE-2022-24521 at this point,” Narang said.
Another vulnerability Microsoft patched this month — CVE-2022-35803 — also seems to be related to the same Windows log file component. While there are no indications CVE-2022-35803 is being actively exploited, Microsoft suggests that exploitation of this flaw is more likely than not.
Trend Micro’s Dustin Childs called attention to CVE-2022-34718, a remote code execution flaw in the Windows TCP/IP service that could allow an unauthenticated attacker to execute code with elevated privileges on affected systems without user interaction.
“That officially puts it into the ‘wormable’ category and earns it a CVSS rating of 9.8,” Childs said. “However, only systems with IPv6 enabled and IPSec configured are vulnerable. While good news for some, if you’re using IPv6 (as many are), you’re probably running IPSec as well. Definitely test and deploy this update quickly.”
Cisco Talos warns about four critical vulnerabilities fixed this month — CVE-2022-34721 and CVE-2022-34722 — which have severity scores of 9.8, though they are “less likely” to be exploited, according to Microsoft.
“These are remote code execution vulnerabilities in the Windows Internet Key Exchange protocol that could be triggered if an attacker sends a specially crafted IP packet,” wrote Jon Munshaw and Asheer Malhotra. “Two other critical vulnerabilities, CVE-2022-35805 and CVE-2022-34700 exist in on-premises instances of Microsoft Dynamics 365. An authenticated attacker could exploit these vulnerabilities to run a specially crafted trusted solution package and execute arbitrary SQL commands. The attacker could escalate their privileges further and execute commands as the database owner.”
 Not to be outdone, Apple fixed at least two zero-day vulnerabilities when it released updates for iOS, iPadOS, macOS and Safari. CVE-2022-32984 is a problem in the deepest recesses of the operating system (the kernel). Apple pushed an emergency update for a related zero-day last month in CVE-2022-32983, which could be used to foist malware on iPhones, iPads and Macs that visited a booby-trapped website.
Also listed under active attack is CVE-2022-32817, which has been fixed on macOS 12.6 (Monterey), macOS 11.7 (Big Sur), iOS 15.7 and iPadOS 15.7, and iOS 16. The same vulnerability was fixed in Apple Watch in July 2022, and credits Xinru Chi of Japanese cybersecurity firm Pangu Lab.
“Interestingly, this CVE is also listed in the advisory for iOS 16, but it is not called out as being under active exploit for that flavor of the OS,” Trend Micro’s Childs noted. “Apple does state in its iOS 16 advisory that ‘Additional CVE entries to be added soon.’ It’s possible other bugs could also impact this version of the OS. Either way, it’s time to update your Apple devices.”
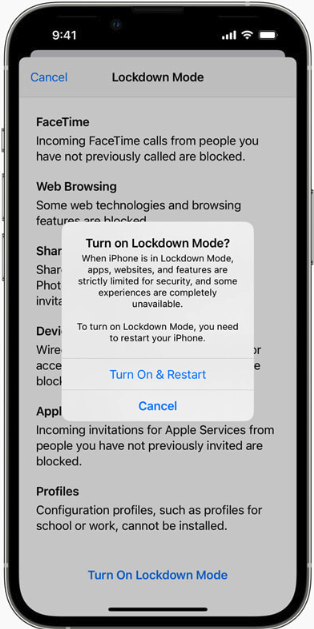
Apple’s iOS 16 includes two new security and privacy features — Lockdown Mode and Safety Check. Wired.com describes Safety Check as a feature for users who are at risk for, or currently experiencing, domestic abuse.
“The tool centralizes a number of controls in one place to make it easier for users to manage and revoke access to their location data and reset privacy-related permissions,” wrote Lily Hay Newman.
“Lockdown Mode, on the other hand, is meant for users who potentially face targeted spyware attacks and aggressive state-backed hacking. The feature comprehensively restricts any nonessential iOS features so there are as few potential points of entry to a device as possible. As more governments and repressive entities around the world have begun purchasing powerful commodity spyware to target individuals of particular importance or interest, iOS’s general security defenses haven’t been able to keep pace with these specialized threats.”
To turn on Lockdown Mode in iOS 16, go to Settings, then Privacy and Security, then Lockdown Mode. Safety Check is located in the same area.
Finally, Adobe released seven patches addressing 63 security holes in Adobe Experience Manager, Bridge, InDesign, Photoshop, InCopy, Animate, and Illustrator. More on those updates is here.
Don’t forget to back up your data and/or system before applying any security updates. If you experience glitches or problems installing any of these patches this month, please consider leaving a comment about it below; there’s a decent chance other readers have experienced the same and may chime in here with useful tips.
Text extracted automatically; images, tables and formatting may be missing. Original: https://krebsonsecurity.com/2022/09/wormable-flaw-0days-lead-sept-2022-patch-tuesday/