Chaotic Eclipse Releases GenDigital Avast Antivirus ZeroDay PrettyPrague
Researcher Chaotic Eclipse released PrettyPrague, a PoC zero-day privilege escalation exploit against fully patched GenDigital Avast Antivirus.
Security researcher Chaotic Eclipse (also known as INFINITE NIGHTMARE or MSNightmare) published a PoC named PrettyPrague exploiting a zero-day privilege escalation flaw in Avast Antivirus. The PoC abuses a flaw in the Avast Sandbox to dump the Windows SAM database and spawn a SYSTEM-level shell, reportedly working on fully patched Avast and patched Windows 11 25H2. The researcher believes the flaw may also affect other GenDigital products such as AVG and Norton. It follows his recent HardBreacher PoC for a Kaspersky Endpoint Security privilege escalation flaw.
- PoC dumps the SAM database by abusing a vulnerability in Avast Sandbox
- Works on fully patched Avast Antivirus and patched Windows 11 25H2
- Researcher suspects impact on other GenDigital products including AVG and Norton
- Chaotic Eclipse previously released zero-day PoCs for Defender and Kaspersky products
Full article313 words · extracted from securityaffairs.com · click to collapse
 Pierluigi Paganini
 September 01, 2026

Chaotic Eclipse released PrettyPrague, a PoC exploit for a GenDigital Avast Antivirus ZeroDay Elevation of Privileges Vulnerability
Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting GenDigital Avast Antivirus. The researcher named the exploit PrettyPrague, it triggers a privilege escalation flaw.
The researcher claims to have found another zero-day in an antimalware product, this time targeting Avast Antivirus. The PoC exploits a flaw in Avast Sandbox to dump the Windows SAM database and gain a SYSTEM-level shell. It reportedly works even on fully patched Avast Antivirus and Windows 11 25H2. The researcher also suspects the flaw may affect other Gen Digital products, including AVG and Norton.
“Another zeroday in an antimalware provider, I’m not sure but I believe this vulnerability affect other GenDigital products as well (such as AVG, Norton…) For now the PoC is compatible with any version of Avast Antivirus.” reads the announcement. “The PoC will dump the SAM database by abusing a vulnerability in Avast Sandbox and spawn a full SYSTEM shell, at the time of writing this the PoC works with fully patched Avast Antivirus + Patched Windows 11 25H2”
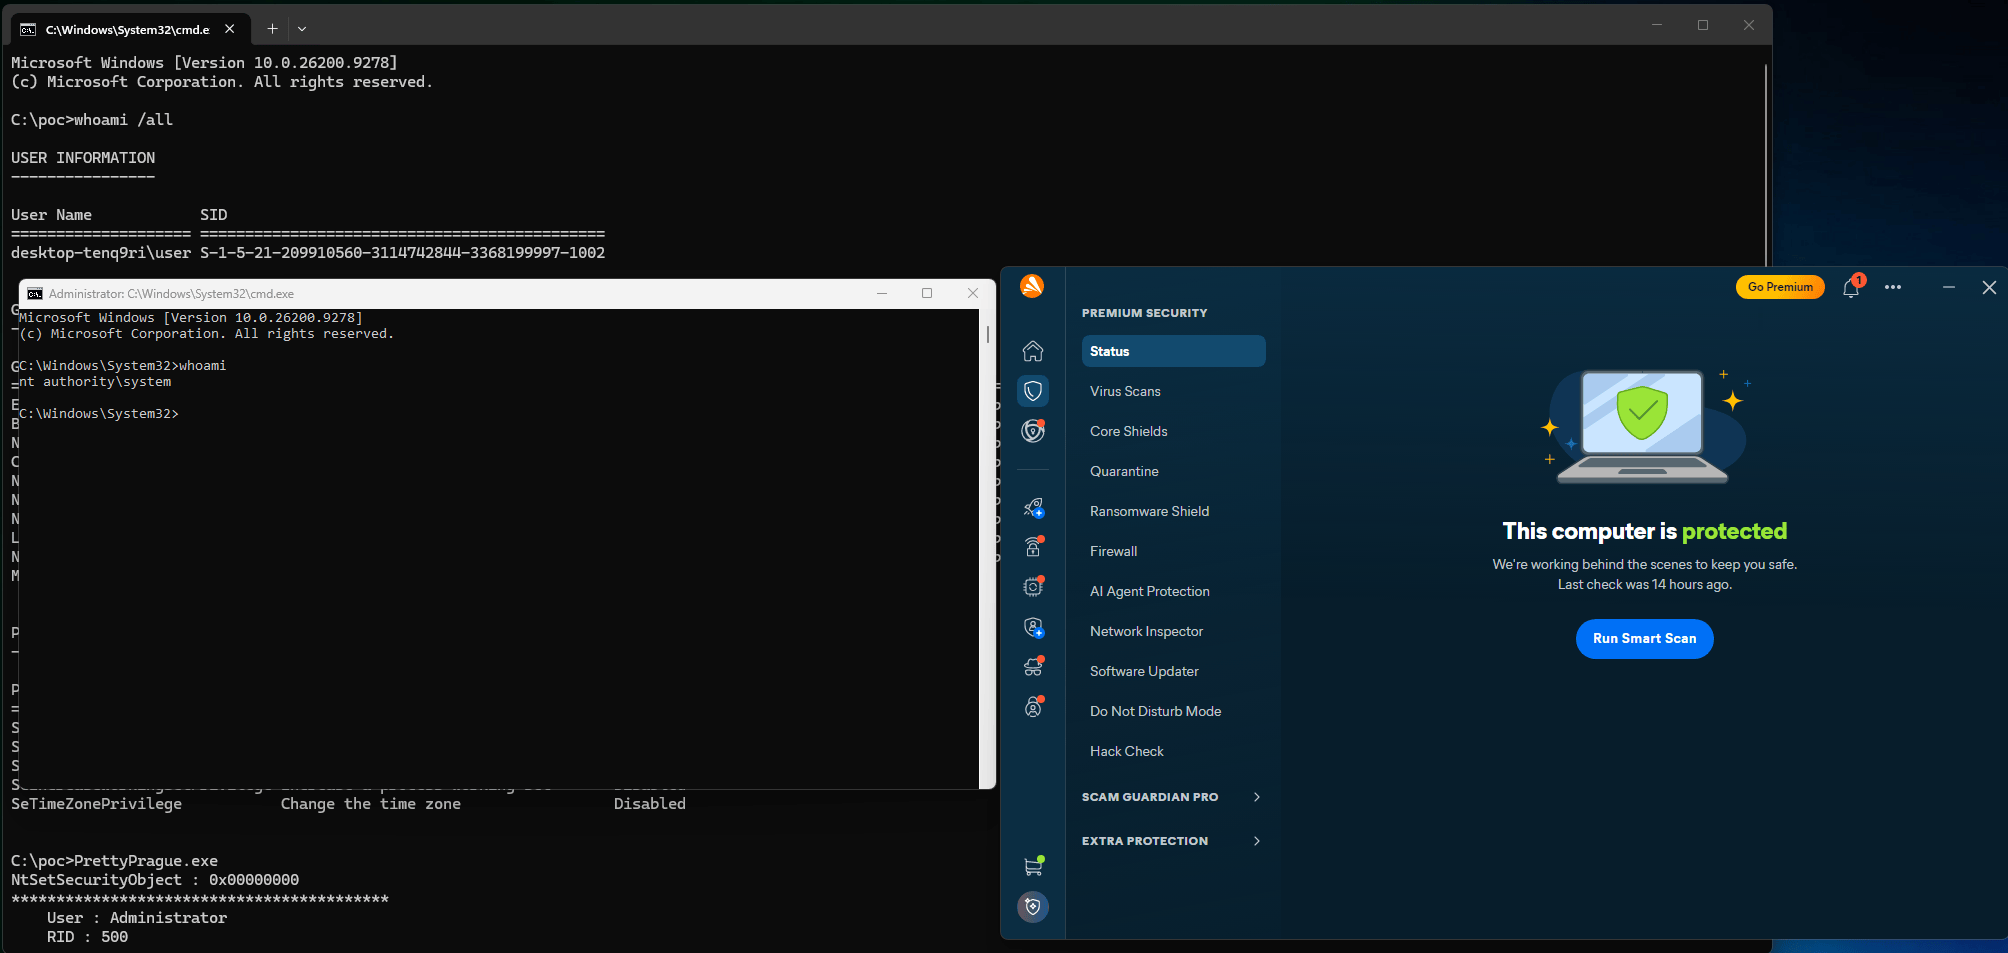
Recently, Chaotic Eclipse released another exploit targeting anti-malware solutions. It is named HardBreacher, a PoC exploit for a Kaspersky Endpoint Security privilege escalation flaw.
Chaotic Eclipse, also known as Nightmare Eclipse, is a researcher known for publicly releasing PoC exploits for zero-day vulnerabilities, often after criticizing vendors’ handling of vulnerability reports. His releases have mainly targeted Microsoft products, including Windows and Microsoft Defender, with some later exploited in the wild. Among the most notable are the Undefend and RedSun Defender zero-days.
His work has fueled debate over responsible disclosure and the risks of publishing working exploits.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Chaotic Eclipse)
Text extracted automatically; images, tables and formatting may be missing. Original: https://securityaffairs.com/198243/hacking/chaotic-eclipse-releases-gendigital-avast-antivirus-zeroday-prettyprague.html