Update Chrome now to protect against an actively exploited vulnerability
Google shipped Chrome 153.0.8010.36/.37 fixing 230 flaws including actively exploited V8 out-of-bounds write CVE-2026-87491 enabling sandboxed code execution.
Chrome stable channel updated to 153.0.8010.36/.37 for Windows and Mac and 153.0.8010.36 for Linux, including 230 security fixes. CVE-2026-87491 is an out-of-bounds write in Chrome's V8 JavaScript engine that a crafted HTML page can exploit to execute arbitrary code inside the browser sandbox; Google rates it medium severity, but it is confirmed as actively exploited. The update also fixes five Critical vulnerabilities, four of which were found in WebGL. Users should update via Settings > About Chrome and restart the browser.
- Chrome 153.0.8010.36/.37 ships 230 fixes, including one actively exploited V8 bug
- CVE-2026-87491 lets a crafted web page run attacker code inside the browser sandbox
- Five Critical fixes included, four of them in WebGL
- Users should verify updates via Settings > About Chrome and restart the browser
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2026-87491 | Actively Exploited Out-of-Bounds Write in Google Chrome V8 CVE-2026-87491 is an out-of-bounds write (CWE-787) in the V8 JavaScript engine in Google Chrome, fixed in Chrome 153.0.8010.36, which Google shipped alongside roughly 230 other security fixes. An attacker can trigger the flaw remotely by luring a user (user interaction required) into opening a crafted HTML page that corrupts memory in V8. Successful exploitation allows the attacker to execute arbitrary code inside the Chrome browser sandbox, which constrains but does not eliminate the impact. All Google Chrome users running versions prior to 153.0.8010.36 are affected; because the flaw resides in V8, CISA tracks it as 'Google Chromium V8', and other Chromium-based browsers may inherit the fix in their own updates. The flaw is being actively exploited in the wild — it is the seventh actively exploited Chrome zero-day of 2026 and was added to CISA's KEV catalog on 2026-09-09 — though no public proof-of-concept is known and ransomware use is unknown. Do: Update Google Chrome to 153.0.8010.36 or later immediately (open Help > About Google Chrome to force the update and relaunch), and verify the version on all endpoints. Also patch headless or automated Chrome deployments (CI runners, scrapers, kiosks, CDP-based tooling) that may lag auto-updates, and prioritize remediation per CISA KEV and BOD 26-04 requirements for federal systems. No public PoC is known and ransomware use is unknown, but confirmed in-the-wild exploitation warrants urgent patching. | 8.8 | <1% | KEV |
| massbillions of installations (Chrome's install base exceeds 3 billion users) |
Full article460 words · extracted from malwarebytes.com · click to collapse
Chrome is rolling out an update for its desktop browser. The update includes 230 security fixes, one of which is known to be actively exploited.
The stable channel has been updated to 153.0.8010.36/.37 for Windows and Mac, and 153.0.8010.36 for Linux.
How to update Chrome
If you don’t want to wait for the rollout to reach you, manually updating is easy.
The easiest option is to allow Chrome to update automatically. But you can end up lagging behind on updates if you never close your browser or if something goes wrong, such as an extension preventing the update.
To update manually, click the More menu (three dots), then go to Settings > About Chrome. If an update is available, Chrome will start downloading it automatically. Restart Chrome to complete the update, and you’ll be protected against these vulnerabilities.
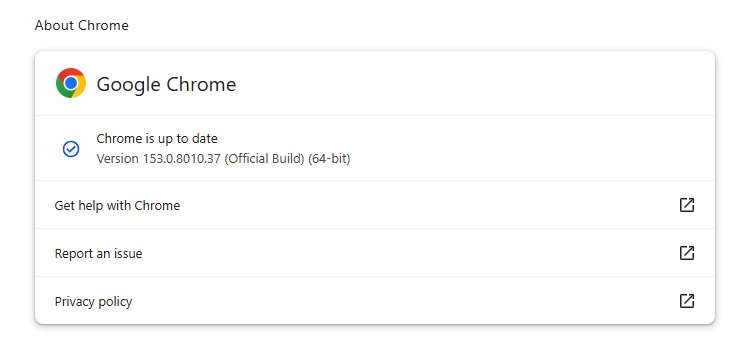
You can find an explanation of the version numbering system and step-by-step instructions in our guide: How to update Chrome on every operating system.
Technical details
The actively exploited vulnerability is tracked as CVE-2026-87491. The description says it’s an out-of-bounds write vulnerability in Chrome’s V8 engine that could allow a remote attacker to execute arbitrary code inside the browser’s sandbox via a crafted HTML page.
This means the bug was found in the part of Chrome that runs JavaScript. A malicious website could exploit it by getting someone to load a specially designed web page, causing Chrome’s JavaScript engine to mishandle memory and run attacker-chosen instructions. Those instructions would initially run within Chrome’s security sandbox rather than with unrestricted access to the whole device.
Chrome’s sandbox is intended to limit that code’s access to the rest of the device, but the flaw is still serious because it gives an attacker a foothold simply by getting a target to view a malicious web page. Emails are unlikely to trigger the flaw because most reputable email clients sanitize incoming HTML before displaying it. They strip or disable active web features that would let a sender run code in the inbox, such as JavaScript. However, an email could contain a link that takes the recipient to a malicious website.
Besides this medium-severity flaw, the update fixes five vulnerabilities rated Critical, four of which were found in WebGL (Web Graphics Library). WebGL is a JavaScript programming interface used to render interactive 2D and 3D graphics inside the browser without needing extra plugins.
Stop threats before they can do any harm.
Malwarebytes Browser Guard blocks phishing pages and malicious sites automatically. Free, one click to install. Add it to your browser →
About the author
Was a Microsoft MVP in consumer security for 12 years running. Can speak four languages. Smells of rich mahogany and leather-bound books.
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.malwarebytes.com/blog/bugs/2026/09/update-chrome-now-to-protect-against-an-actively-exploited-vulnerability