Ivanti patched CVE-2026-104935 after UTA0576 chained flaws to root on Connect Secure VPN appliances.
Ivanti released fixes on October 13, 2026, for CVE-2026-104935, a Connect Secure zero-day exploited before a patch existed. Volexity, which found the activity during an incident investigation, tracks the attacker as UTA0576. The actor chained three vulnerabilities to go from an unauthenticated web request to root-level code execution on an ICS VPN appliance running 22.8R2.4.
CVE-2026-104935 was exploited before Ivanti’s October 13, 2026 fixes.
Volexity found the activity in an incident and tracks the actor as UTA0576.
Three flaws were chained from an unauthenticated web request to root on ICS 22.8R2.4.
Auth Bypass to Command Execution in Ivanti Connect Secure
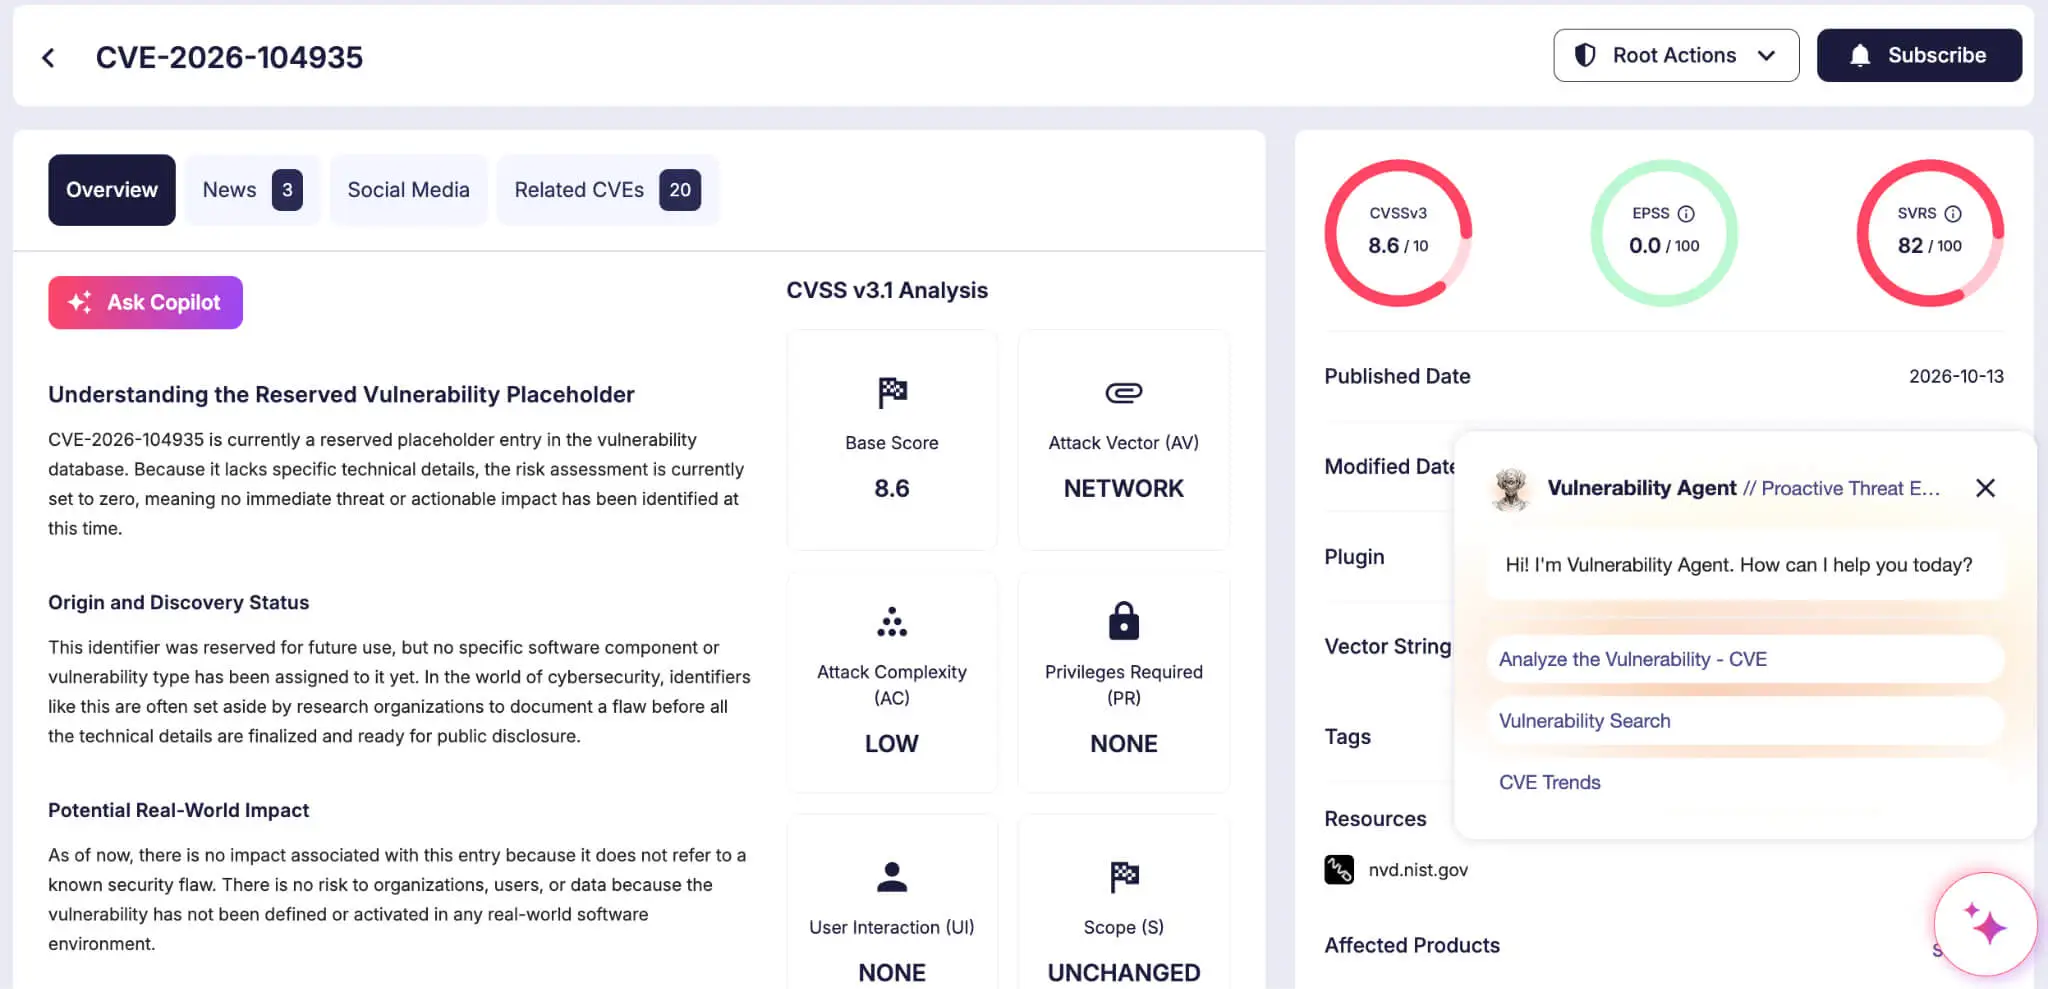
CVE-2026-104935 is an authentication bypass by spoofing (CWE-290) in Ivanti Connect Secure. A remote, unauthenticated attacker can spoof authentication on affected gateways and then execute arbitrary commands. Impact is high confidentiality loss with lower integrity and availability impact (CVSS 3.1 base 8.6; network, low complexity, no privileges or user interaction). It affects Connect Secure builds before 25.1.3.0 and does not affect 22.7R2.14 or earlier. CISA added it to the Known Exploited Vulnerabilities catalog on 2026-10-13 after reported zero-day attacks; ransomware use is listed as unknown, public proof-of-concept references exist, and EPSS is about 26% (98th percentile).
Do: Upgrade Ivanti Connect Secure to 25.1.3.0 or later. Builds at 22.7R2.14 and earlier are not affected. Because this is in CISA’s KEV catalog, apply the vendor’s mitigations, follow BOD 26-04 and CISA forensics-triage guidance, and treat internet-exposed appliances as potentially compromised until reviewed.
8.6
26%
KEV PoC ×2
Ivanti Connect Secure versions before 25.1.3.0, excluding 22.7R2.14 and earlier
largeon the order of 10,000–50,000 internet-exposed gateways for the product line; vulnerable-version subset unknown
Ivanti Connect Secure Zero-Day CVE-2026-104935 Exploited in Chained Attacks
Oct 14, 2026
11 Mins Read
Summarize with:
Ivanti Connect Secure Zero-Day CVE-2026-104935 Exploited in Chained Attacks
Ivanti released fixes on October 13, 2026, for CVE-2026-104935, an Ivanti Connect Secure zero-day that attackers exploited before a patch existed. Volexity, which uncovered the activity during an incident investigation, tracks the attacker as UTA0576. According to the published analysis, the actor chained three vulnerabilities to move from an unauthenticated web request to root-level code execution on an ICS VPN appliance running version 22.8R2.4, which was fully patched at the time.
CVE-2026-104935 covers the first two links in the chain: an authentication bypass and a remote code execution flaw. The third, a privilege escalation flaw, has no CVE and no patch yet. Ivanti says exploitation has affected “a limited number of customers,” and the full scope is still under investigation.
The case matters for any organization running ICS at the network edge. The actor stole credentials, mapped Active Directory and sniffed internal traffic, and researchers assess with high confidence that this was preparation for lateral movement and a broader compromise of the victim network. It also defeated the tool most ICS customers rely on to check appliance integrity, which makes a quiet compromise harder to rule out.
Details of CVE-2026-104935 (SOCRadar Vulnerability Intelligence)
Key Takeaways
Exploited Zero-Day: A threat actor tracked as UTA0576 chained three Ivanti Connect Secure (ICS) zero-days to gain unauthenticated root access on a fully patched ICS 22.8R2.4 appliance
Partial Fix: Ivanti patched the authentication bypass and remote code execution steps as CVE-2026-104935 on October 13, 2026; the privilege escalation flaw remains unpatched
KEV Listing: CISA added CVE-2026-104935 to the Known Exploited Vulnerabilities catalog on October 13, 2026
Detection Gap: The chain modifies code only in memory, so Ivanti’s Integrity Checker Tool does not detect it
Credential Theft: The attacker harvested domain credentials and queried Active Directory for LAPS passwords and BitLocker recovery keys
CVE-2026-104935 at a Glance
Attribute
Detail
CVE
CVE-2026-104935
CVSS
8.6 (CVSS v3.0)
Weakness
CWE-290, authentication bypass by spoofing
Affected Product
Ivanti Connect Secure (ICS)
Exploitation Status
Exploited in the wild as a zero-day; listed in CISA KEV on October 13, 2026
Patch Status
Authentication bypass and RCE patched; privilege escalation flaw unpatched
Threat Actor
UTA0576
Exploitation Discovered By
Volexity (Ivanti found part of the flaw internally in June 2026)
Affected and Fixed Versions
Fixed versions as listed breakdown of Ivanti’s advisory:
Affected Versions
Fixed Version
25.1.1.1 and prior
25.1.1.2
25.1.2.2 and prior
25.1.3.0 or 25.1.3.1
22.8R2.4 and prior
22.8R2.5
Public CVE record data lists versions before 25.1.3.0 as affected, which does not match 25.1.1.2 as a fix; confirm against Ivanti’s advisory before relying on 25.1.1.2.
Versions 22.7.x and below are not affected. The 22.7 and 22.8 code lines reach end of life on January 31, 2027, according to coverage of the advisory, and Ivanti describes 22.8 as a temporary bridge and recommends moving to 25.1.
Attack Timeline
Date
Event
June 2026
Ivanti finds part of the flaw during internal security checks and schedules it for a regular release
September 30 to October 7, 2026
The attacker-used host, 108.165.147[.]64, runs an OpenVPN server
October 3, 2026
UTA0576 begins exploiting the victim ICS appliance
October 5, 2026
Investigation of suspicious activity at the victim network starts and is traced to the ICS appliance
October 13, 2026
Ivanti releases patches and an advisory for CVE-2026-104935; the research is published; CISA adds the CVE to KEV
Pending
Ivanti fix for the privilege escalation flaw, expected in a future release
Other reporting puts the earliest confirmed exploitation at October 1, 2026, and quotes researchers saying activity may have started in late September.
How the Exploit Chain Works
The chain has three vulnerabilities, plus a staged payload that keeps most of the attacker’s code out of the file system.
Step 1: Authentication Bypass in welcome.cgi
The public login path /dana-na/auth/url_default/welcome.cgi accepts an X-DSCGI-PATH header. The appliance checks the requested URL to decide whether authentication is required, but routes the request to whatever script the header names. By pointing the header at a protected CGI script such as wu.cgi, an unauthenticated attacker reaches code that should sit behind the login.
Step 2: Race Condition in the wu.cgi Upload Handler
The wu.cgi upload handler writes an uploaded file to /home/runtime/tmp/<MD5(filename)> before it checks whether the file is a valid ZIP archive. Invalid files are deleted, but only after a short window. The attacker uploads a Perl script with a .zip extension and, at the same time, sends several requests that use the same header trick to execute the temporary file before it disappears. When a request wins the race, the script runs as the cgi-server user.
Step 3: Staged In-Memory Payload
The Perl script runs a Bash script, which in turn runs a Python script. The Python stage is Base64-encoded and zlib-compressed and is run with exec(), so it exists only in memory.
Step 4: Privilege Escalation Through DSCache
From the cgi-server context, the payload patches the in-memory copy of /home/lib/libdsplibs.so. That patch lets it change a DSCache maintenance task so the task launches the Perl interpreter, and then ask the root-level dsinvoked service to run it.
The exploit confirms root access by reading /etc/shadow, then restores the DSCache entry, which normally points the ScriptUtil/updateOpswatSDK command at /home/bin/updateOpswatSDK.pl, and reverses the library patch.
Each command the attacker ran re-executed the full chain, and results came back in the HTTP response. There was no web shell, no first-stage malware and no separate C2 channel.
UTA0576 Post-Exploitation Activity
Researchers assess with high confidence that the operator reviewed command output and adjusted its actions, rather than running a fixed script. Observed activity included:
Active Directory Reconnaissance: Custom LDAP tools (/tmp/ml.py, /tmp/rq5.py), run with an ICS Active Directory service account, searched for LAPS local administrator passwords, BitLocker recovery information, userPassword and unixUserPassword attributes, and logon script paths, exporting results as JSON to /tmp/
Credential Theft: The actor extracted credentials stored on the appliance, including domain credentials used for LDAP
Traffic Capture: A renamed tcpdump binary, /data/.icscap/dsstatmond, captured plaintext protocols such as LDAP, HTTP, FTP and telnet across eight rotating capture files; the actor parsed /data/.icscap/cap0 for TCP 389 traffic and tried to exfiltrate its first 8 KB
Credential Harvesting From Traffic: /data/.icscap/h.py extracted plaintext LDAP credentials, HTTP Basic credentials and NTLM challenge-response material
Kerberos Abuse: /tmp/mk.py included Kerberoasting functionality, and /tmp/rr.py tested credentials
Configuration and Log Collection: The actor targeted /home/etc/pulse/, /home/etc/, /home/*.cfg and /home/runtime, and pulled usernames from log.events.vc0 into /tmp/pu.txt
Network Reconnaissance and Password Spraying: The actor exfiltrated /etc/resolv.conf, resolved internal domains and ran a spraying script, sp_run.py, which produced sp_out.txt and spray_hits.json
All data left over the exploit channel itself. The operation was detected and disrupted before its final objective became clear.
Anti-Forensics
UTA0576 put real effort into hiding its tracks:
Log Tampering: Selective removal of recent entries from /home/runtime/dlogs/debuglog and /var/log/audit/audit.log
Payload Cleanup: Self-deletion of the root Perl payload and the Python stage’s cleanup script, removal of temporary results and the CGI source, and deletion of /tmp/rq5.py and /tmp/rr.py
Memory Restoration: Reversal of the DSCache change and the in-memory library patch through /proc/self/mem
Quiet Execution: Output of background cleanup redirected to /dev/null
Masquerading: tcpdump renamed to dsstatmond and run from a hidden .icscap directory, with rotating captures that overwrote earlier traffic
Because the debug and audit logs were edited, investigators had to work with Ivanti to collect memory images, disk images and core dumps to reconstruct the chain. Memory analysis exposed the dsstatmond sniffer (PID 5012) and recovered the actor’s scripts, JSON output and PCAP files.
Why the Integrity Checker Misses It
Ivanti’s Integrity Checker Tool looks for unexpected file changes on disk. Because this chain patches library code only in memory and restores the DSCache entries it alters, “the tool does not detect any modifications.” CISA issued the same warning, noting that the tool may not detect evidence of exploitation because attacker commands run in memory. A clean Integrity Checker result does not rule out compromise, and forensic investigation is required to identify exploitation.
Possible Use of AI in Exploit Development
Researchers assess with medium confidence that UTA0576 uses large language models for exploit development and post-exploitation work. The evidence cited is the choice of a continuous exploit channel over a simple web shell, highly specific scripts with hardcoded credentials, and the overall complexity of the chain. On motive, they assess with low confidence that the actor is criminal rather than espionage-driven.
Ivanti Edge Devices Remain a Prime Target
This is not an isolated case. CISA has listed 36 Ivanti defects in KEV since late 2021, and at least six Ivanti defects have been exploited since late January 2026, per reporting on the disclosure. Ivanti found part of this flaw internally in June 2026 but said it “did not meet the threshold for an out-of-band release,” leaving a window that attackers used before the fix shipped.
Researchers note that edge devices often give attackers a foothold for pivoting into networks. One researcher warned that the trivial authentication bypass and repeatable race condition make “widespread, indiscriminate exploitation” likely as attackers study the patches.
Indicators of Compromise
Network:
108.165.147[.]64 (Evoxt VPS)
Request Patterns:
High volumes of requests to /dana-na/auth/url_default/welcome.cgi
The complete indicator set is published in a public repository.
How to Check Whether Your Appliance Was Compromised
Review Web Logs: Look for high volumes of welcome.cgi requests and for any request where the X-DSCGI-PATH header does not match the URL path, including paths beyond the two listed above
Inspect Temporary Directories: Check /tmp/ and /home/runtime/tmp/ for unexpected scripts, JSON output or text files
Look for the Sniffer: Check for a dsstatmond process or a hidden .icscap directory under /data/
Compare Log Continuity: Gaps in /home/runtime/dlogs/debuglog or /var/log/audit/audit.log may indicate selective deletion
Capture Memory: If anything looks suspicious, collect memory and network evidence, since the chain leaves little on disk
Mitigation and Recommendations
Patch Now: Upgrade to 25.1.1.2, 25.1.3.0 or later, or 22.8R2.5, and plan migration to the 25.1 code line before 22.7 and 22.8 reach end of life
Track the Remaining Fix: Ivanti is still developing a fix for the privilege escalation flaw; apply it as soon as it ships
Hunt for Exploitation: Monitor for high volumes of welcome.cgi requests and for mismatches between the URL path and the X-DSCGI-PATH header
Check Temporary Directories: Review /tmp/ for post-exploitation artifacts
Run Forensics: If compromise is suspected, perform network and memory forensics; do not rely on the Integrity Checker Tool alone
Assume Stored Credentials Are Exposed: On a compromised appliance, treat stored domain credentials as stolen, since UTA0576 extracted stored LDAP credentials and harvested plaintext credentials from captured traffic
Frequently Asked Questions
What Is CVE-2026-104935?
CVE-2026-104935 is an authentication bypass and remote code execution vulnerability in Ivanti Connect Secure, rated CVSS 8.6. It lets a remote, unauthenticated attacker reach protected CGI scripts and run commands as the cgi-server user. Attackers exploited it as a zero-day before Ivanti released a fix on October 13, 2026.
Is CVE-2026-104935 Being Exploited?
Yes. A threat actor tracked as UTA0576 has exploited it since early October 2026, and Ivanti says a limited number of customers were compromised. CISA added it to the Known Exploited Vulnerabilities catalog on October 13, 2026.
Which Ivanti Connect Secure Versions Are Fixed?
The fixed versions are 25.1.1.2, 25.1.3.0 or 25.1.3.1, and 22.8R2.5. Versions 22.7.x and below are not affected. Ivanti recommends moving to the 25.1 code line, since 22.7 and 22.8 reach end of life on January 31, 2027.
Does Patching Fully Close the Attack Chain?
No. The patch fixes the authentication bypass and remote code execution steps, which removes unauthenticated access to the chain. The privilege escalation flaw used to reach root is still unpatched, and Ivanti is working on a fix for a future release.
Can the Ivanti Integrity Checker Tool Detect This Attack?
Not reliably. The exploit chain changes library code only in memory and restores the configuration it modifies, so the Integrity Checker Tool does not detect it. Network and memory forensics are needed on any appliance suspected of compromise.
What Did the Attackers Steal?
The attacker extracted credentials stored on the appliance, including domain credentials used for LDAP, and harvested plaintext credentials and NTLM material from captured traffic. It also queried Active Directory for LAPS passwords and BitLocker recovery information and exfiltrated configuration data and usernames from appliance logs.
Who Is UTA0576?
UTA0576 is the designation for the unidentified threat actor that chained the Ivanti Connect Secure zero-days. Researchers assess with low confidence that the actor is criminally motivated rather than espionage-driven, and with medium confidence that it uses large language models for exploit development and post-exploitation work. The operation was disrupted, so its final objective is unknown.
PROTECTION OF PERSONAL DATA****COOKIE POLICY FOR THE INTERNET SITE
Protecting your personal data is one of the core principles of our organization, SOCRadar, which operates the internet site (www.socradar.com). This Cookie Usage Policy (“Policy”) explains the types of cookies used and the conditions under which they are used to all website visitors and users.
Cookies are small text files stored on your computer or mobile device by the websites you visit.
Cookies are commonly used to provide you with a personalized experience while using a website, enhance the services offered, and improve your overall browsing experience, contributing to ease of use while navigating a website. If you prefer not to use cookies, you can delete or block them through your browser settings. However, please be aware that this may affect your usage of our website. Unless you change your cookie settings in your browser, we will assume that you accept the use of cookies on this site.
1. WHAT KIND OF DATA IS PROCESSED IN COOKIES?
Cookies on websites collect data related to your browsing and usage preferences on the device you use to visit the site, depending on their type. This data includes information about the pages you access, the services and products you explore, your preferred language choice, and other preferences.
2. WHAT ARE COOKIES AND WHAT ARE THEIR PURPOSES?
Cookies are small text files stored on your device or web server by the websites you visit through your browsers. These small text files, containing your preferred language and other settings, help us remember your preferences on your next visit and assist us in making improvements to our services to enhance your experience on the site. This way, you can have a better and more personalized user experience on your next visit.
The main purposes of using cookies on our Internet Site are as follows:
Improve the functionality and performance of the website to enhance the services provided to you,
Enhance and introduce new features to the Internet Site and customize the provided features based on your preferences,
Ensure legal and commercial security for the Internet Site, yourself, and the Organization, and prevent fraudulent transactions through the Site,
Fulfill legal and contractual obligations, including those arising from Law No. 5651 on the Regulation of Publications on the Internet and the Fight Against Crimes Committed Through These Publications, as well as the Regulation on the Procedures and Principles Regarding the Regulation of Publications on the Internet.
3. TYPES OF COOKIES USED ON OUR INTERNET SITE****3.1. Session Cookies
Session cookies ensure the smooth operation of the internet site during your visit. They are used for purposes such as ensuring the security and continuity of our sites and your visits. Session cookies are temporary cookies and are deleted when you close your browser; they are not permanent.
3.2. Persistent Cookies
These cookies are used to remember your preferences and are stored on your device through browsers. Persistent cookies remain stored on your device even after you close your browser or restart your computer. These cookies are stored in your browser’s subfolders until deleted from your browser’s settings. Some types of persistent cookies can be used to provide personalized recommendations based on your usage purposes.
With persistent cookies, when you revisit our website with the same device, the website checks if a cookie created by our website exists on your device. If so, it is understood that you have visited the site before, and the content to be presented to you is determined accordingly, offering you a better service.
3.3. Mandatory/Technical Cookies
Mandatory cookies are essential for the proper functioning of the visited internet site. The purpose of these cookies is to provide necessary services by ensuring the operation of the site. For example, they allow access to secure sections of the internet site, use of its features, and navigation.
3.4. Analytical Cookies
These cookies gather information about how the website is used, the frequency and number of visits, and show how visitors navigate to the site. The purpose of using these cookies is to improve the operation of the site, increase its performance, and determine general trend directions. They do not contain data that can identify visitors. For example, they show the number of error messages displayed or the most visited pages.
3.5. Functional Cookies
Functional cookies remember the choices made by visitors within the site and recall them during the next visit. The purpose of these cookies is to provide ease of use to visitors. For example, they prevent the need to re-enter the user’s password on each page visited by the site user.
3.6. Targeting/Advertising Cookies
They measure the effectiveness of advertisements shown to visitors and calculate how many times ads are displayed. The purpose of these cookies is to present personalized advertisements to visitors based on their interests.
Similarly, they determine the specific interests of visitors’ navigation and present appropriate content. For example, they prevent the same advertisement from being shown again to the visitor in a short period.
4. HOW TO MANAGE COOKIE PREFERENCES?
To change your preferences regarding the use of cookies, block or delete cookies, you only need to change your browser settings.
Many browsers offer options to accept or reject cookies, only accept certain types of cookies, or receive notifications from the browser when a website requests to store cookies on your device.
Also, it is possible to delete previously saved cookies from your browser.
If you disable or reject cookies, you may need to manually adjust some preferences, and certain features and services on the website may not work properly as we will not be able to recognize and associate with your account. You can change your browser settings by clicking on the relevant link from the table below.
5. EFFECTIVE DATE OF THE INTERNET SITE PRIVACY POLICY
The Internet Site Privacy Policy is dated The effective date of the Policy will be updated if the entire Policy or specific sections are renewed. The Privacy Policy is published on the Organization’s website (www.socradar.com) and made accessible to relevant individuals upon request.
SOCRadar
Address: 651 N Broad St, Suite 205 Middletown, DE 19709 USA
Phone: +1 (571) 249-4598
Email: [email protected]
Website: www.socradar.com


 Extended Threat Intelligence Threat intelligence enriched with External Attack Surface Management, Brand Protection, and Dark Web Radar. Explore XTIAgentic Threat Intelligence Stay ahead of cybercriminals with AI agents that autonomously think, adapt, and act. Explore ATI Advanced Dark Web Monitoring
 Dark Web Report