SideCopy Hackers Target Indian Organizations With ReverseRAT Malware to Steal Data
SideCopy is spear-phishing Indian organizations with malicious shortcuts to deploy in-memory ReverseRAT for data theft.
Indian authorities warned that SideCopy is spear-phishing Indian organizations, including academic institutions, to deploy ReverseRAT on Windows. Trellix documented a chain that starts with a ZIP and a disguised LNK shortcut, pulls an obfuscated HTA from docsportal.in, and executes it through mshta.exe. Persistence uses a Registry Run key; a second HTA reflectively loads ReverseRAT, which can steal passwords, screenshots, clipboard data, and files and open remote shells. Reported command-and-control is dns.educationportals.biz over TCP port 5863, protected with a hardcoded key. The advisory rates the threat medium severity.
- Indian authorities warned that SideCopy is spear-phishing Indian organizations, including academia.
- Weaponized ZIPs contain LNK shortcuts that fetch an HTA and run it with mshta.exe.
- A Registry Run key restarts the chain; ReverseRAT is loaded reflectively in memory.
- ReverseRAT steals passwords, screenshots, and clipboard data and can run commands.
- Command-and-control uses educationportals.biz on TCP port 5863 with a hardcoded key.
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | dns.educationportals.biz | oints. Reported command-and-control infrastructure includes dns[.]educationportals[.]biz, with communications using TCP port 5863. The malware a |
| domain | docsportal.in | ication, or HTA, from attacker-controlled infrastructure at docsportal[.]in. Windows executes this script through mshta.exe, allowing |
Full article486 words · extracted from gbhackers.com · click to collapse
Indian authorities have warned that SideCopy hackers are targeting Indian organizations, including academic institutions, with spear-phishing attacks that deploy ReverseRAT on Windows systems.
The October 15, 2026, advisory classifies the threat as medium severity and highlights malware that can steal passwords, capture screenshots, and collect sensitive information.
The campaign combines deceptive attachments, malicious Windows shortcuts, obfuscated scripts, and legitimate operating system utilities.
SideCopy Hackers Target Indian Organizations
Trellix researchers documented a multistage infection chain that establishes persistence before loading the remote access Trojan into memory, complicating detection through conventional file scanning.
The intrusion begins with a phishing email carrying a weaponized ZIP archive. Inside, a malicious LNK shortcut masquerades as a document with a misleading name and a spoofed PDF icon, encouraging recipients to run it.
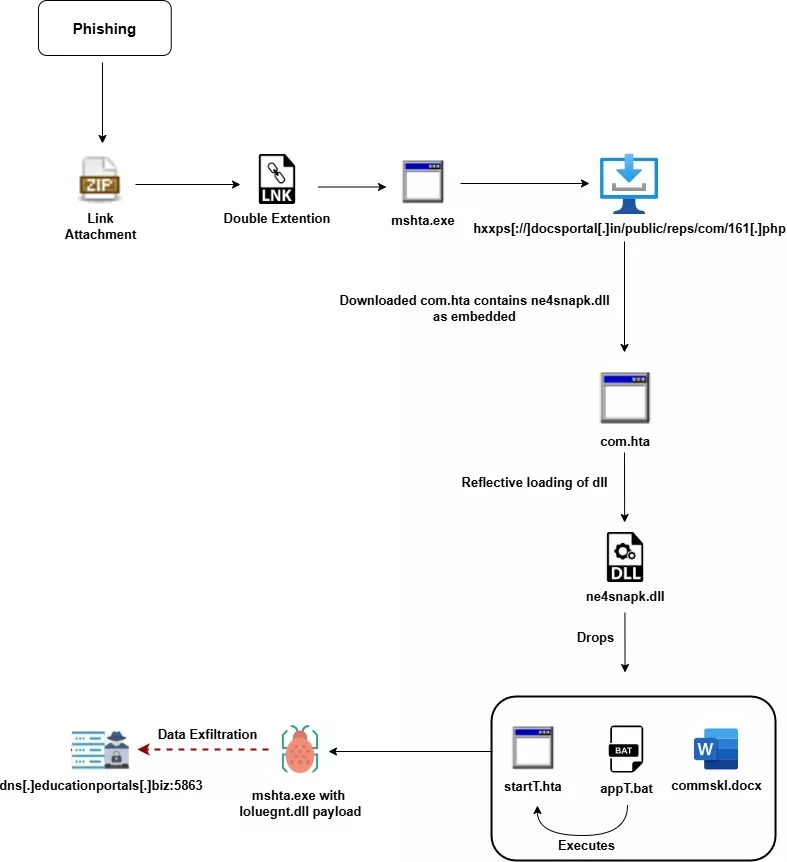
Opening the shortcut retrieves an obfuscated HTML Application, or HTA, from attacker-controlled infrastructure at docsportal[.]in. Windows executes this script through mshta.exe, allowing attackers to exploit a legitimate system utility as their execution host.
The HTA embeds ne4snapk.dll, which loads into the mshta.exe process through .NET deserialization. This DLL acts as a dropper, extracting three compressed components: appT.bat, startT.hta, and commskl.docx. The document serves as a decoy while the scripts advance the infection.
CSk said Persistence relies on a Windows Registry Run key that launches appT.bat when the affected user signs in. The batch script then starts mshta.exe to execute startT.hta in the background, enabling the malware to resume without another phishing interaction.
The secondary HTA reconstructs its obfuscated payload and reflectively loads ioluegnt.dll, identified by Trellix as ReverseRAT. This process uses .NET deserialization to convert encoded content into an active in-memory payload.
Although the final execution phase reduces exposure to disk-based scanning, the broader intrusion still creates scripts and other artifacts. It is therefore a staged infection with an in-memory payload, rather than an entirely fileless attack.
ReverseRAT can collect system metadata, installed software details, screenshots, passwords, and clipboard contents. Operators can also execute commands, manipulate files, upload additional content, and initiate shell sessions, giving them extensive access to compromised endpoints.
Reported command-and-control infrastructure includes dns[.]educationportals[.]biz, with communications using TCP port 5863. The malware also uses a hardcoded cryptographic key to protect command-and-control traffic and stolen information.
Defenders should prioritize unusual mshta.exe activity, especially connections to external infrastructure followed by script execution and unexpected Registry Run changes. Correlating these behaviors can expose the infection chain more effectively than relying on individual filenames alone.
Organizations should strengthen email filtering, restrict malicious shortcut execution, and deploy behavioral detection. Suspected infections warrant evidence preservation and incident response because ReverseRAT’s surveillance and file-theft capabilities create an immediate data-exposure risk.
Join 16,000+ SOC teams using ANY.RUN to streamline threat investigations and reduce manual effort. Explore for your team
Eswar is a Cyber security content editor with a passion for creating captivating and informative content. With years of experience under his belt in Cyber Security, he is covering Cyber Security News, technology and other news.