Tren de Aragua ATM Jackpotting Network Linked to $40.7 Million in U.S. Losses
The U.S. Treasury sanctioned a Tren de Aragua network tied to $40.7 million in ATM jackpotting losses.
The U.S. Treasury on September 30 sanctioned a Tren de Aragua-linked network accused of malware-driven ATM jackpotting that stole an estimated $40.73 million from U.S. financial institutions. OFAC designated eight individuals, two Mexico-based companies, and seven TRON addresses under Executive Orders 13581 and 13224. Treasury said the operation conducted more than 1,500 U.S. jackpotting attacks as of August 2025, with cash laundered through international channels including cryptocurrency. Separately, the Justice Department has indicted 98 people in ATM jackpotting cases since October 21, 2025; the allegations remain unproven in court.
- OFAC sanctioned eight people, two Mexican companies, and seven TRON addresses.
- Treasury says the network conducted over 1,500 U.S. ATM jackpotting attacks by August 2025.
- Alleged malware author Anibal Canelon Aguirre is on the FBI Ten Most Wanted list.
- The Justice Department has indicted 98 people in ATM jackpotting cases since October 2025.
- TRM Labs says the seven wallets received about $6.1 million since March 2022.
Full article683 words · extracted from gbhackers.com · click to collapse
The U.S. Treasury Department has sanctioned a Tren de Aragua (TdA)-linked financial network accused of using malware-driven ATM jackpotting attacks to steal an estimated $40.73 million from U.S. financial institutions.
The September 30 action adds eight individuals, two Mexico-based companies, and seven TRON cryptocurrency addresses to the Office of Foreign Assets Control’s (OFAC) Specially Designated Nationals and Blocked Persons List.
Jackpotting is a physical-cybercrime technique in which attackers compromise automated teller machines or interactive teller machines with malware, bypass transaction controls, and force the devices to dispense cash without debiting a customer account.
The cash is then collected by cash-out crews and, according to Treasury, laundered through international financial channels, including cryptocurrency transactions.
The action highlights the convergence of organized crime, malware-enabled attacks, cross-border cash laundering, and virtual-asset infrastructure.
TdA, a Venezuela-origin criminal organization designated by OFAC as a Transnational Criminal Organization in July 2024 and later designated by the State Department as a Foreign Terrorist Organization, allegedly used the jackpotting operation as a major revenue source.
Treasury’s designation was issued under Executive Orders 13581 and 13224, authorities used to target transnational criminal organizations and terrorism-linked financial networks.
A principal target is Anibal Alexander Canelon Aguirre, also known as “Prometheus,” who is listed on the FBI’s Ten Most Wanted Fugitives list.
Treasury alleges that Canelon Aguirre engineered the malware used in the cash-out operations and directed a network targeting U.S. ATM infrastructure.
Six alleged associates were sanctioned alongside him: Eric Gabriel Cardenas Arzola, Jose Dario Galeano Bazurto, Anthony Wuiliam Hernandez Guerrero, Carlos Javier Martinez Armenta, Oscar Leonardo Martinez Pirona, and Alejandro Mejia Castillo.
Each was linked to a newly sanctioned TRON address.bankingjournal.
ATM Jackpotting Network
The designations also cover Aslhy Javier Galeano Basurto, as well as Mexico-based entities Enigma Community S. de R.L. de C.V. and Soluciones Integrales Toluca S.A. de C.V.
TRM Researchers observed that, Treasury said the alleged TdA operation conducted more than 1,500 ATM jackpotting attacks in the United States as of August 2025.
Treasury separately sanctioned Juan Gabriel Rivas Nunez, known as “Juancho,” an alleged senior TdA figure accused of overseeing illicit gold mining, narcotics exports, and violent criminal activity across South America.
The allegations against the individuals remain unproven unless and until established in court.
Blockchain intelligence firm TRM Labs said the seven sanctioned TRON addresses collectively received approximately $6.1 million in inflows from March 2022 onward.
The firm cautioned that not all funds moving through the wallets are necessarily connected to the jackpotting campaign. The address attributed to Cardenas Arzola received the largest share, approximately $2.1 million.
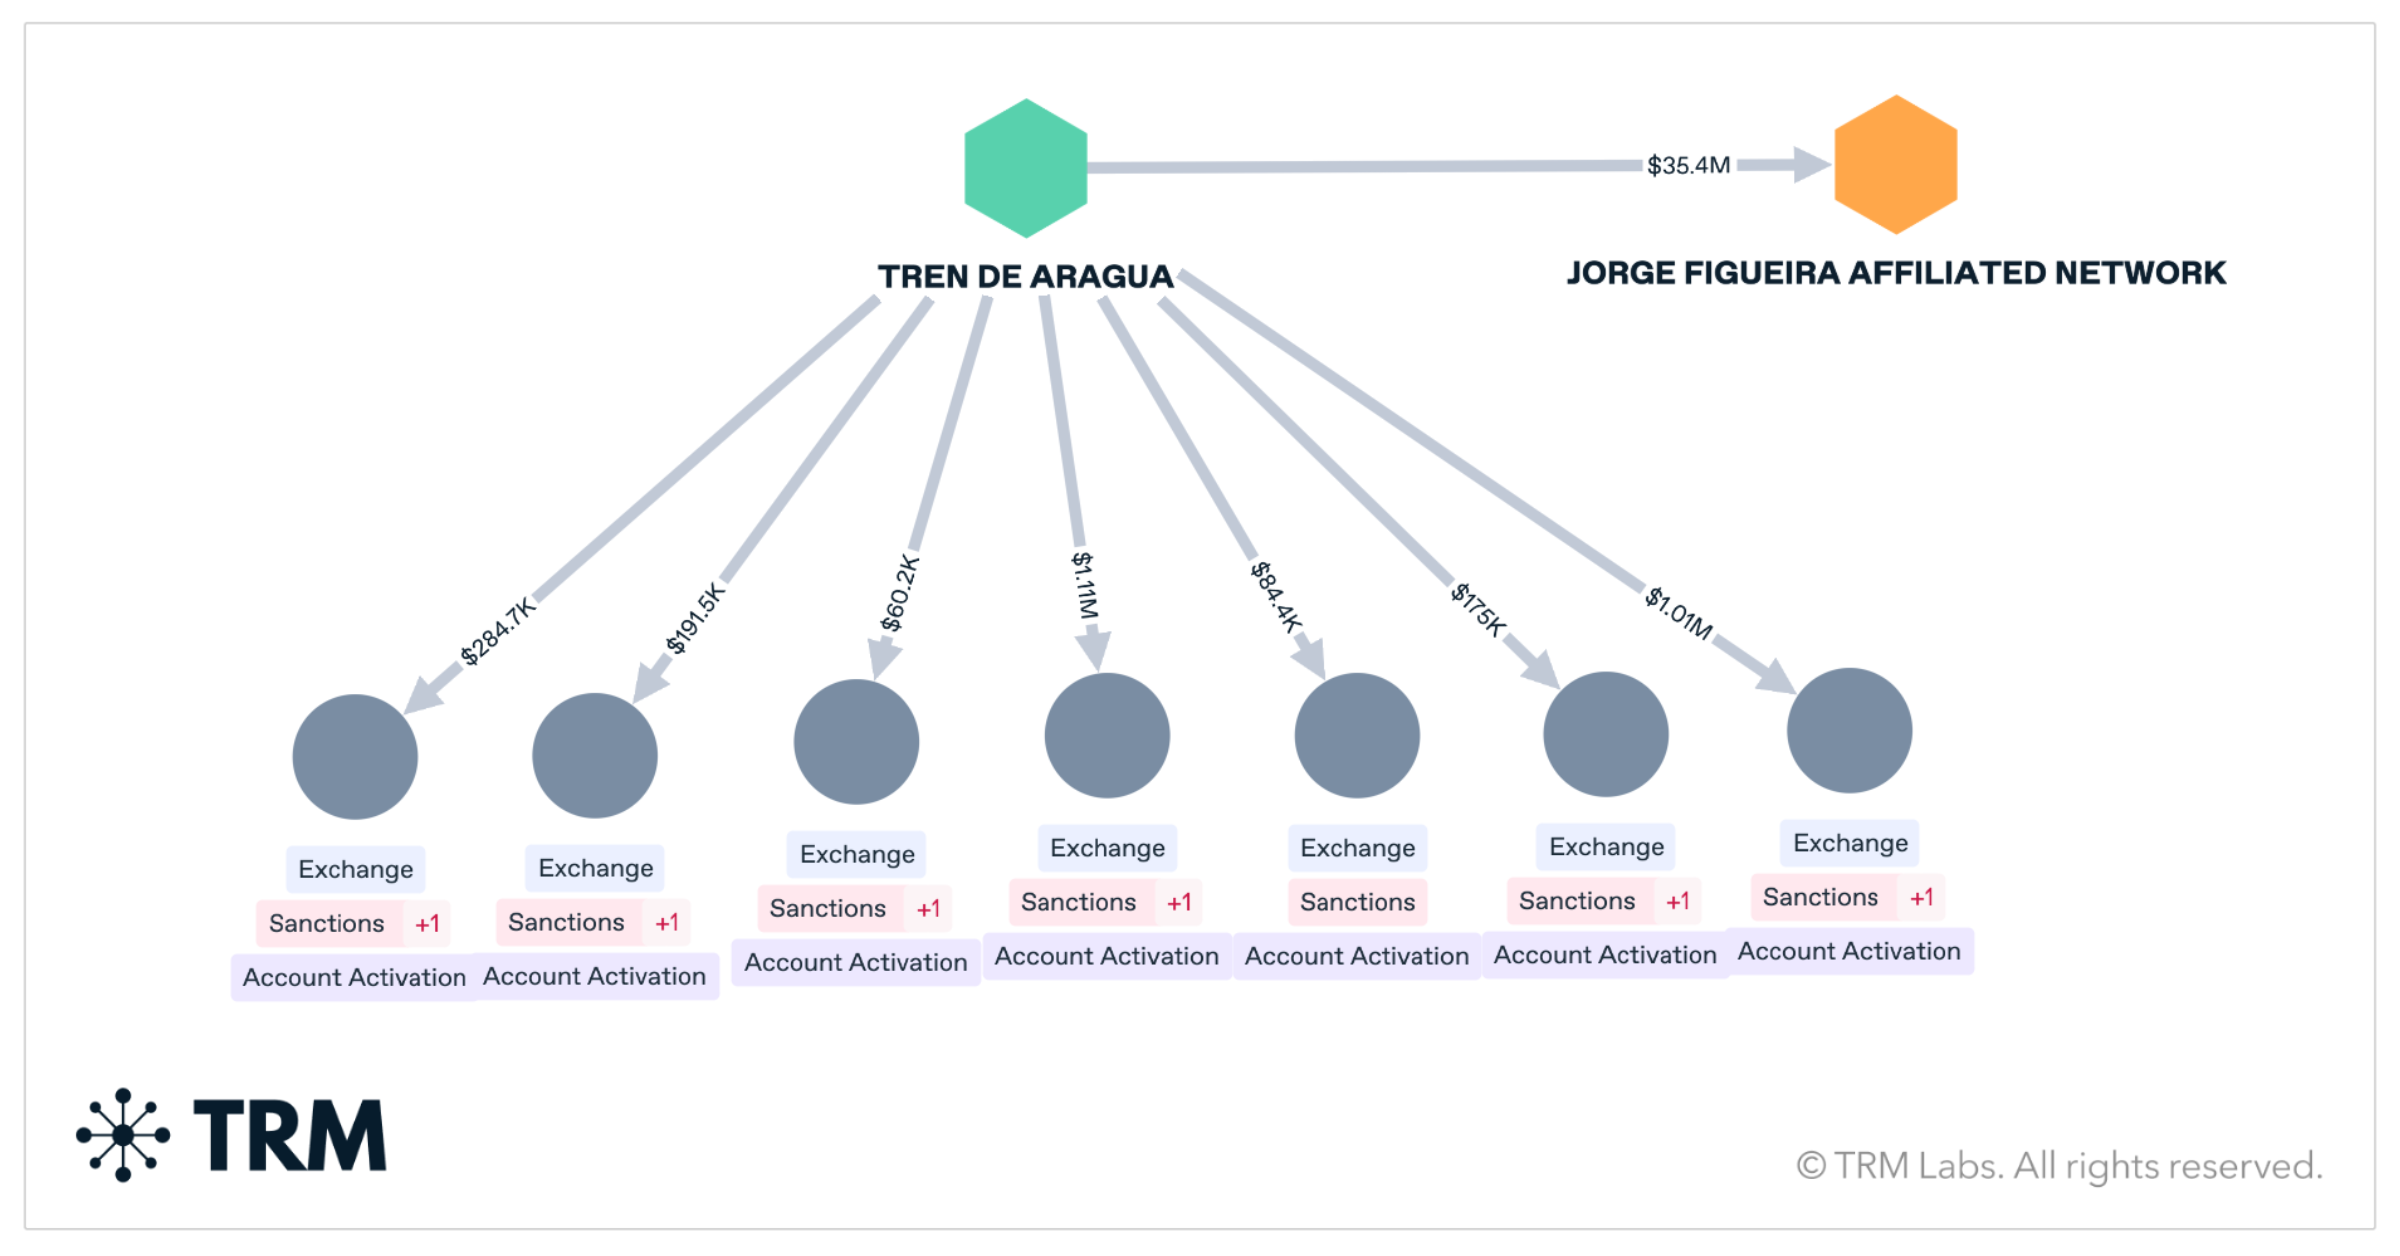
All seven are exchange-hosted deposit addresses, a pattern that creates immediate compliance implications for centralized exchanges, virtual asset service providers, and financial institutions.
Screening must account not only for direct transfers to the designated wallets, but also indirect exposure through intermediary addresses, deposits, withdrawals, and counterparties associated with the broader TdA ecosystem.
TRM said the wallets sent funds to other TdA-associated addresses, which subsequently transferred an estimated $35 million to a network U.S. authorities have linked to Venezuelan national Jorge Figueira, who faces separate money-laundering allegations.
For banks, ATM operators, and cryptocurrency platforms, the case underscores that ATM jackpotting is no longer merely a localized cash-theft problem.
The sanctions action follows an expanding federal crackdown on TdA-linked financial and cyber-enabled crime.
Treasury said it has taken more than 30 actions involving over 300 individuals and entities tied to transnational criminal organizations since 2025.
Separately, the Justice Department has indicted 98 people in ATM jackpotting cases since October 21, 2025, including defendants charged with bank fraud, bank burglary, computer damage, money laundering, and providing material support to TdA.
It is an organized cyber-enabled fraud model in which malware intrusion, physical cash collection, and blockchain-based laundering operate as connected stages of a transnational criminal pipeline.
Cut every SOC alert investigation by 21 min. Power your SOC with instant IOC context for immediate response: Integrate TI Lookup in your SOC
Mayura Kathirhttps://gbhackers.com/
Mayura Kathir is a cybersecurity reporter at GBHackers News, covering daily incidents including data breaches, malware attacks, cybercrime, vulnerabilities, zero-day exploits, and more.